
lazyrecon
 jhaddix/lazyrecon
This script is intended to automate your reconnaissance process in an organized fashion
information-gatheringnetwork-mappingpenetration-testing+4
488 years ago
jhaddix/lazyreconThis script is intended to automate your reconnaissance process in an organized fashion
 m0usem0use/erl_mouse
python script to find vulnerable targets of CVE-2025-32433
 s0md3v/smap
a drop-in replacement for Nmap powered by shodan.io
 eldraco/domain_analyzer
Analyze the security of any domain by finding all the information possible. Made in python.
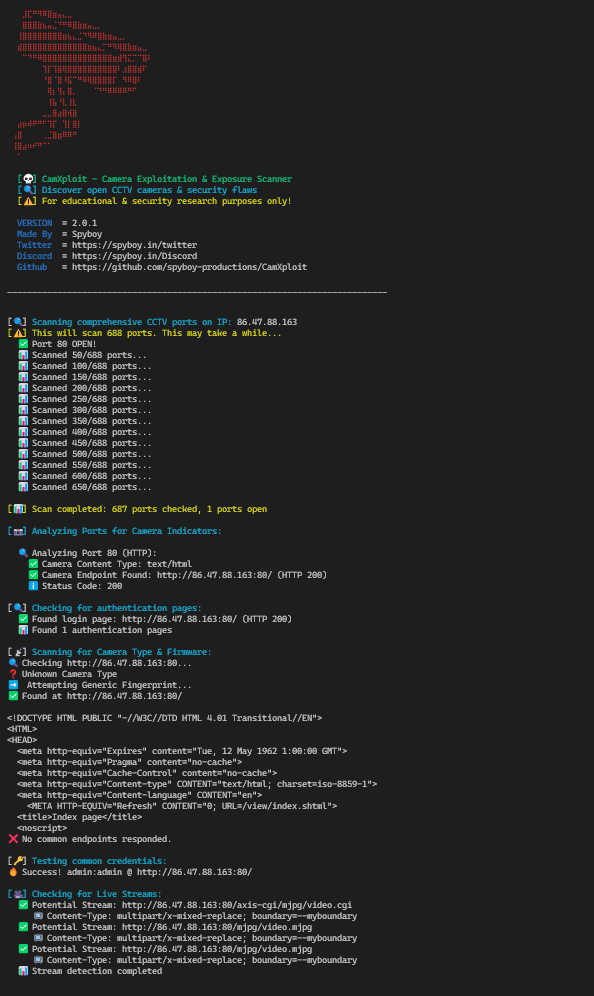 spyboy-productions/camxploit
Security reconnaissance and assessment tool for identifying potentially exposed IP cameras by analyzing open ports, service configurations, and…
 praetorian-inc/nerva
Fast service fingerprinting CLI for 170+ protocols (TCP/UDP/SCTP) - built by Praetorian
 edu4rdshl/unimap
Scan only once by IP address and reduce scan times with Nmap for large amounts of data.
 g0ldencybersec/cloudrecon
Suite of tools for red teamers and bug hunters to discover ephemeral cloud assets by scanning IP ranges and inspecting SSL certificates for hidden…
 cisagov/findcdn
Scans domains to identify which Content Delivery Network (CDN) they use by fingerprinting HTTPS headers, CNAME records, and WHOIS data, with JSON…
 yukselberkay/asnap
Automates reconnaissance by mapping IPv4/IPv6 addresses to organizations using GeoLite2 databases, with integrated nmap port scanning and batch…
 pownjs/recon
A powerful target reconnaissance framework powered by graph theory.
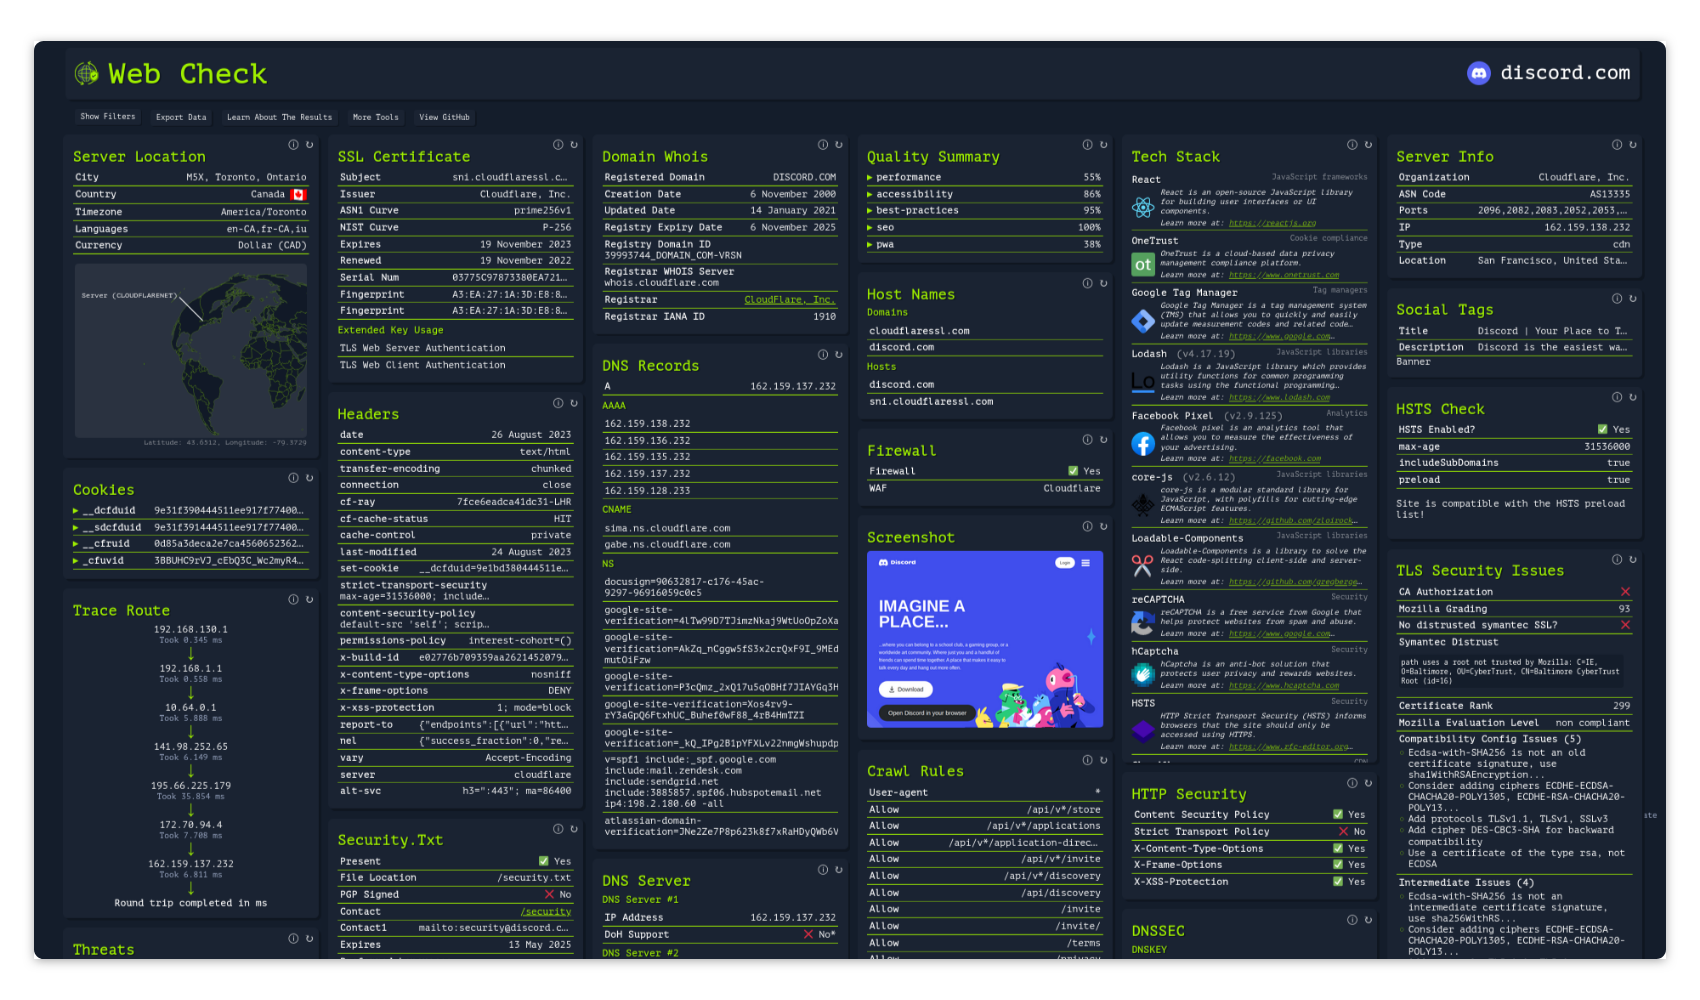 lissy93/web-check
🕵️♂️ All-in-one OSINT tool for analysing any website
 autorecon/autorecon
Multi-threaded network reconnaissance tool that automates service enumeration, port scanning, and information gathering for penetration testing and…
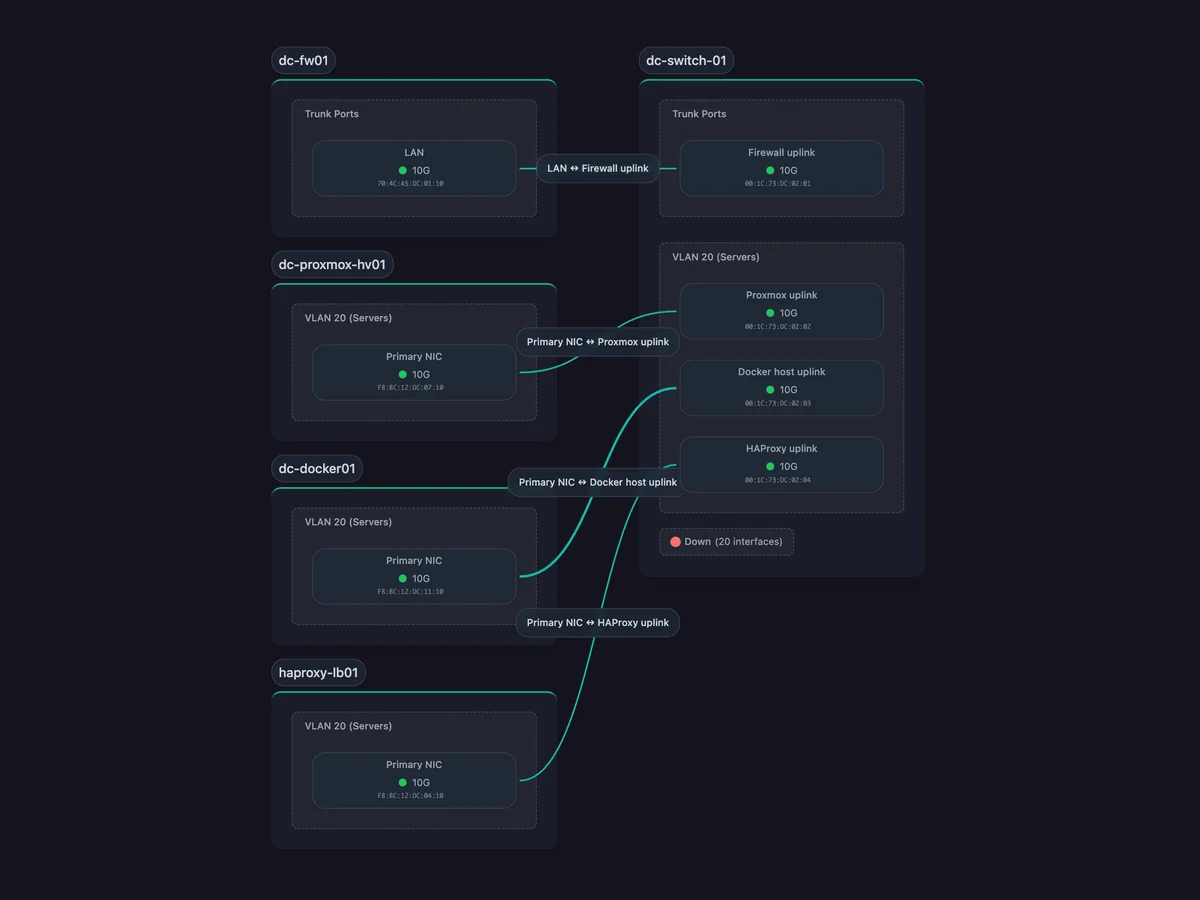 scanopy/scanopy
Network diagrams that update themselves
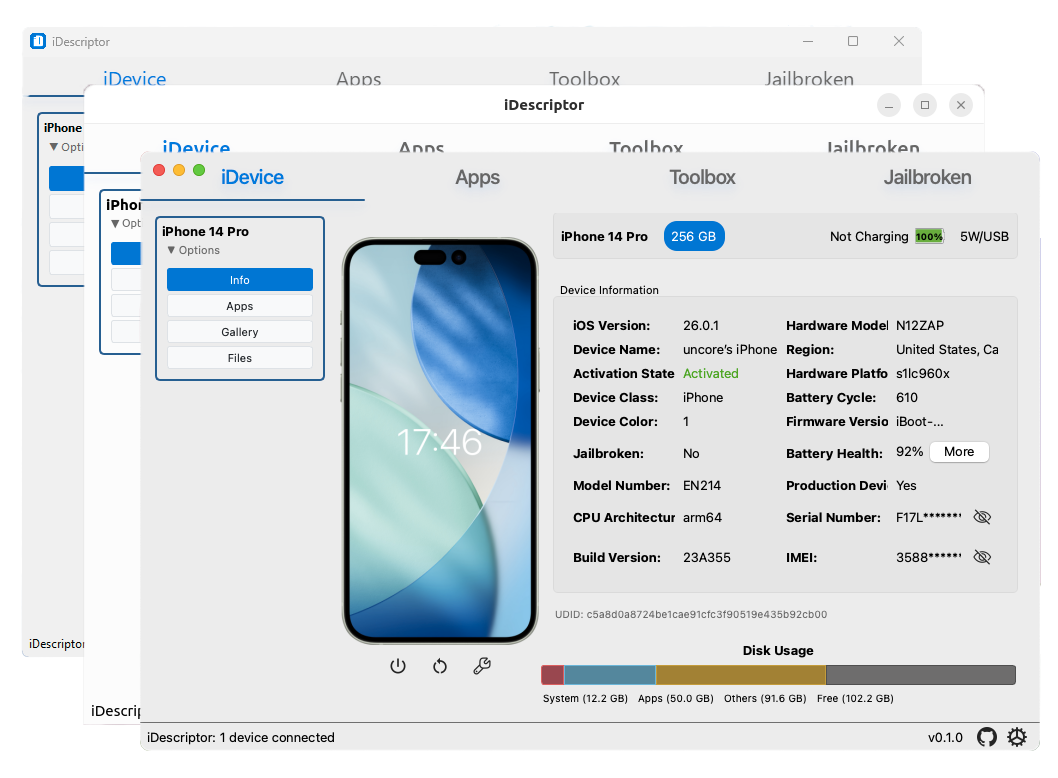 idescriptor/idescriptor
privacy-first, open-source and free idevice management tool written in Rust and Qt
 rapid7/recog
Pattern recognition for hosts, services, and content
 ullaakut/nmap
Idiomatic Go library for invoking a network scanner binary, enabling host discovery, port scanning, service/OS detection, and scripted vulnerability…
 phaethon/kamene
Network packet and pcap file crafting/sniffing/manipulation/visualization security tool. Originally forked from scapy in 2015 and providing python3…