

spoonmap
 trustedsec/spoonmap
Python wrapper around masscan and nmap for large-scale port discovery, host discovery, banner grabbing, and NSE-based vulnerability scanning across…
defensive-toolsinformation-gatheringnetwork-mapping+7
214
trustedsec/spoonmapPython wrapper around masscan and nmap for large-scale port discovery, host discovery, banner grabbing, and NSE-based vulnerability scanning across…
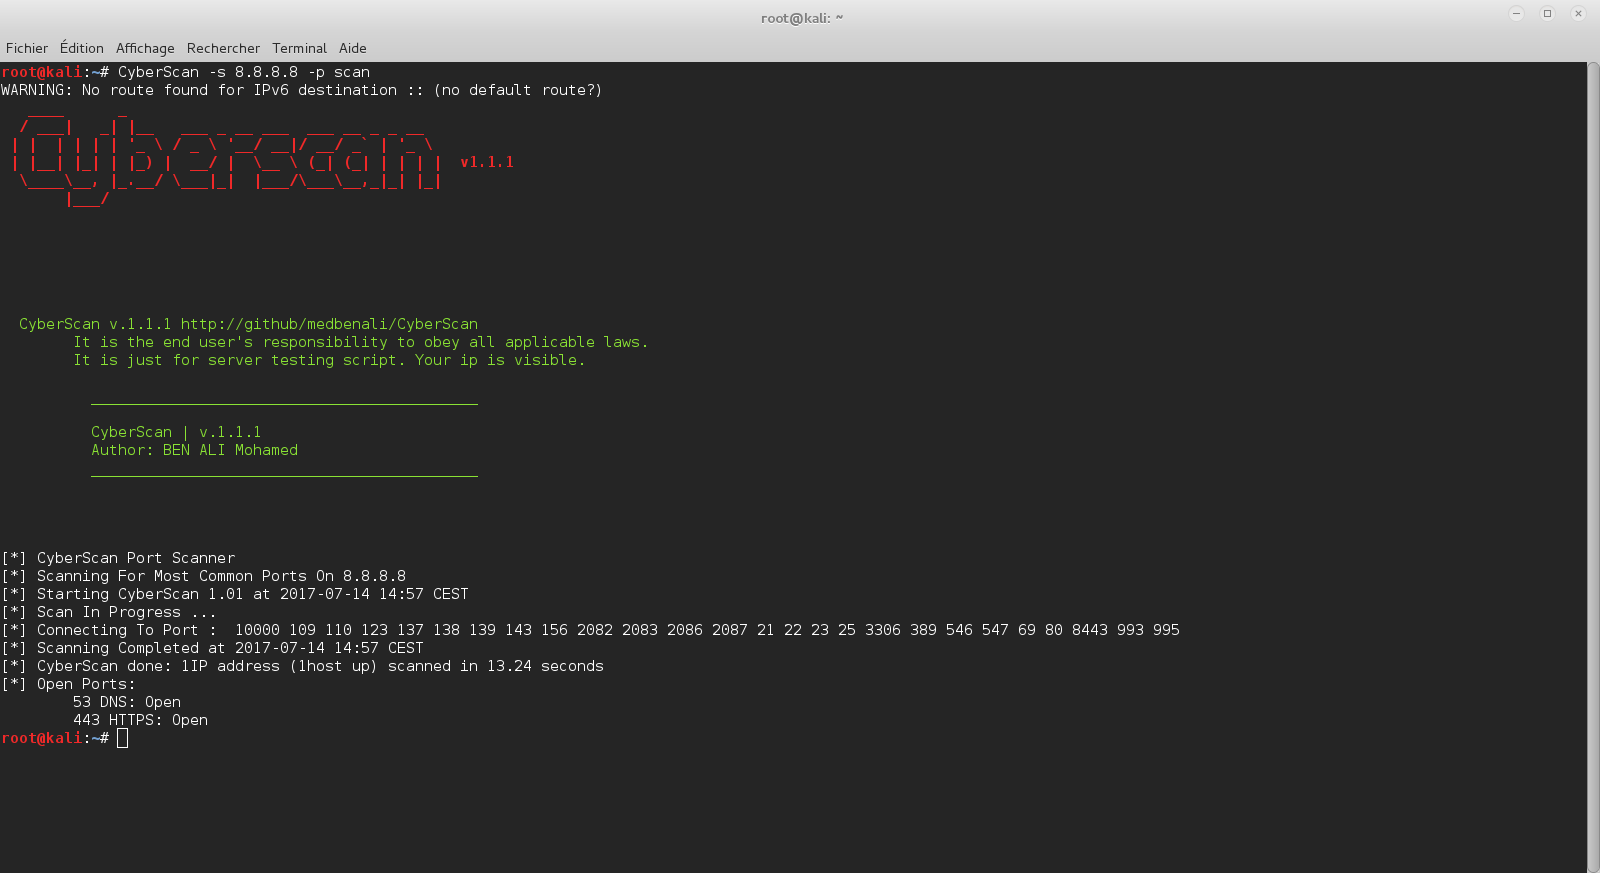 medbenali/cyberscan
Open-source network forensics toolkit for packet analysis, port scanning, host discovery, and IP geolocation. Supports ARP, ICMP, TCP, UDP pings and…
 ullaakut/nmap
Idiomatic Go library for invoking a network scanner binary, enabling host discovery, port scanning, service/OS detection, and scripted vulnerability…
 dedsecinside/torbot
Crawls .onion sites over Tor to collect page titles, hostnames, and link relationships, exporting JSON trees and visualizations for dark web OSINT…
 haishanzheng/cve-2019-0708-generate-hosts
CIDR-based host discovery tool that uses nmap to identify Windows machines with open port 3389 (RDP), reducing target IPs for CVE-2019-0708…
 sakispat/simple-pentesting
An educational Python toolkit for authorized penetration testing: threaded port scanner, subdomain & directory enumeration, banner grabber and host…
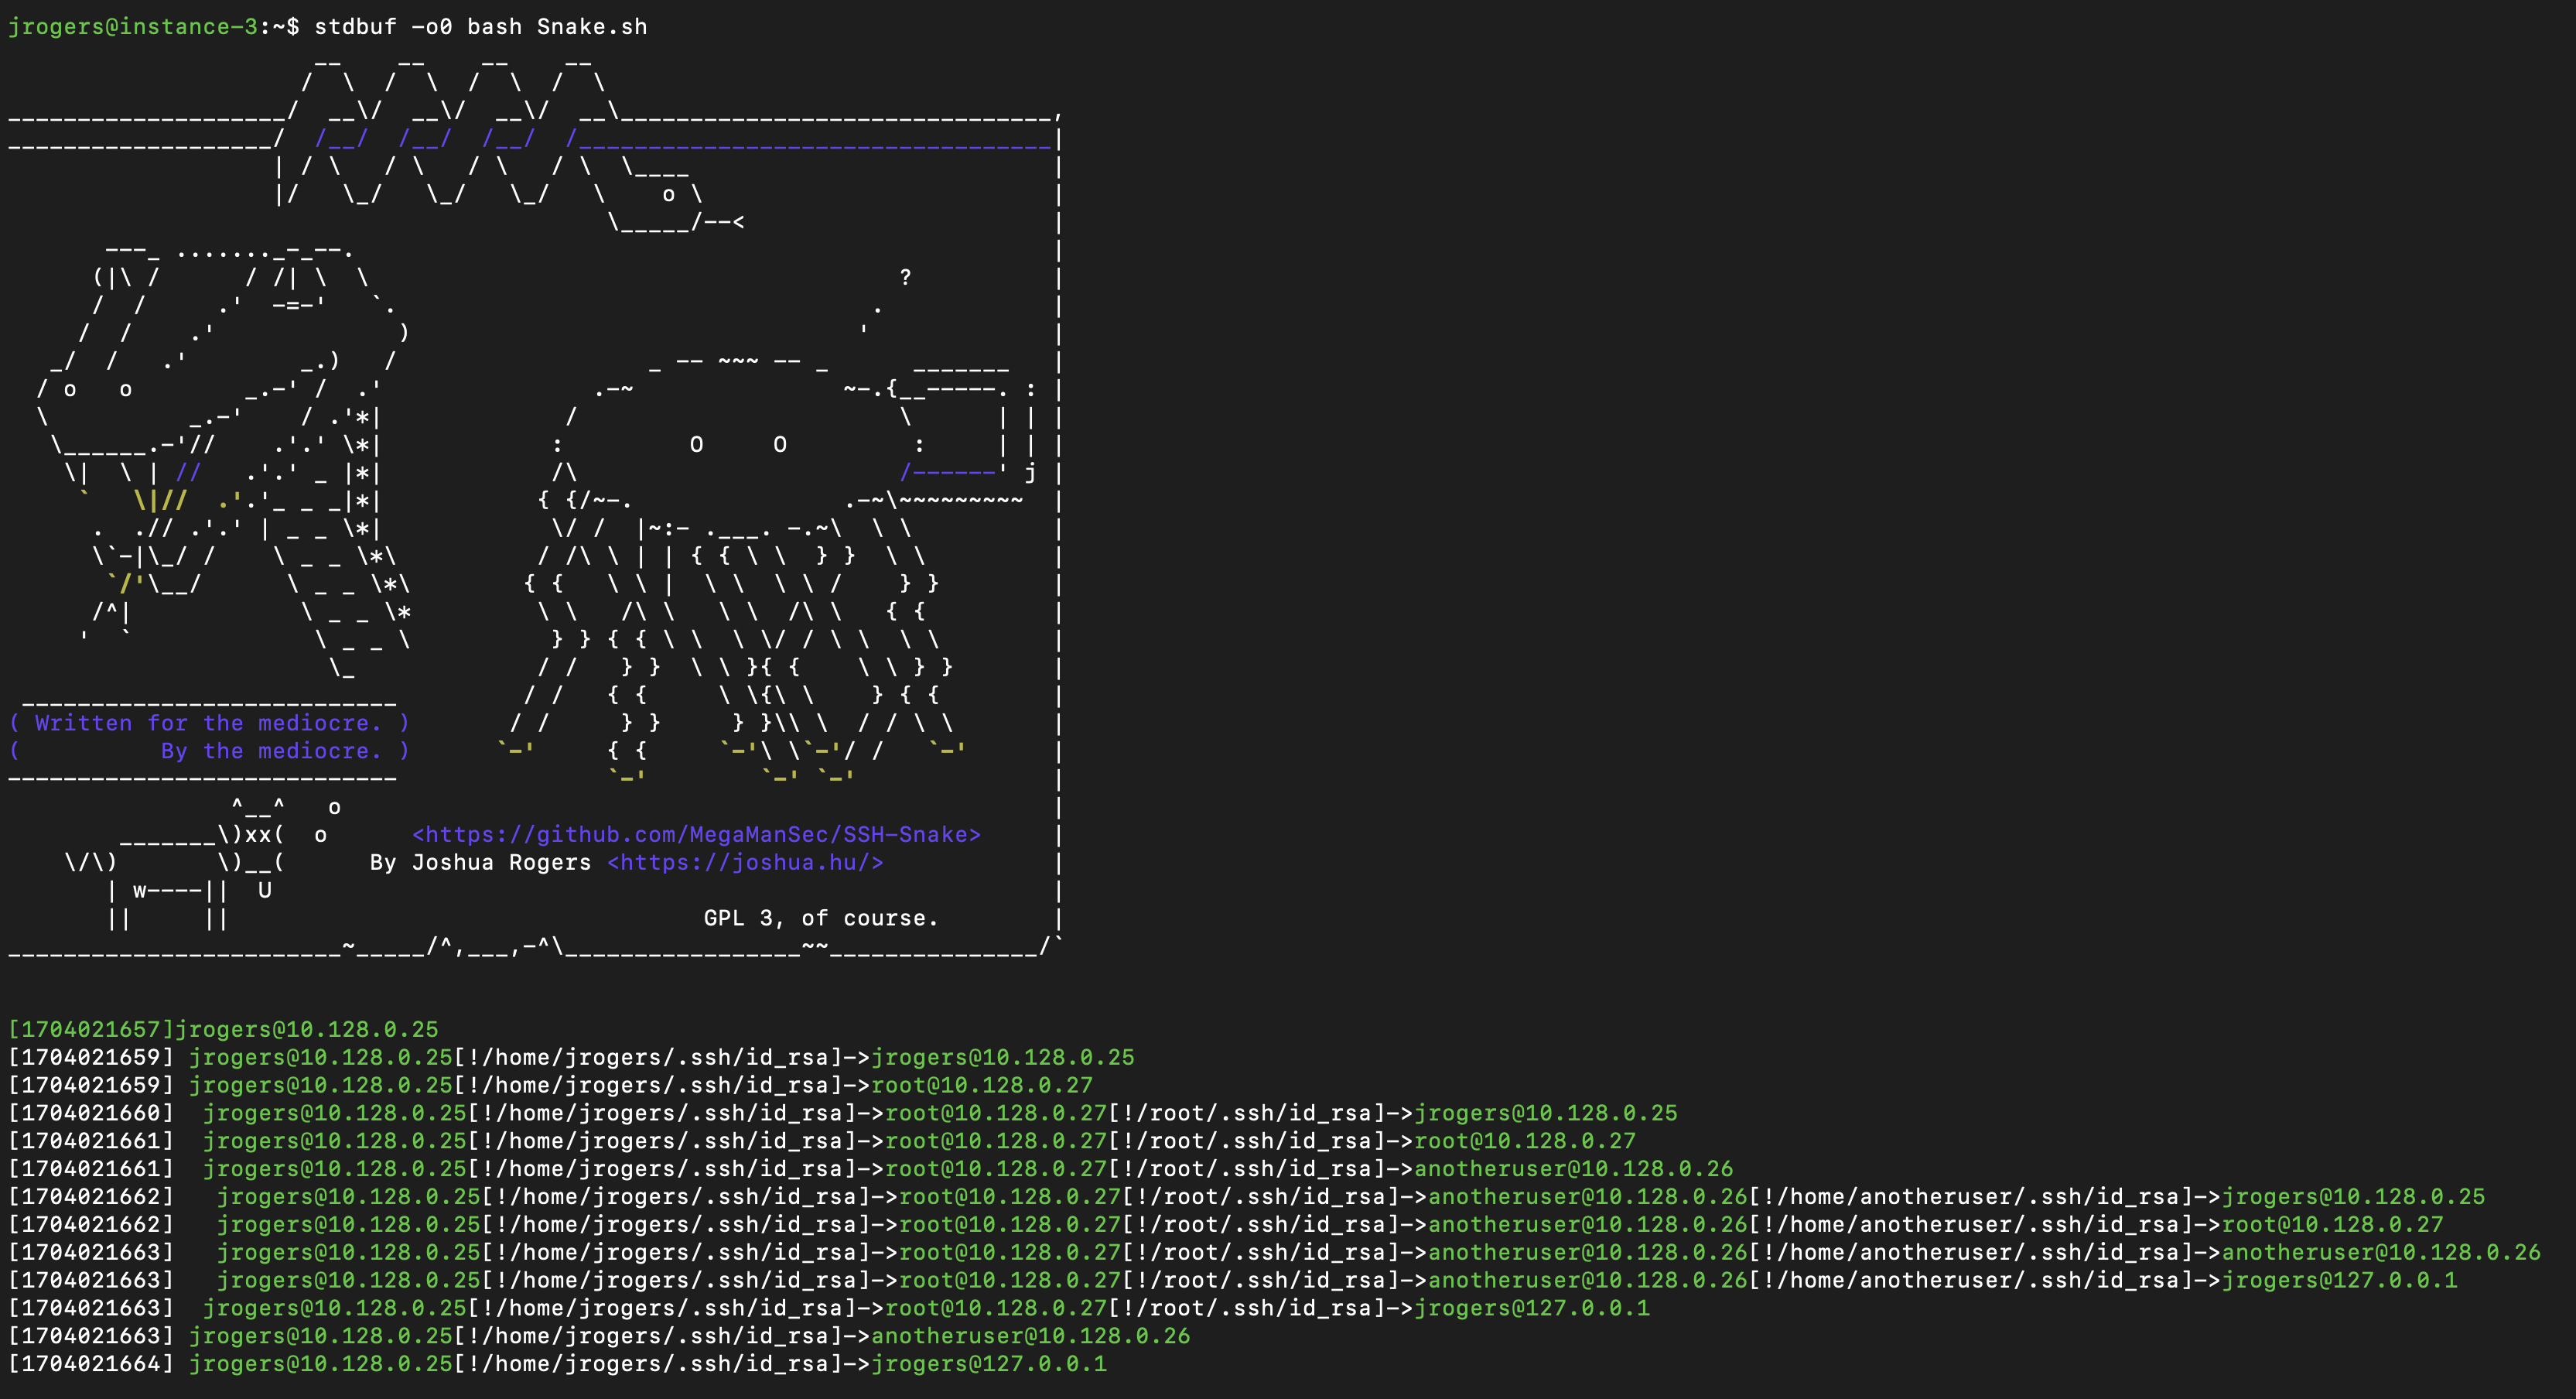 megamansec/ssh-snake
SSH-Snake is a self-propagating, self-replicating, file-less script that automates the post-exploitation task of SSH private key and host discovery.
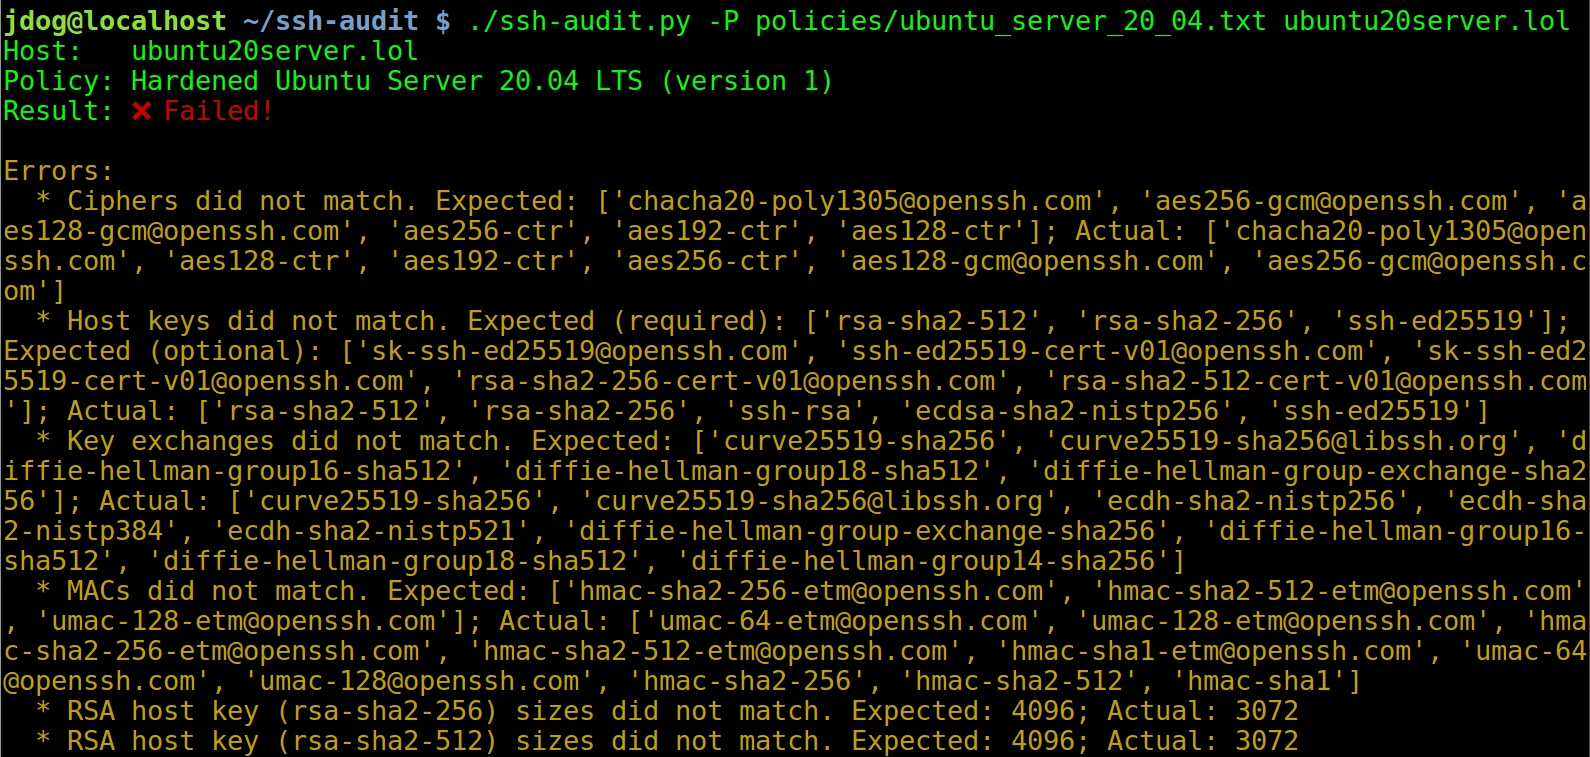 jtesta/ssh-audit
SSH server & client security auditing (banner, key exchange, encryption, mac, compression, compatibility, security, etc)
 serain/netmap.js
Fast browser-based network discovery module
 initroot/cve-2020-6308-poc
PoC CVE-2020-6308
 1n3/sn1per-mcp
MCP server that lets AI assistants drive a self-hosted Sn1per install, running scoped, audited scans and returning findings, ports, subdomains and…
 nurdilin/cve-2018-16706
Or how I turn off my TV via a cronjob
 rhimavanth32-max/metasploitable2-reconnaissance-and-unrealircd-backdoor-exploitation
End-to-end recon and exploitation of a known backdoor (CVE-2010-2075) on Metasploitable2 using Nmap and Metasploit.