

Archived
aquatone
 michenriksen/aquatone
A Tool for Domain Flyovers
information-gatheringnetwork-mappingosint+3
6.0k
 j3ssie/metabigor
OSINT reconnaissance tool for network discovery, subdomain enumeration, IP enrichment, and secret detection via certificate logs, Shodan, and GitHub…
 r3vn/badkarma
network reconnaissance toolkit
 maldevel/intelspy
Perform automated network reconnaissance scans
 divinelabio/argus
The Ultimate Information Gathering Toolkit
 knowledge-wisdom-understanding/recon
Enumerate a target Based off of Nmap Results
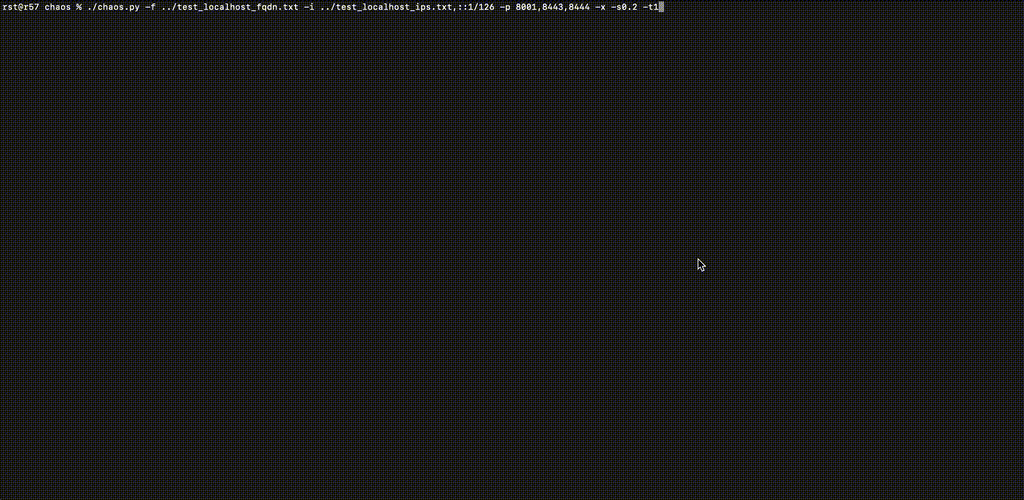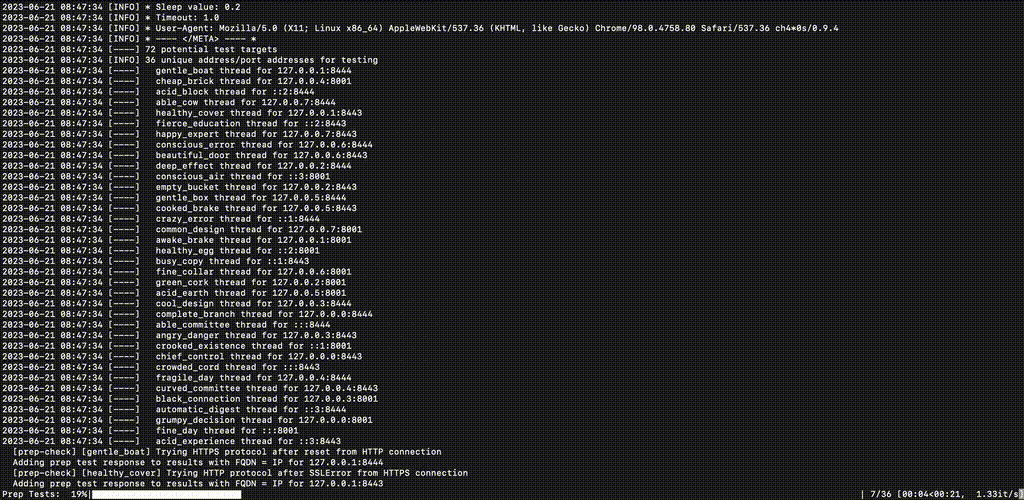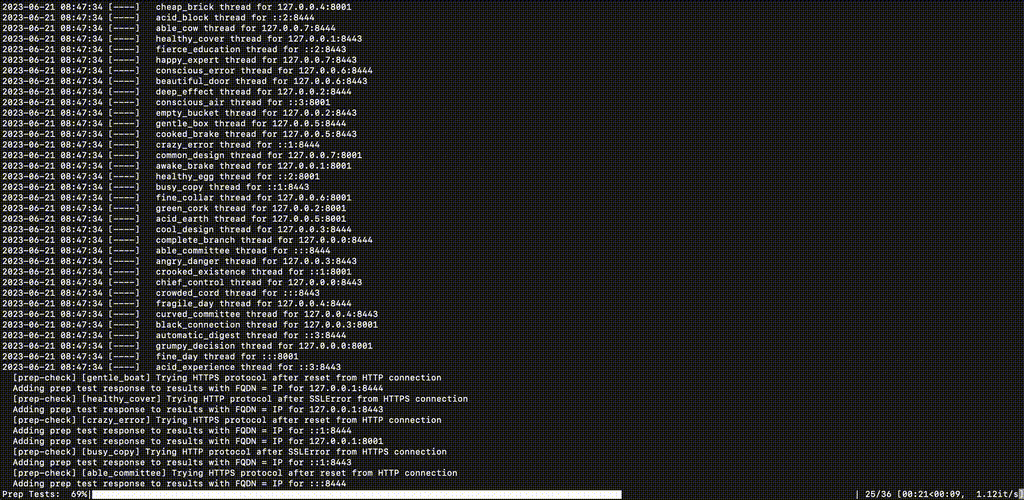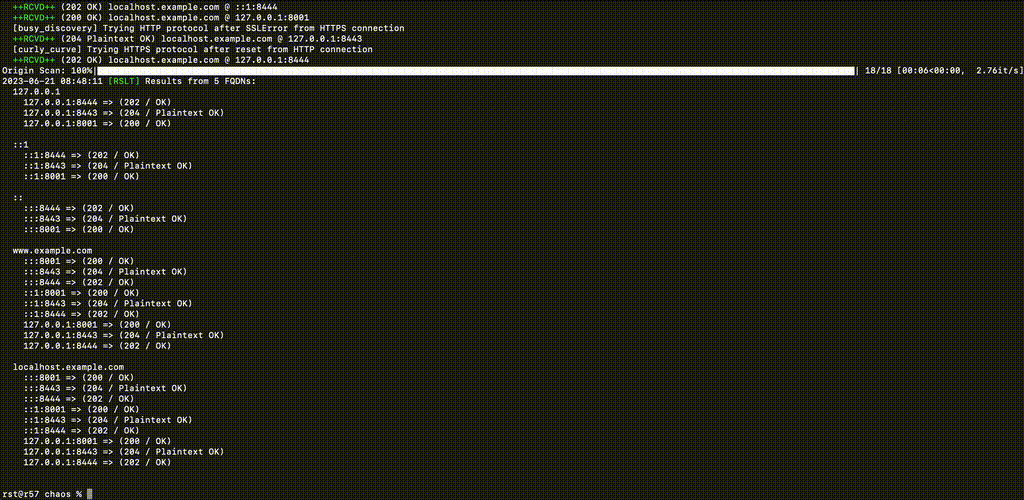 r57-labs/chaos
Origin IP scanning utility developed with ChatGPT
 qyvora/qyvora-anansi
Terminal-first attack surface intelligence engine. Built for speed, portability, and raw technical signal.
 escape-technologies/awesome-attack-surface-management
A curated collection of tools, techniques, frameworks, and learning resources focused on Attack Surface Management (ASM).
 enenumxela/ps.sh
A bash script that automates port scanning on specified target host(s). The aim of the scripts is reducing scan time, increasing scan efficiency and…

 vqkro/ultrasploiter
A single binary that folds a port scanner, the full Exploit-DB index (47k entries) and runnable exploit modules into one tool. Written in Rust, runs…
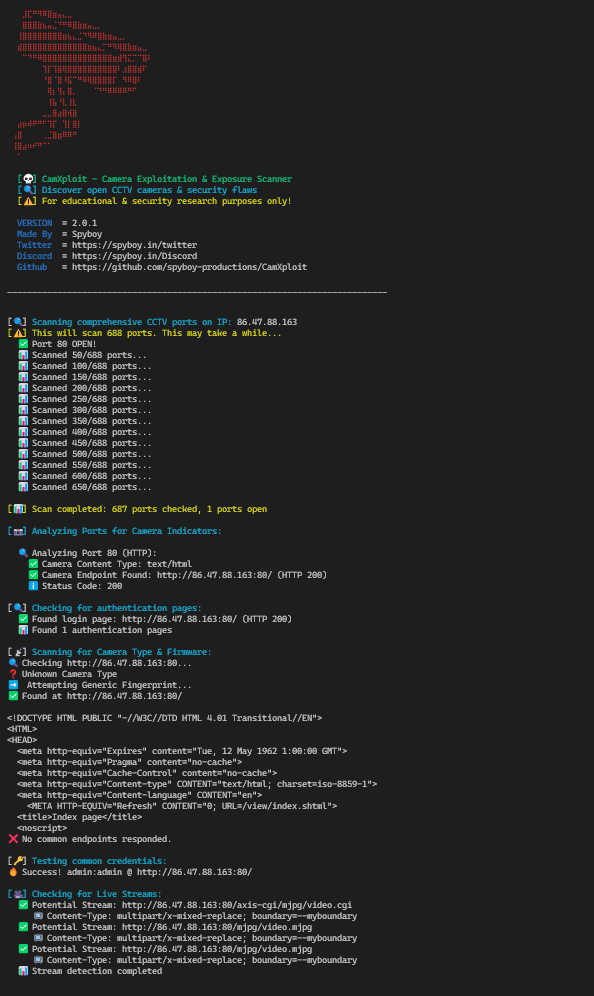 spyboy-productions/camxploit
Security reconnaissance and assessment tool for identifying potentially exposed IP cameras by analyzing open ports, service configurations, and…
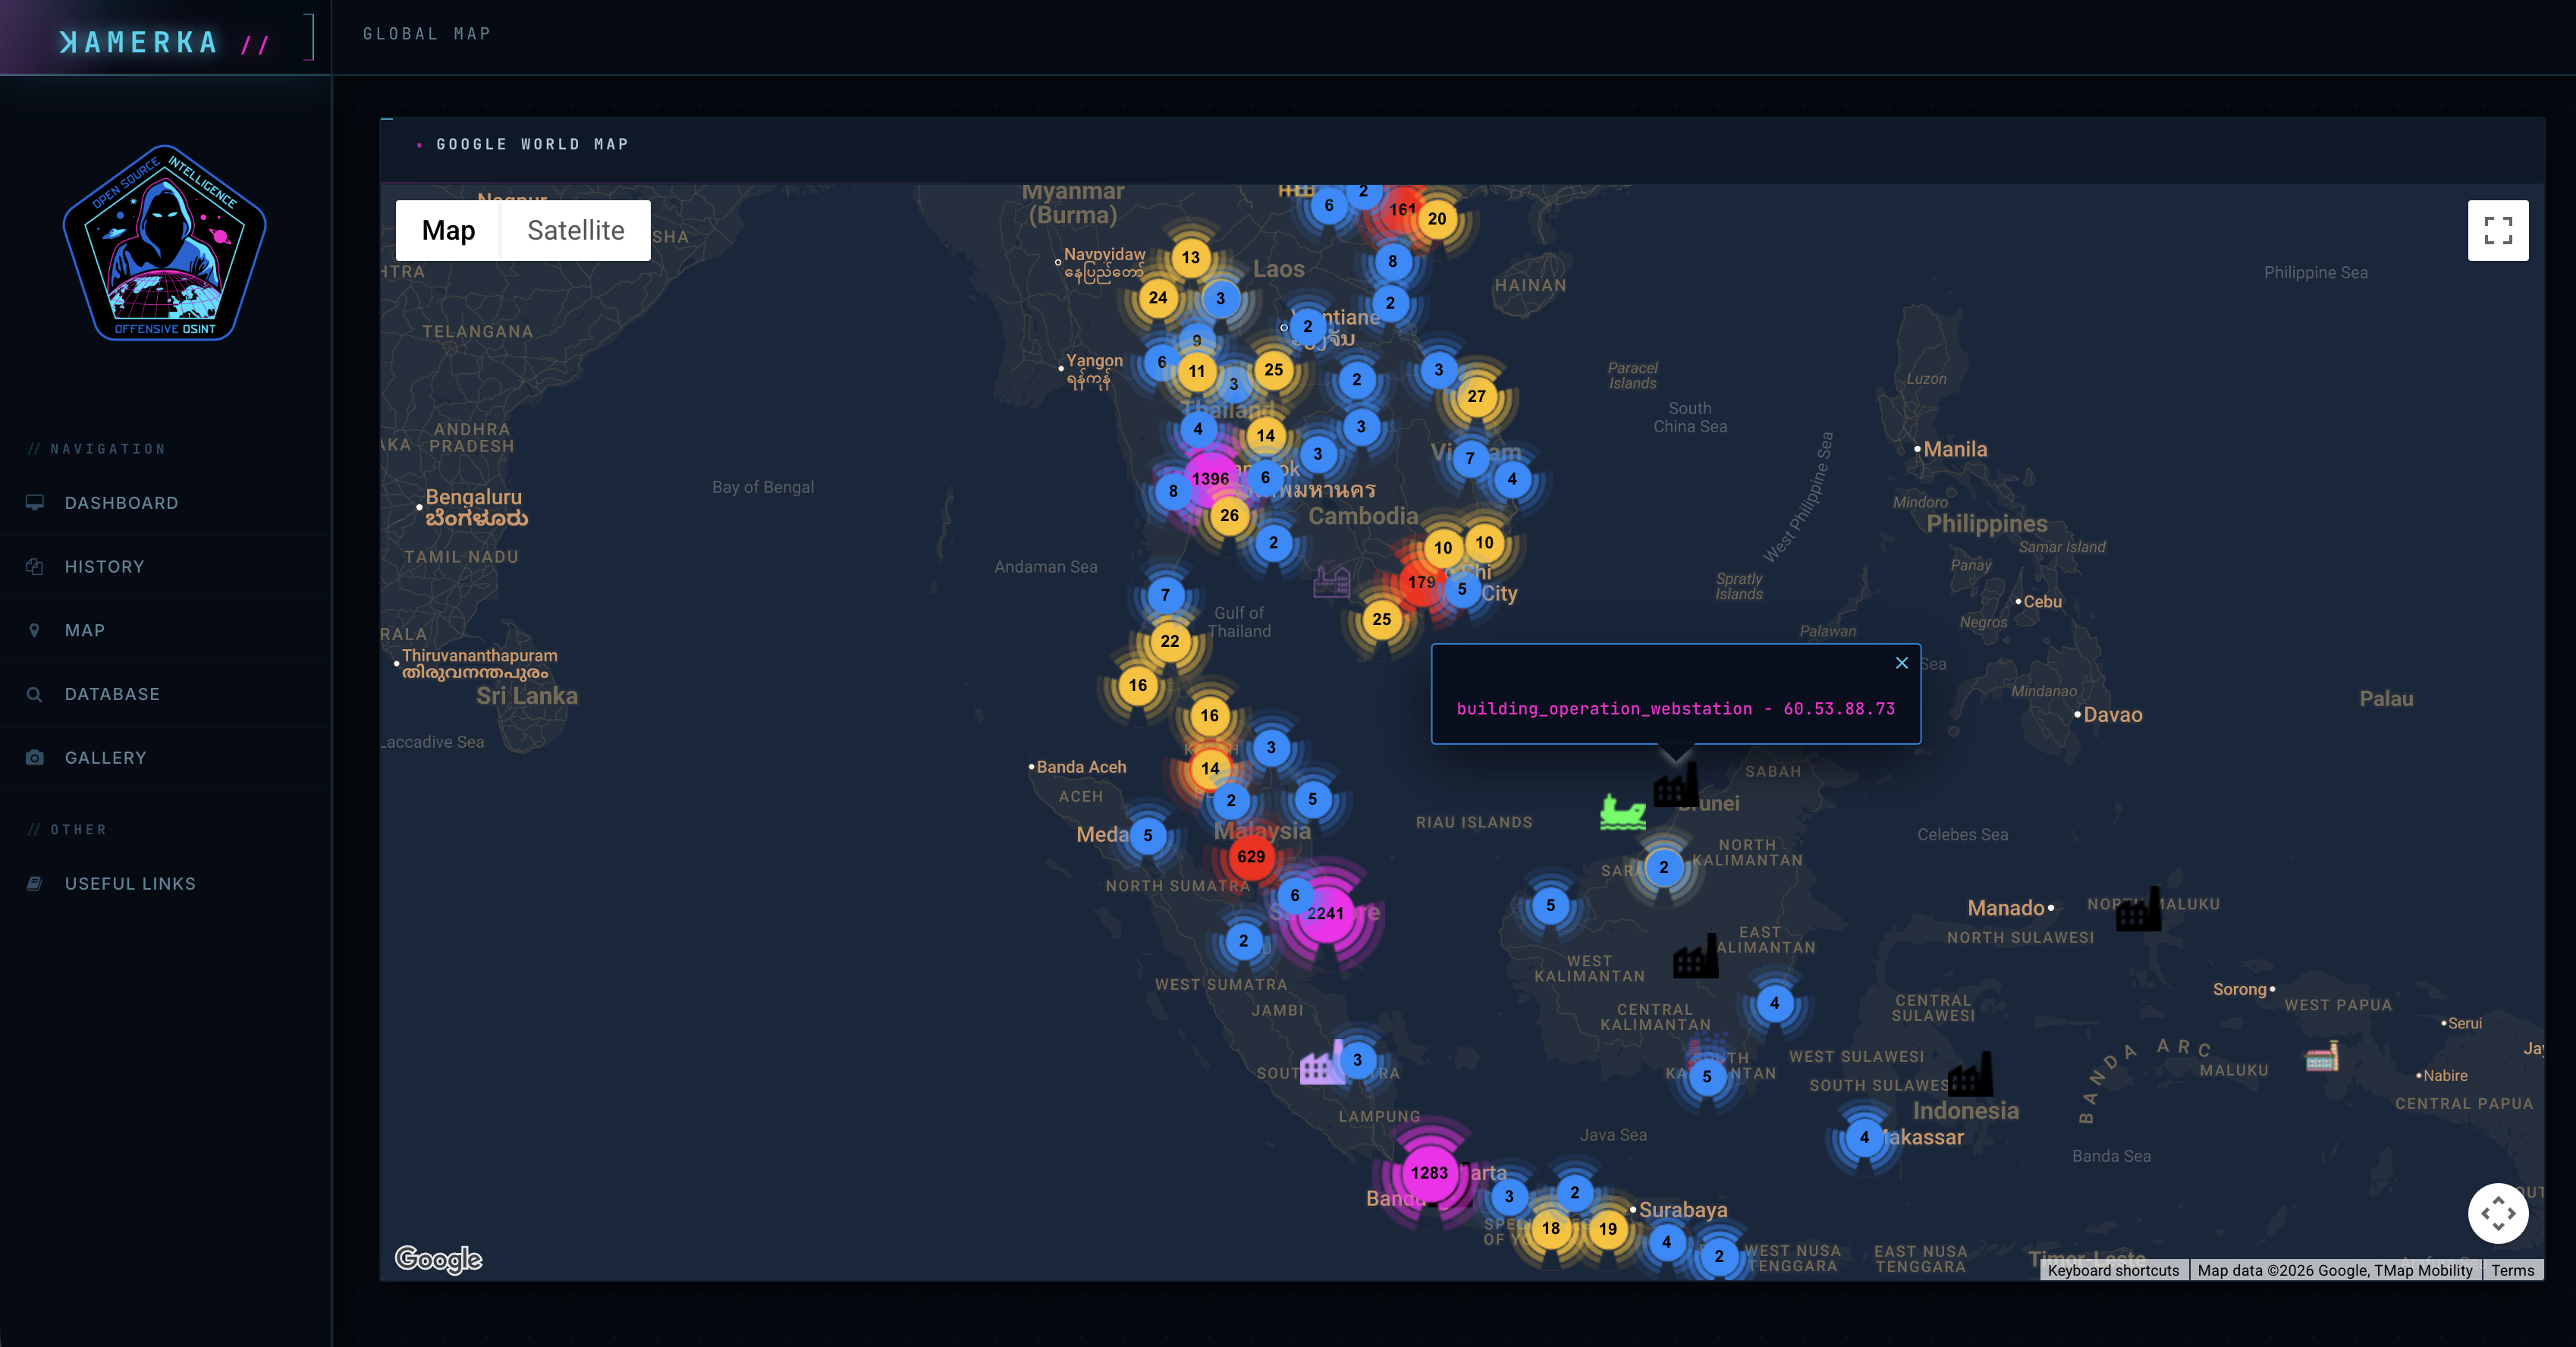 woj-ciech/kamerka-gui
Ultimate Internet of Things/Industrial Control Systems reconnaissance tool.
 pielco11/fav-up
Shodan-powered tool to discover real IP addresses behind Cloudflare by hashing favicon icons using MurmurHash3, enabling origin server identification…
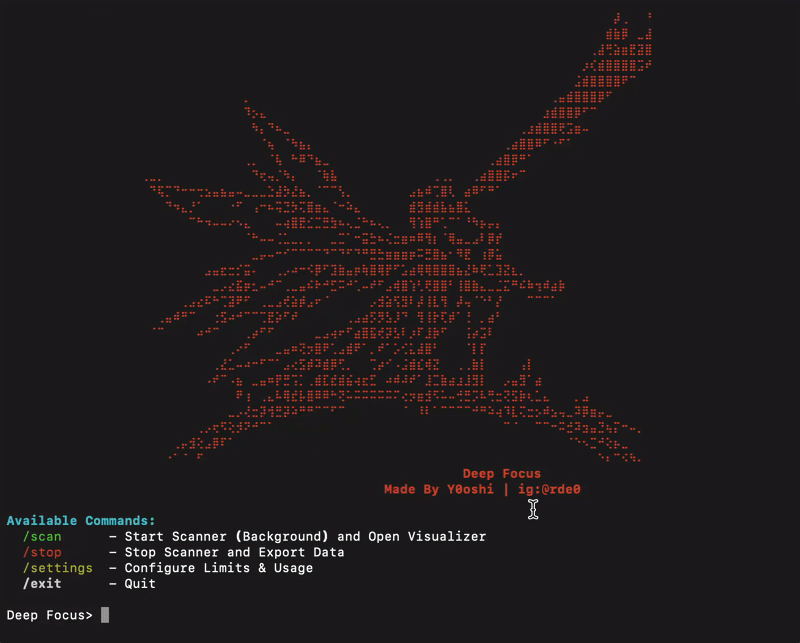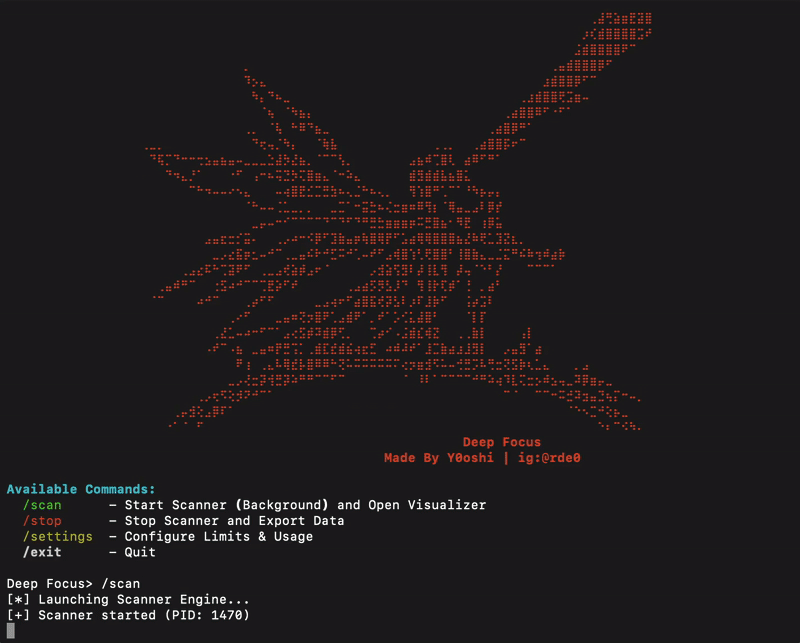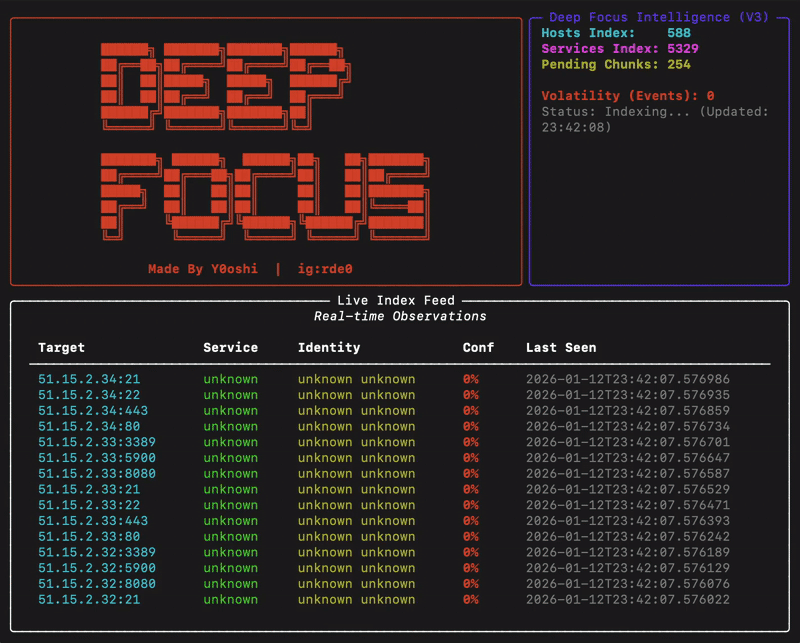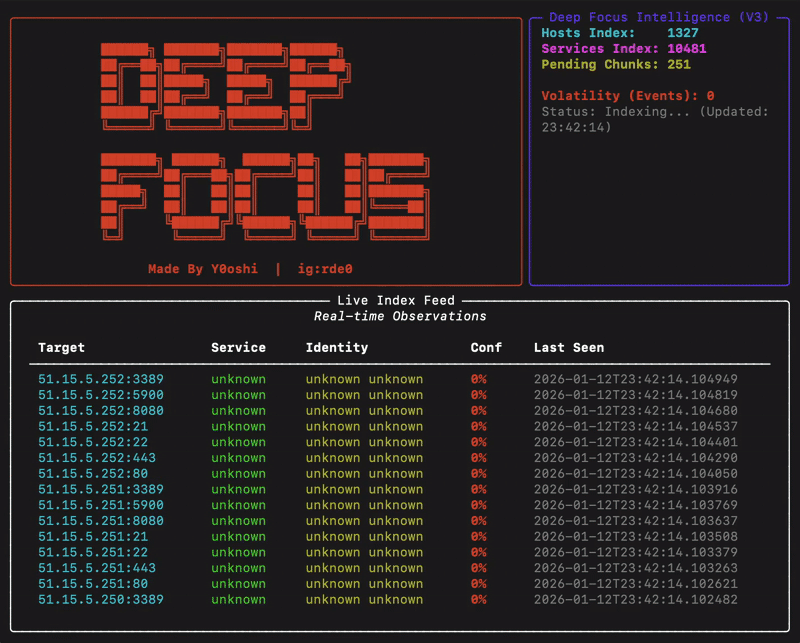 y0oshi/project-deep-focus
Asynchronous network reconnaissance engine for large-scale service discovery and fingerprinting. Identifies unsecured services (RTSP cameras, VNC,…
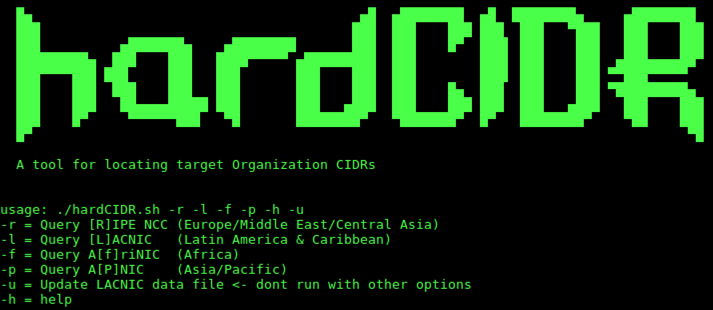 trustedsec/hardcidr
Bash script for passive reconnaissance that queries RIRs and BGP route servers to discover target organization netblocks, ASNs, and CIDR ranges…
 boydhacks/ntlmscout
Unauthenticated NTLM endpoint reconnaissance tool that decodes Type-2 challenges across HTTP, SMB, MSSQL, SMTP, IMAP, POP3, NNTP, LDAP, and RDP to…
 jhaddix/lazyrecon
This script is intended to automate your reconnaissance process in an organized fashion