

ehids-agent
 gojue/ehids-agent
A Linux Host-based Intrusion Detection System based on eBPF.
container-escapedefensive-toolsdns-analysis+5
455
gojue/ehids-agentA Linux Host-based Intrusion Detection System based on eBPF.
 p0dalirius/sharehound
A python tool to map the access rights of network shares into a BloodHound OpenGraphs easily
 zeronetworks/bloodhound-tools
Collection of tools that reflect the network dimension into Bloodhound's data
 evilsocket/spycast
A crossplatform mDNS enumeration tool.
 alechilczenko/kimi
Attack Surface Discovery tool built on a microservice approach, utilizing multi-threading for fast, internet-scale asset indexing
 joasasantos/php2shell-scanner
Non-destructive scanner for CVE-2026-109618 / CVE-2026-109619 (PHP core RCE). Subdomain recon via crt.sh + subfinder, robust banner grabbing,…
 dviros/excalibur
Excalibur is an Eternalblue exploit payload based "Powershell" for the Bashbunny project.
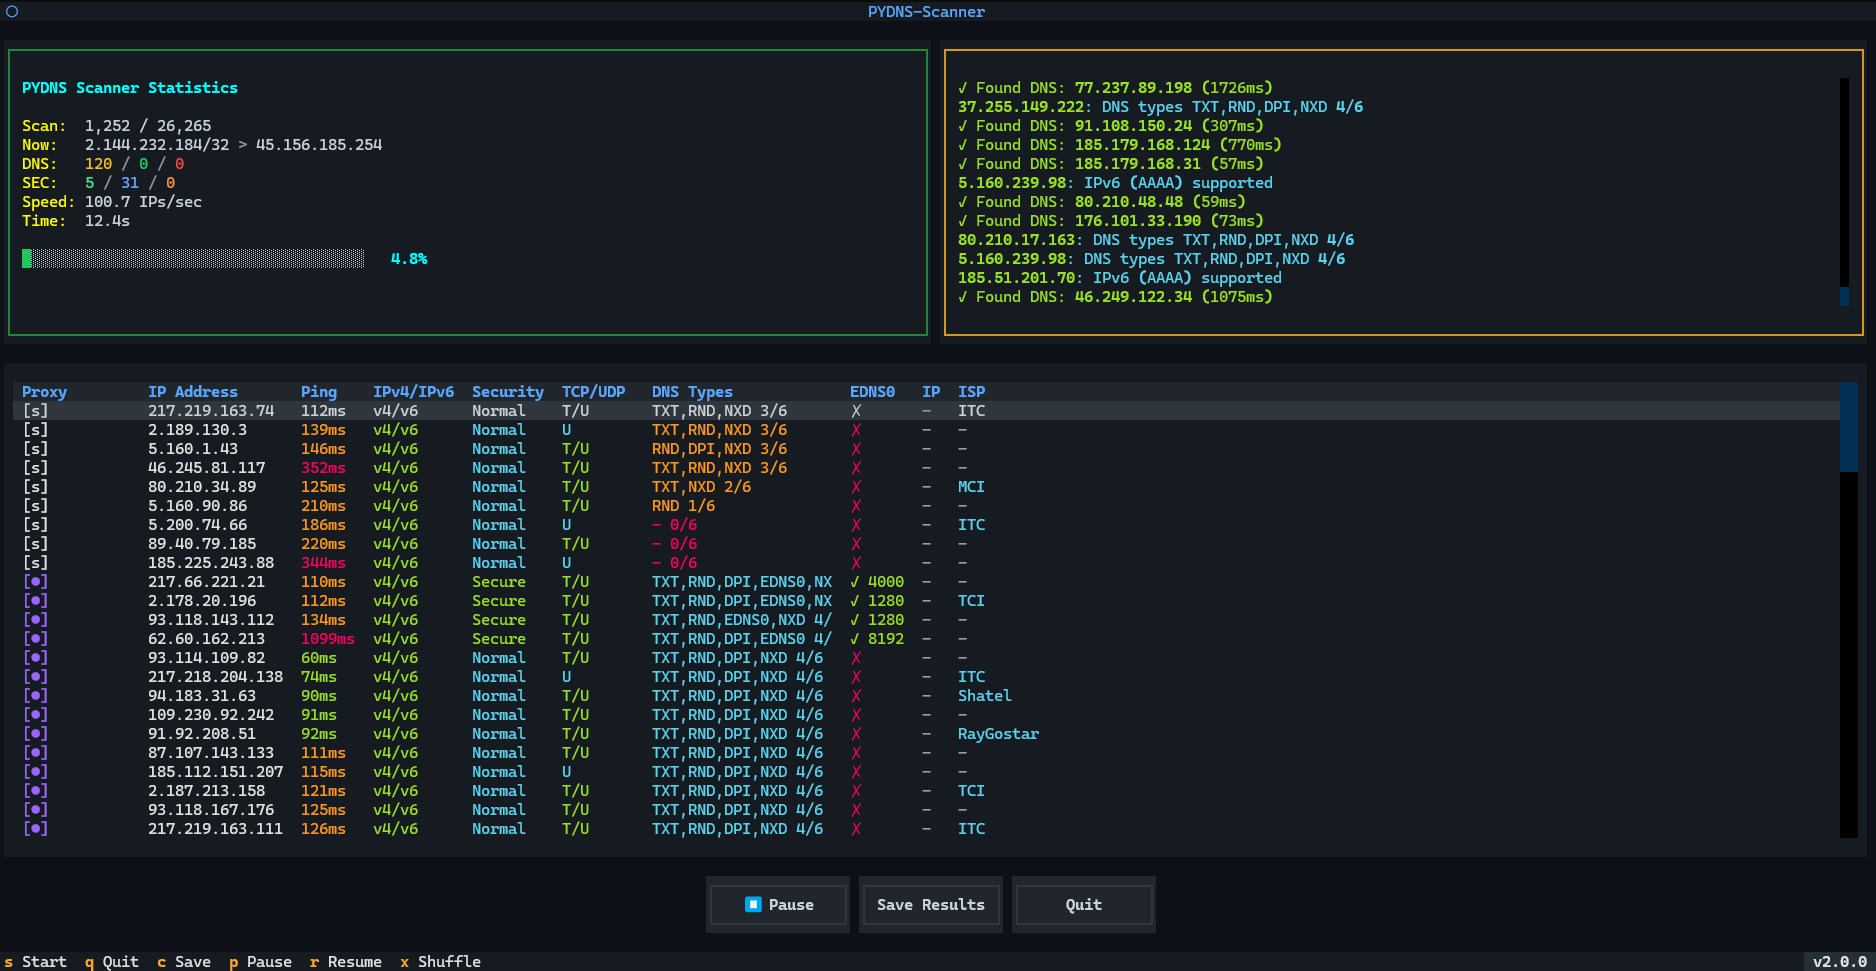 xullexer/pydns-scanner
A modern, high-performance DNS scanner with a beautiful Terminal User Interface (TUI) built with Textual. This tool can scan millions of IP addresses…
 mubix/netview
Netview enumerates systems using WinAPI calls
 postmodern/ruby-nmap
A Ruby interface to nmap, the exploration tool and security / port scanner. Allows automating nmap and parsing nmap XML files.
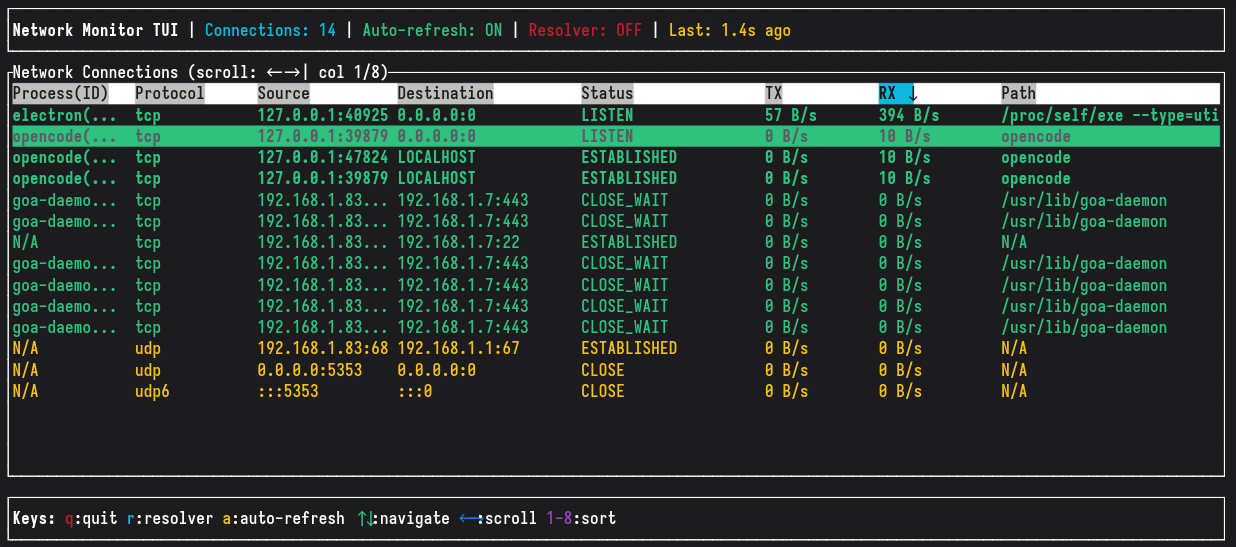 grigio/network-monitor
A real-time network connection monitoring tool built with Rust and GTK4, displaying active connections with live I/O statistics in a modern graphical…
 rickdejager/cupshax
Quick proof-of-concept for recent CUPS exploit enabling remote code execution via PPD injection and DNS-SD printer discovery. Executes arbitrary…
 abdulgaphy/r3con1z3r
R3con1z3r is a lightweight Web information gathering tool with an intuitive features written in python. it provides a powerful environment in which…
 nccgroup/port-scan-automation
Automate NMAP Scans and Generate Custom Nessus Policies Automatically
 sigploiter/gtscan
The Nmap Scanner for Telco
 tijldeneut/icssecurityscripts
Python scripts for security assessment of industrial PLCs: scanning, enumeration, control, and exploitation of Beckhoff, Siemens, Schneider,…
 sfan5/fi6s
IPv6 port scanner designed to be fast, aimed at Internet scanning and discovery
 zmap/zannotate
Utility for annotating Internet datasets with contextual metadata (e.g., origin AS, MaxMind GeoIP2, reverse DNS, and WHOIS)