

Argus
 divinelabio/argus
The Ultimate Information Gathering Toolkit
crawlerdns-subdomain-enumerationemail-harvesting+8
divinelabio/argusThe Ultimate Information Gathering Toolkit
 wattocyber/cantina
OSCP-legal network recon orchestrator for port discovery, service classification, and enum-only plugin dispatch across HTTP, SMB, FTP, SNMP, SSH, and…
 jhaddix/awsscrape
A tool to scrape the AWS ranges looking for a keyword in SSL certificate data.
 scramblr/rf-chaos
RF CHAOS is an Android App That Is Designed To Cause Chaos via All RF Adapters Possible - Enjoy!
 nccgroup/nlist
An nmap script to produce target lists for use with various tools.
 nccgroup/ps2
A port scanner written purely in PowerShell.
 jenderal92/reverse-ip-new-api
This tool is used to perform reverse IP lookups— searching for all domains hosted on one IP address.
 cappricio-securities/ghostrecon
gh0str3con is a All in one cloud based web Recon tool.
 nccgroup/sniffle
Bluetooth 5 and 4.x LE sniffer for TI CC1352/CC26x2 hardware with support for extended advertising, all PHY modes, MAC/RSSI filtering, and PCAP…
 bettercap/bettercap
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
 qruiqai/leakish
Browser privacy-leak detector — eight detection modules, risk scoring, and per-account history, all in your browser.
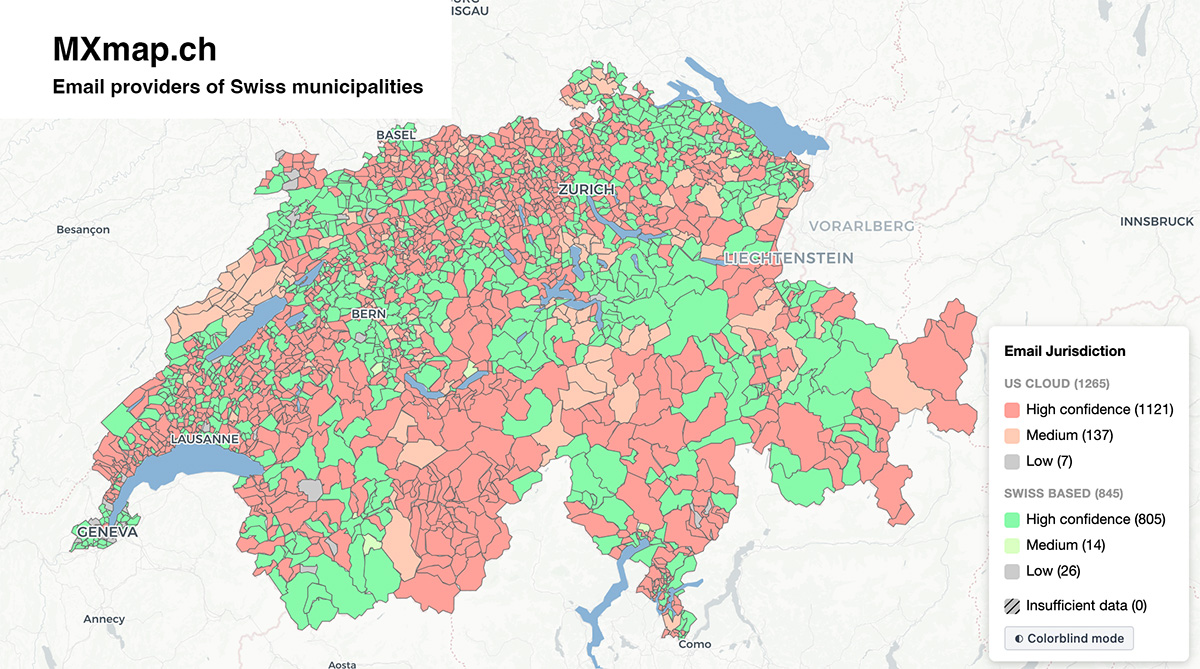 davidhuser/mxmap
Automated pipeline that resolves Swiss municipality domains, scrapes websites for email addresses, and classifies email providers via MX, SPF, DKIM,…
 eldraco/domain_analyzer
Analyze the security of any domain by finding all the information possible. Made in python.
 reddyyz/astsu
A network scanner tool, developed in Python 3 using scapy.
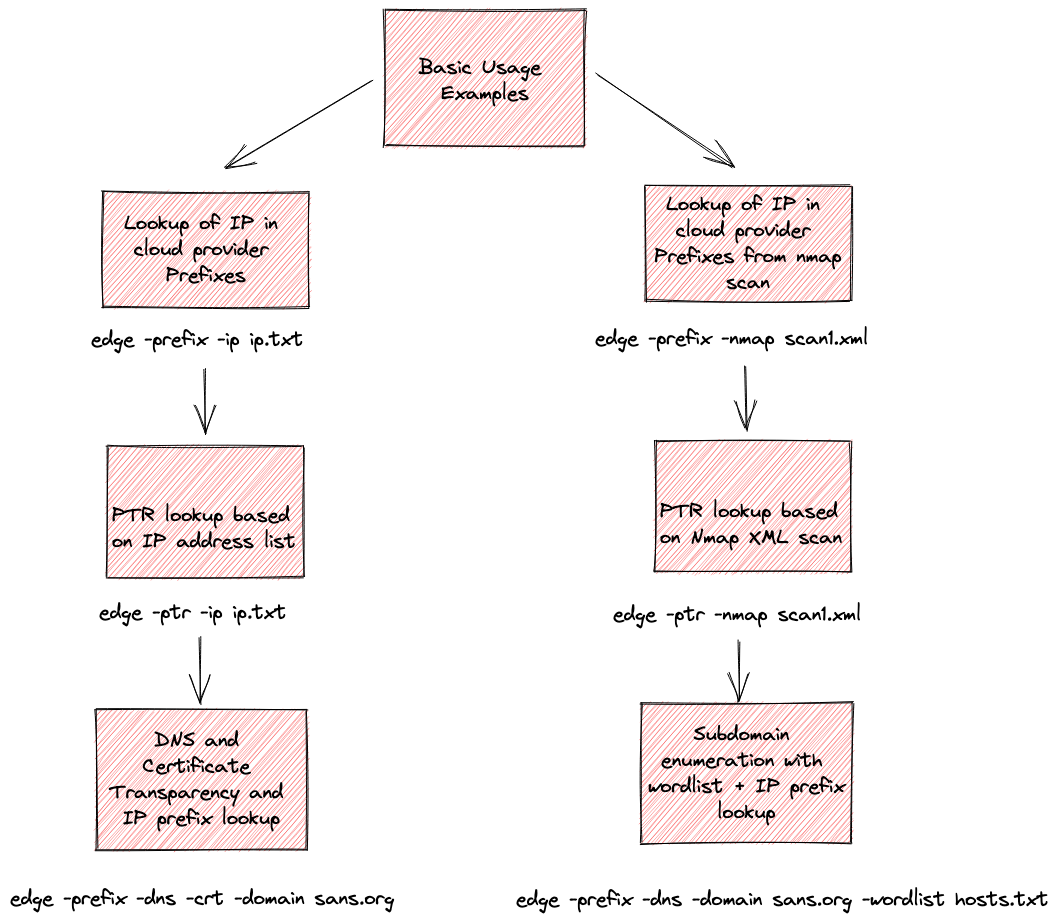 iknowjason/edge
Whois for the Cloud: Recon tool for cloud provider attribution. Supports AWS, Azure, Google, Cloudflare, and Digital Ocean.
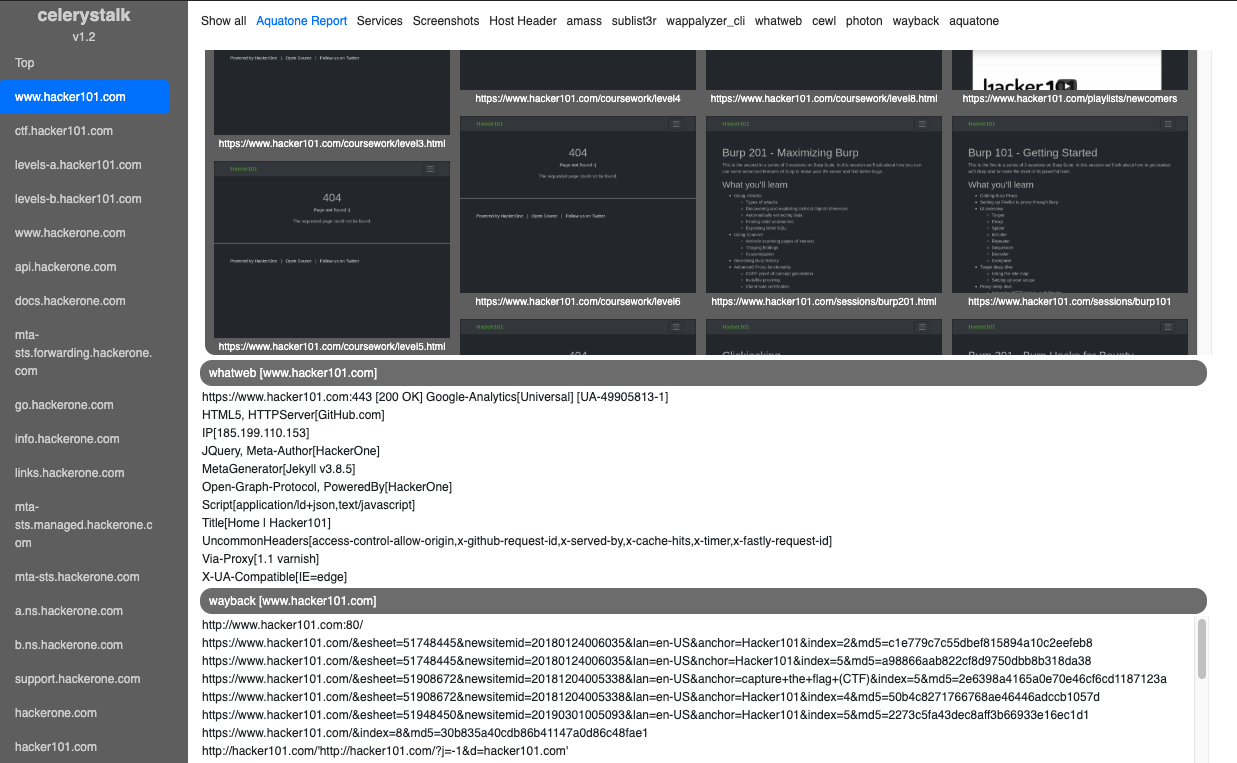 sethsec/celerystalk
An asynchronous enumeration & vulnerability scanner. Run all the tools on all the hosts.