
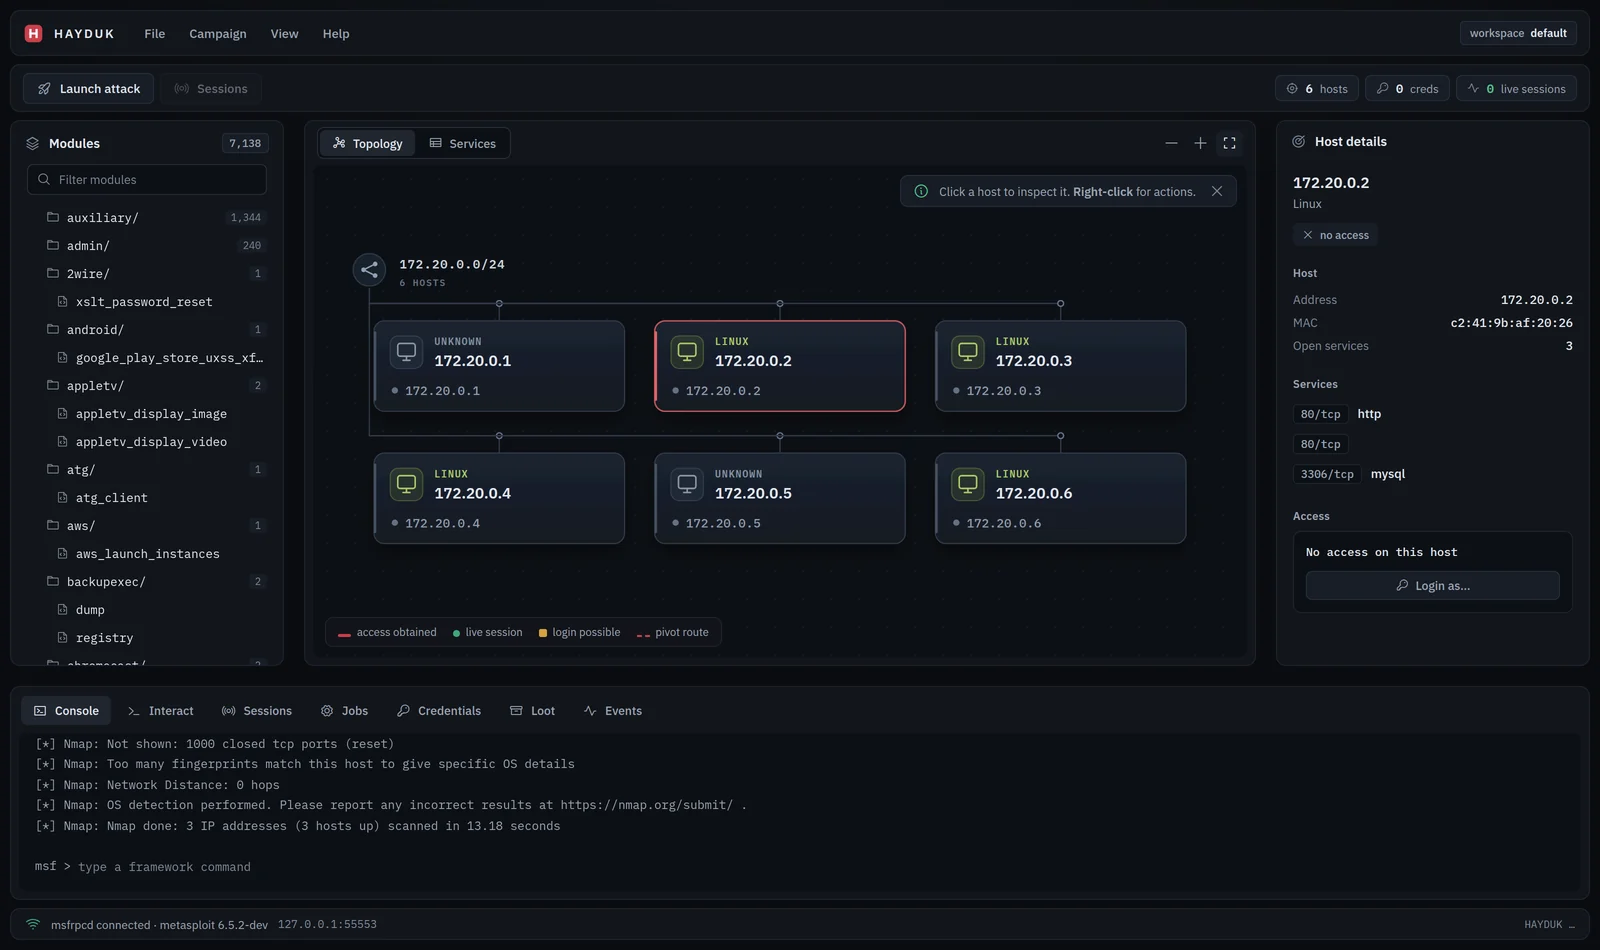
hayduk
 jolovicdev/hayduk
Graphical attack management console for Metasploit: the lineage of Armitage as a single Go binary with a browser UI. Live network topology, campaign…
exploit-frameworksnetwork-mappingpenetration-testing-frameworks+3
6
jolovicdev/haydukGraphical attack management console for Metasploit: the lineage of Armitage as a single Go binary with a browser UI. Live network topology, campaign…
 sdnewhop/sdwan-harvester
🌐 Automatically enumerate and fingerprint SD-WAN nodes on the internet
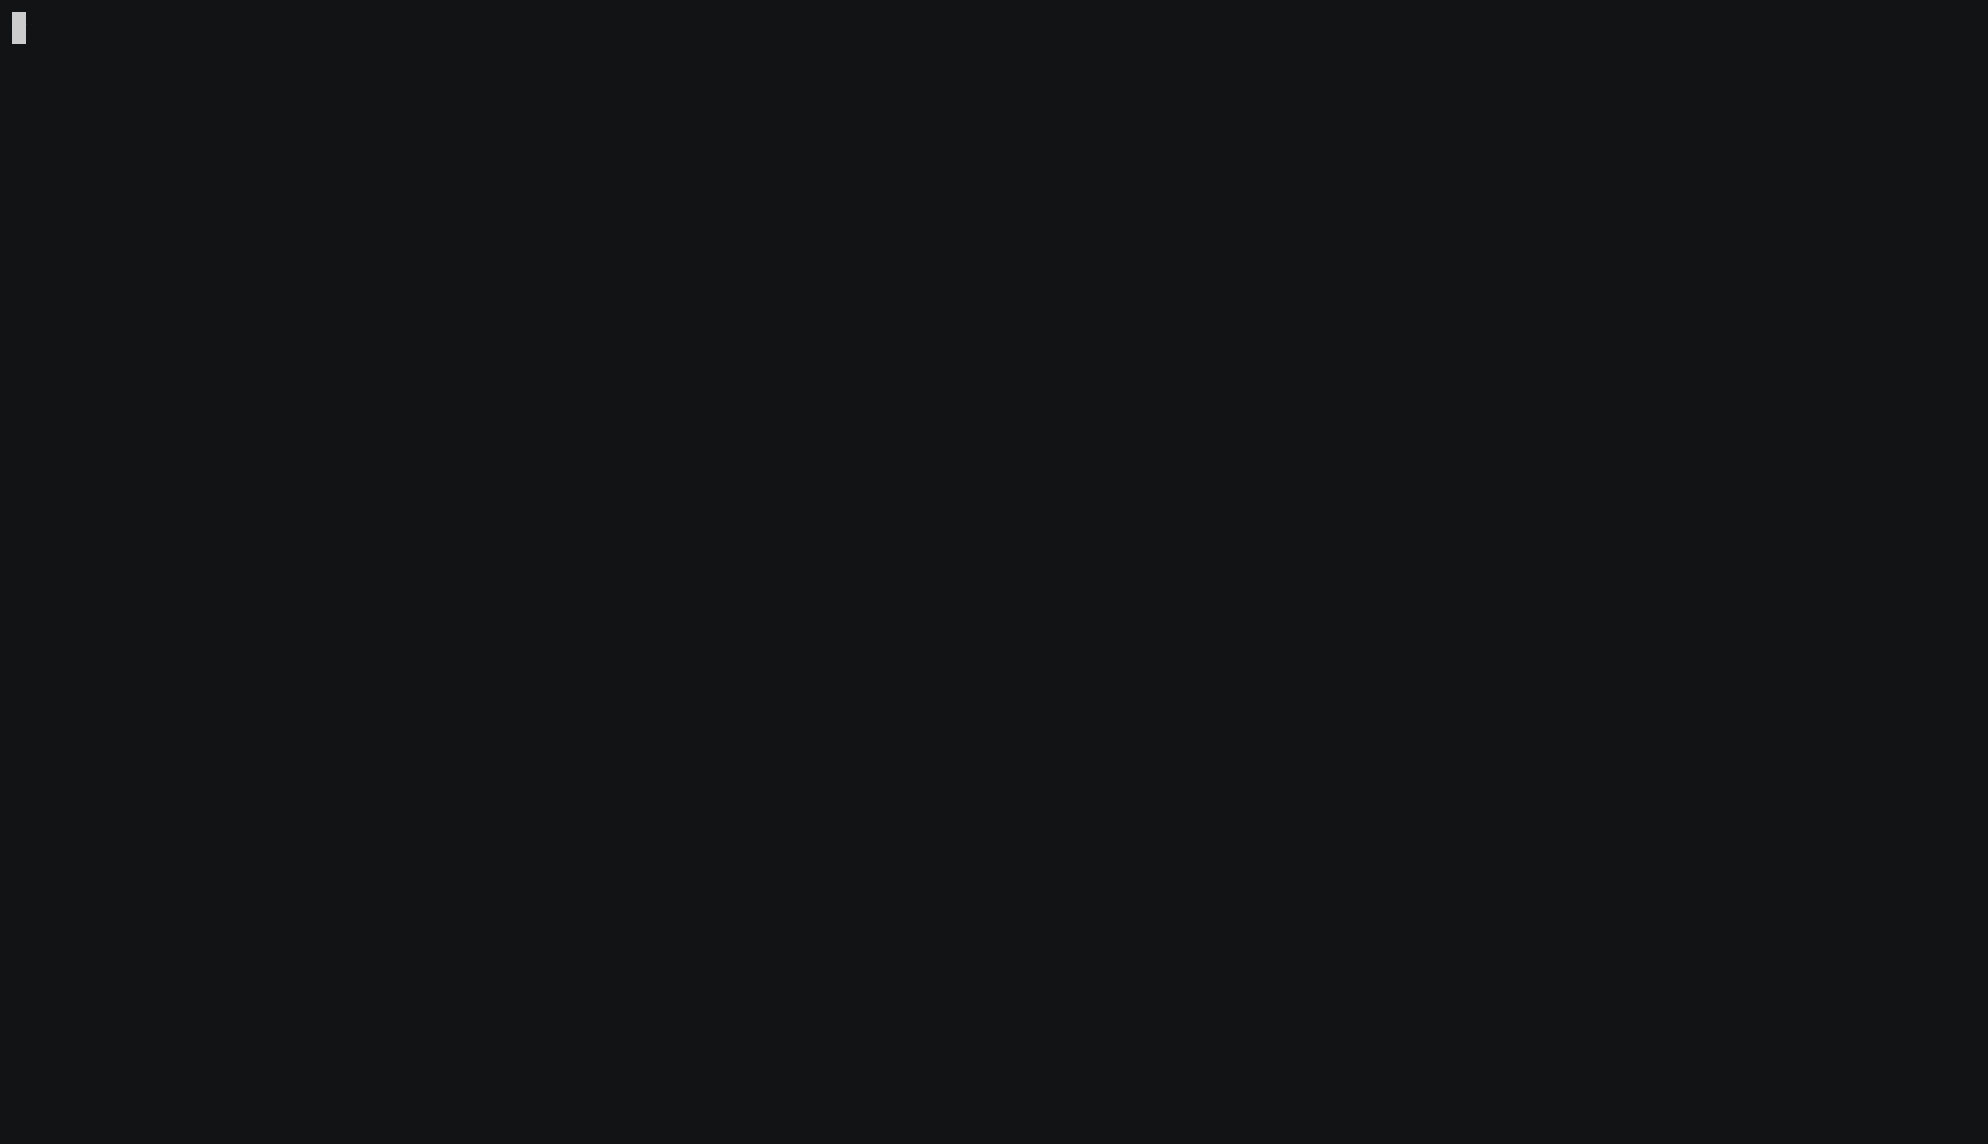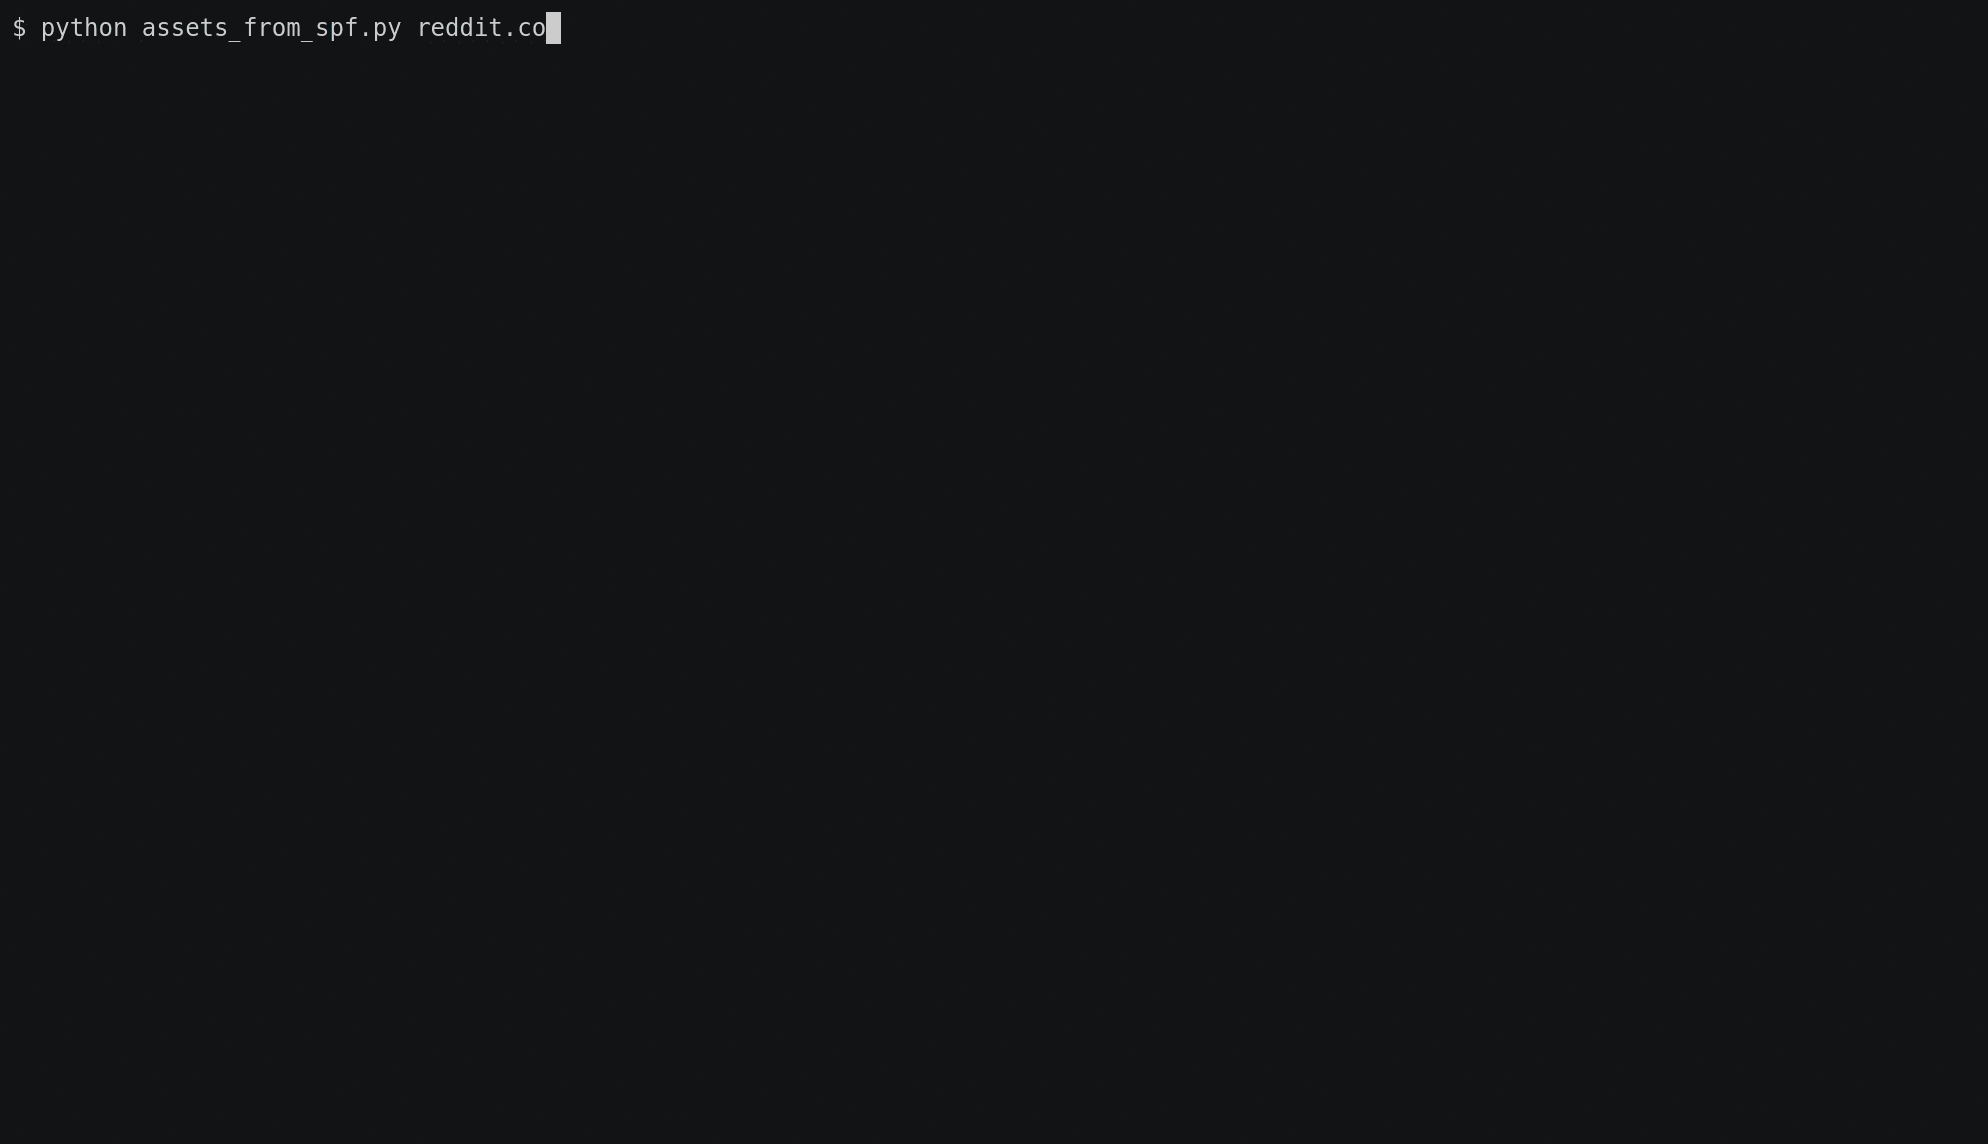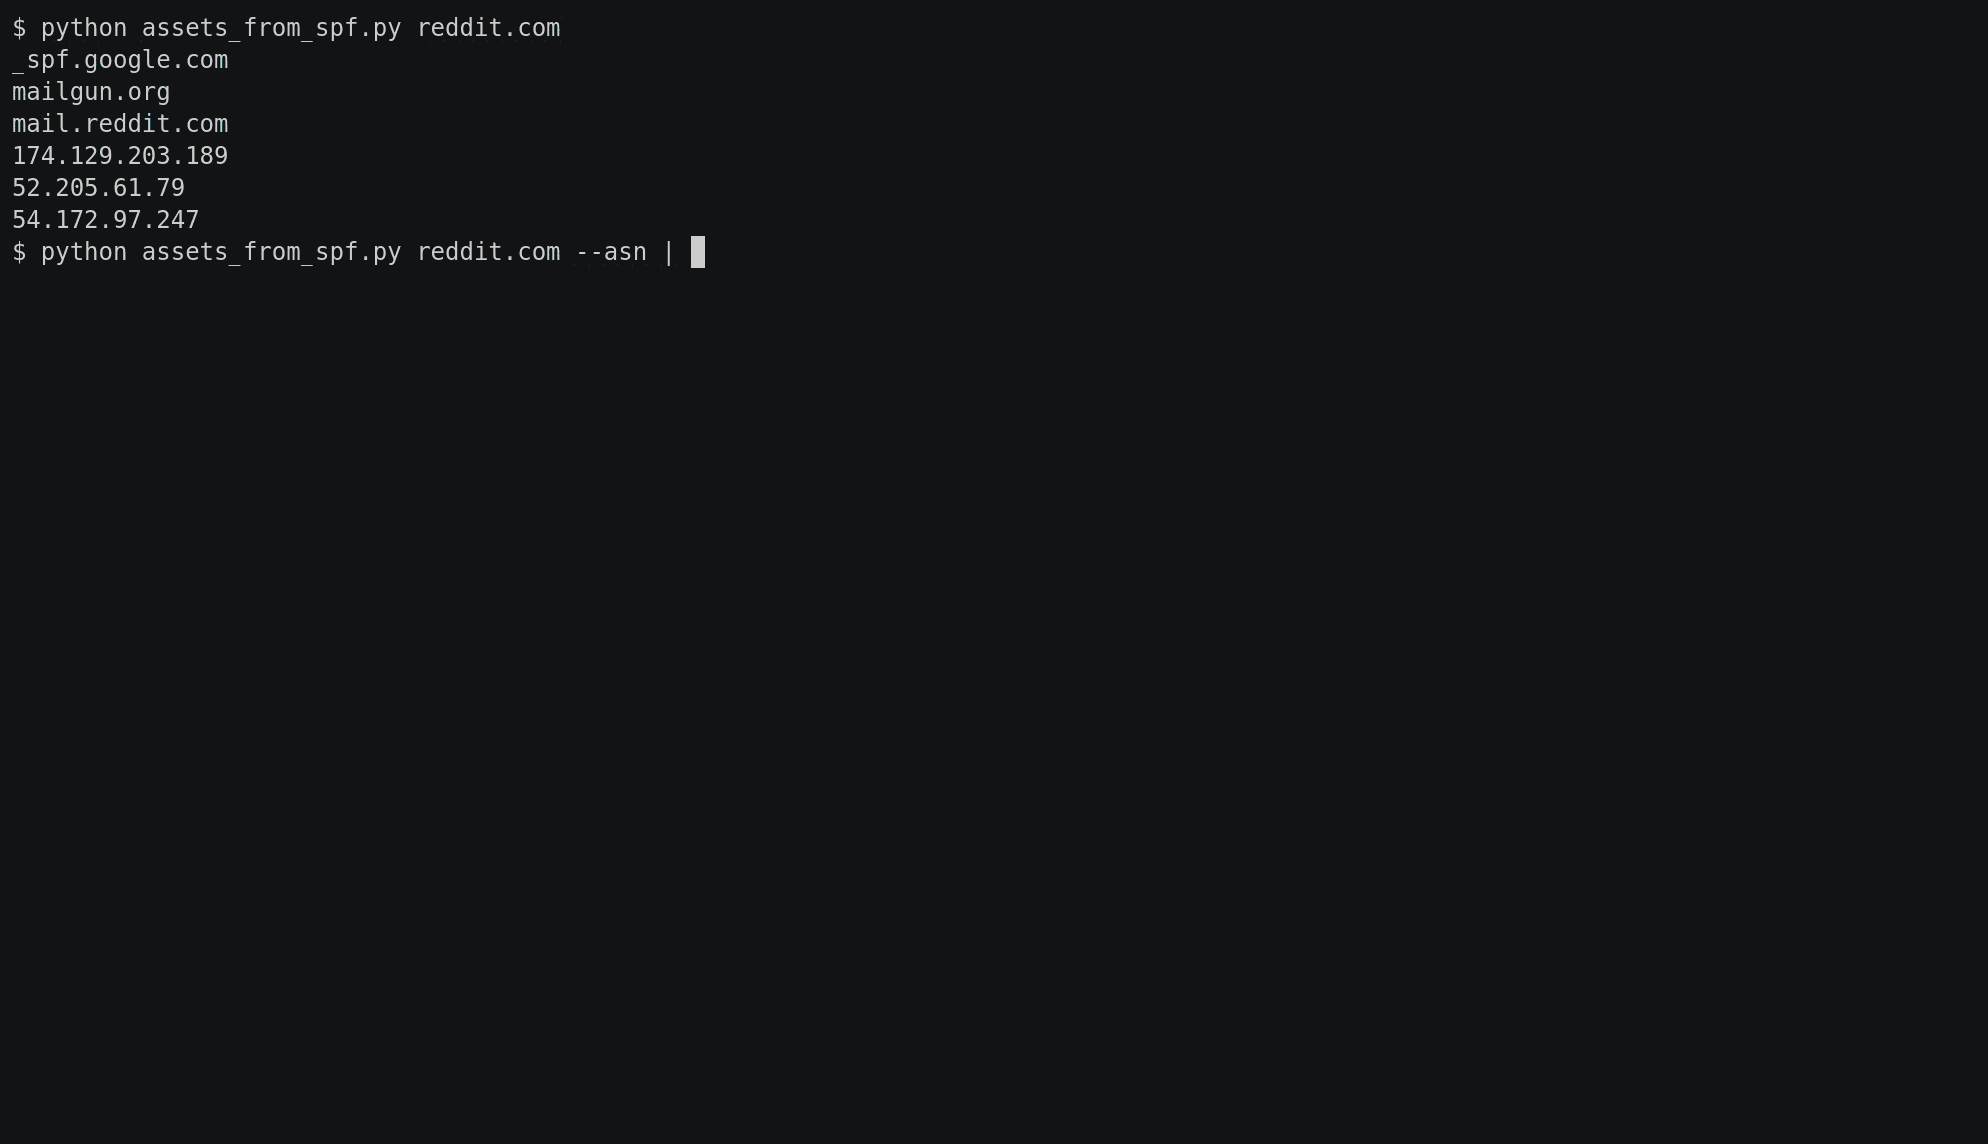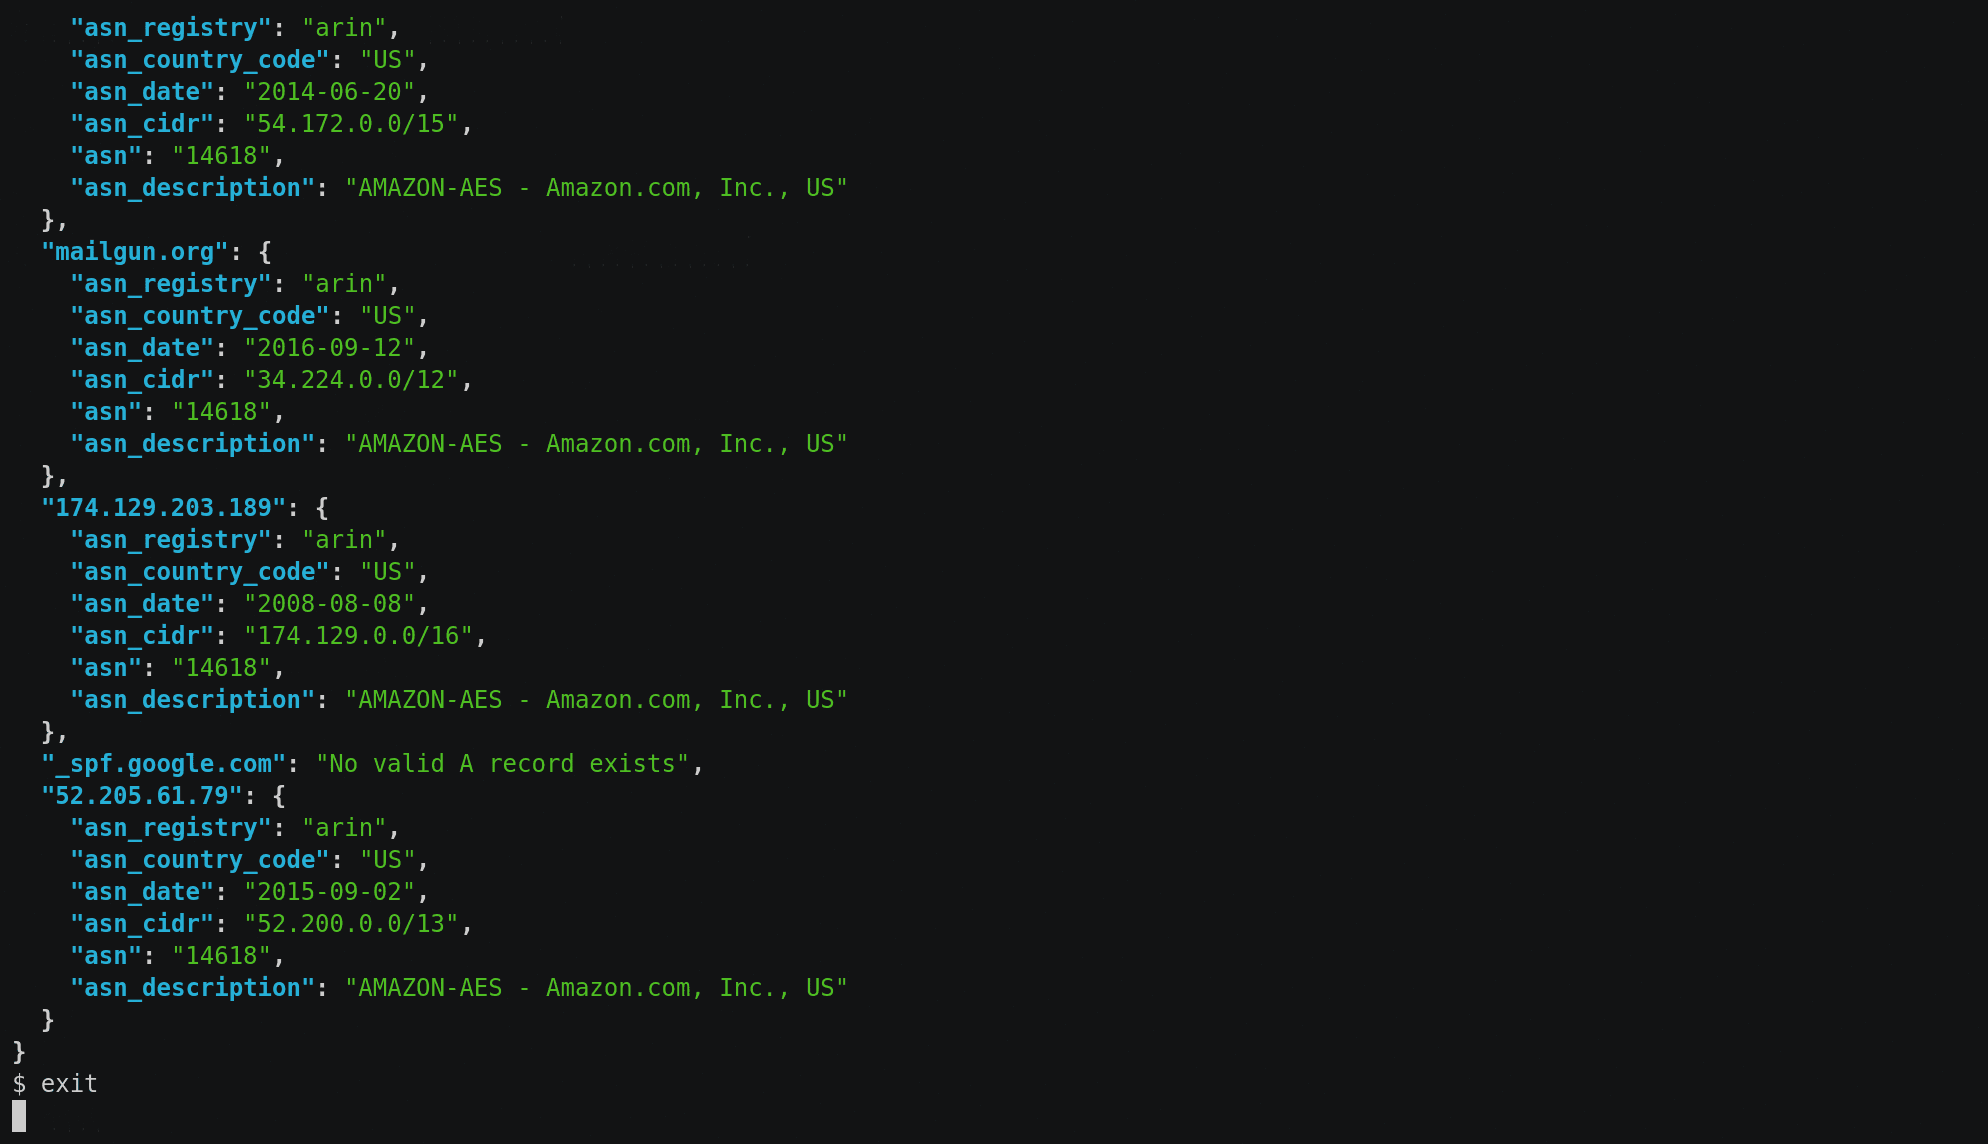 0xbharath/assets-from-spf
A Python script to parse net blocks & domain names from SPF record
 rapid7/recog
Pattern recognition for hosts, services, and content
 allfro/sploitego
Maltego Penetration Testing Transforms
 sensepost/snoopy
Snoopy: A distributed tracking and data interception framework
 sensepost/snoopy-ng
Snoopy v2.0 - modular digital terrestrial tracking framework
 abdullah50i/internal-penetration-testing-project-using-metasploit
Initialized & connected PostgreSQL to Metasploit. Reconnoitered 10.1.16.0/24 with Nmap and imported results. Enumerated hosts/services using SYN, SMB…
 indiquarks/vsftpd-cve-2011-2523-lab
Pen Tesing Lab exploiting VSFTPD 2.3.4 backdoor via Metasploit Framework
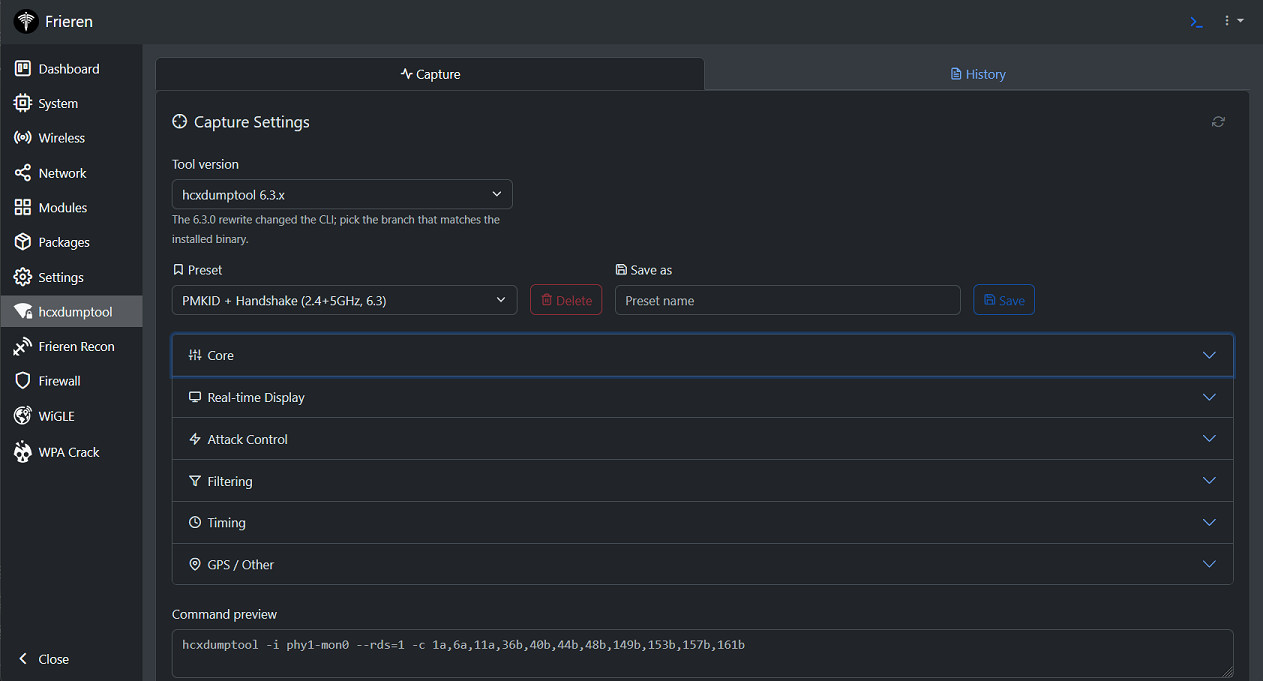 xchwarze/frieren
Frieren is a micro-framework designed for use in routers and Single Board Computers (SBCs). This framework is built to be lightweight, efficient, and…
 ethicalhackinglabs/metasploitable2-exploitation-metasploit
Full Metasploit exploitation walkthrough against Metasploitable2 — vsftpd backdoor, Samba CVE-2007-2447, UnrealIRCd backdoor, Netcat exfiltration,…

 r00ts3c/ddos-rootsec
Explore RootSec's DDOS Archive, featuring top-tier scanners, powerful botnets (Mirai & QBot) and other variants, high-impact exploits, advanced…
 orange-cyberdefense/bof
BOF (Boiboite Opener Framework) is a testing framework for industrial protocols implementations and devices.
 the-tcpdump-group/libpcap
System-independent library for user-level packet capture and filtering. Provides a portable framework for low-level network monitoring, security…
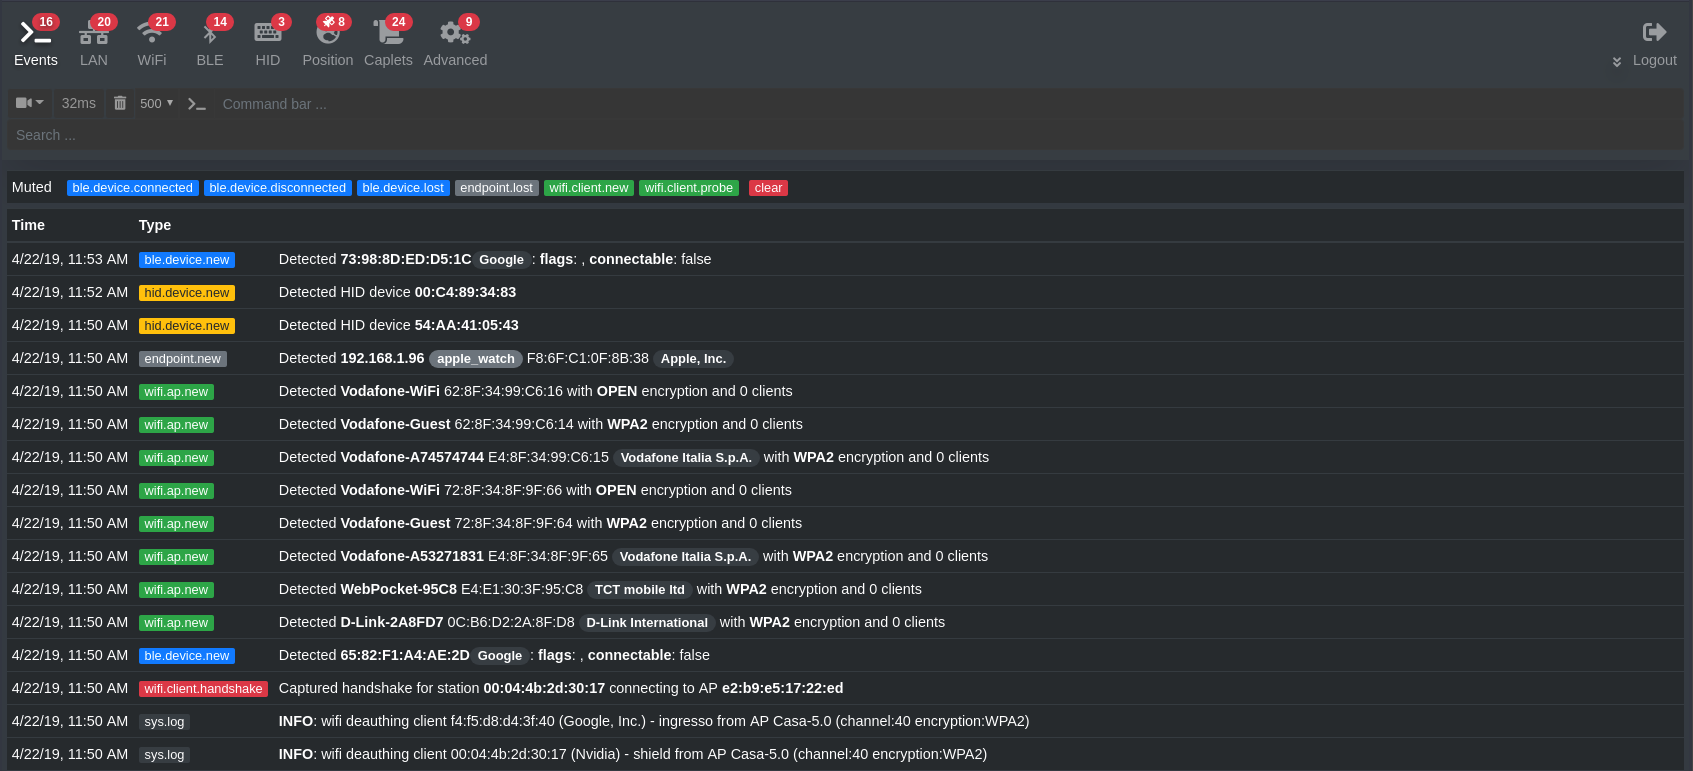 bettercap/bettercap
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
 tjnull/cygor
An modular asset discovery framework written in python to automate the repeating manual work
 gobysec/cve-2019-0708
BlueKeep (CVE-2019-0708) vulnerability checker integrated with Goby's network asset discovery and scanning framework for rapid security assessment.