

SharkMCP
 weirdmachine64/sharkmcp
A swiss-knife MCP server for analysing PCAP files
ctfdigital-forensicseducation+6
754 months ago
weirdmachine64/sharkmcpA swiss-knife MCP server for analysing PCAP files
 cristianzsh/forensictools
Collection of forensic tools
 secdev/scapy
Python-based interactive packet manipulation library for forging, decoding, sending, capturing, and analyzing network packets across a wide range of…
 wireshark/wireshark
Capture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…
 oisf/suricata
Open-source network IDS/IPS/NSM engine for real-time traffic inspection, intrusion detection and prevention, protocol analysis, and rule-based threat…
 security-onion-solutions/securityonion
Open-source security monitoring platform for threat hunting, intrusion detection, log management, incident response, and endpoint visibility with…
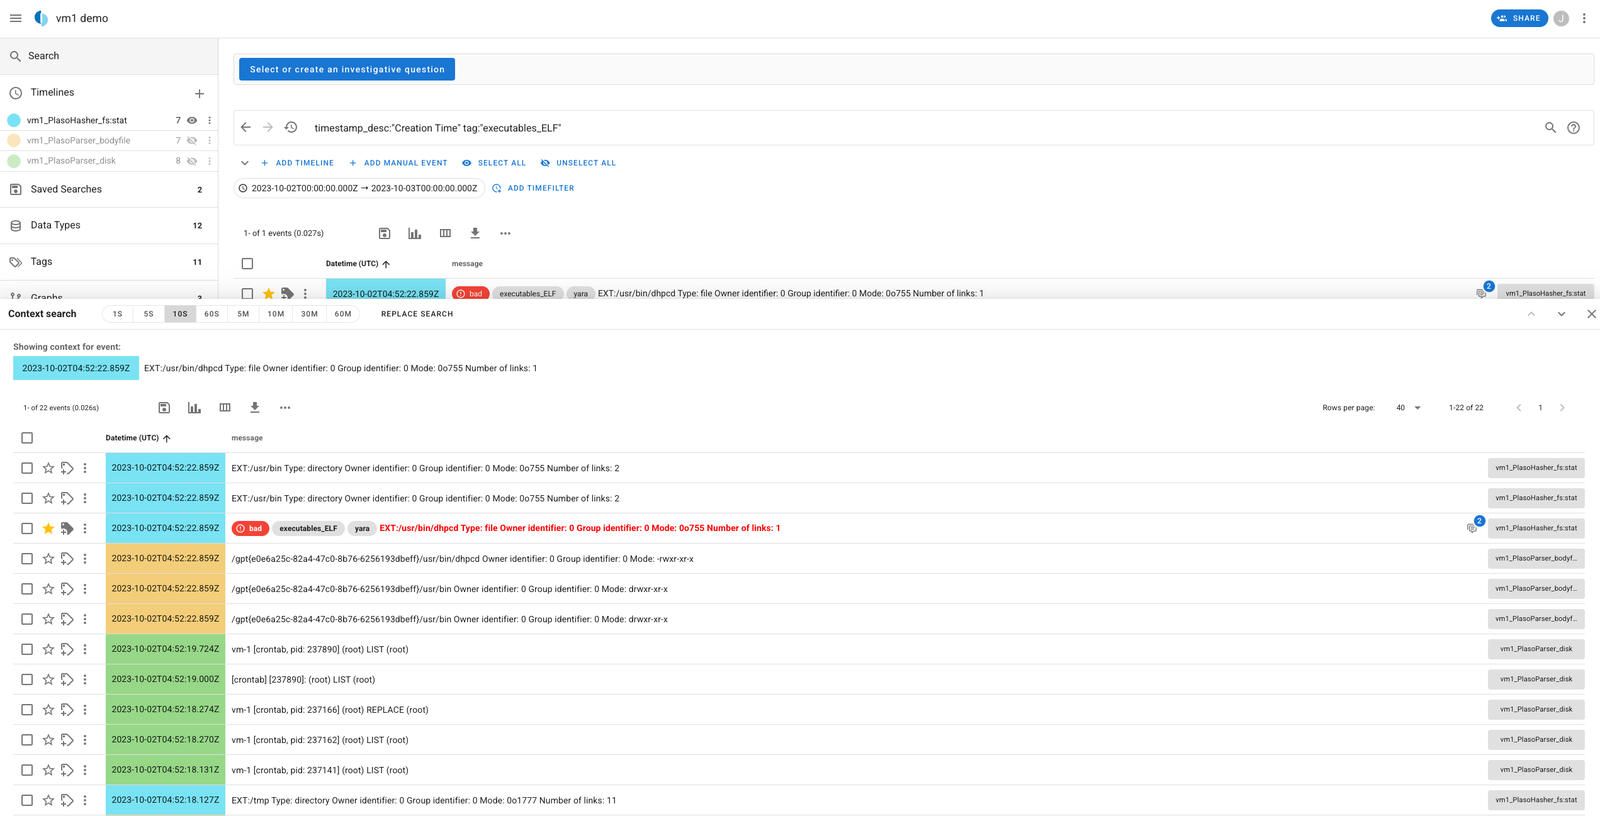 google/timesketch
Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…
 seladb/pcapplusplus
Multiplatform C++ library for high-performance network packet capture, parsing, crafting, and analysis. Supports libpcap, DPDK, AF_XDP, PF_RING, and…
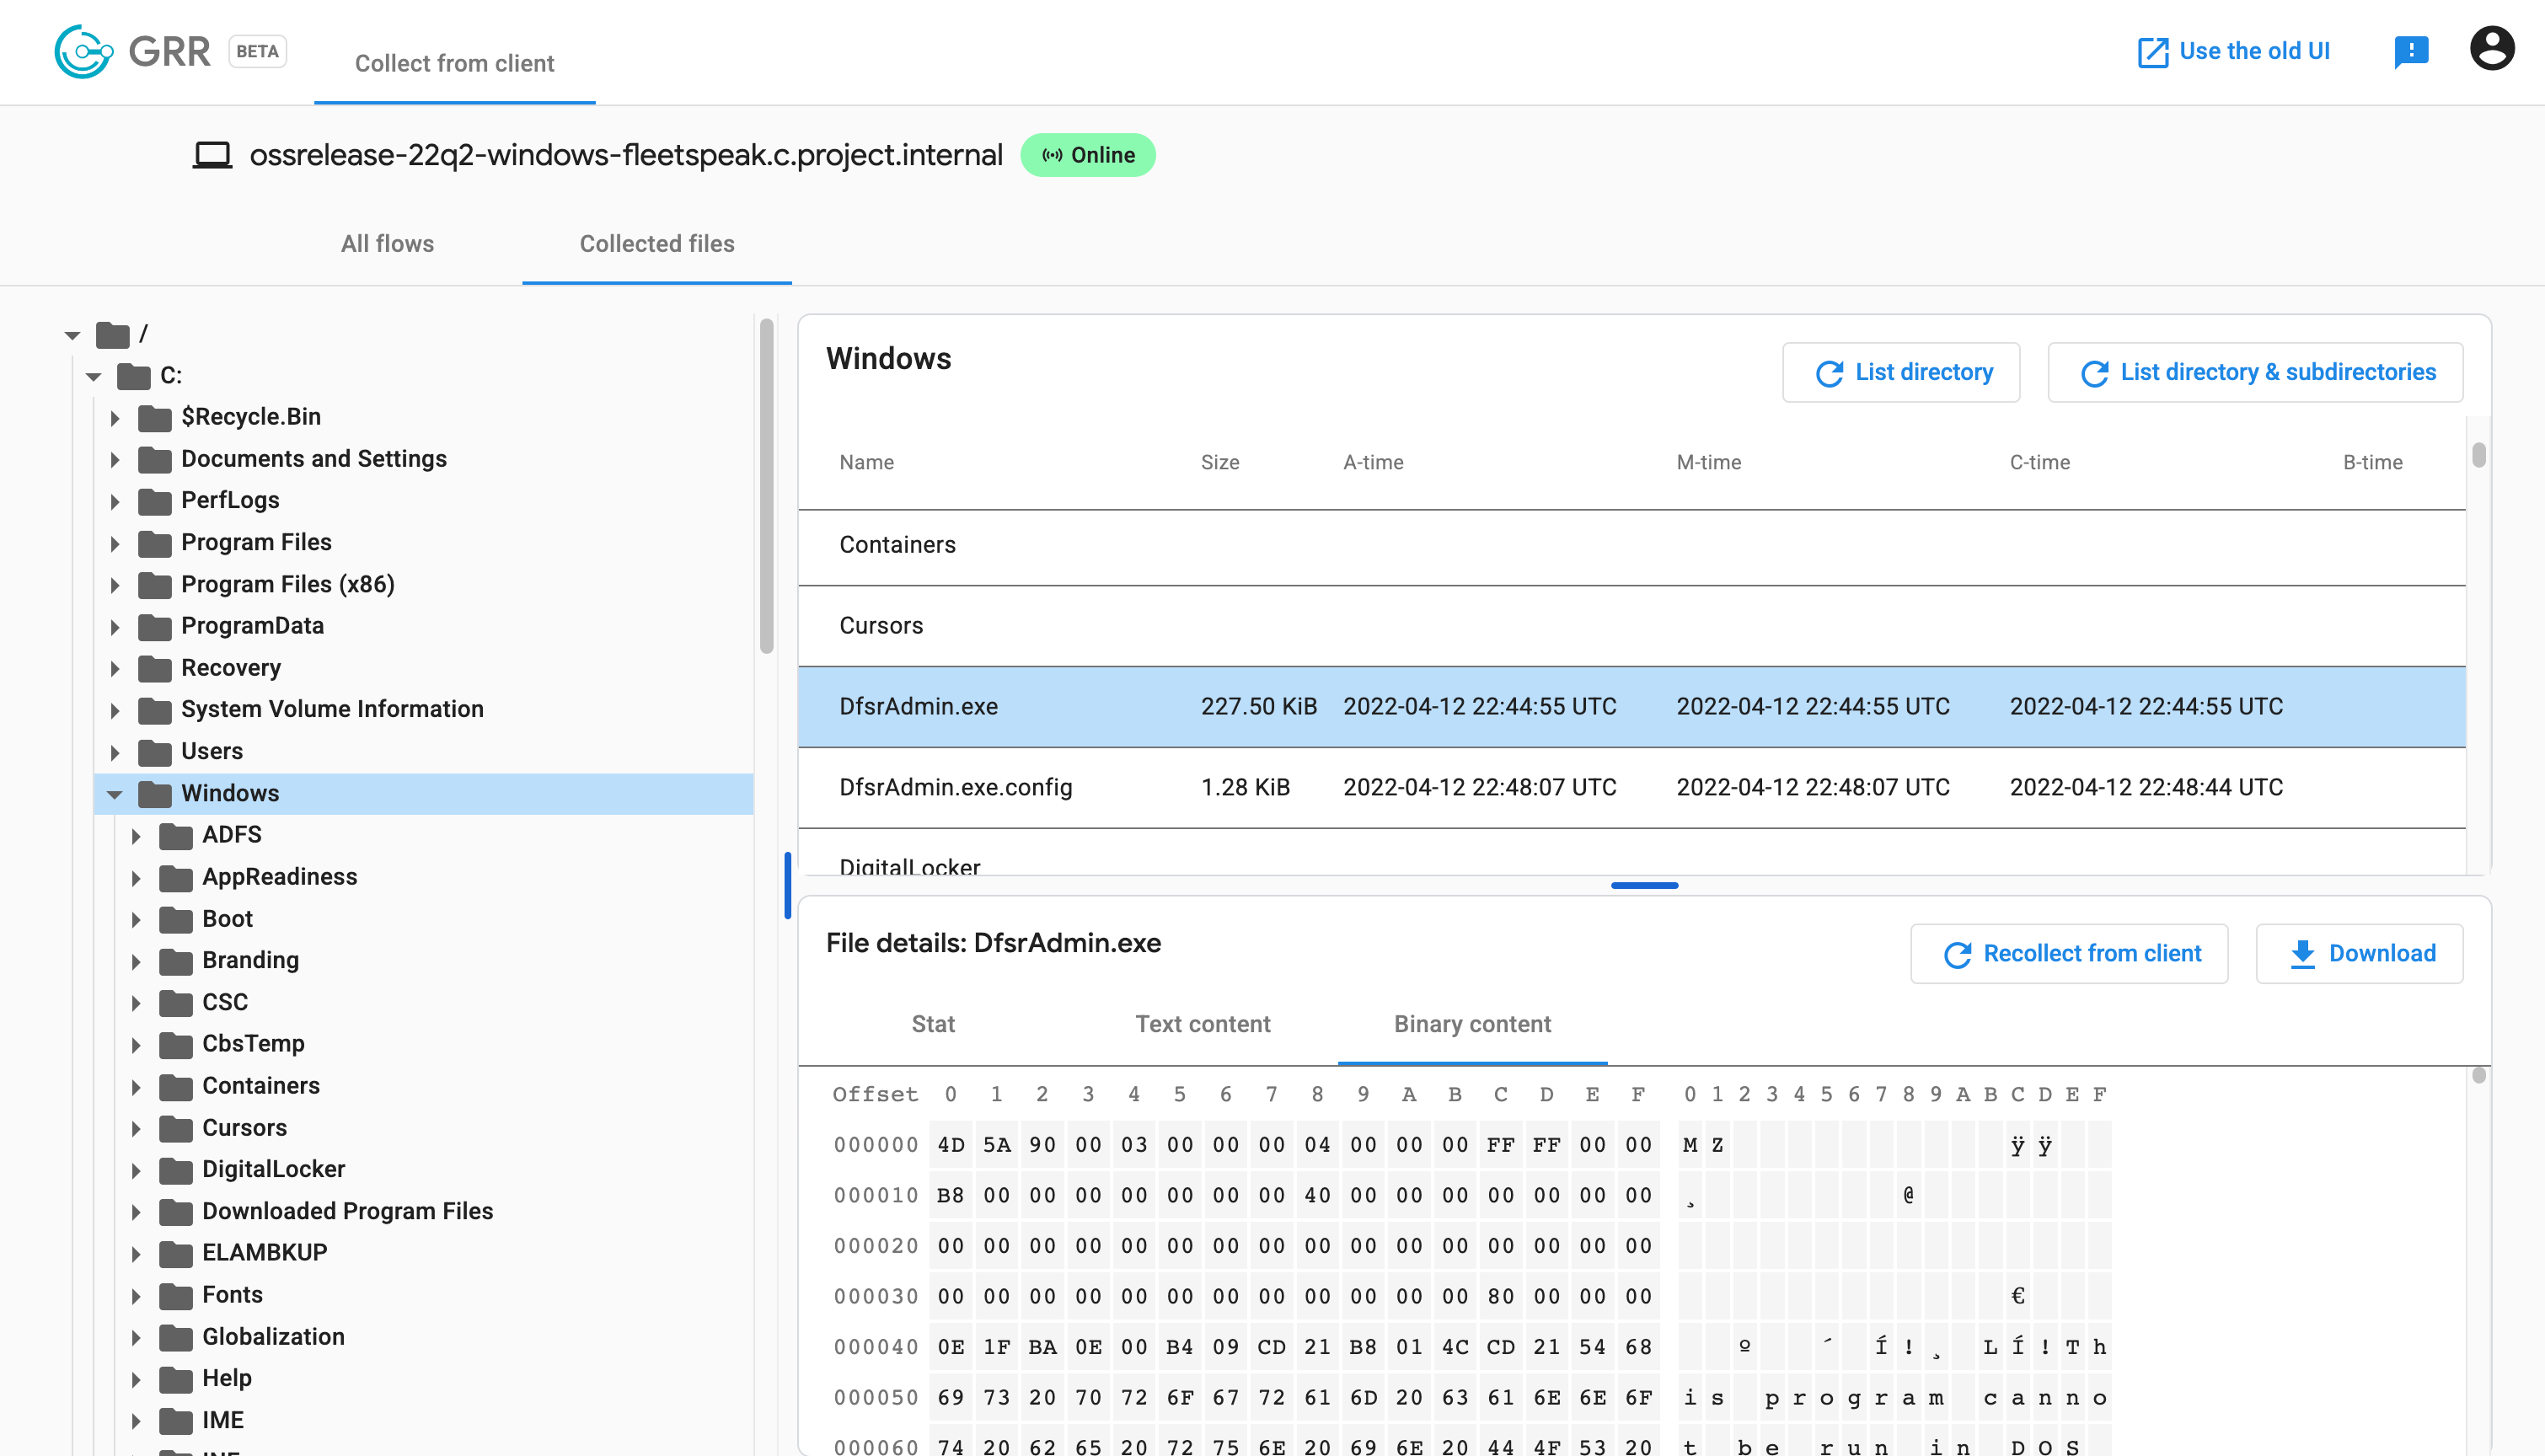 google/grr
Remote live forensics and incident response framework with Python agent for collecting forensic data from endpoints, including memory, disk, and…
 gcla/termshark
A terminal UI for tshark, inspired by Wireshark
 google/gopacket
Provides packet processing capabilities for Go
 cisagov/malcolm
Containerized network traffic analysis suite ingesting PCAP, Zeek logs, and Suricata alerts for automated normalization, enrichment, and correlation…
 neo23x0/loki
IOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…
 kiminewt/pyshark
Python wrapper for tshark, allowing python packet parsing using wireshark dissectors
 gamelinux/passivedns
A network sniffer that logs all DNS server replies for use in a passive DNS setup
 cisco/joy
A package for capturing and analyzing network flow data and intraflow data, for network research, forensics, and security monitoring.
 netsniff-ng/netsniff-ng
A Swiss army knife for your daily Linux network plumbing.
 idaholab/malcolm
Malcolm is a powerful, easily deployable network traffic analysis tool suite for full packet capture artifacts (PCAP files), Zeek logs and Suricata…