
game-of-kingshot-re
Educational reverse engineering study of a Unity/IL2CPP Android game. Documents gateway protocol decoding, native anti-tampering SDK analysis, SSL…

Educational reverse engineering study of a Unity/IL2CPP Android game. Documents gateway protocol decoding, native anti-tampering SDK analysis, SSL…

All-in-One malware analysis tool.

Malware samples, analysis exercises and other interesting resources.

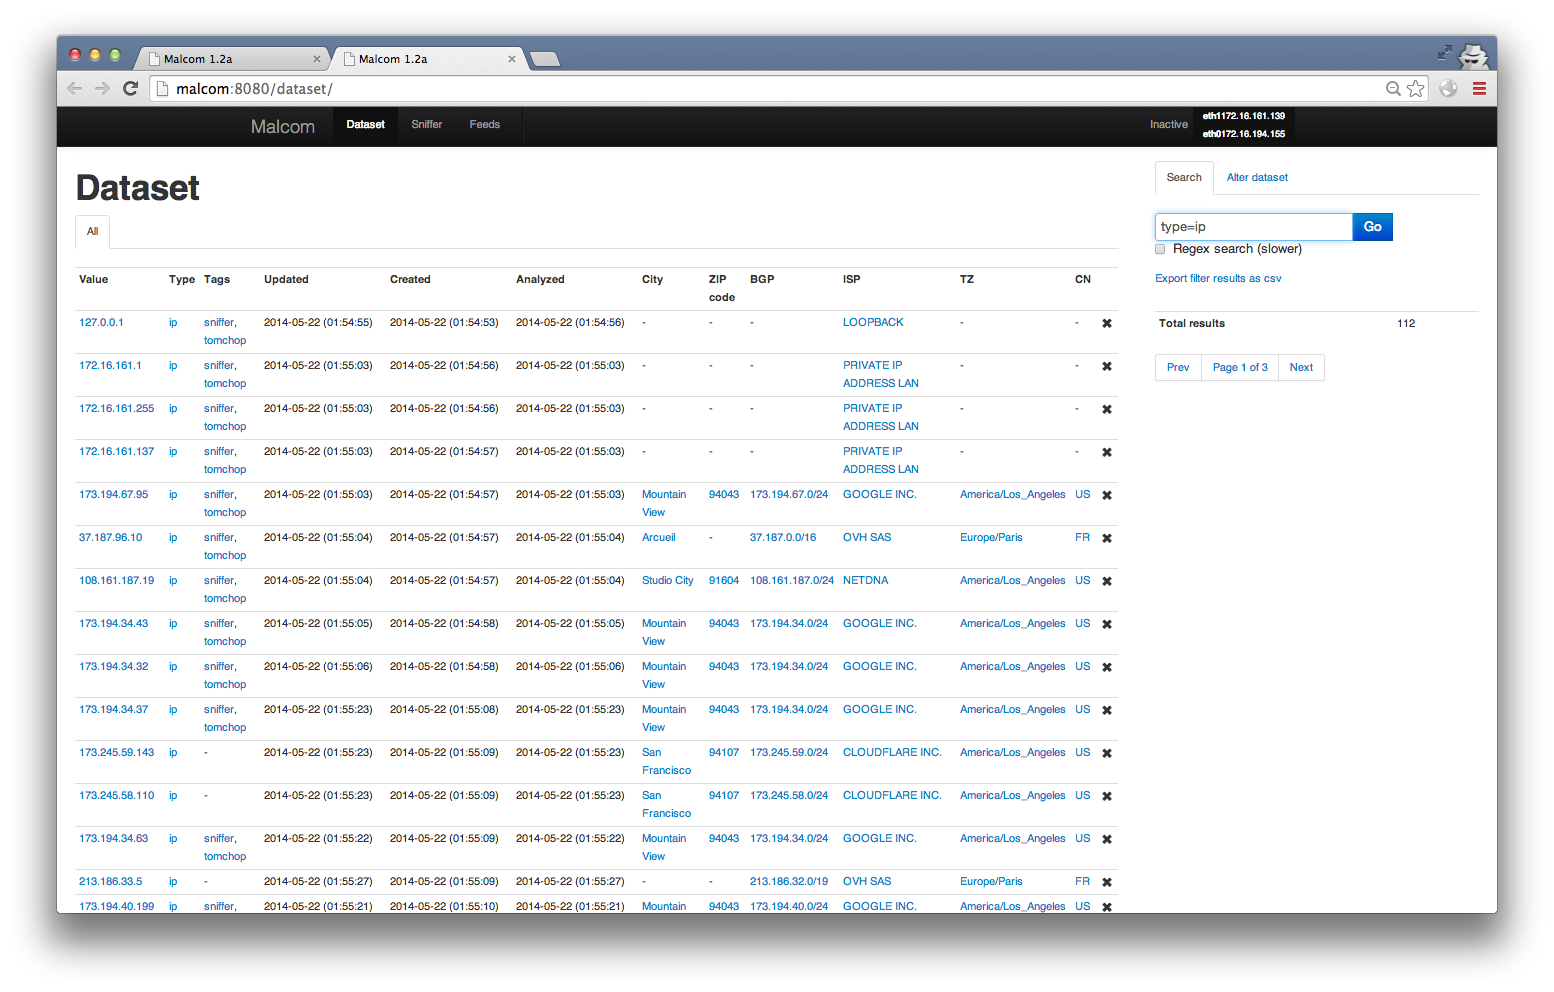
Malcom - Malware Communications Analyzer

Collection of forensic tools

Python library for dissecting and parsing Cobalt Strike related data such as Beacon payloads and Malleable C2 Profiles

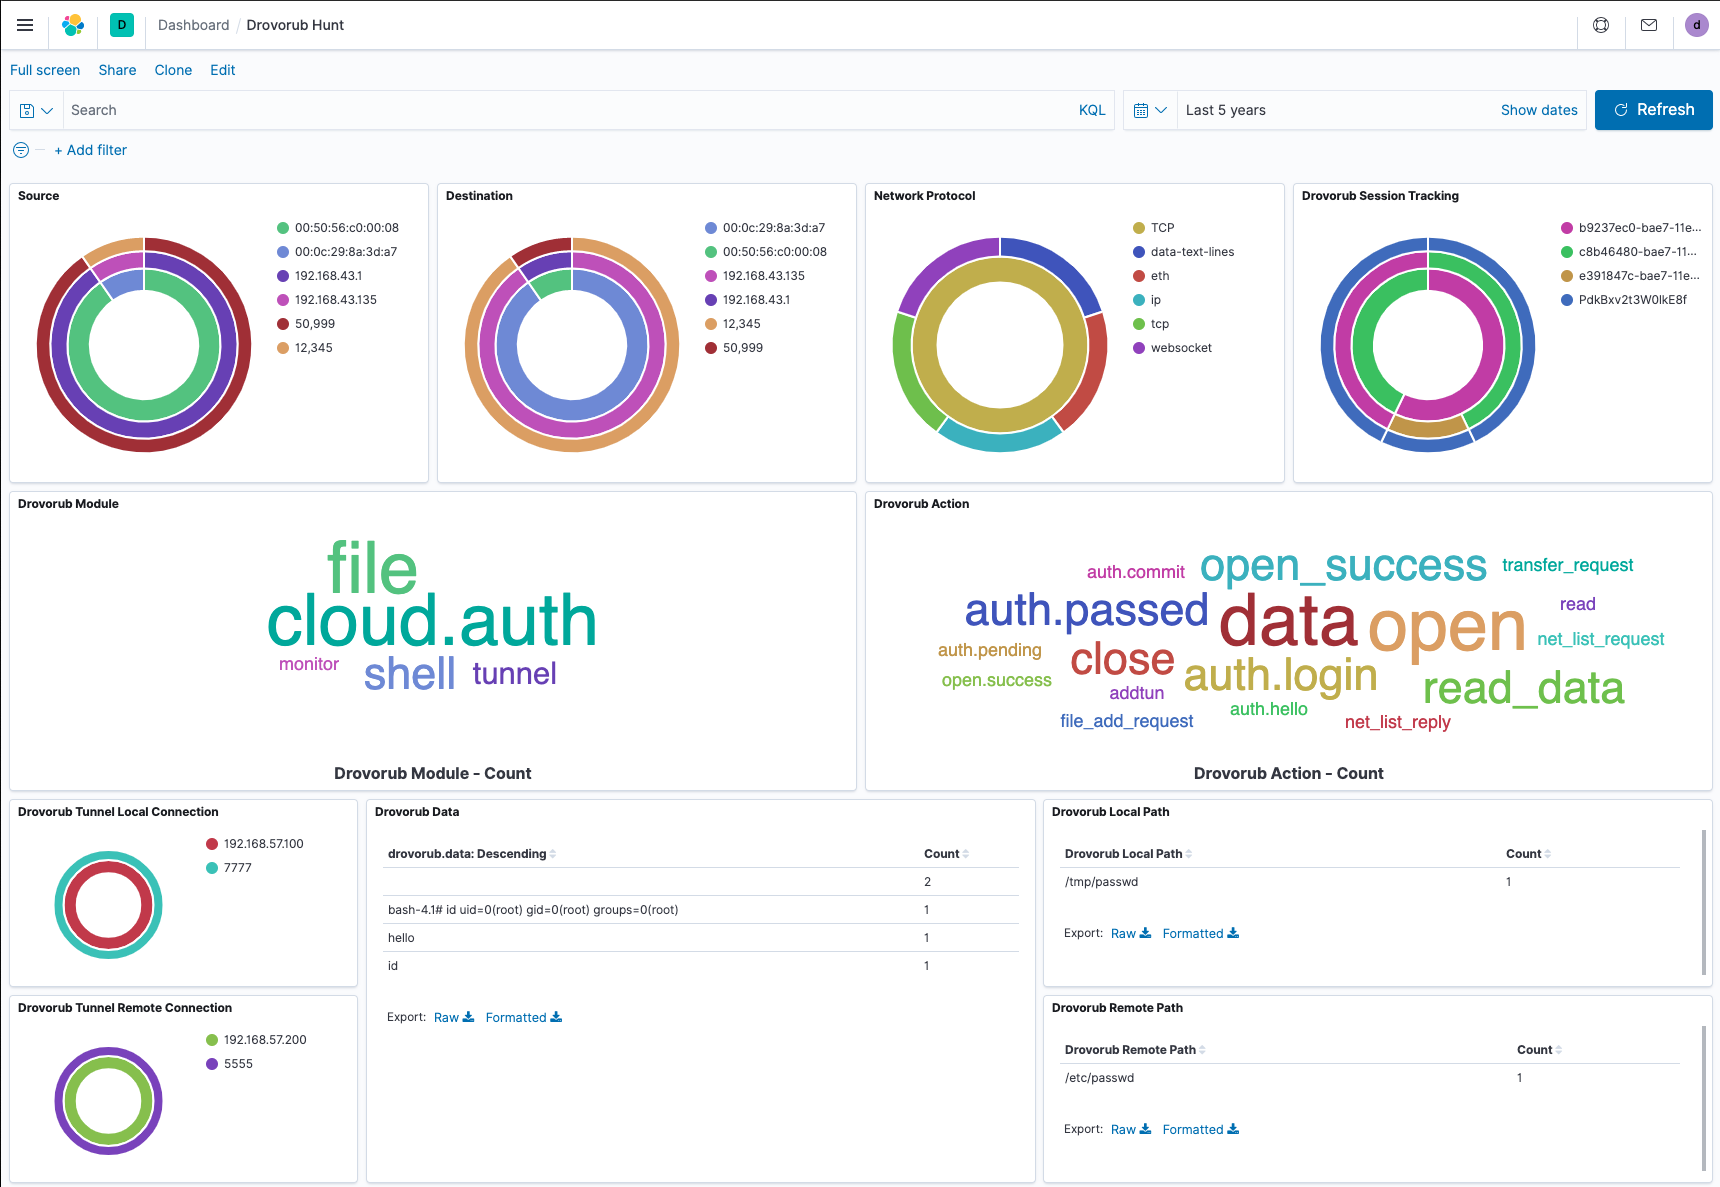
A tool to assist with network-based hunting for GRU's Drovorub malware c2

Breakdown of a c2-network of chinese beamers - SilentSDK-Analysis

Walk any memory dump. Find what's hidden. Linux + Windows kernel forensics from a single static Rust binary — no Python required.

Parsing Ramnit's traffic

A Zeek based NetSupport detector. NetSupport is often abused by attackers in malware.

CVE-2017-0199 XLS --> HTA --> VBS --> STEGANOGRAPHY --> DBATLOADER/GULOADER STYLE MALWARE