
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
27 results
Malcolm preview

Malcolm

GitHubidaholab/malcolm

Malcolm is a powerful, easily deployable network traffic analysis tool suite for full packet capture artifacts (PCAP files), Zeek logs and Suricata…
defensive-toolsdigital-forensicsforensics+8
482
27 days ago
fatt preview

fatt

GitHub0x4d31/fatt

FATT /fingerprintAllTheThings - a pyshark based script for extracting network metadata and fingerprints from pcap files and live network traffic

network-forensicspacket-sniffing-analysisthreat-intelligence
6854 years ago
irflow-timeline preview

irflow-timeline

GitHubr3nzsec/irflow-timeline

DFIR Timeline Analysis for macOS — SQLite-backed viewer for CSV, TSV, XLSX, EVTX, Plaso, $MFT, and $J files with AI Artifacts, AI Secret Hunt,…
digital-forensicsdisk-forensicsforensics+7
36913 days ago
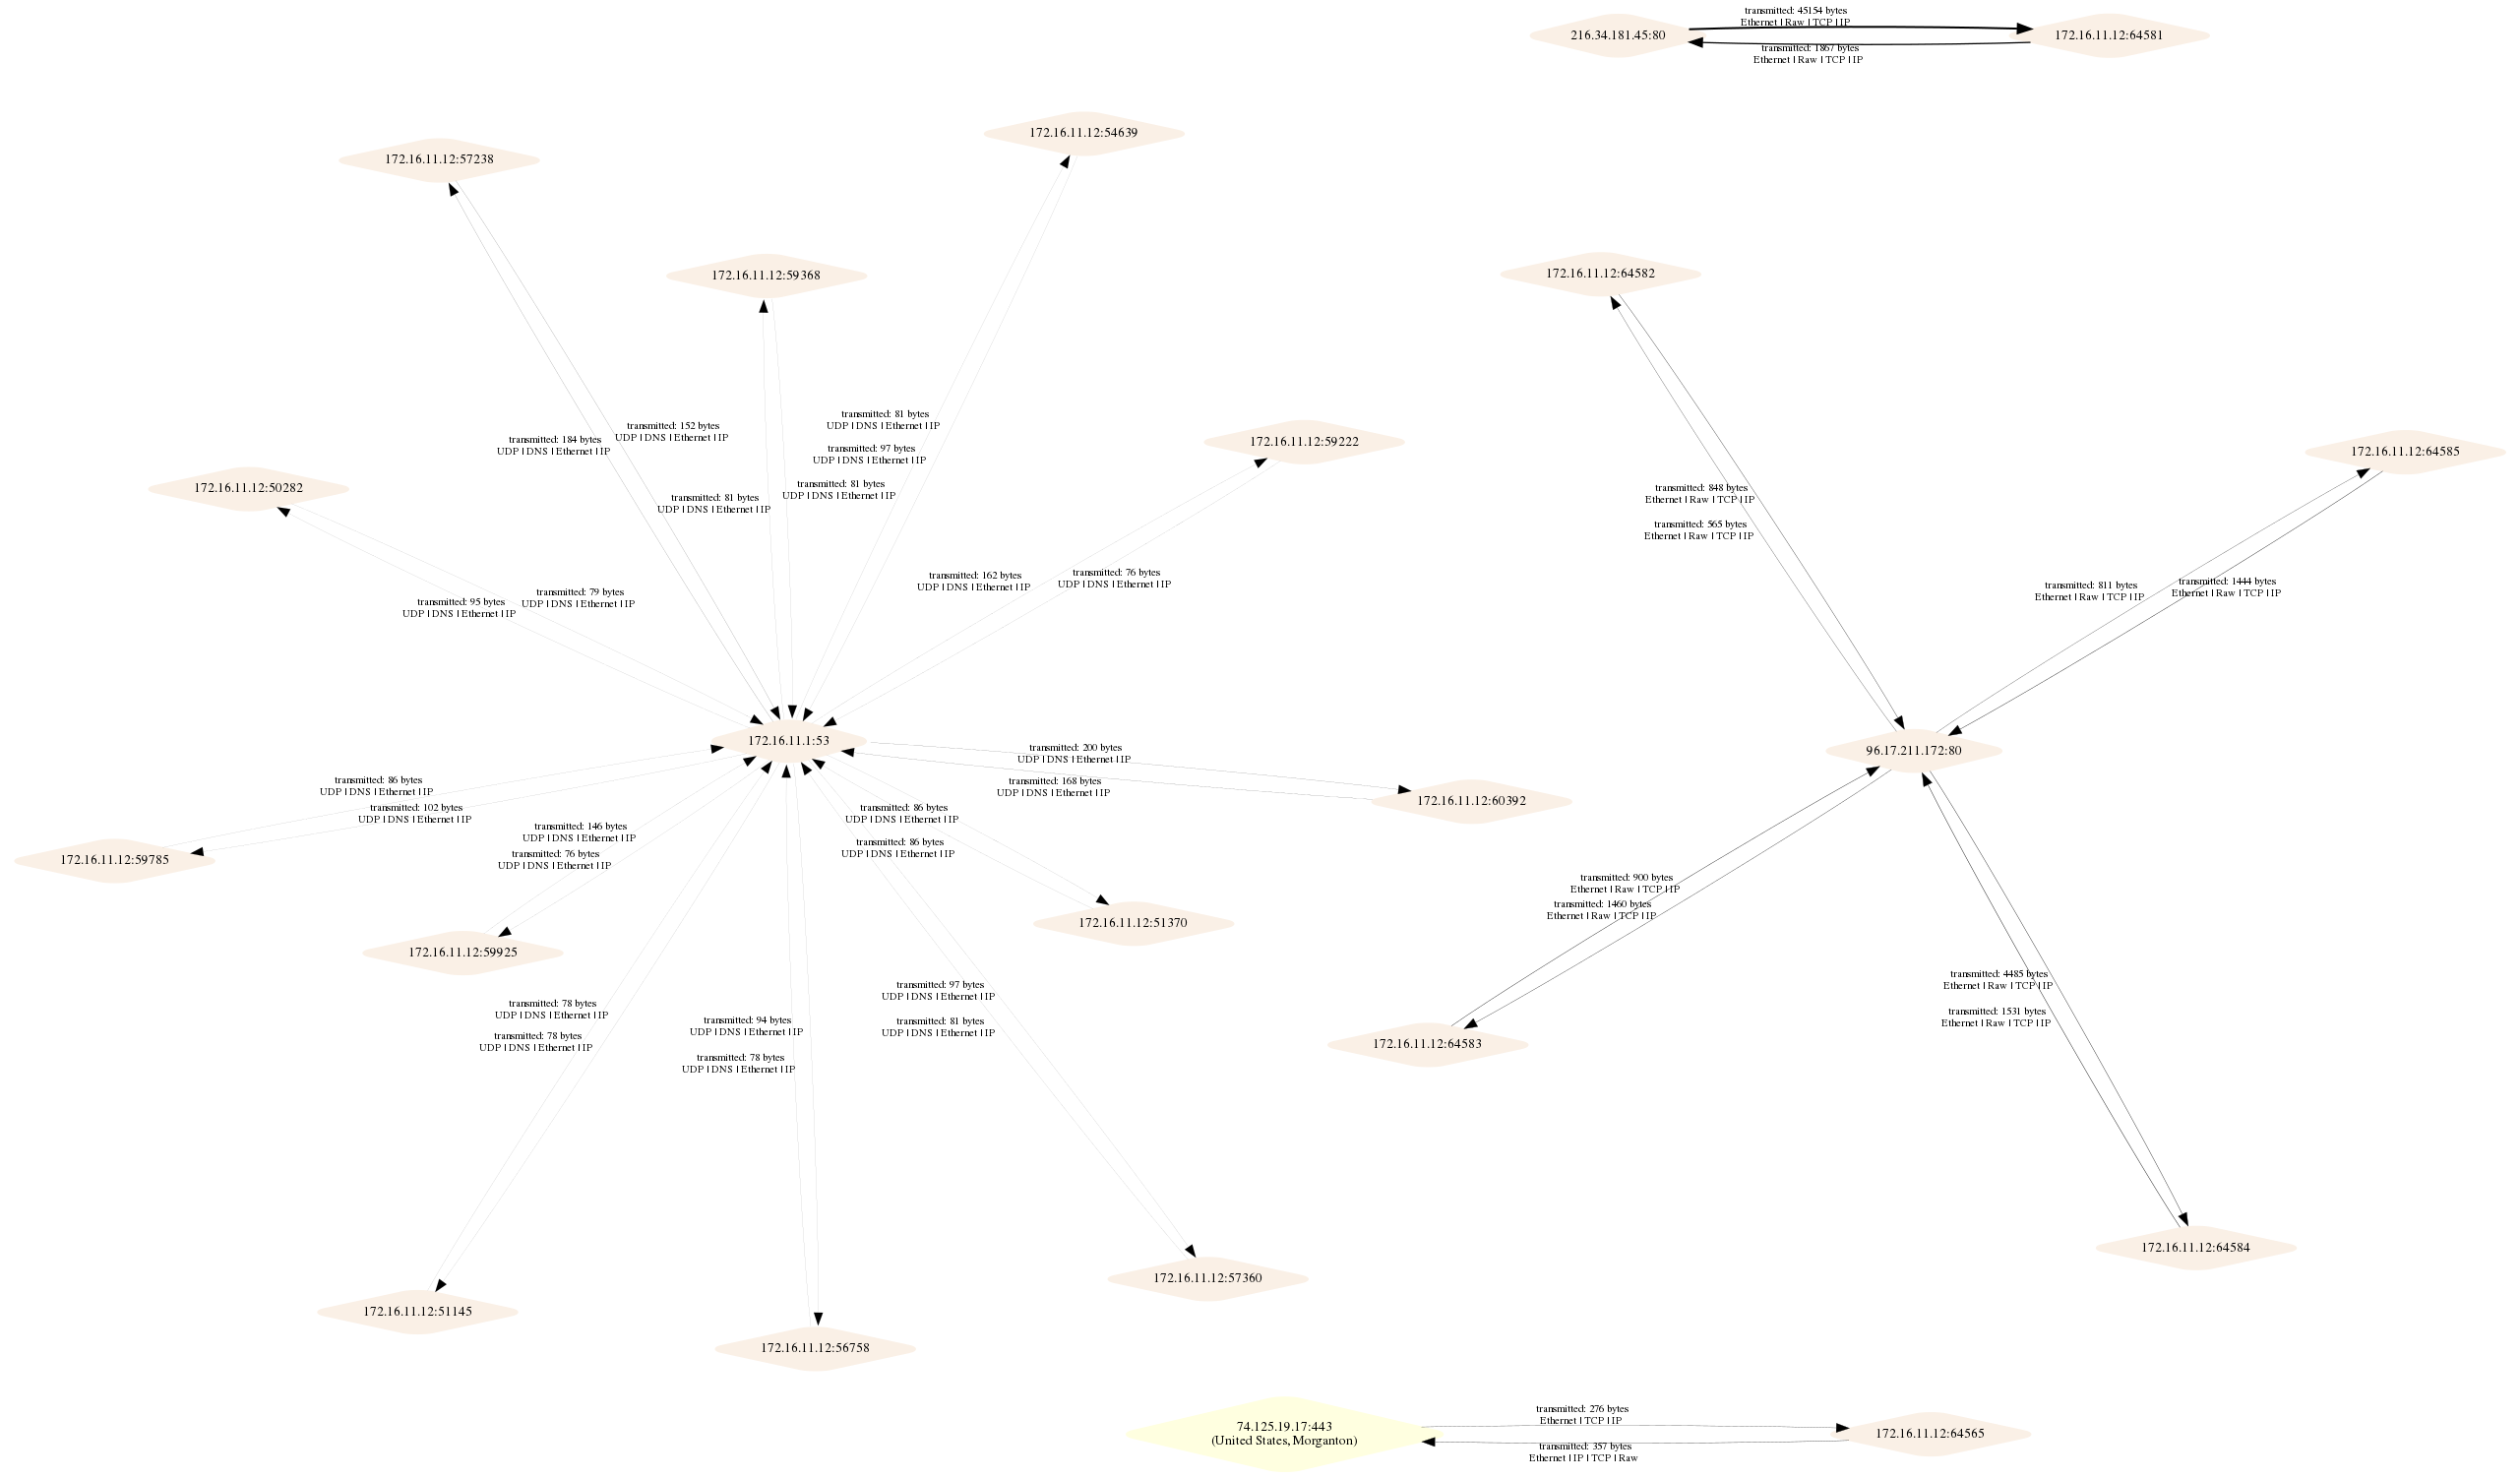
PcapViz preview

PcapViz

GitHub1ultimat3/pcapviz

Visualize network topologies and collect graph statistics based on pcap files
information-gatheringnetwork-forensicsnetwork-mapping+1
3603 years ago
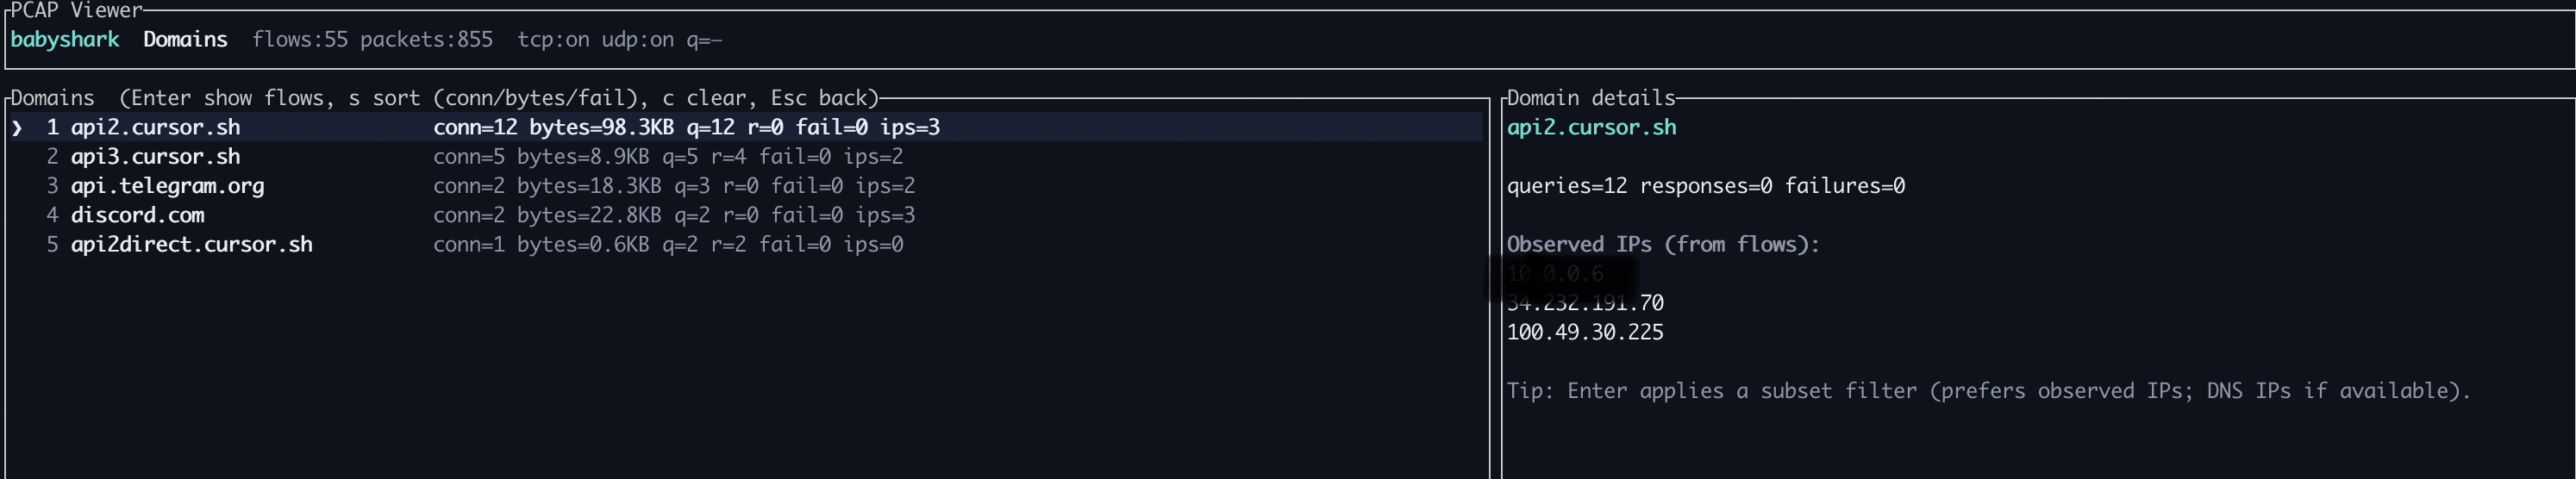
babyshark preview

babyshark

GitHubvignesh07/babyshark

Flows-first PCAP TUI (case files, gorgeous UX). Do do do do.

anomaly-detectiondns-analysisforensics+5
5686 months ago
IpGeo preview

IpGeo

GitHubz4l4mi/ipgeo

Extracts IP addresses from pcap/pcapng network traffic files and generates CSV reports with geolocation, ISP, and organizational details for each IP.
information-gatheringnetwork-forensicsosint+1
1323 years ago
pcapfex preview

pcapfex

GitHubvikwin/pcapfex

'Packet Capture Forensic Evidence eXtractor' is a tool that finds and extracts files from packet capture files
data-recoverydigital-forensicsforensics+2
2306 years ago
wireshark-forensics-plugin preview

wireshark-forensics-plugin

GitHubrjbhide/wireshark-forensics-plugin

Wireshark plugin that correlates network traffic with threat intelligence, asset tags, and vulnerability data to accelerate forensic analysis of PCAP…
digital-forensicsforensicsnetwork-forensics+3
1024 years ago
packetsifterTool preview

packetsifterTool

GitHubpacketsifter/packetsiftertool

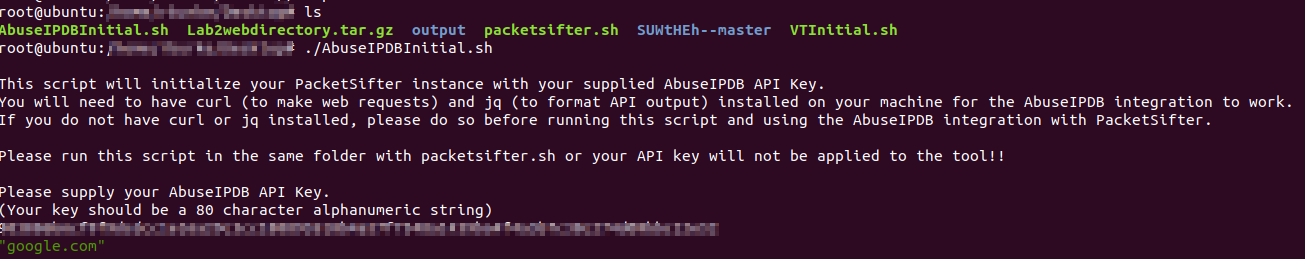
PacketSifter is a tool/script that is designed to aid analysts in sifting through a packet capture (pcap) to find noteworthy traffic. Packetsifter…
defensive-toolsdigital-forensicsforensics+5
935 years ago
netstat2neo4j preview

netstat2neo4j

GitHubtrinitor/netstat2neo4j

create cypher create statements for neo4j out of netstat files from multiple machines

information-gatheringlog-analysisnetwork-forensics
415 years ago
SharkMCP preview

SharkMCP

GitHubweirdmachine64/sharkmcp

A swiss-knife MCP server for analysing PCAP files
ctfdigital-forensicseducation+6
764 months ago
ipdecap preview

ipdecap

GitHublpefferkorn/ipdecap

Decapsulate traffic encapsulated within GRE, IPIP, 6in4, ESP (ipsec) protocols, can also remove IEEE 802.1Q (virtual lan) header. Works with pcap…
encryption-decryption-toolsforensicsnetwork-forensics+3
357 years ago
BlueFish preview

BlueFish

GitHubemrekybs/bluefish

Automation tool designed to simplify the analysis of PCAP (Packet Capture) files
forensicsincident-responseinformation-gathering+2
205 months ago
Sandb0x-Xtract0r preview

Sandb0x-Xtract0r

GitHubdarnellwashingtonjr94-art/sandb0x-xtract0r

Automated cross-platform sandbox that detonates suspicious files in isolated VMs/emulators, captures network and memory artifacts, and creates LLM…
dynamic-analysis-sandboxingmalware-analysismemory-forensics+3
32 days ago
RCE-CVE-2017-0199-detection-analysis preview

RCE-CVE-2017-0199-detection-analysis

GitHubahmed-tarek22752/rce-cve-2017-0199-detection-analysis

This repository contains a full blue-team malware analysis of a real malicious DOCX exploiting CVE-2017-0199. The lab includes sandbox execution,…

command-and-controldigital-forensicseducation+8
120 days ago
digital-forensics-lab preview

digital-forensics-lab

GitHubfrankwxu/digital-forensics-lab

Free hands-on digital forensics labs for students and faculty

ai-securityctfdigital-forensics+9
3.0k4 days ago
Qu1cksc0pe preview

Qu1cksc0pe

GitHubcyb3rmx/qu1cksc0pe

All-in-One malware analysis tool.
android-securitydynamic-analysis-sandboxingforensics+4
2.1k3 days ago
BruteShark preview

BruteShark

GitHubodedshimon/bruteshark

Network Analysis Tool

dns-analysisforensicshash-analysis+4
3.4k4 years ago
Previous12Next