An-Integrated-Wireless-Network-Forensic-Analysis-Framework

This framework combines a set of existing open source tools into an integrated package that automates the forensics investigation process. It is able…

This framework combines a set of existing open source tools into an integrated package that automates the forensics investigation process. It is able…

Arkime is an open source, large scale, full packet capturing, indexing, and database system.

Open-source network forensics toolkit for packet analysis, port scanning, host discovery, and IP geolocation. Supports ARP, ICMP, TCP, UDP pings and…

IOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…

OpenFPC, Open Source Full Packet Capture

JA4+ is a suite of network fingerprinting standards

Dshell is a network forensic analysis framework.

Multiplatform C++ library for high-performance network packet capture, parsing, crafting, and analysis. Supports libpcap, DPDK, AF_XDP, PF_RING, and…


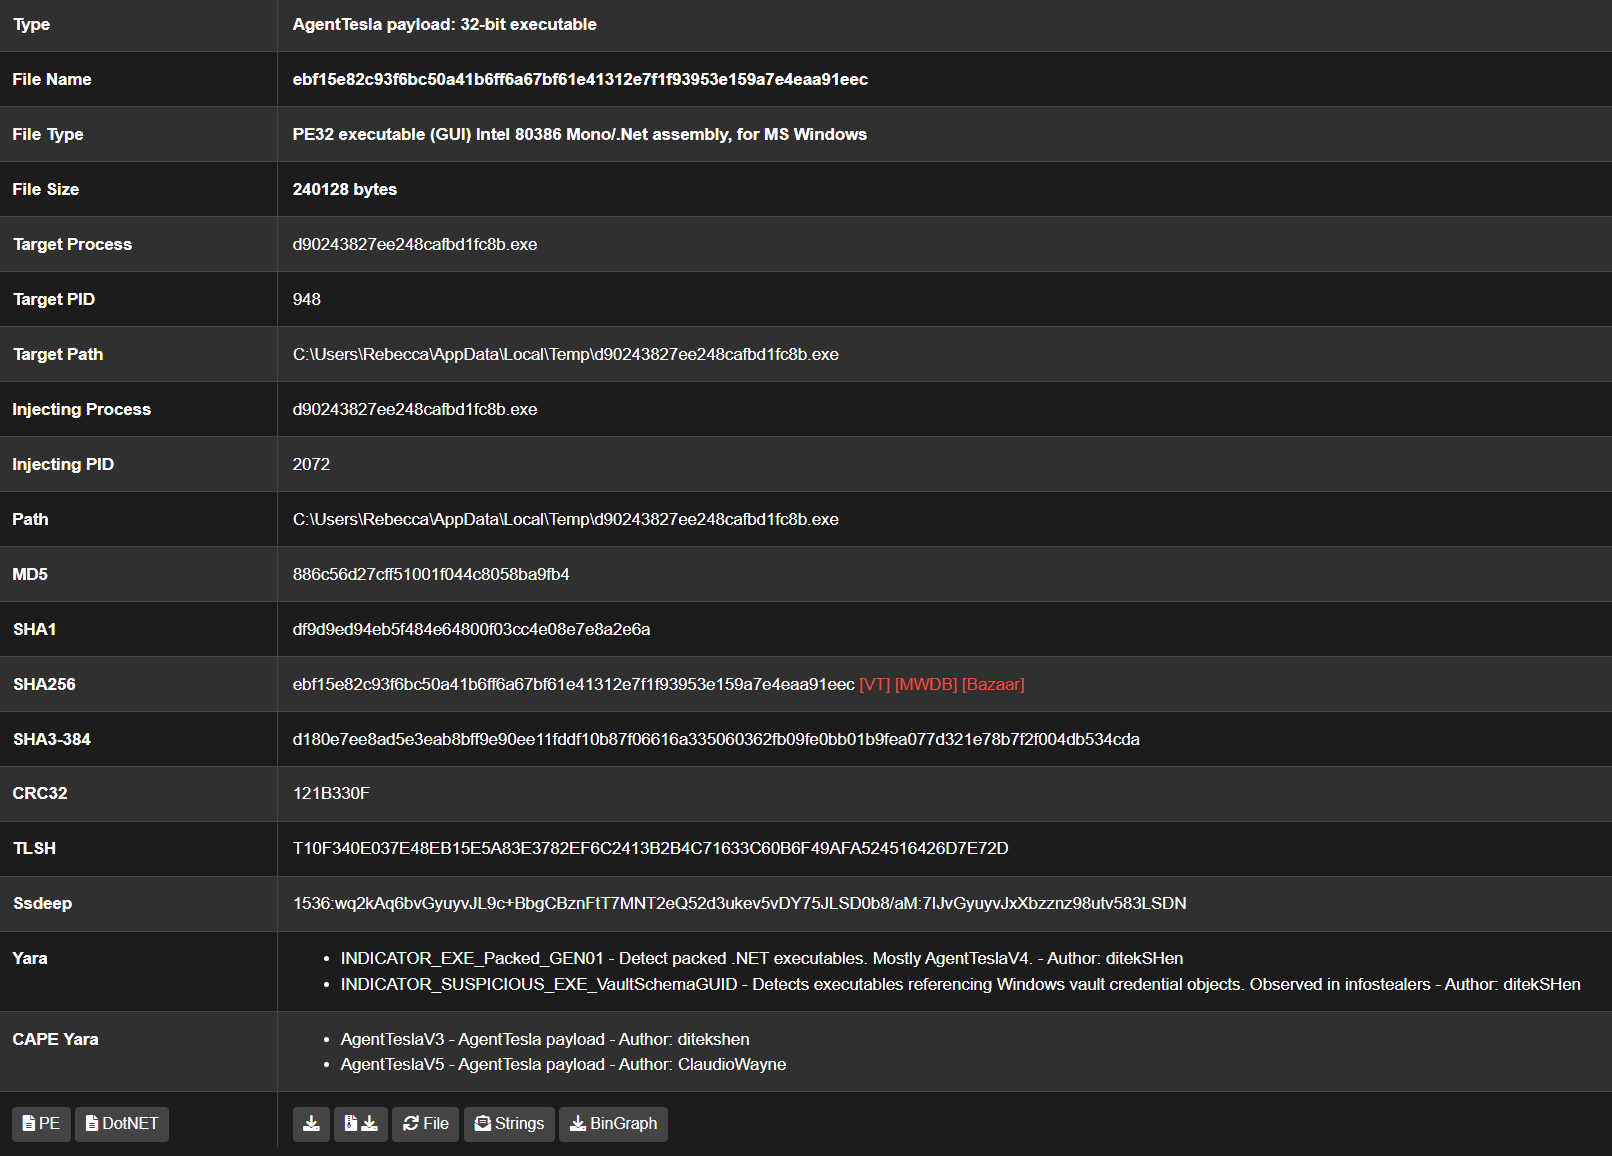
Malware Configuration And Payload Extraction

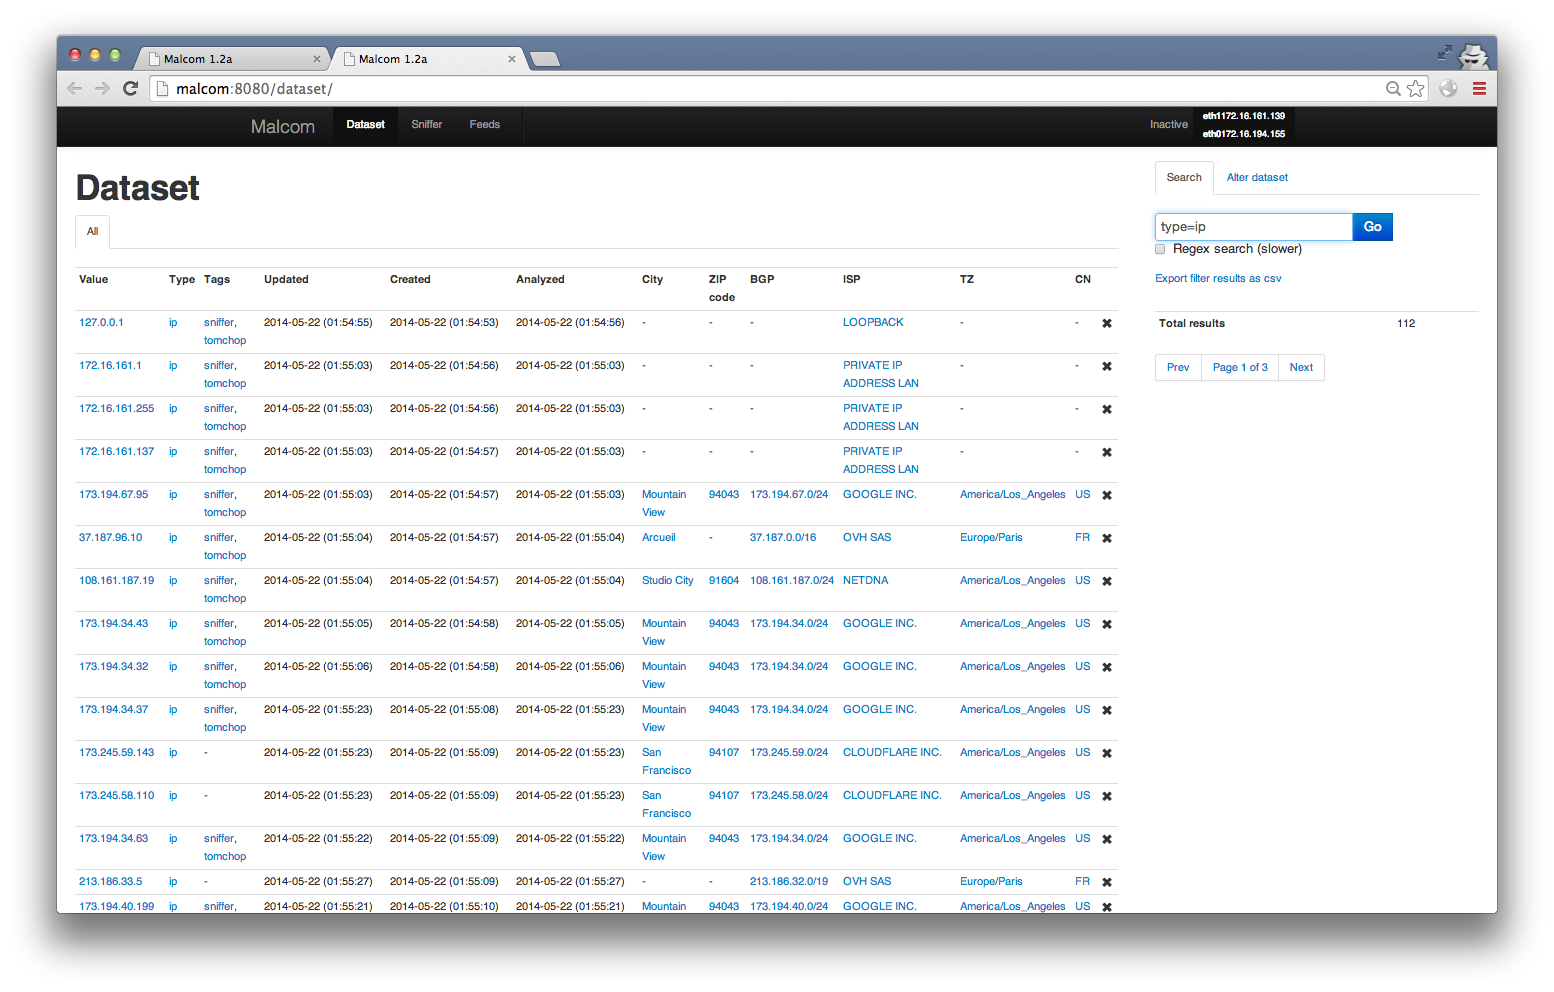
Malcom - Malware Communications Analyzer

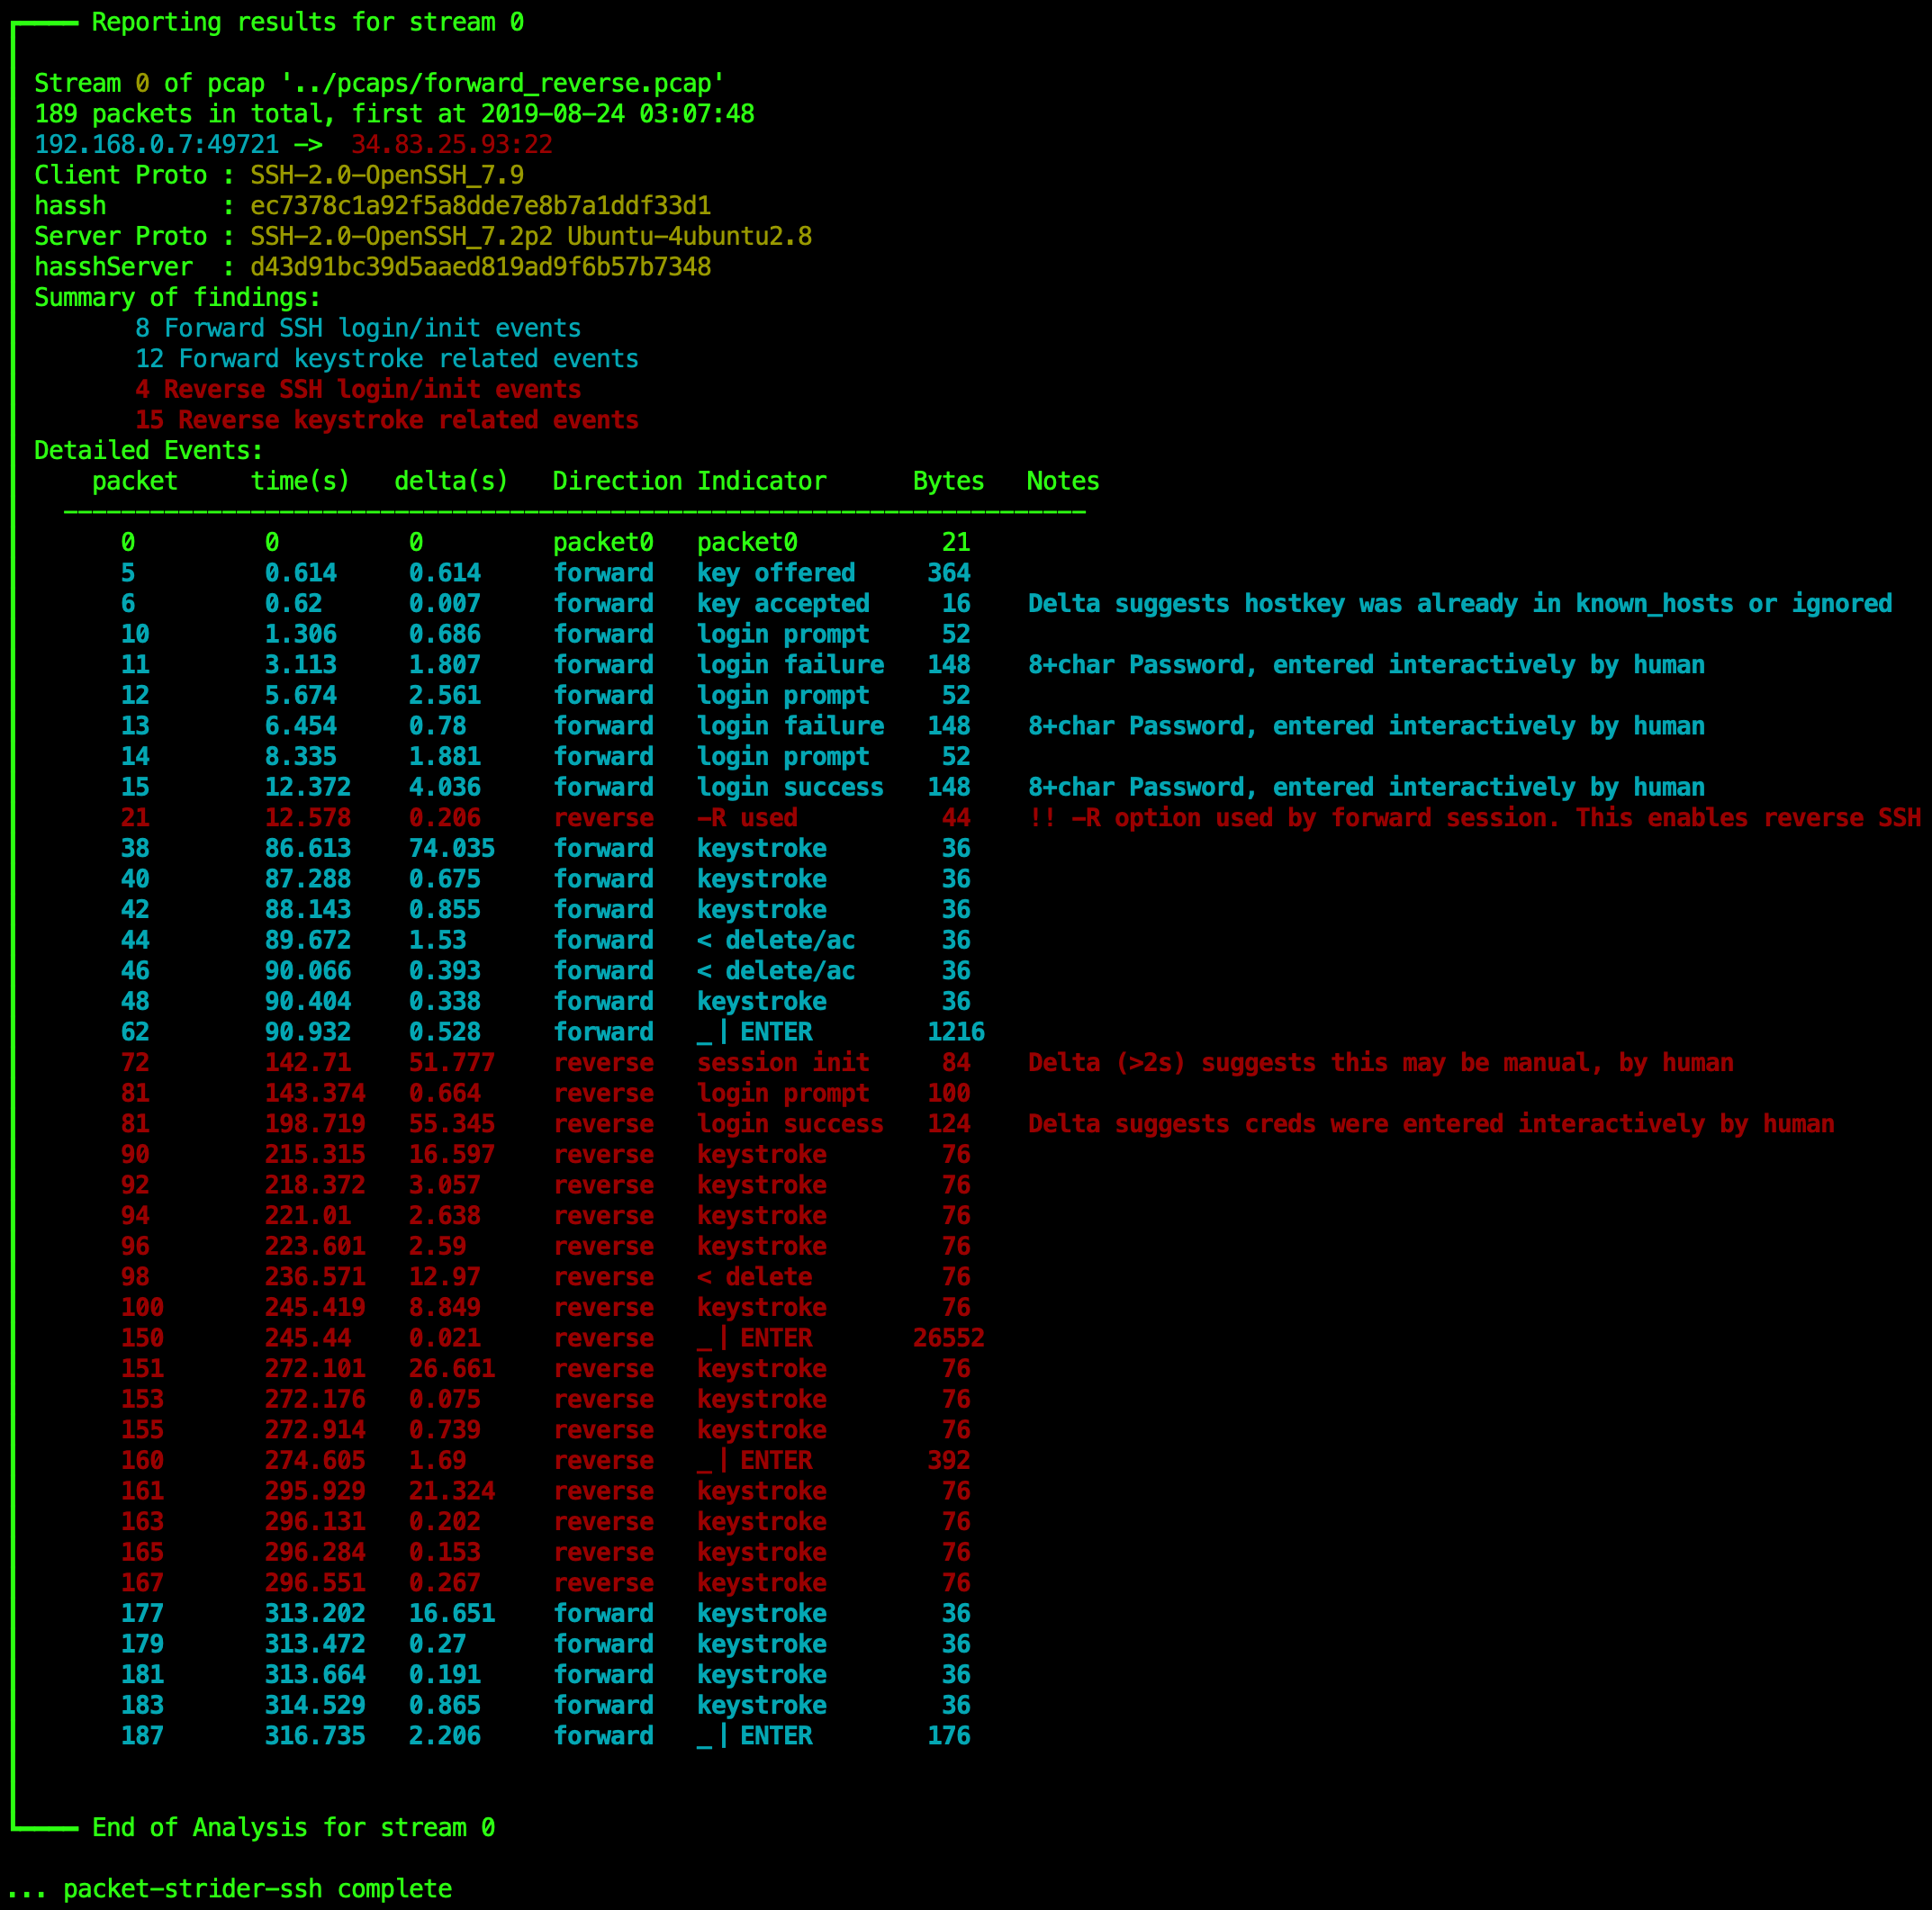
A network packet forensics tool for SSH

A collection of scripts for processing network forensics type data and intelligence, mainly into a postgres database.

PowerShell script that monitors Windows DNS traffic via pktmon to detect poisoning, spoofing, rogue resolver responses, and gateway MAC changes,…

Indicators of Compromise and hunting guidance for CVE-2026-88771, an unauthenticated command injection in Citrix NetScaler ADC and Gateway, covering…

Zeek support for Community ID flow hashing.

Python-based interactive packet manipulation library for forging, decoding, sending, capturing, and analyzing network packets across a wide range of…

A tool to analyze the network flow during attack/defence Capture the Flag competitions