

netsniff-ng
 netsniff-ng/netsniff-ng
A Swiss army knife for your daily Linux network plumbing.
network-forensicsnetwork-mappingnetwork-security+4
1.4k1 year ago
netsniff-ng/netsniff-ngA Swiss army knife for your daily Linux network plumbing.
 seladb/pcapplusplus
Multiplatform C++ library for high-performance network packet capture, parsing, crafting, and analysis. Supports libpcap, DPDK, AF_XDP, PF_RING, and…
 sydsec/syd
Offline AI Security Assistant for Air-Gapped Pentesting
 wireshark/wireshark
Capture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…
 zeek/zeek
Zeek is a powerful network analysis framework that is much different from the typical IDS you may know.
 watchtowrlabs/citrix-netscaler-cve-2026-88771-iocs
Indicators of Compromise and hunting guidance for CVE-2026-88771, an unauthenticated command injection in Citrix NetScaler ADC and Gateway, covering…
 stamparm/maltrail
Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
 arkime/arkime
Arkime is an open source, large scale, full packet capturing, indexing, and database system.

 microlaser/dns_watchdog_windows2
PowerShell script that monitors Windows DNS traffic via pktmon to detect poisoning, spoofing, rogue resolver responses, and gateway MAC changes,…
 capesandbox/capesolo
Standalone Windows VM malware sandbox running capemon, with GUI triage viewer, YARA signatures, IOC extraction, network analysis, and…
 secdev/scapy
Python-based interactive packet manipulation library for forging, decoding, sending, capturing, and analyzing network packets across a wide range of…


 wireshark/wireshark
Wireshark's official code repository. You can keep the releases coming by donating at https://wiresharkfoundation.org/donate/.
 corelight/zeek-spicy-ospf
A Zeek OSPF packet analyzer based on Spicy.
 gosecure/pyrdp
RDP monster-in-the-middle (mitm) and library for Python with the ability to watch connections live or after the fact
 gamelinux/passivedns
A network sniffer that logs all DNS server replies for use in a passive DNS setup
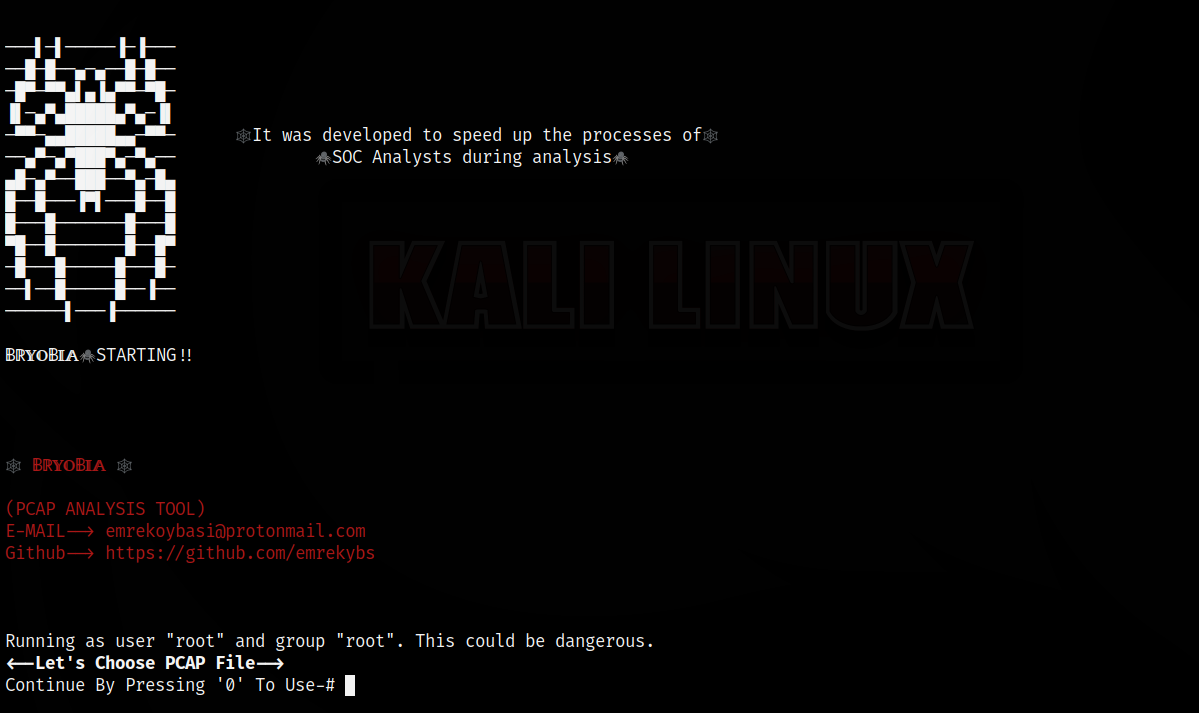 emrekybs/bryobio
It was developed to speed up the processes of SOC Analysts during analysis