

scapy
 secdev/scapy
Python-based interactive packet manipulation library for forging, decoding, sending, capturing, and analyzing network packets across a wide range of…
bluetooth-securitycryptographydata-exfiltration+23
12.6k
secdev/scapyPython-based interactive packet manipulation library for forging, decoding, sending, capturing, and analyzing network packets across a wide range of…
 ntop/ntopng
Web-based Traffic and Cybersecurity Network Traffic Monitoring
 srixivas/pcapxray
❄️ PcapXray - A Network Forensics Tool - To visualize a Packet Capture offline as a Network Diagram including device identification, highlight…
 0x4d31/fatt
FATT /fingerprintAllTheThings - a pyshark based script for extracting network metadata and fingerprints from pcap files and live network traffic
 halildeniz/networkassessment
NetworkAssessment: Network Compromise Assessment Tool
 zeek/zeek
Zeek is a powerful network analysis framework that is much different from the typical IDS you may know.
 wireshark/wireshark
Capture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…
 oisf/suricata
Open-source network IDS/IPS/NSM engine for real-time traffic inspection, intrusion detection and prevention, protocol analysis, and rule-based threat…
 google/grr
Remote live forensics and incident response framework with Python agent for collecting forensic data from endpoints, including memory, disk, and…

 seladb/pcapplusplus
Multiplatform C++ library for high-performance network packet capture, parsing, crafting, and analysis. Supports libpcap, DPDK, AF_XDP, PF_RING, and…
 cisagov/malcolm
Containerized network traffic analysis suite ingesting PCAP, Zeek logs, and Suricata alerts for automated normalization, enrichment, and correlation…
 usarmyresearchlab/dshell
Dshell is a network forensic analysis framework.

 wireshark/wireshark
Wireshark's official code repository. You can keep the releases coming by donating at https://wiresharkfoundation.org/donate/.
 mikeroyal/digital-forensics-guide
Digital Forensics Guide. Learn all about Digital Forensics, Computer Forensics, Mobile device Forensics, Network Forensics, and Database Forensics.
 foxio-llc/ja4
JA4+ is a suite of network fingerprinting standards
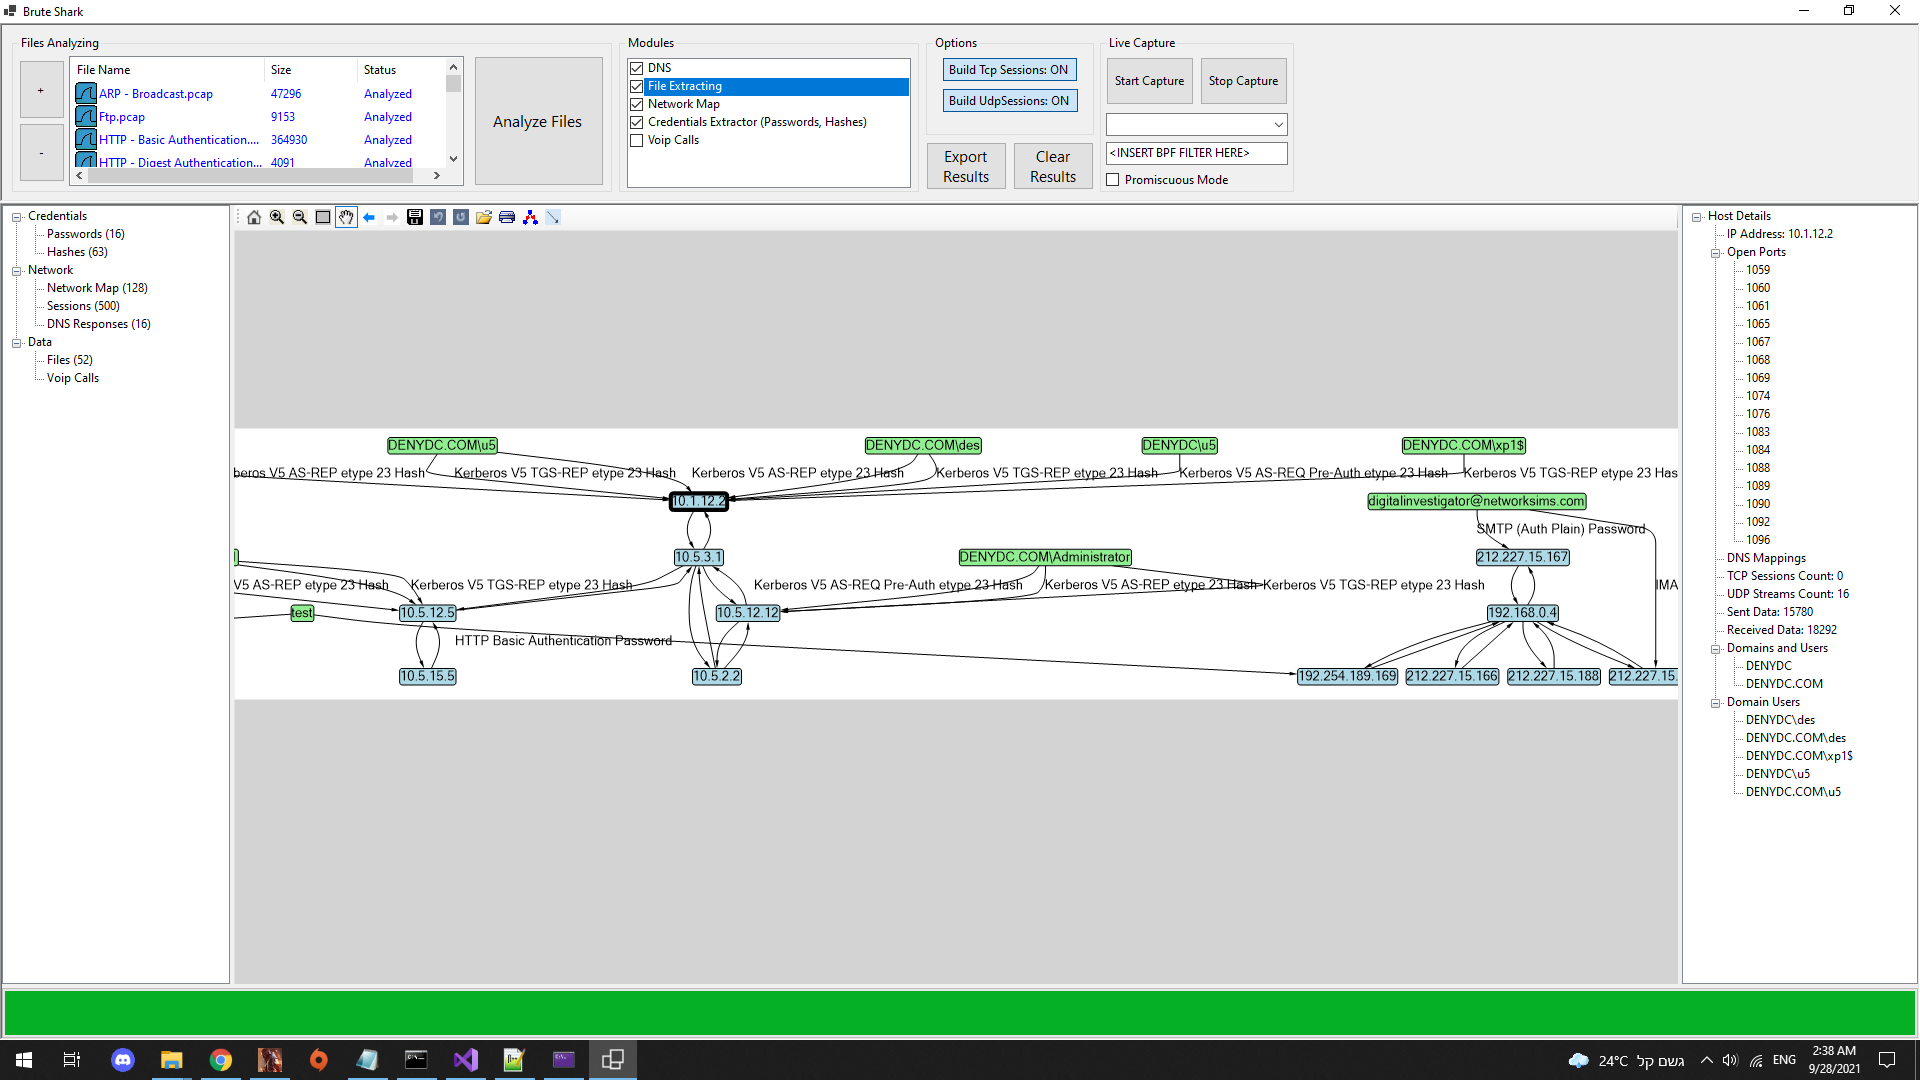
 gamelinux/passivedns
A network sniffer that logs all DNS server replies for use in a passive DNS setup