

timesketch
 google/timesketch
Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…
data-recoverydigital-forensicsdisk-forensics+7
3.4k
google/timesketchCollaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…
 security-onion-solutions/securityonion
Open-source security monitoring platform for threat hunting, intrusion detection, log management, incident response, and endpoint visibility with…
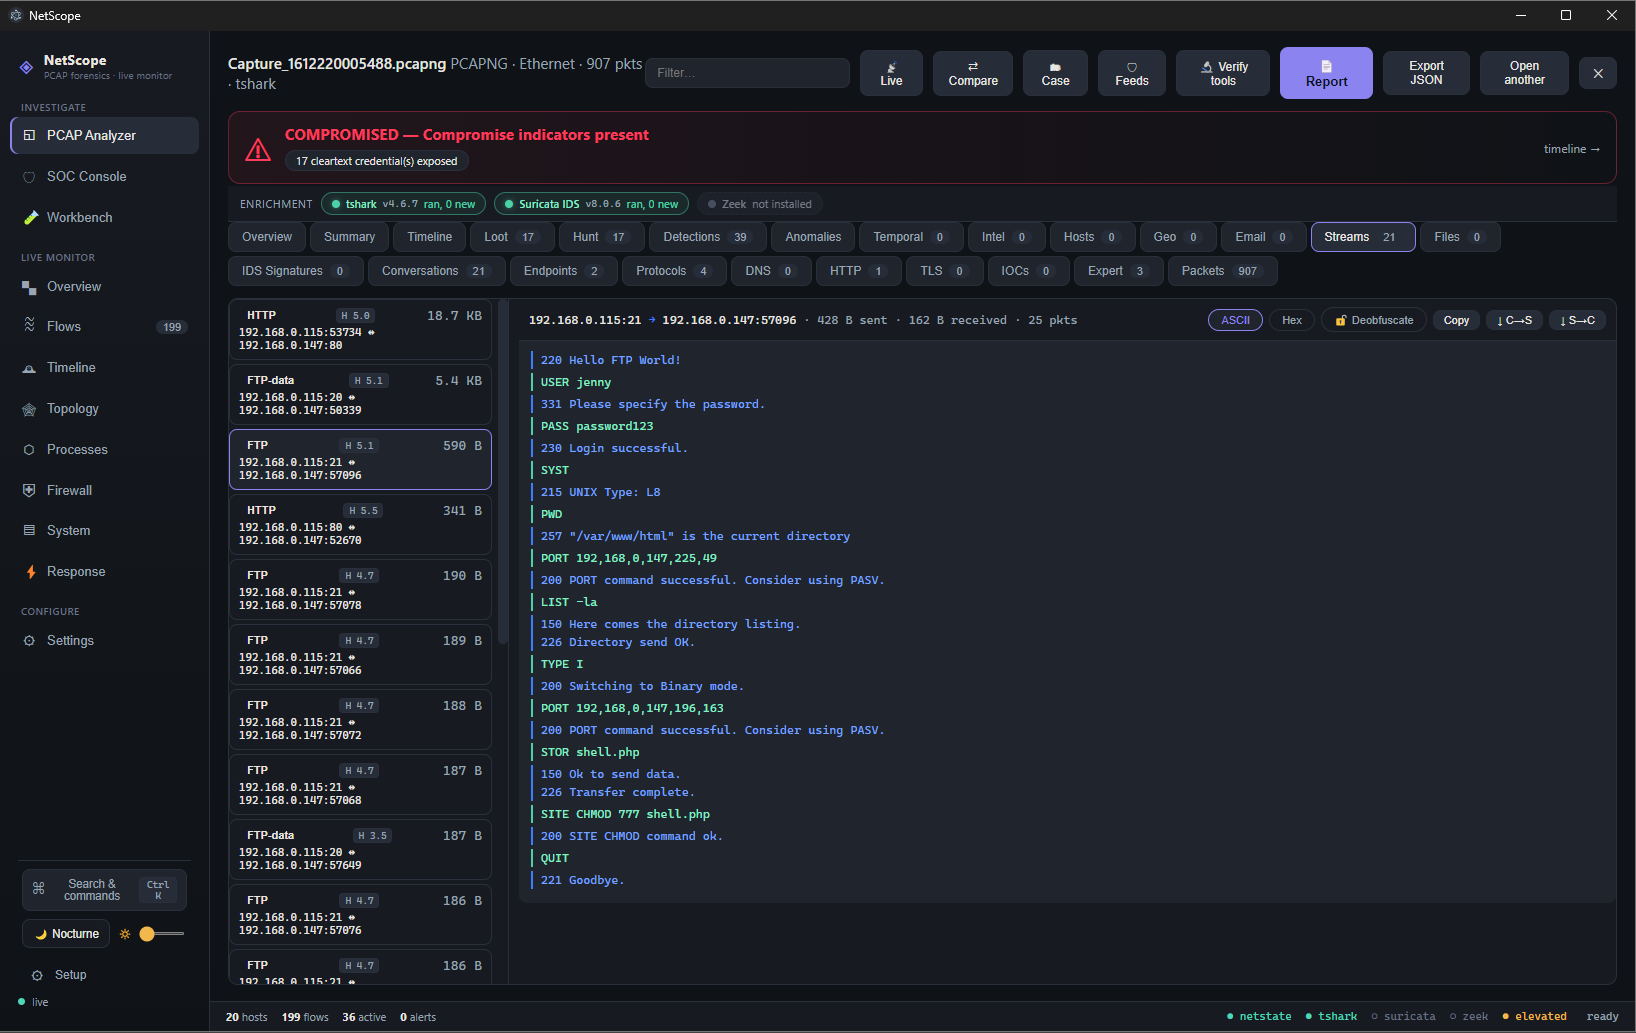 spectralzero/netscope
Offline-first network investigation and response platform for Windows. Turns a pcap or live capture into a full forensic verdict — attack story,…
 mozilla/mig
Distributed & real time digital forensics at the speed of the cloud
 frankwxu/digital-forensics-lab
Free hands-on digital forensics labs for students and faculty
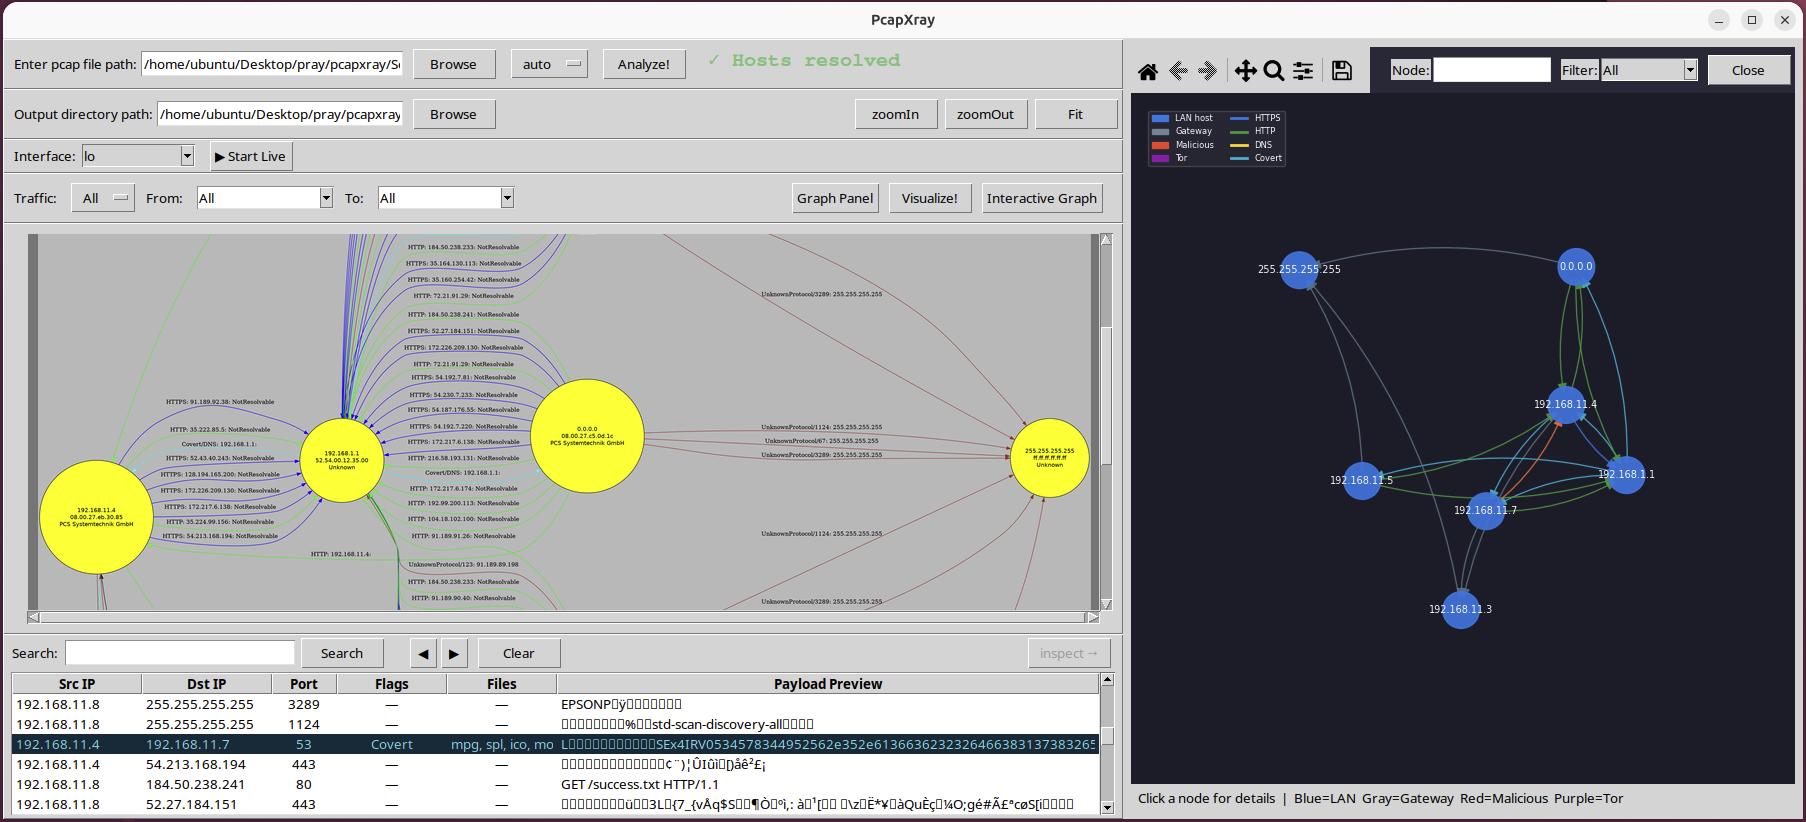 srixivas/pcapxray
❄️ PcapXray - A Network Forensics Tool - To visualize a Packet Capture offline as a Network Diagram including device identification, highlight…
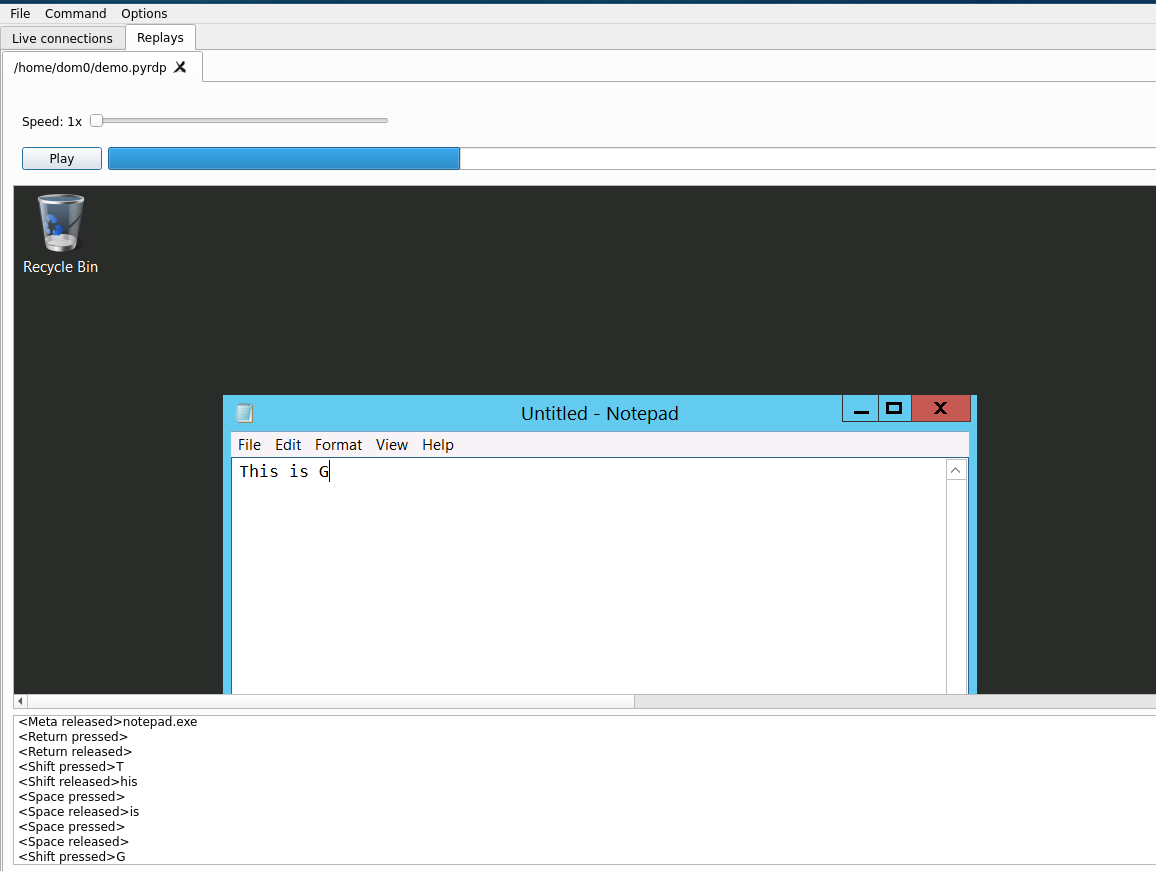 gosecure/pyrdp
RDP monster-in-the-middle (mitm) and library for Python with the ability to watch connections live or after the fact
 azr43lkn1ght/dfir-labs
Hands-on DFIR challenges covering digital forensics, incident response, malware analysis, and threat hunting with CTF-style flags and real-world…
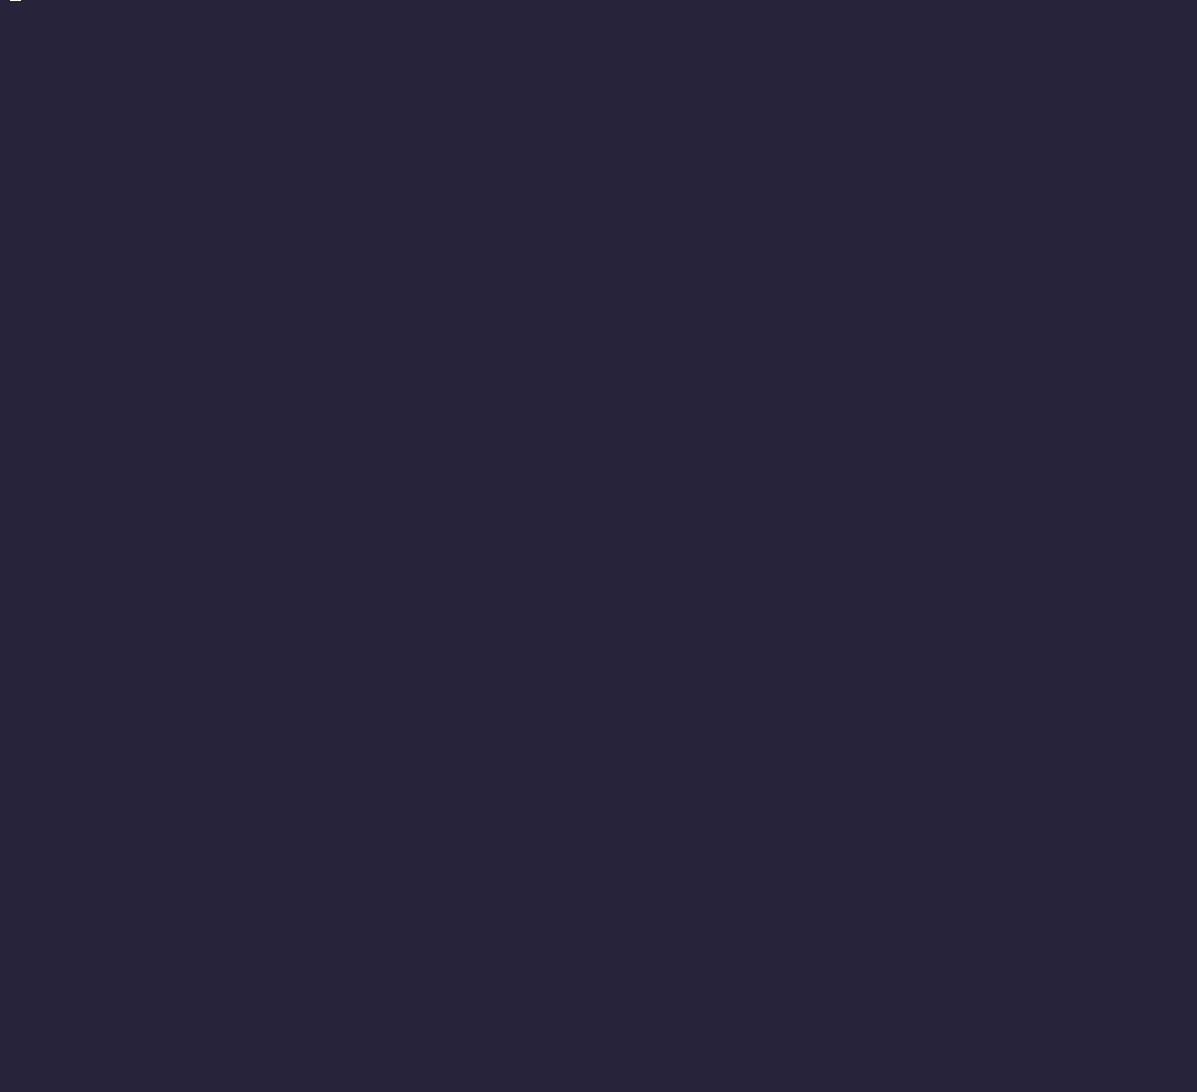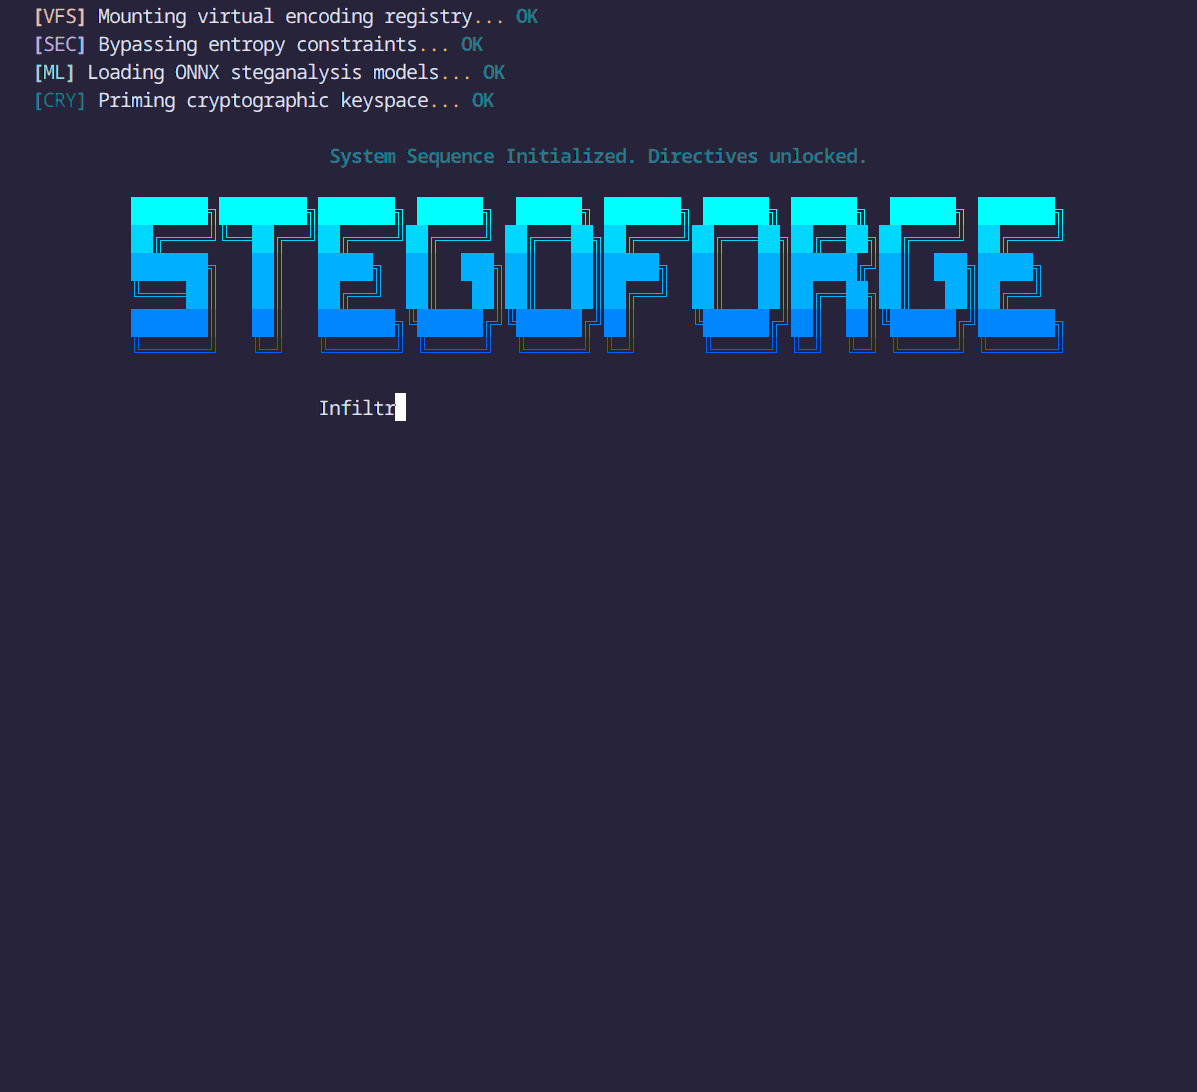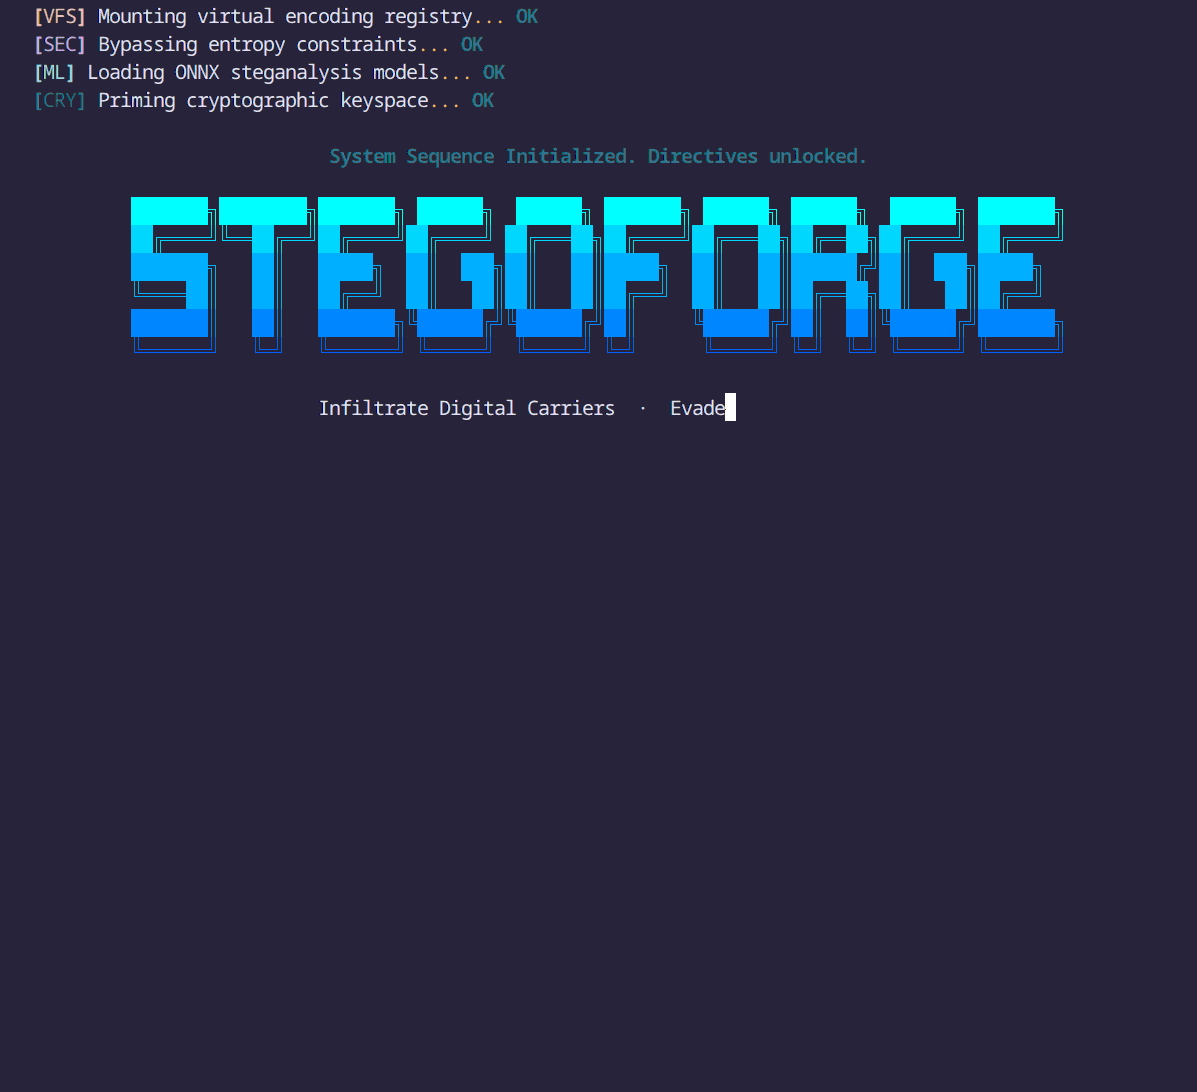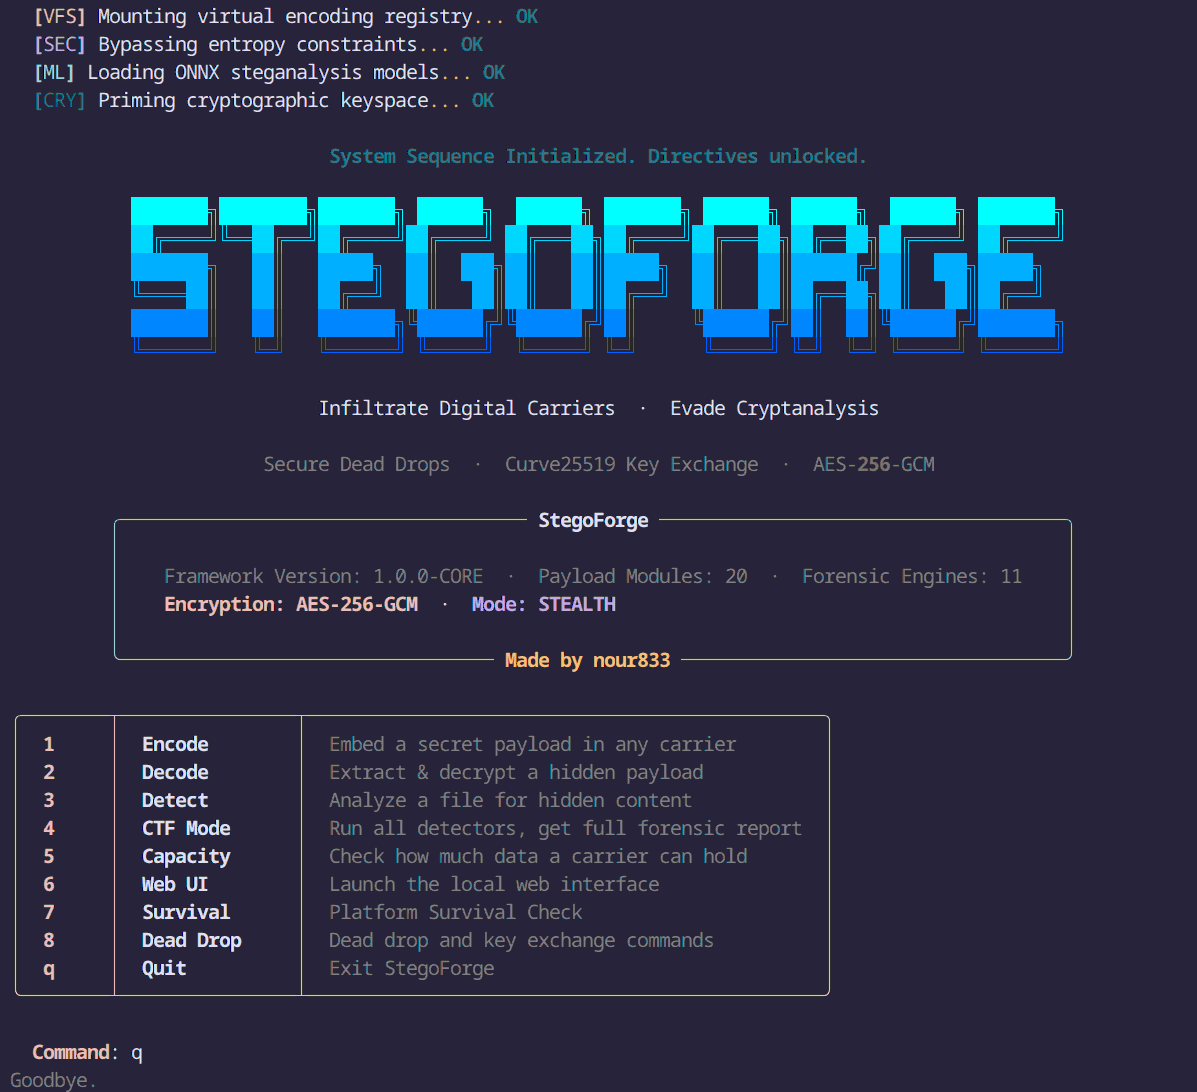 nour833/stegoforge
The ultimate steganography and digital forensics toolkit. Hide and extract data across images, audio, video, documents, and network packets, or run…
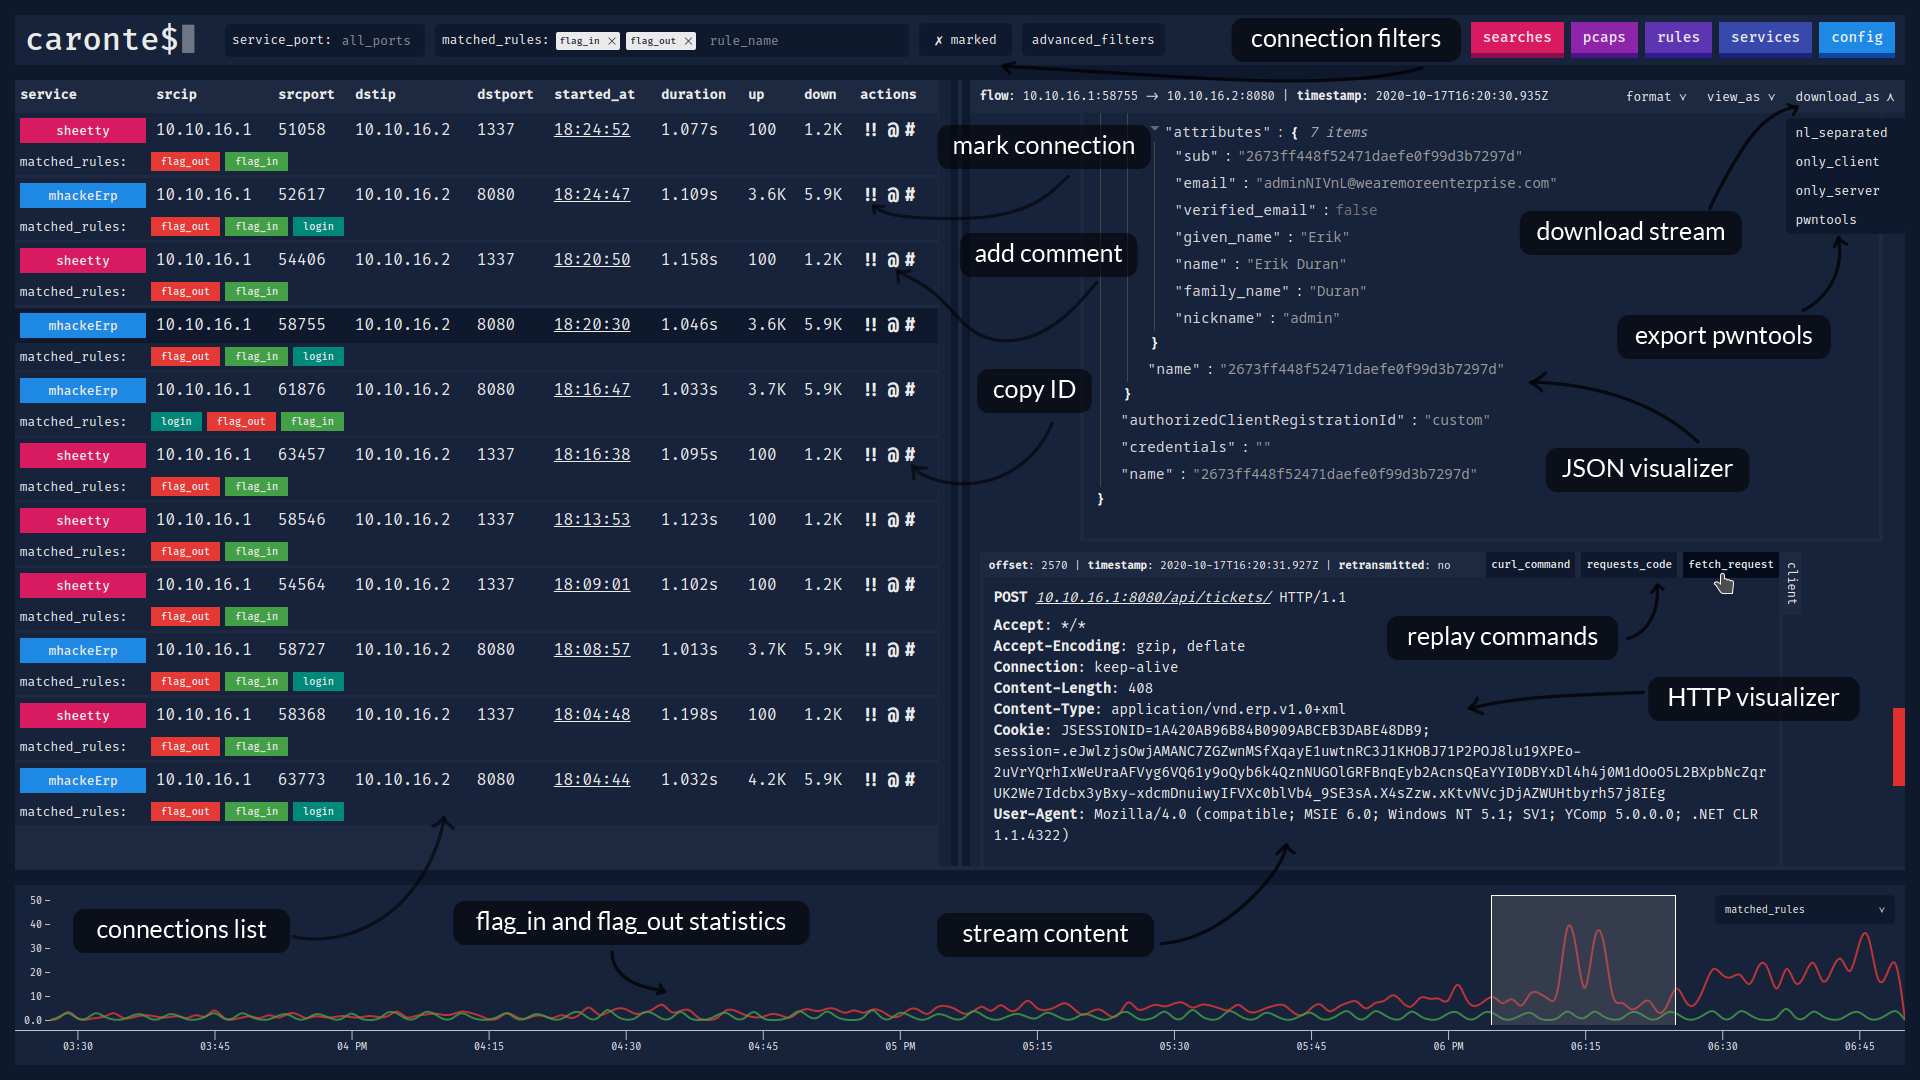 eciavatta/caronte
A tool to analyze the network flow during attack/defence Capture the Flag competitions
 weirdmachine64/sharkmcp
A swiss-knife MCP server for analysing PCAP files
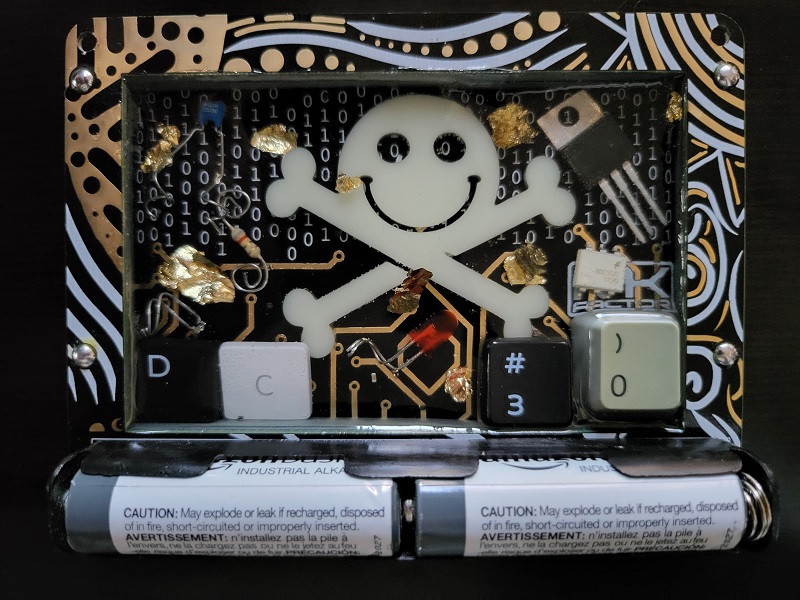 kybr-git/dc30-badge-challenge-writeup
Writeup for the DEF CON 30 badge challenge
 alzeaty1/security-writeups
CTF writeups and teaching scripts for web security, bug bounty techniques, and network forensics, with blank-value versions for active practice.
 mohamedbrek/soc335-cve-2024-49138-exploitation-detected
LetsDefend SOC lab investigating CVE-2024-49138 exploitation and related malicious activity.
 pugazhendii22/keepass-exfil-forensics
Network forensics writeup + tooling for a TryHackMe DFIR challenge: reverses a hex→Base64→XOR exfiltration chain from PCAP traffic, then recovers a…
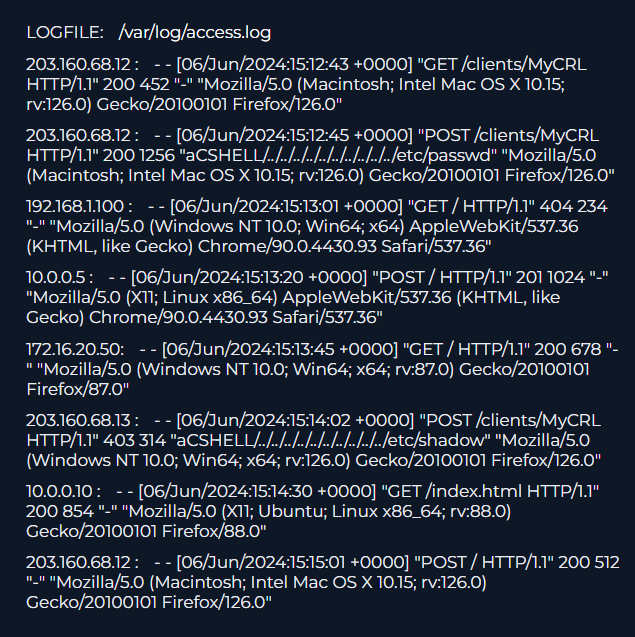 zedocun/incident-analysis-response-check-point-security-gateway-cve-2024-24919-lfi-exploitation
Incident Response (IR) case study documenting the investigation of an exploitation attempt targeting CVE-2024-24919 (Arbitrary File Read) on a Check…
 jhatchi/nexacorp-dfir-inc-2026-001
DFIR investigation + 7 Suricata rules on a simulated NexaCorp intrusion (vsftpd 2.3.4 CVE-2011-2523 + MITRE Caldera C2). 4-day solo engagement…
 trinadh-dasari-cyber/eternalblue-ms17-010-research
Controlled reproduction of CVE-2017-0144 (EternalBlue) in an isolated AWS EC2 lab — exploit analysis, Wireshark traffic capture, and MITRE ATT&CK…