windows-malware-behavioral-analysis

Behavioral Malware Analysis of a Simulated Multi-Stage Windows Malware Sample using FLARE-VM and REMnux. Evidence-driven DFIR investigation with IOC…

Behavioral Malware Analysis of a Simulated Multi-Stage Windows Malware Sample using FLARE-VM and REMnux. Evidence-driven DFIR investigation with IOC…

Hands-on DFIR challenges covering digital forensics, incident response, malware analysis, and threat hunting with CTF-style flags and real-world…

Blue-team analysis of a malicious DOCX exploiting CVE-2017-0199, covering sandbox detonation, network forensics, IOC extraction, MITRE ATT&CK…

Malware samples, analysis exercises and other interesting resources.

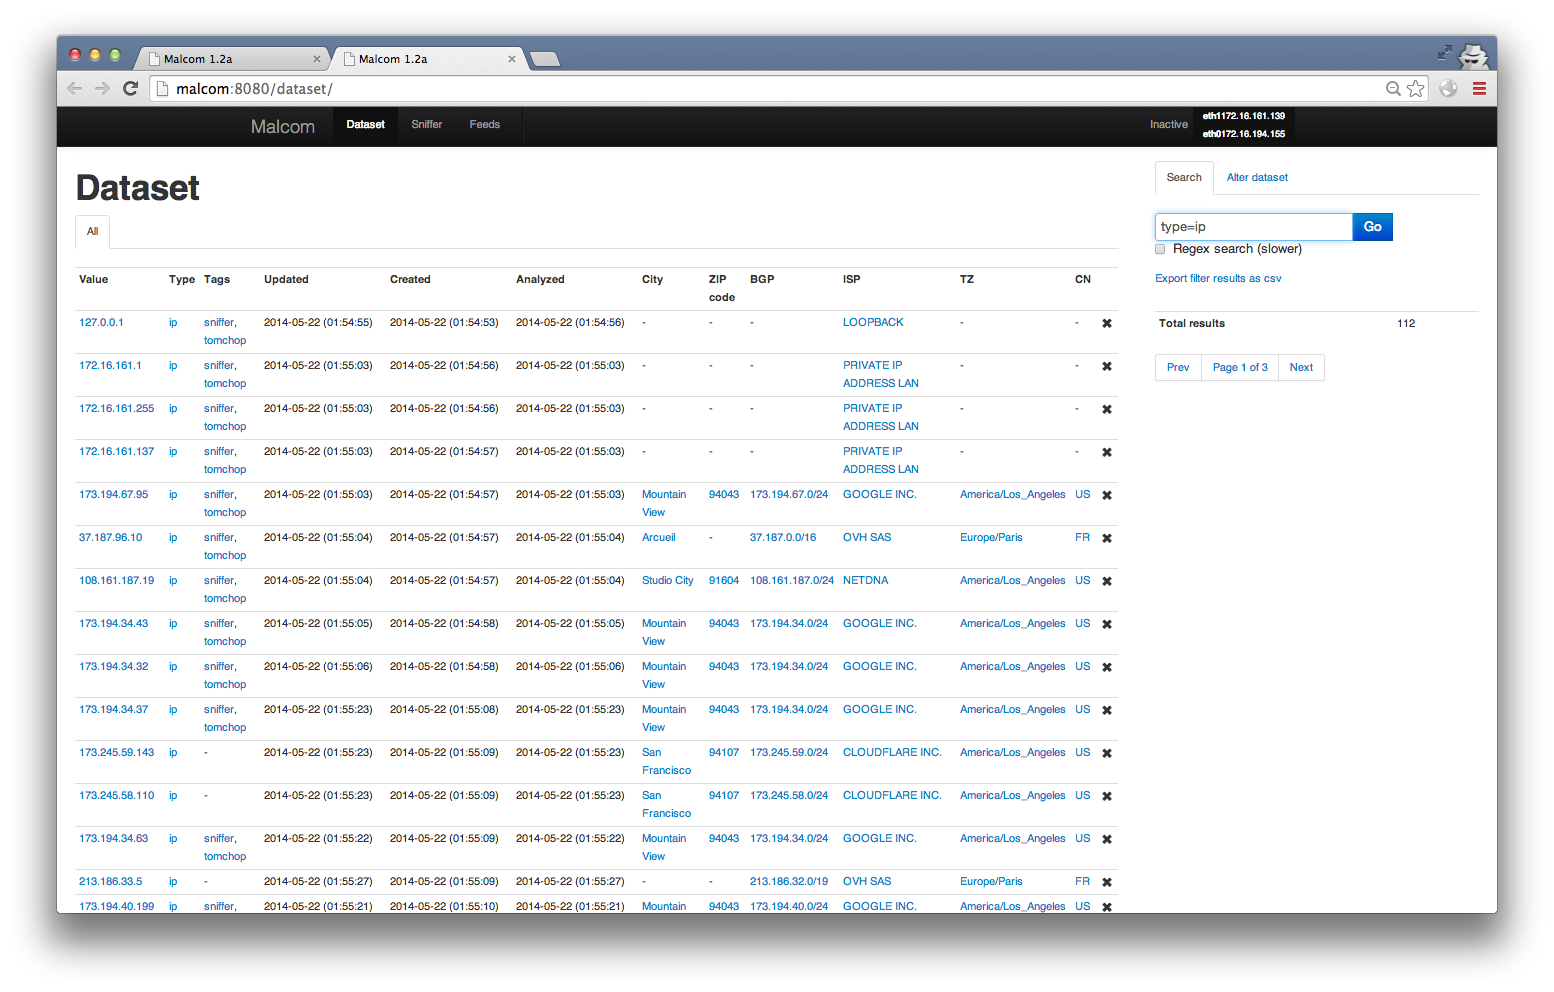
Malcom - Malware Communications Analyzer

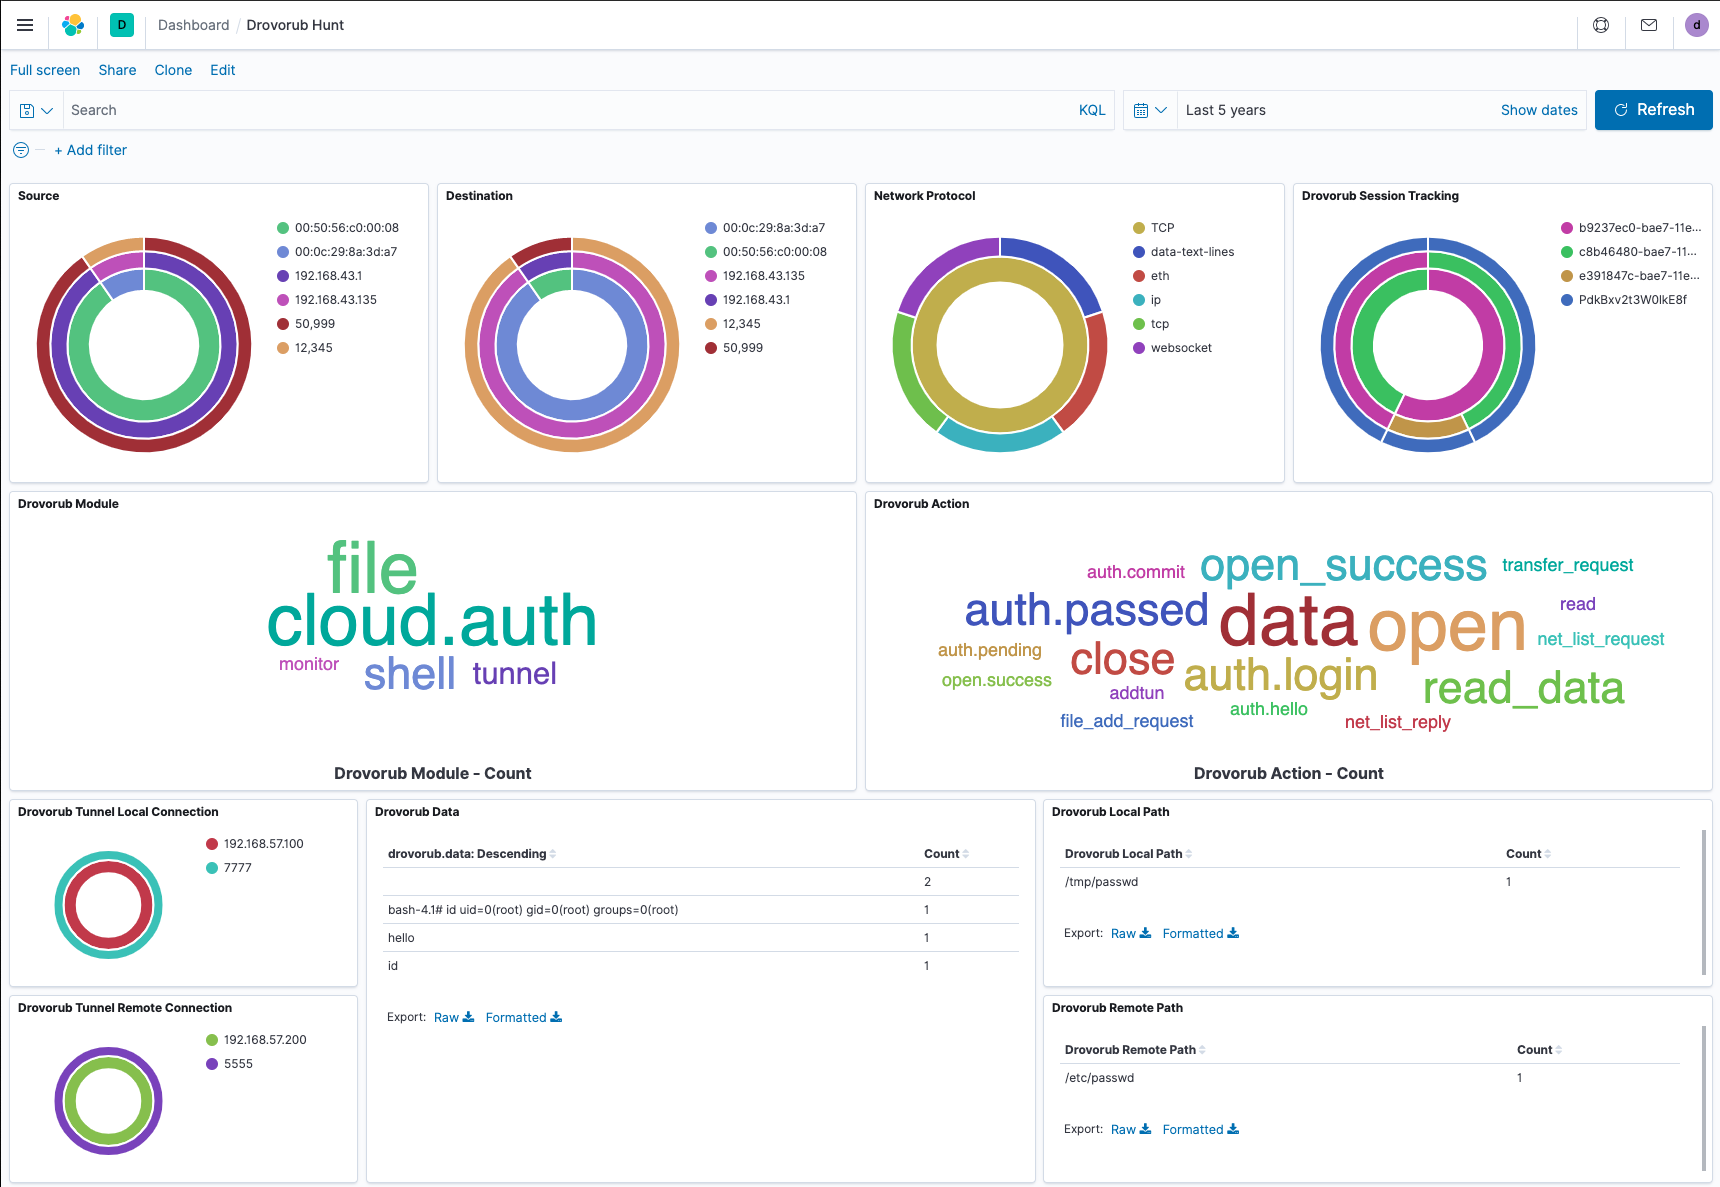
A tool to assist with network-based hunting for GRU's Drovorub malware c2

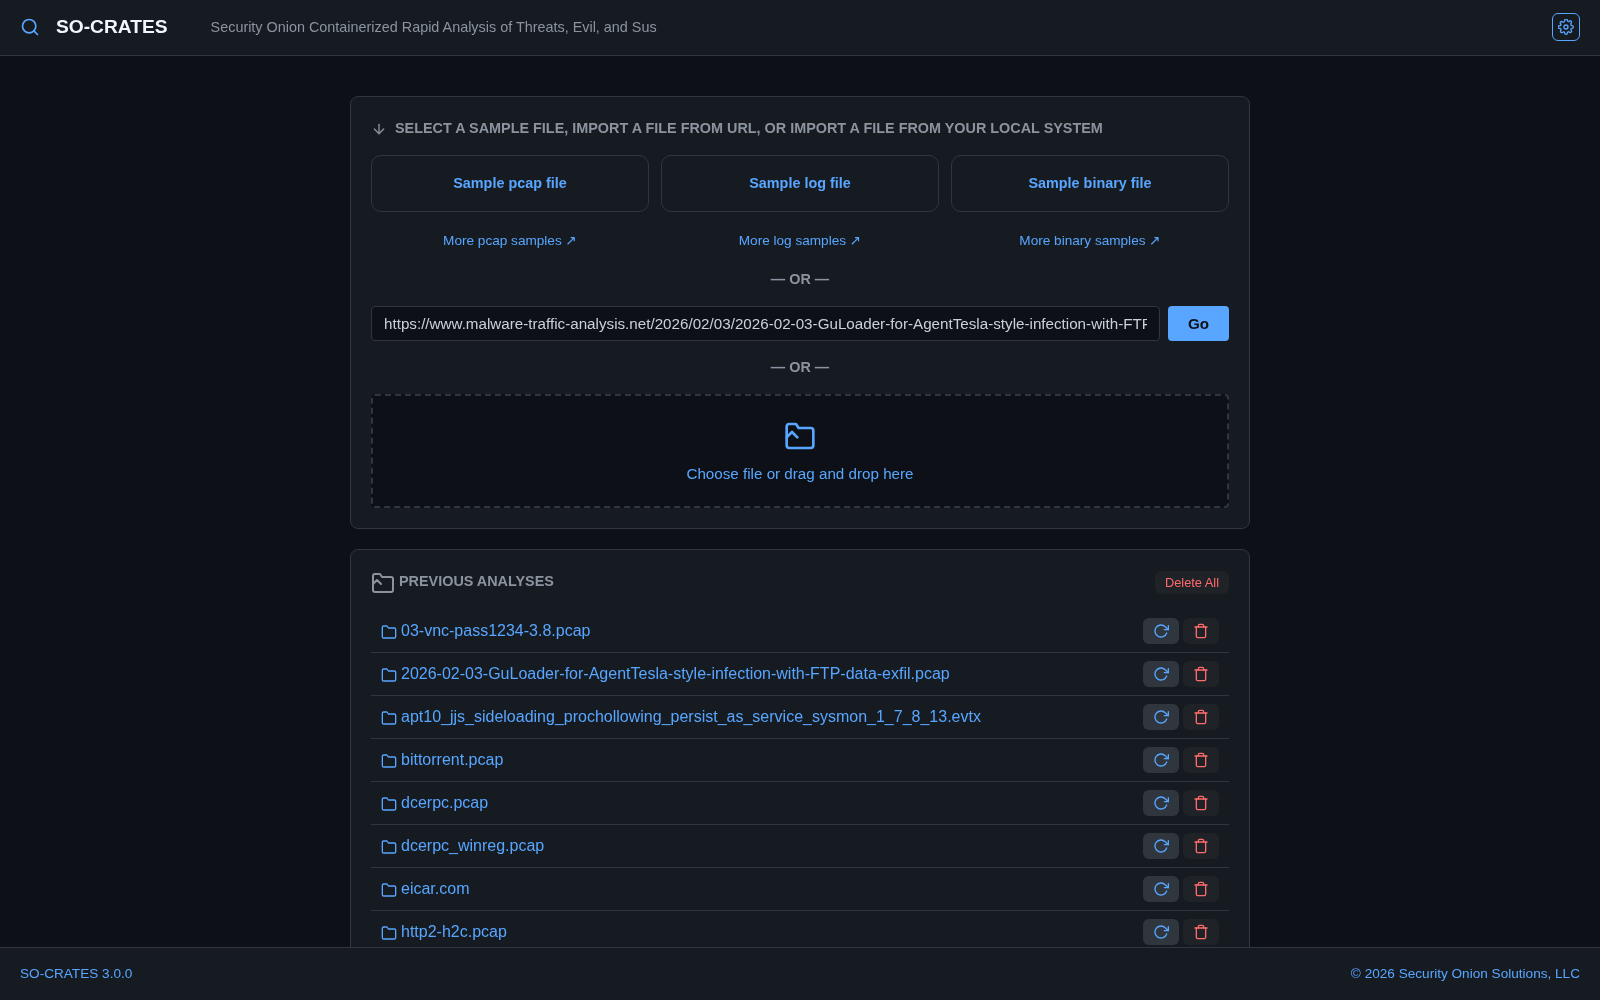
SO-CRATES: Security Onion Containerized Rapid Analysis of Threats, Evil, and Sus!

Wireshark plugin that correlates network traffic with threat intelligence, asset tags, and vulnerability data to accelerate forensic analysis of PCAP…

The Multiplatform Linux Sandbox

Breakdown of a c2-network of chinese beamers - SilentSDK-Analysis

End-to-end simulation of a Python dependency confusion attack, sudo privilege escalation (CVE-2025-32463), and rootkit-based persistence - with full…

Educational reverse engineering study of a Unity/IL2CPP Android game. Documents gateway protocol decoding, native anti-tampering SDK analysis, SSL…

Malware Configuration And Payload Extraction

A list of cyber-chef recipes and curated links

IOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…

JA4+ is a suite of network fingerprinting standards

Dissect is a digital forensics & incident response framework and toolset that allows you to quickly access and analyse forensic artefacts from…

Collection of forensic tools