HiddenNetworks-Python

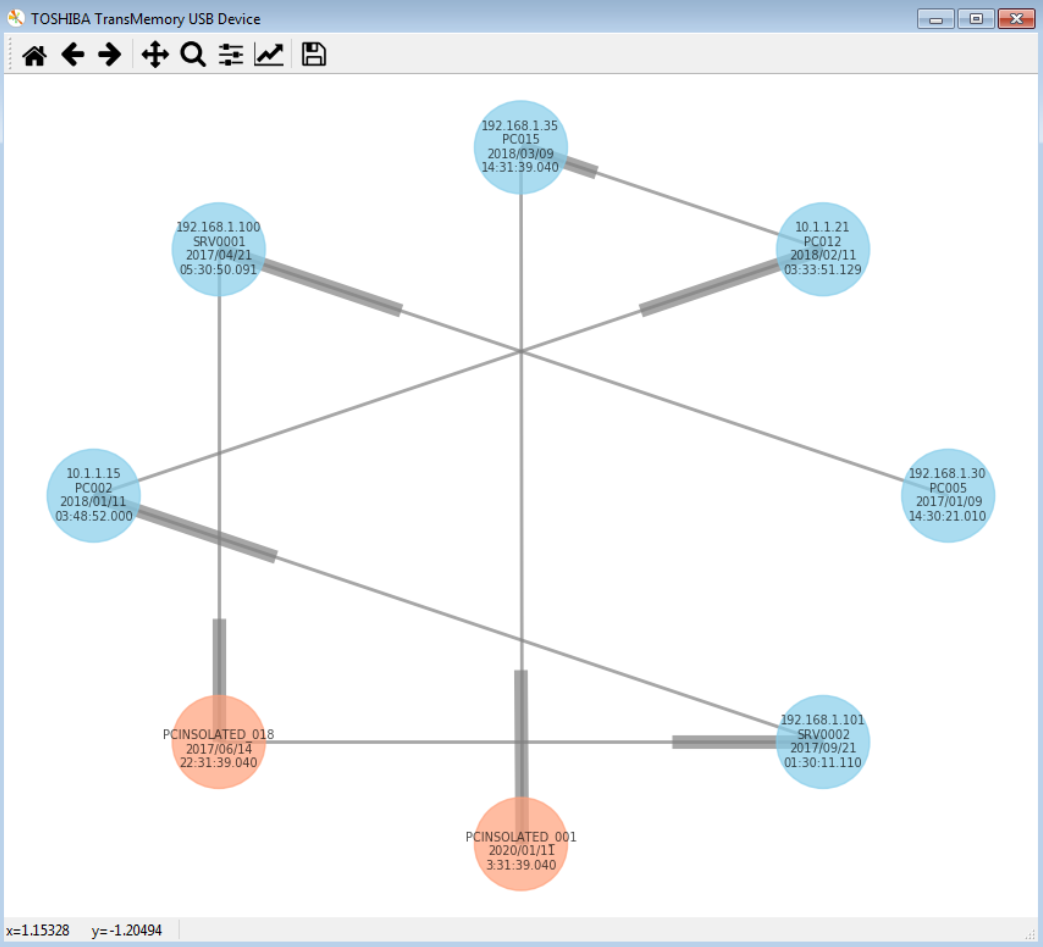
USB device connection forensics tool that traces physical device-to-computer relationships across local and domain networks, generating visual graphs…
digital-forensicsforensicsinformation-gathering+2
38


USB device connection forensics tool that traces physical device-to-computer relationships across local and domain networks, generating visual graphs…

Offline-first network investigation and response platform for Windows. Turns a pcap or live capture into a full forensic verdict — attack story,…

DFIR Timeline Analysis for macOS — SQLite-backed viewer for CSV, TSV, XLSX, EVTX, Plaso, $MFT, and $J files with AI Artifacts, AI Secret Hunt,…