
wireshark-rdp
 awakecoding/wireshark-rdp
Wireshark RDP resources
authenticationcurated-resourceseducation+3
awakecoding/wireshark-rdpWireshark RDP resources
 tsale/awesome-dfir-skills
A curated collection of DFIR skills and workflows for InfoSec practitioners.
 rjbhide/wireshark-forensics-plugin
Wireshark plugin that correlates network traffic with threat intelligence, asset tags, and vulnerability data to accelerate forensic analysis of PCAP…
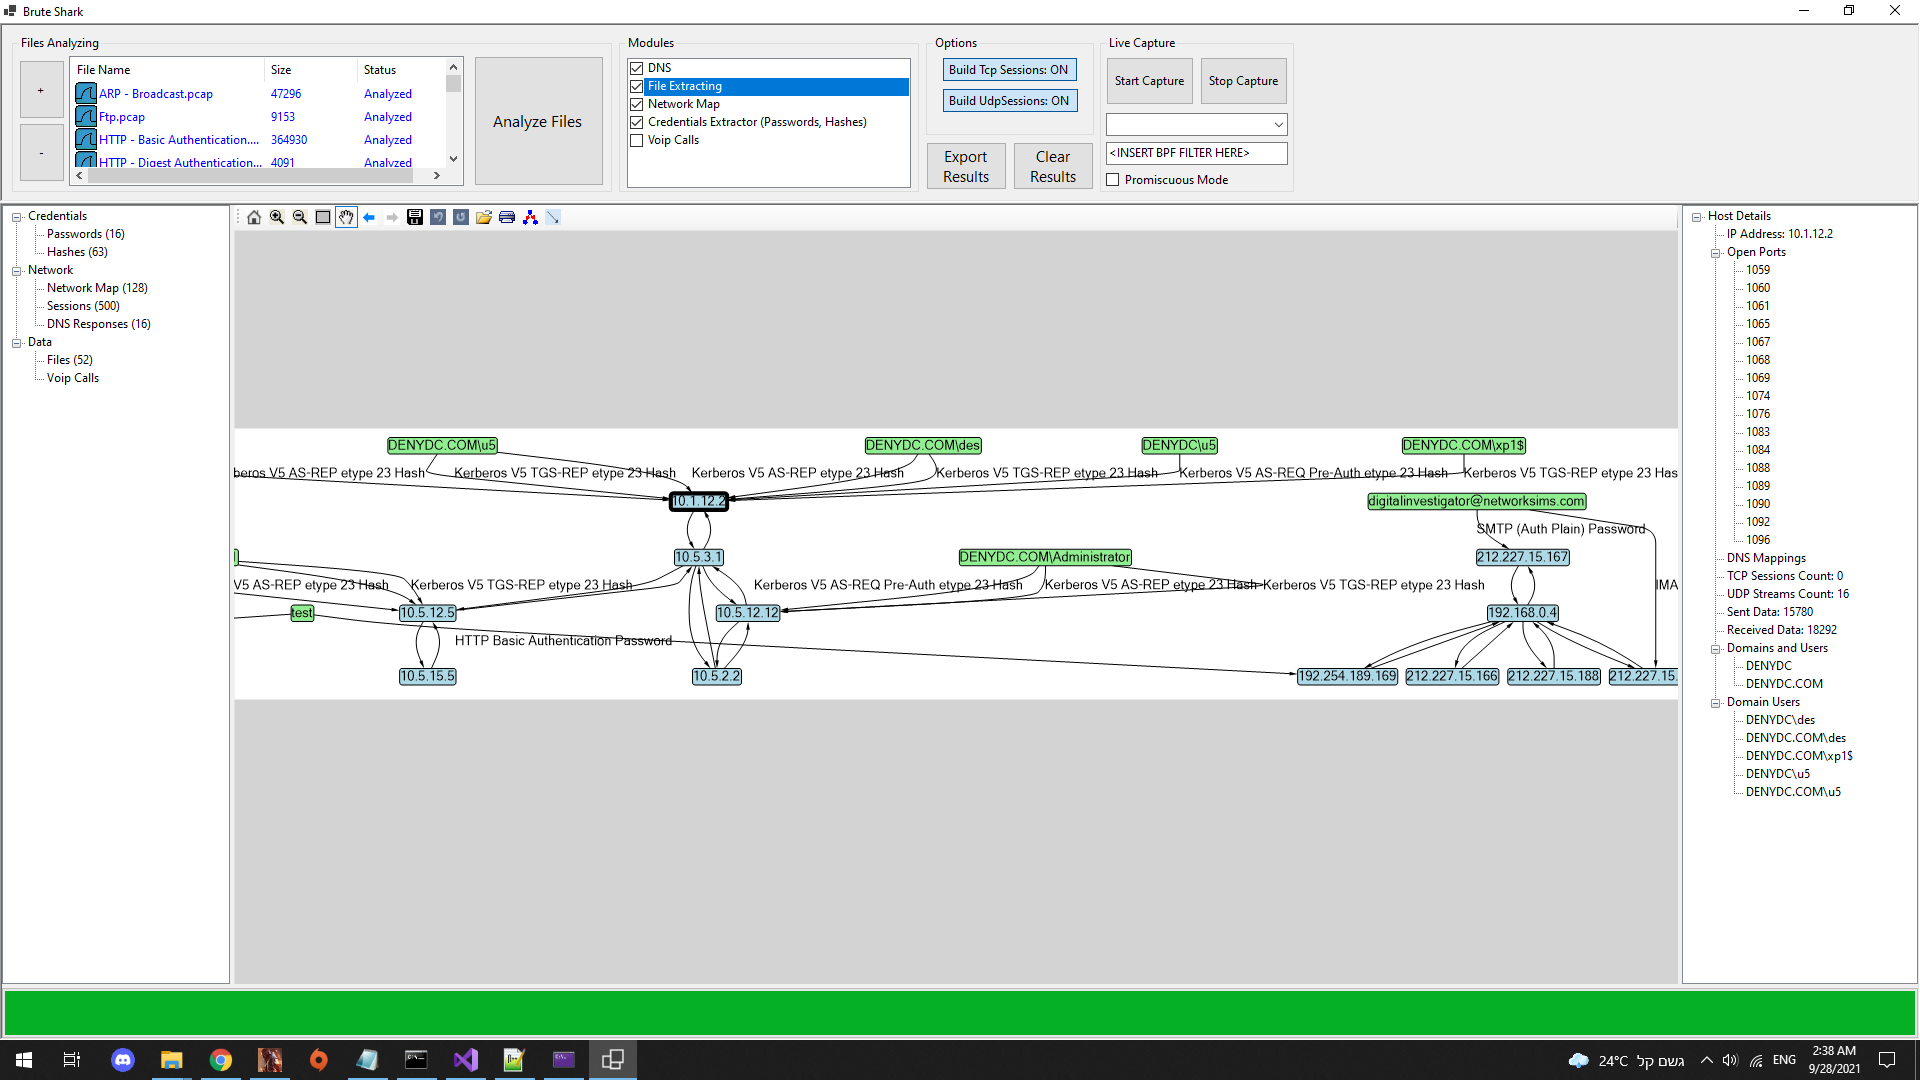
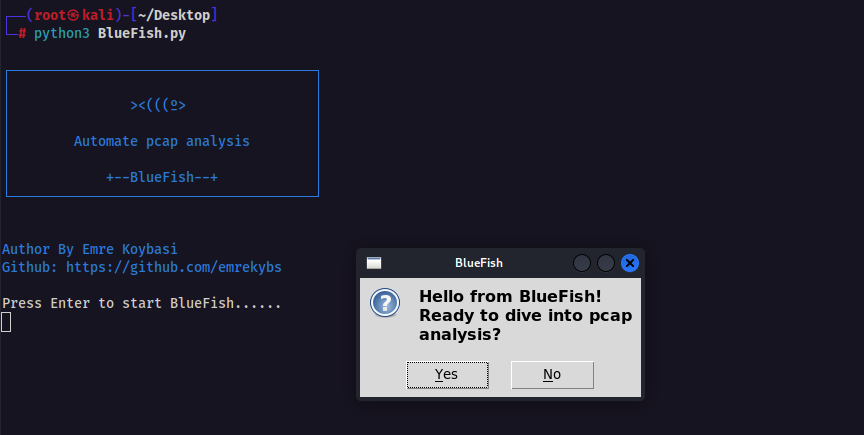 emrekybs/bluefish
Automation tool designed to simplify the analysis of PCAP (Packet Capture) files
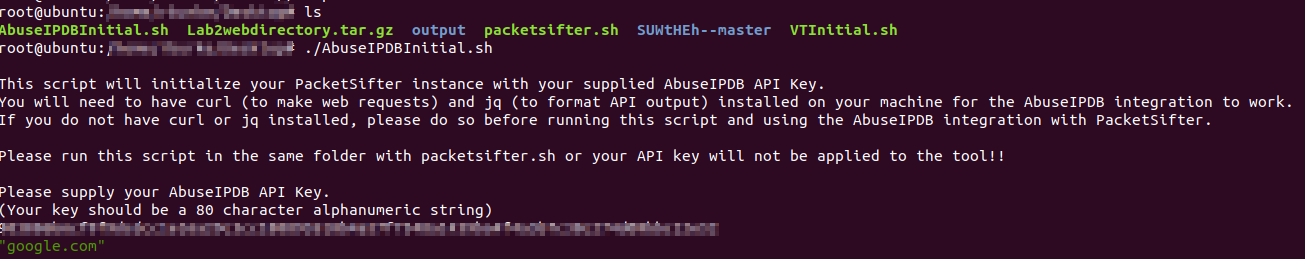 packetsifter/packetsiftertool
PacketSifter is a tool/script that is designed to aid analysts in sifting through a packet capture (pcap) to find noteworthy traffic. Packetsifter…
 nccgroup/baskerville
Selective protocol extractor from PCAPs or interfaces
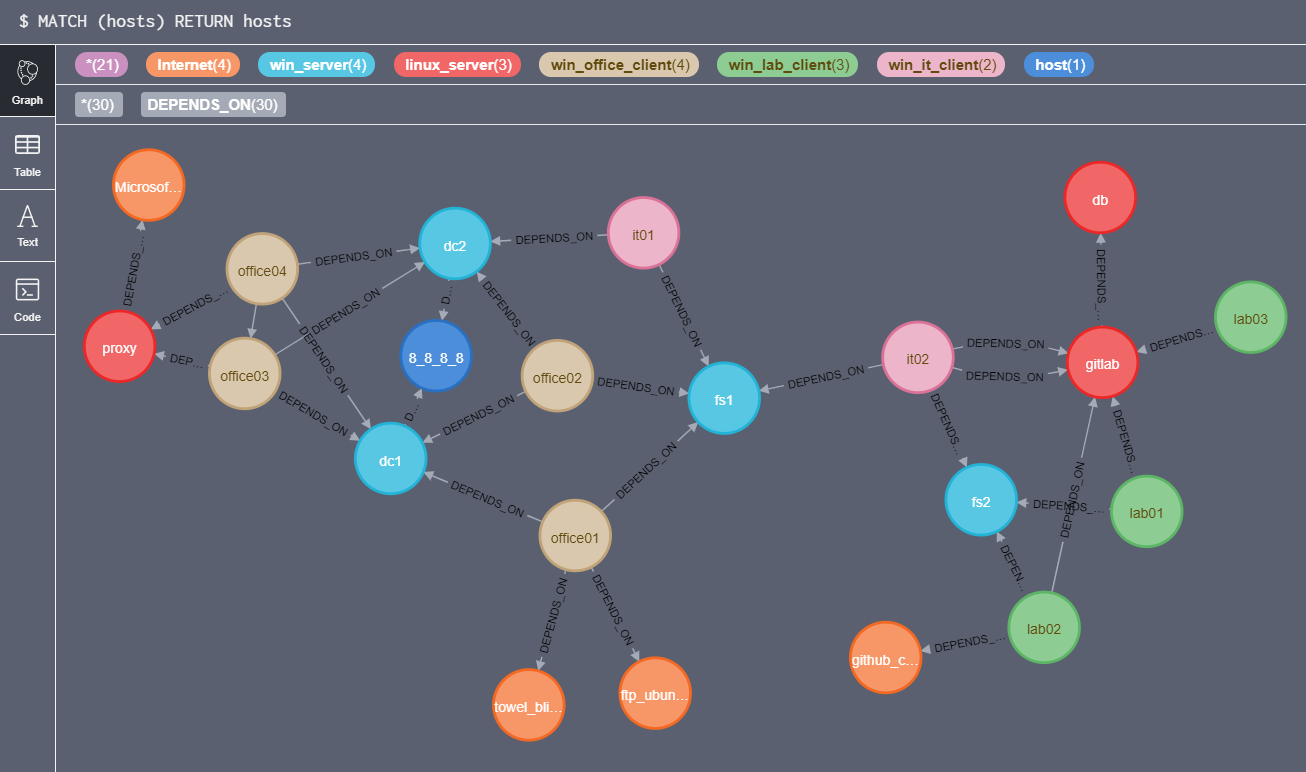 trinitor/netstat2neo4j
create cypher create statements for neo4j out of netstat files from multiple machines
 jstrosch/malware-samples
Malware samples, analysis exercises and other interesting resources.
 ahmed-tarek22752/rce-cve-2017-0199-detection-analysis
This repository contains a full blue-team malware analysis of a real malicious DOCX exploiting CVE-2017-0199. The lab includes sandbox execution,…
 z4l4mi/ipgeo
Extracts IP addresses from pcap/pcapng network traffic files and generates CSV reports with geolocation, ISP, and organizational details for each IP.
 dougburks/so-crates
SO-CRATES: Security Onion Containerized Rapid Analysis of Threats, Evil, and Sus!
 weirdmachine64/sharkmcp
A swiss-knife MCP server for analysing PCAP files
 idaholab/malcolm
Malcolm is a powerful, easily deployable network traffic analysis tool suite for full packet capture artifacts (PCAP files), Zeek logs and Suricata…
 0x4d31/fatt
FATT /fingerprintAllTheThings - a pyshark based script for extracting network metadata and fingerprints from pcap files and live network traffic
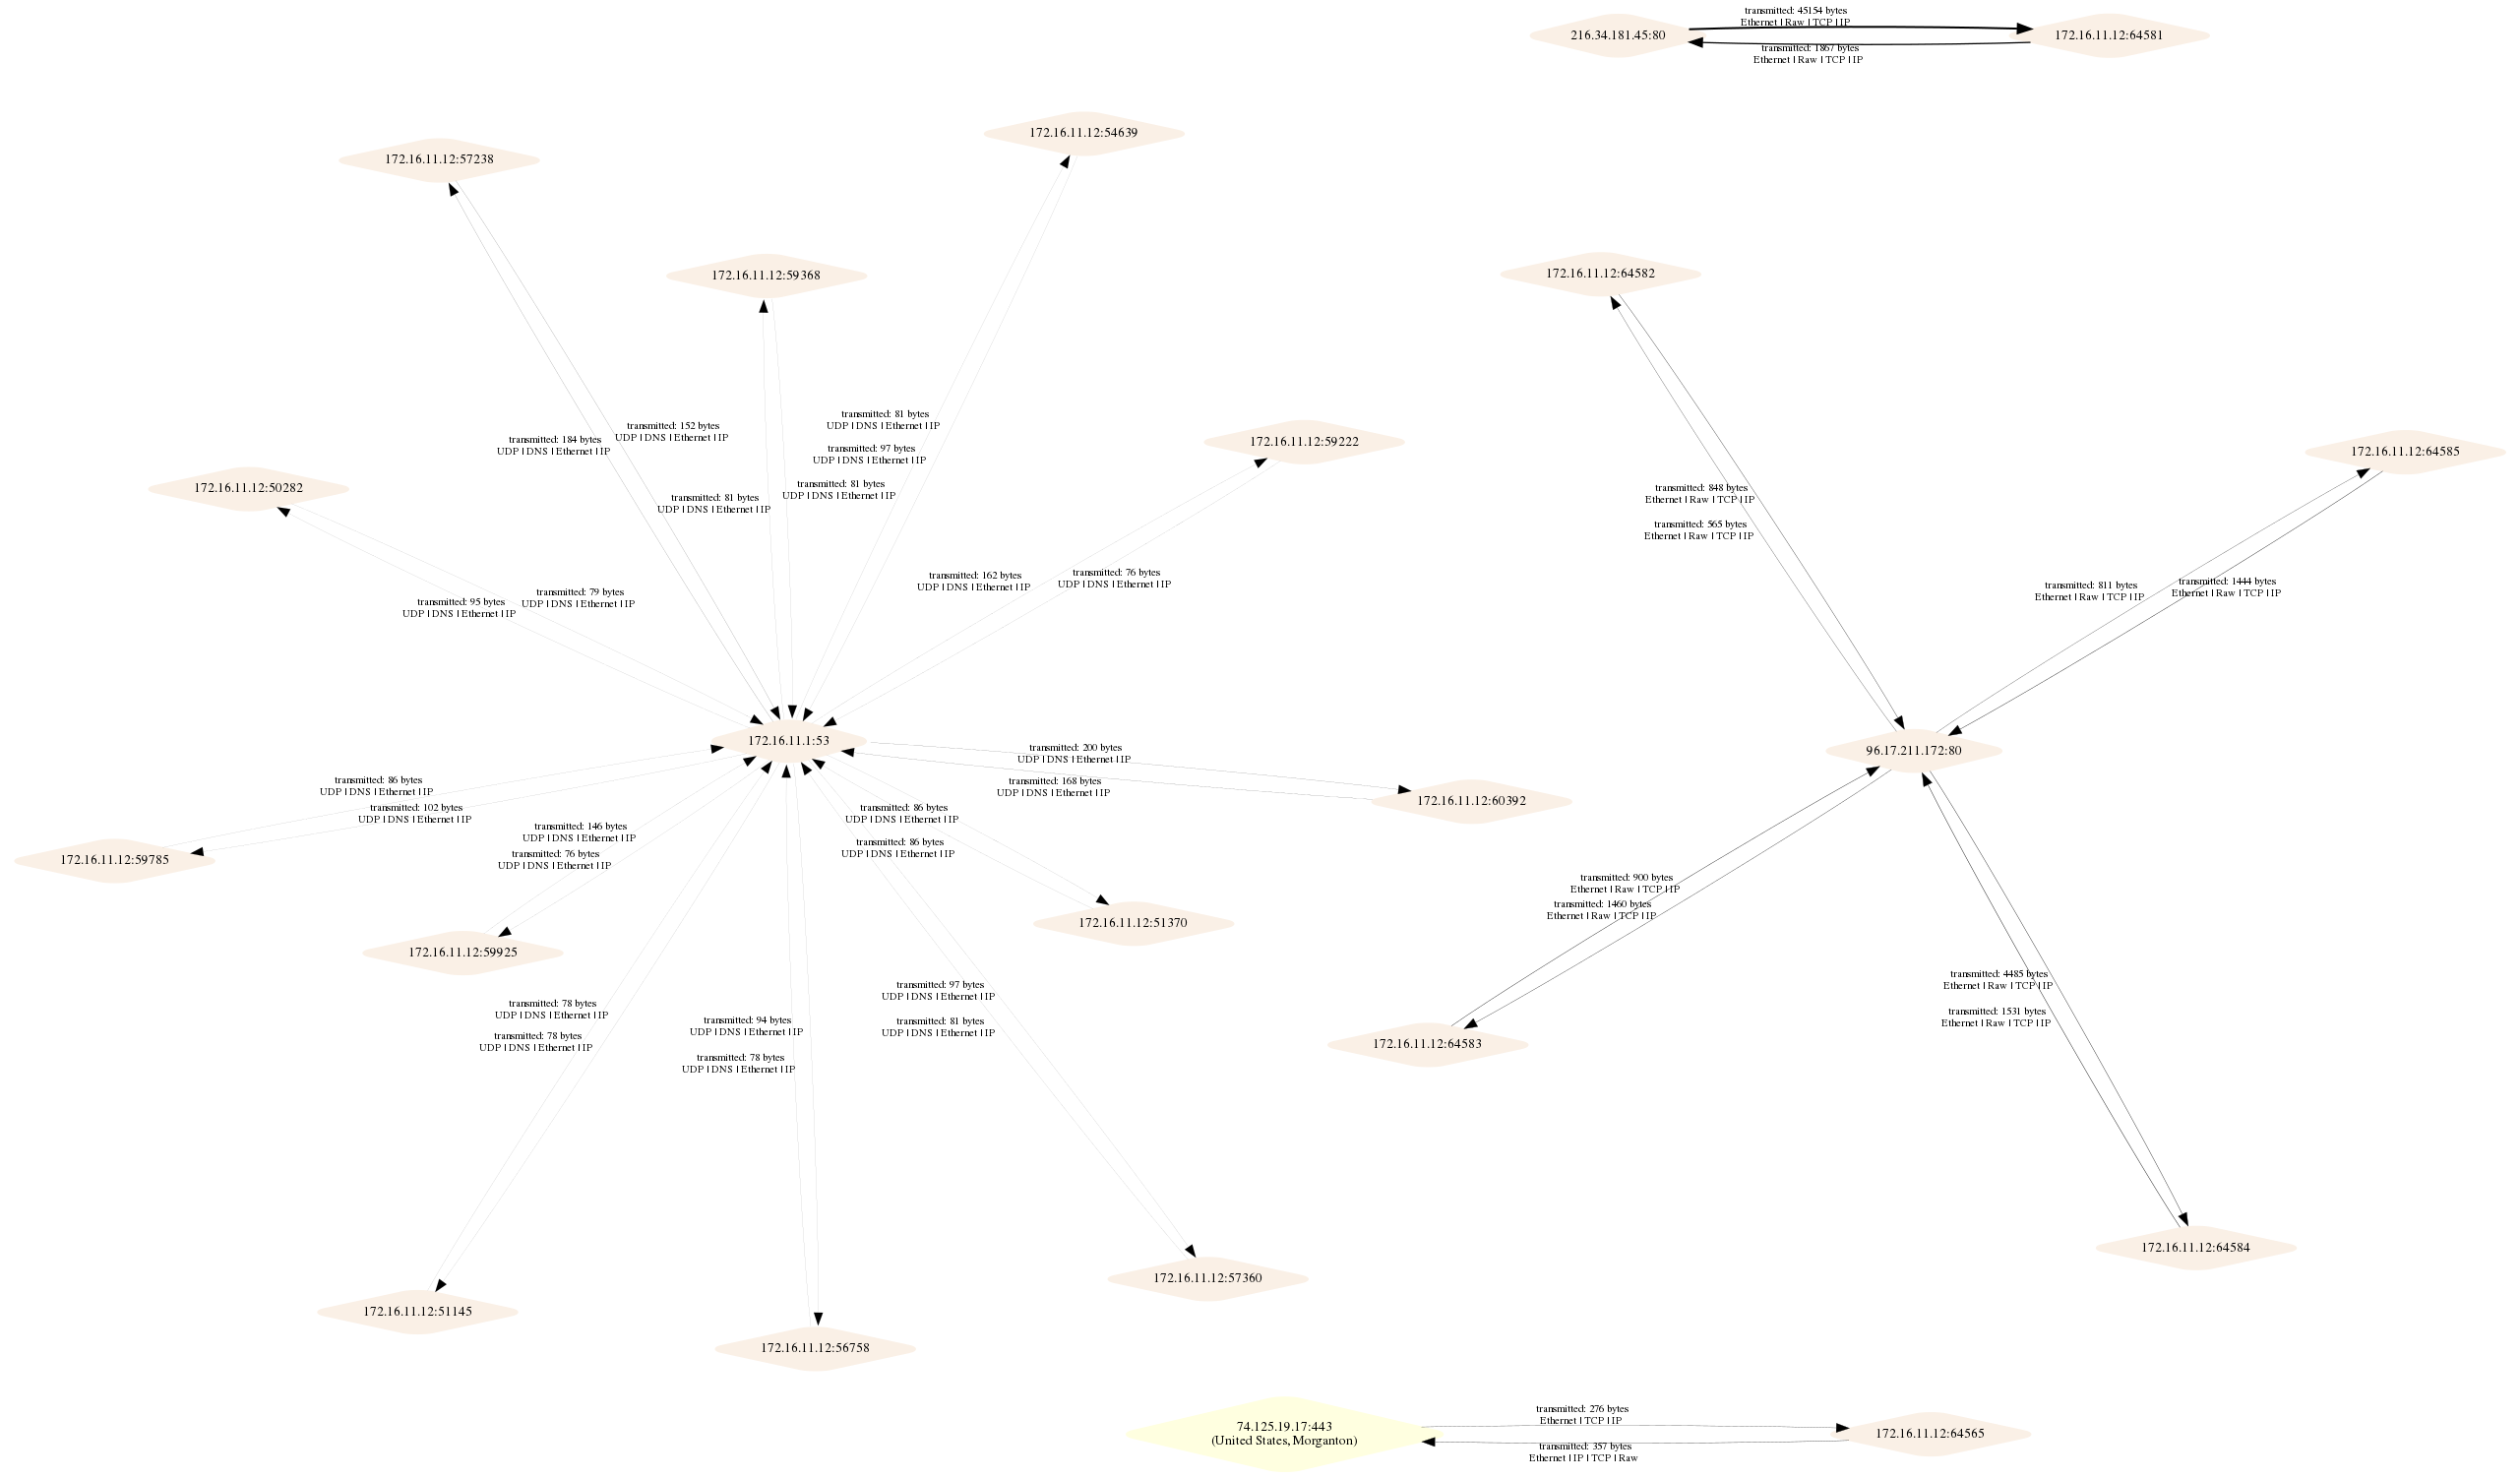 1ultimat3/pcapviz
Visualize network topologies and collect graph statistics based on pcap files
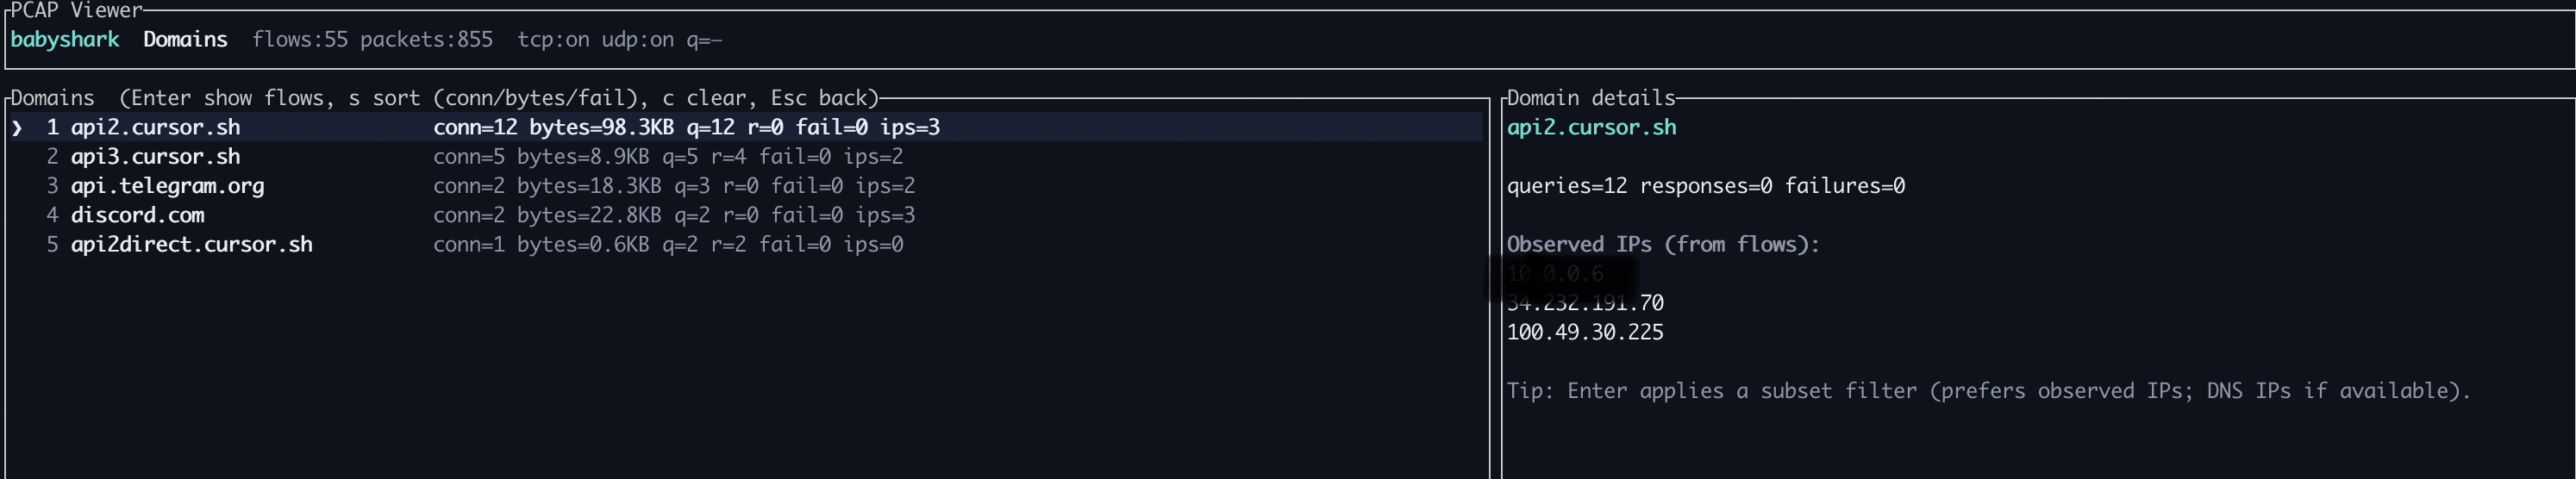 vignesh07/babyshark
Flows-first PCAP TUI (case files, gorgeous UX). Do do do do.
 vikwin/pcapfex
'Packet Capture Forensic Evidence eXtractor' is a tool that finds and extracts files from packet capture files