
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
79 results
ir-rescue preview

ir-rescue

GitHubdiogo-fernan/ir-rescue

A Windows Batch script and a Unix Bash script to comprehensively collect host forensic data during incident response.
digital-forensicsdisk-forensicsforensics+6
489
5 years ago
stenographer preview
Archived

stenographer

GitHubgoogle/stenographer

Stenographer is a packet capture solution which aims to quickly spool all packets to disk, then provide simple, fast access to subsets of those…
forensicsincident-responseintrusion-detection+3
1.8k5 years ago
Dshell preview

Dshell

GitHubusarmyresearchlab/dshell

Dshell is a network forensic analysis framework.
digital-forensicsdns-analysisforensics+3
5.5k3 days ago
packetsifterTool preview

packetsifterTool

GitHubpacketsifter/packetsiftertool

PacketSifter is a tool/script that is designed to aid analysts in sifting through a packet capture (pcap) to find noteworthy traffic. Packetsifter…
defensive-toolsdigital-forensicsforensics+5
935 years ago
wireshark-forensics-plugin preview

wireshark-forensics-plugin

GitHubrjbhide/wireshark-forensics-plugin

Wireshark plugin that correlates network traffic with threat intelligence, asset tags, and vulnerability data to accelerate forensic analysis of PCAP…
digital-forensicsforensicsnetwork-forensics+3
1024 years ago
BlueFish preview

BlueFish

GitHubemrekybs/bluefish

Automation tool designed to simplify the analysis of PCAP (Packet Capture) files
forensicsincident-responseinformation-gathering+2
197 months ago
pcapinator preview

pcapinator

GitHubmspicer/pcapinator

A tool for processing a lot of pcaps using tshark
forensicsinformation-gatheringnetwork-forensics+2
1553 years ago
detux preview

detux

GitHubdetuxsandbox/detux

The Multiplatform Linux Sandbox
dynamic-analysis-sandboxingforensicsmalware-analysis+1
2668 years ago
aiengine preview

aiengine

Bitbucketcamp0/aiengine

AIEngine is a next generation interactive/programmable Python/Ruby/Java/Lua and Go NIDS (Network intrusion detection system).
anomaly-detectiondefensive-toolsdns-analysis+5
3 years ago
Blue-Team-Notes preview

Blue-Team-Notes

GitHubpurp1ew0lf/blue-team-notes

You didn't think I'd go and leave the blue team out, right?

curated-resourcesdigital-forensicseducation+5
1.8k1 month ago
malware-samples preview

malware-samples

GitHubjstrosch/malware-samples

Malware samples, analysis exercises and other interesting resources.
binary-analysiscurated-resourceseducation+3
1.7k2 years ago
DFIR-LABS preview

DFIR-LABS

GitHubazr43lkn1ght/dfir-labs

Hands-on DFIR challenges covering digital forensics, incident response, malware analysis, and threat hunting with CTF-style flags and real-world…

ctfdigital-forensicsdisk-forensics+6
6701 month ago
Bryobio preview

Bryobio

GitHubemrekybs/bryobio

It was developed to speed up the processes of SOC Analysts during analysis

forensicsinformation-gatheringnetwork-forensics+3
487 months ago
CovenantDecryptor preview

CovenantDecryptor

GitHubnaacbin/covenantdecryptor

Decrypts Covenant C2 communications by extracting RSA private keys from minidumps, recovering AES session keys, and converting network captures to…
command-and-controlcryptographydigital-forensics+4
372 years ago
packetStrider preview

packetStrider

GitHubbenjeems/packetstrider

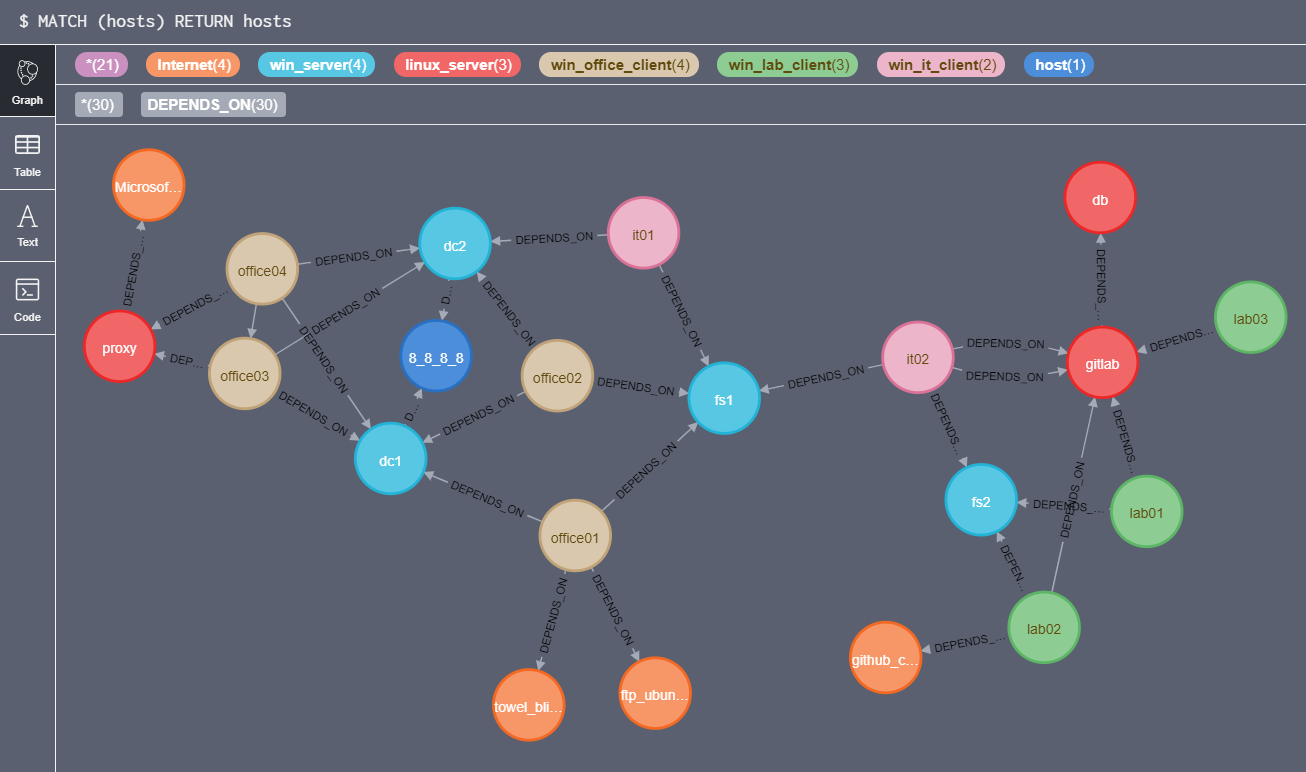
A network packet forensics tool for SSH
anomaly-detectionforensicsintrusion-detection+5
2547 years ago
netstat2neo4j preview

netstat2neo4j

GitHubtrinitor/netstat2neo4j

create cypher create statements for neo4j out of netstat files from multiple machines

information-gatheringlog-analysisnetwork-forensics
415 years ago
ja4 preview

ja4

GitHubfoxio-llc/ja4

JA4+ is a suite of network fingerprinting standards
dns-analysisencryption-decryption-toolsfingerprint-spoofing+9
2.0k26 days ago
malcom preview

malcom

GitHubtomchop/malcom

Malcom - Malware Communications Analyzer

malware-analysisnetwork-forensicsthreat-intelligence
1.2k8 years ago
Previous12345Next