

gopacket
 google/gopacket
Provides packet processing capabilities for Go
network-forensicsnetwork-securitypacket-sniffing-analysis+1
google/gopacketProvides packet processing capabilities for Go
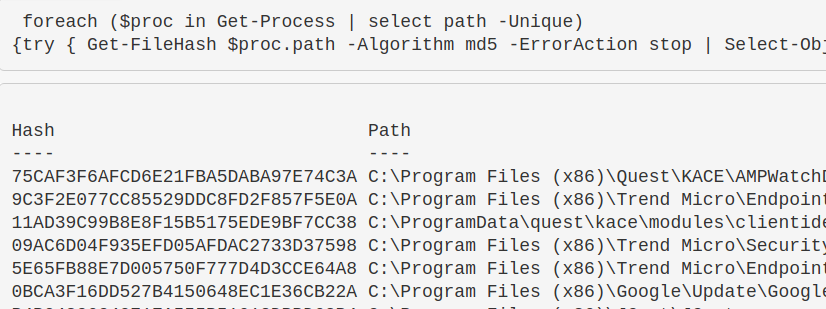 purp1ew0lf/blue-team-notes
You didn't think I'd go and leave the blue team out, right?
 camp0/aiengine
AIEngine is a next generation interactive/programmable Python/Ruby/Java/Lua and Go NIDS (Network intrusion detection system).
 gcla/termshark
A terminal UI for tshark, inspired by Wireshark
 oisf/suricata
Open-source network IDS/IPS/NSM engine for real-time traffic inspection, intrusion detection and prevention, protocol analysis, and rule-based threat…
 ntop/ntopng
Web-based Traffic and Cybersecurity Network Traffic Monitoring

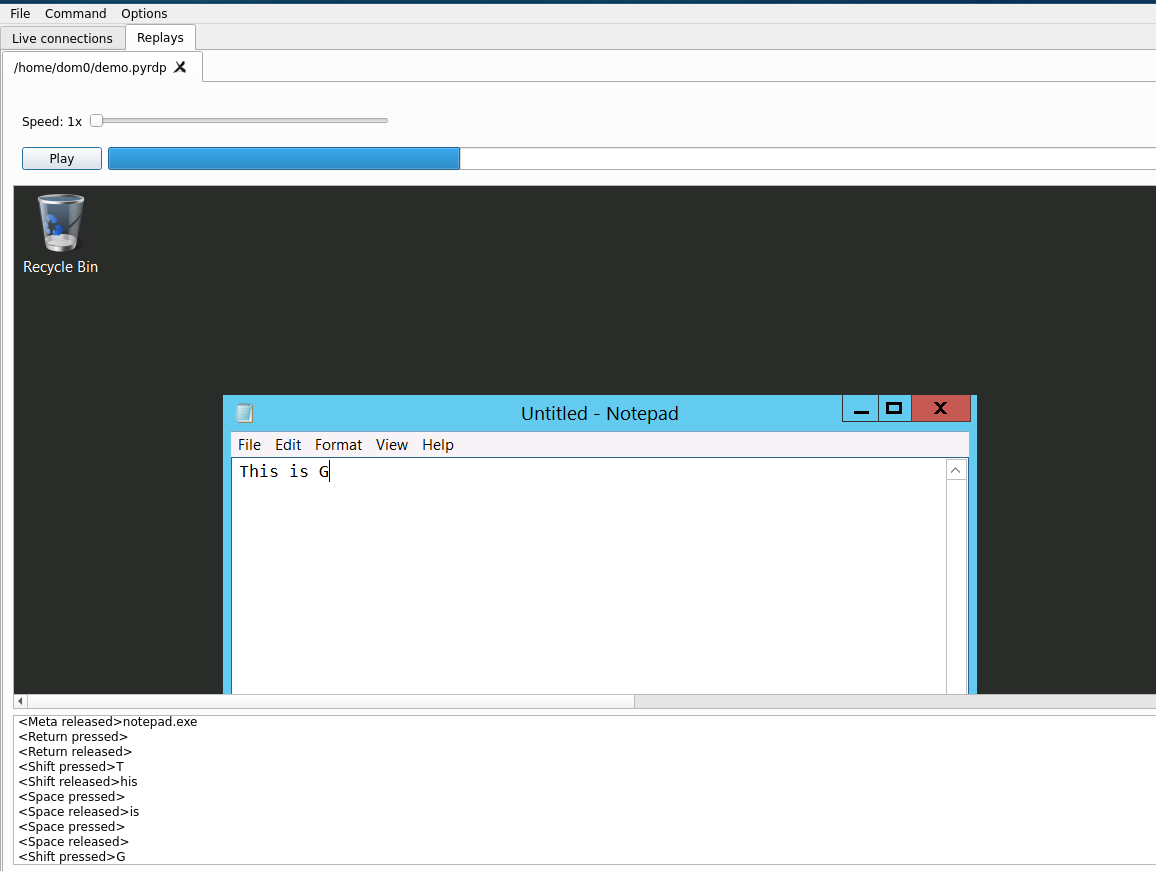 gosecure/pyrdp
RDP monster-in-the-middle (mitm) and library for Python with the ability to watch connections live or after the fact
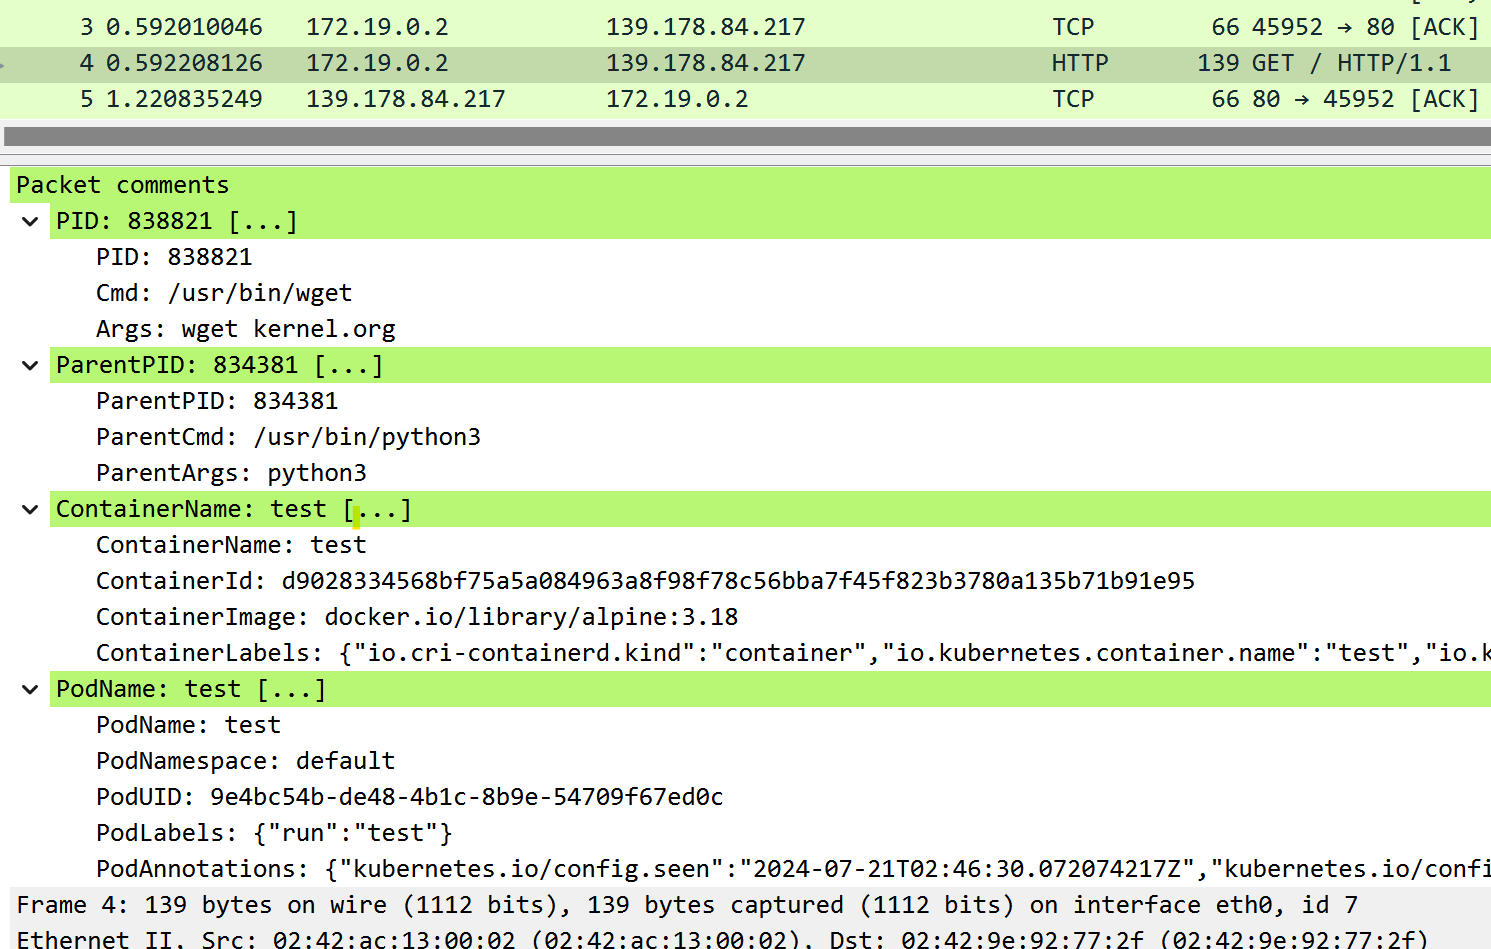 mozillazg/ptcpdump
eBPF-based packet analyzer that captures network traffic with automatic process, container, and Kubernetes pod metadata annotation, supporting…
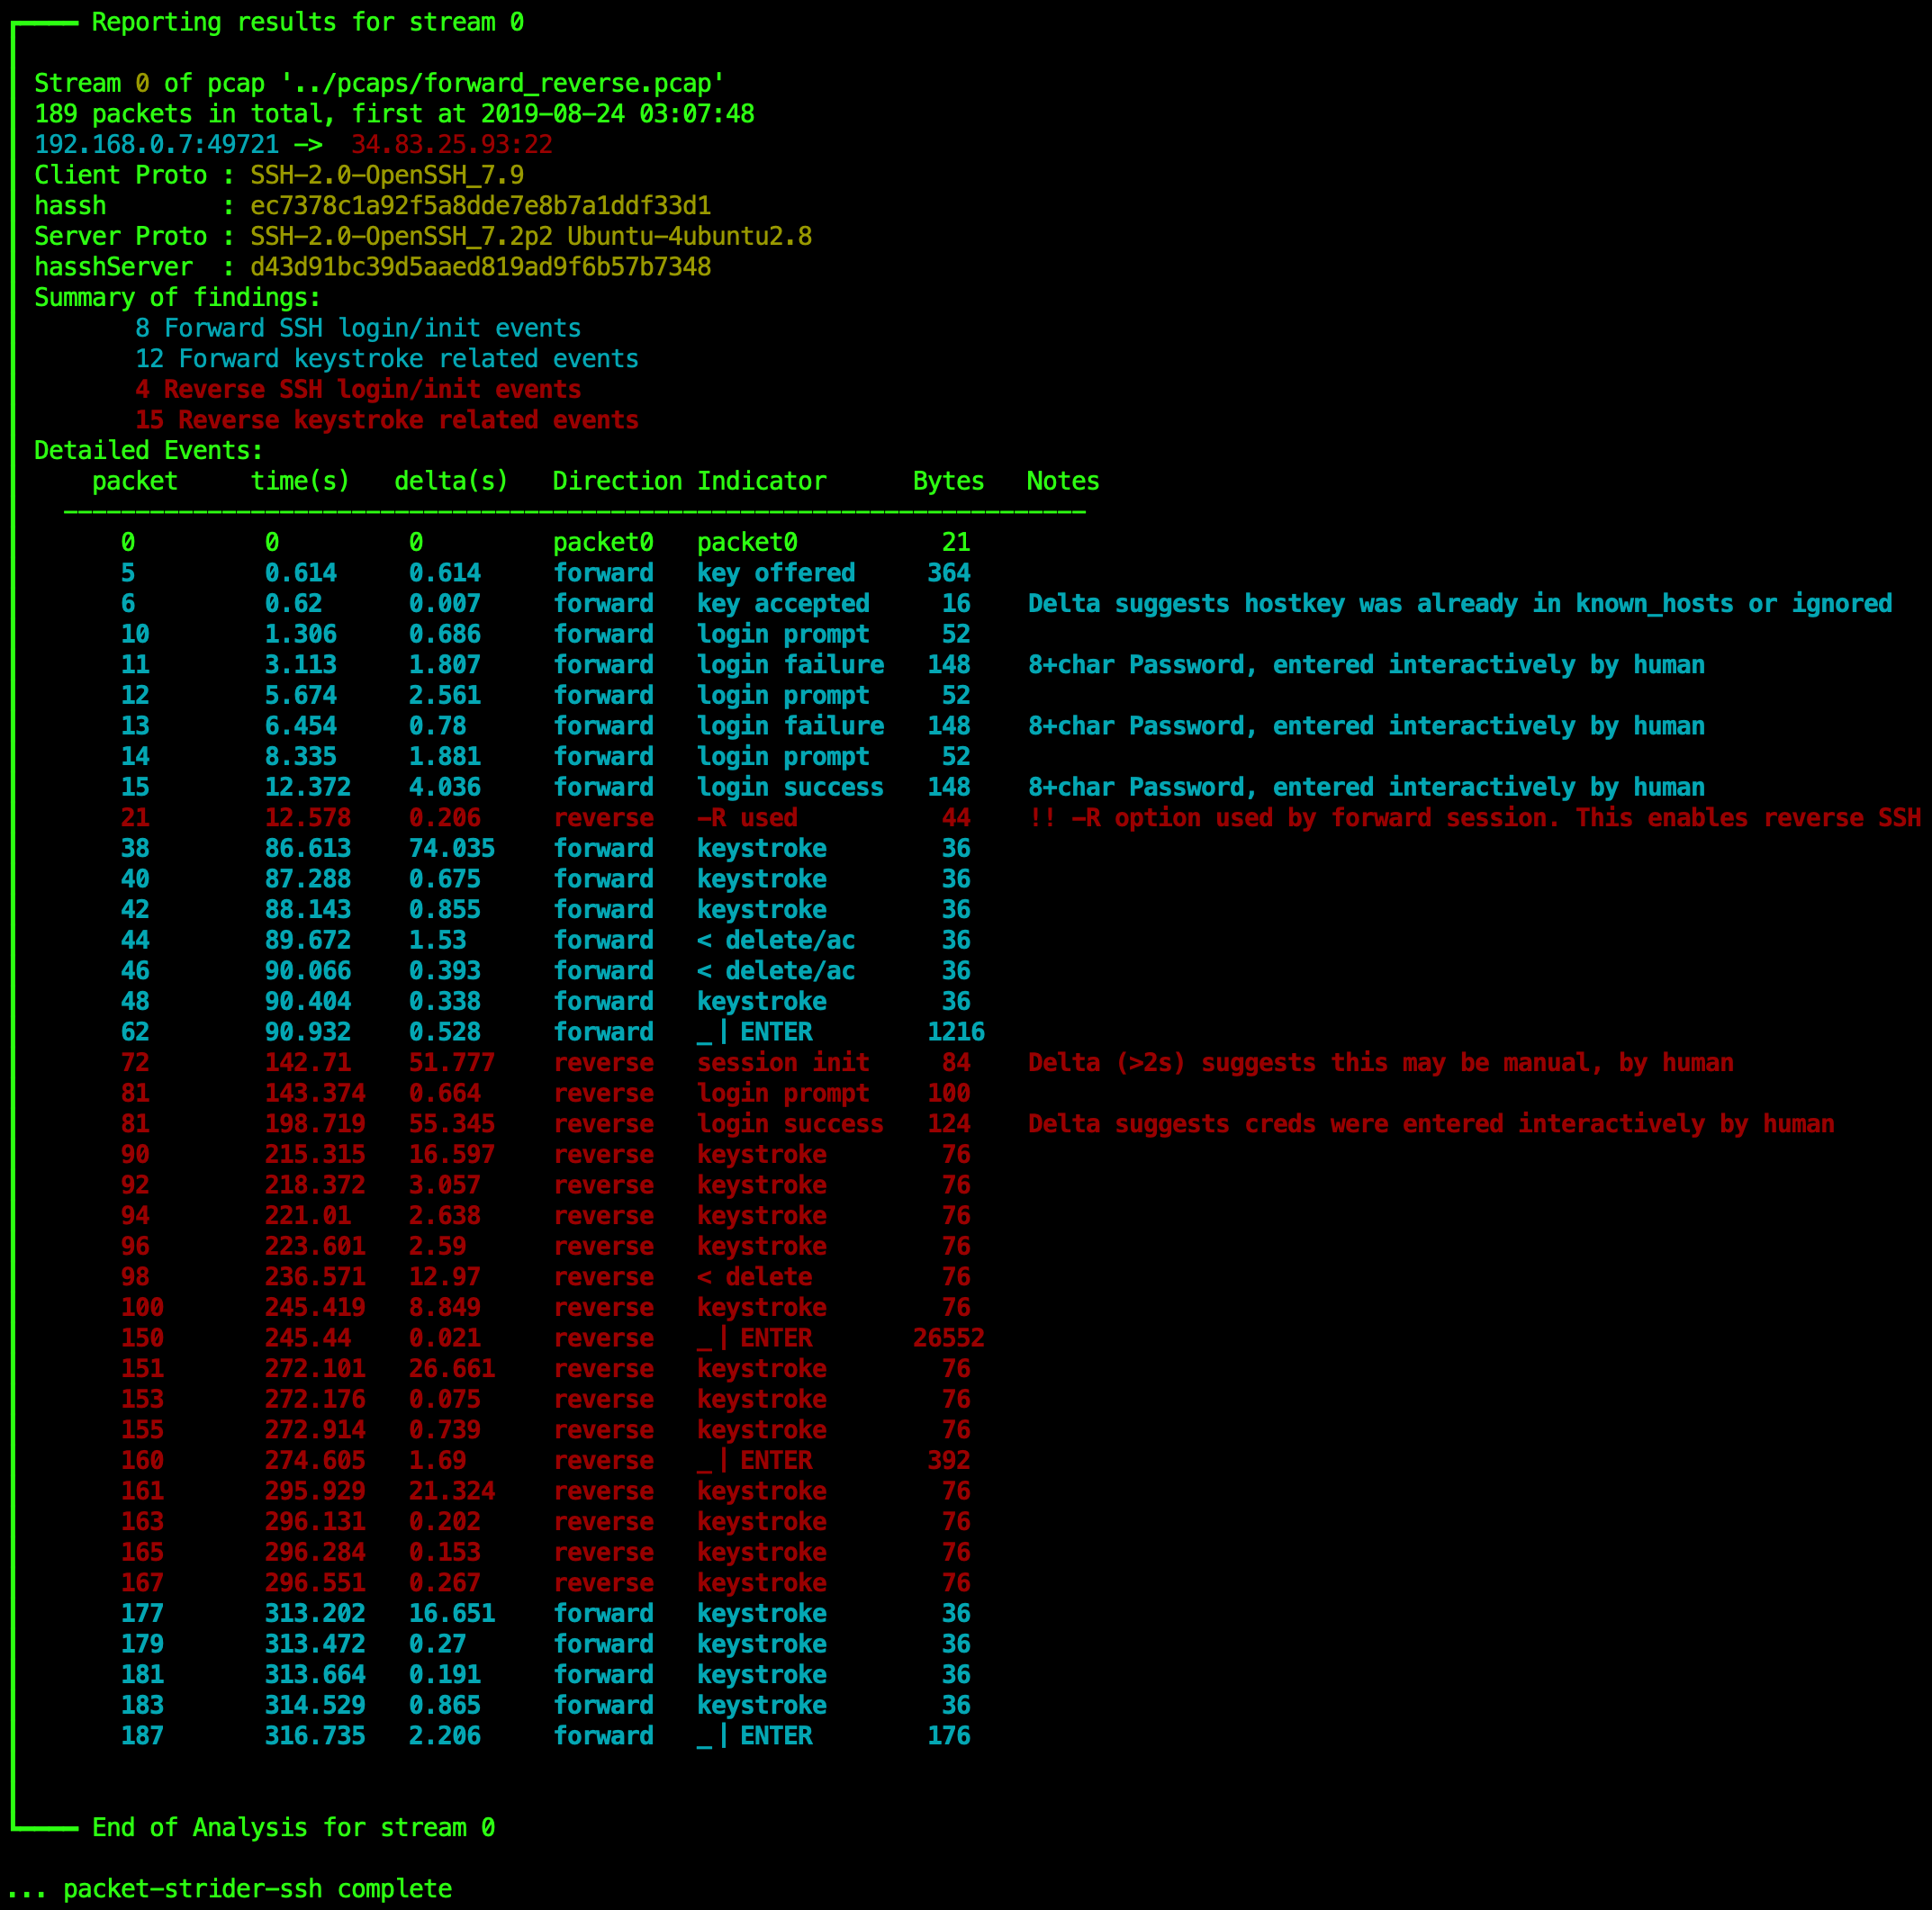 benjeems/packetstrider
A network packet forensics tool for SSH
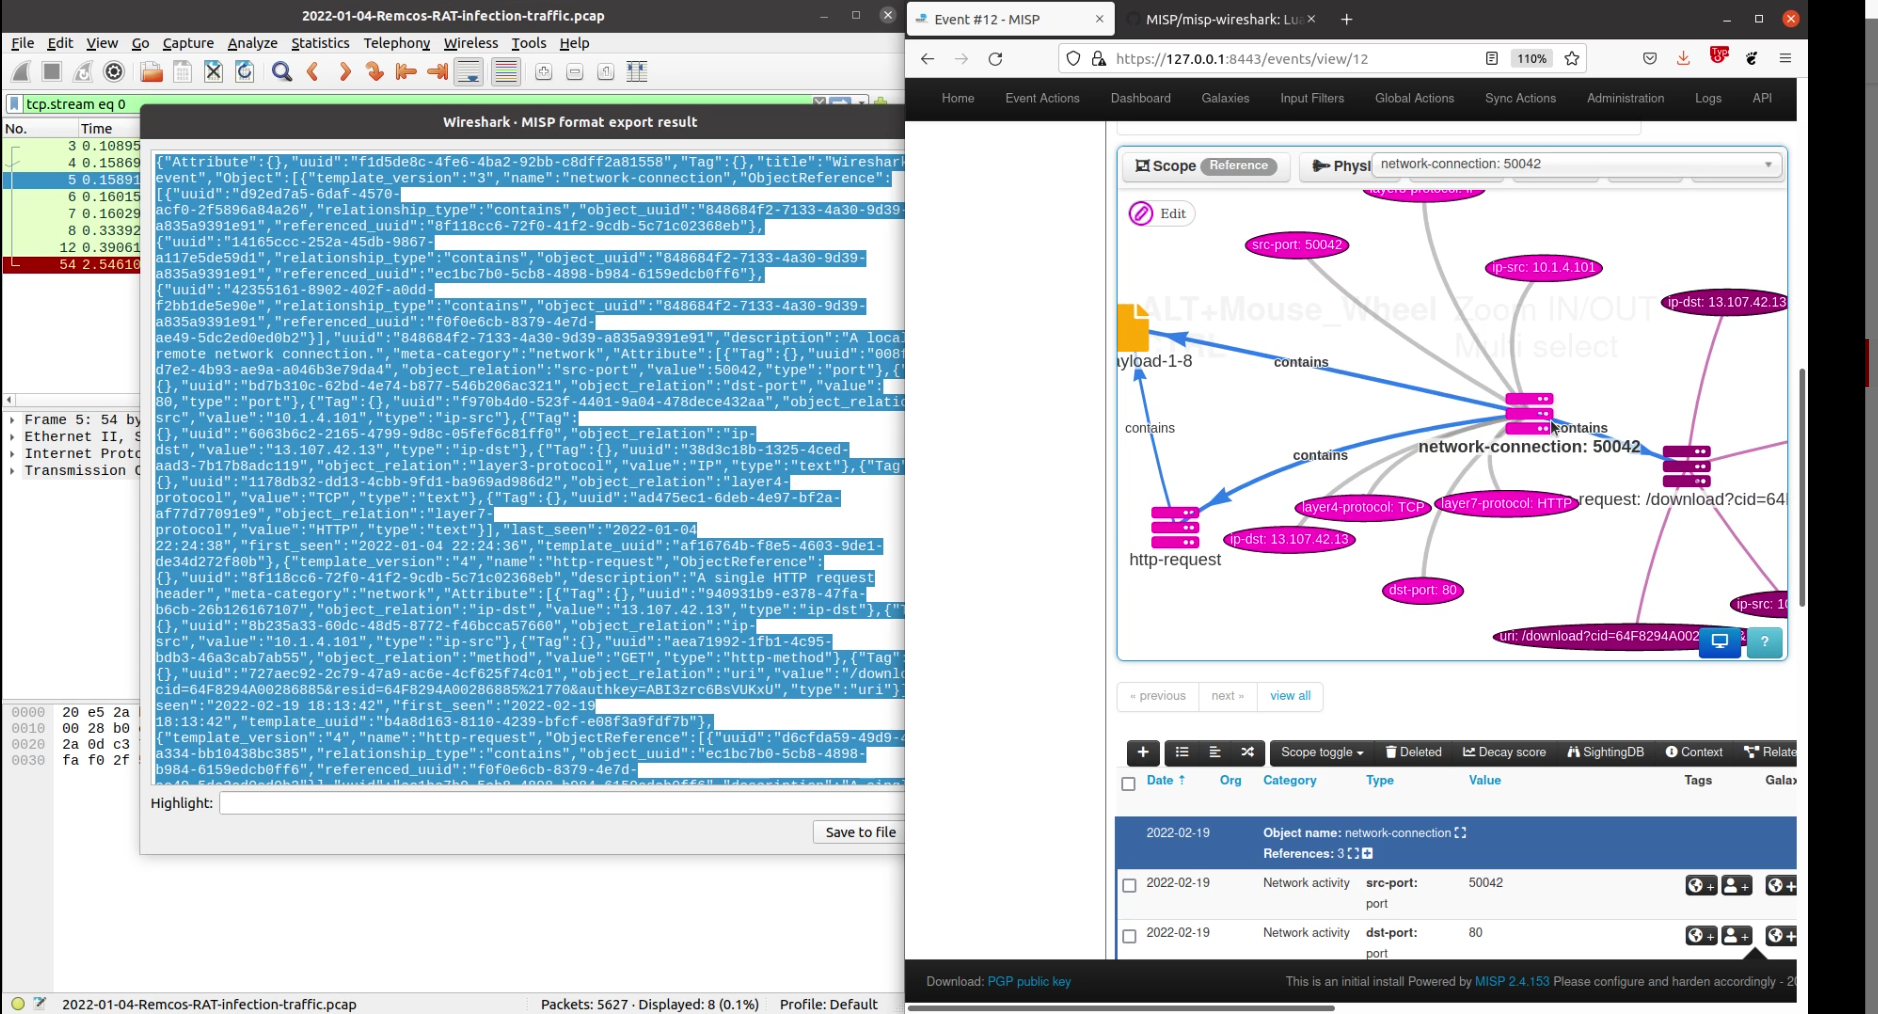 misp/misp-wireshark
Lua plugin to extract data from Wireshark and convert it into MISP format
 agent-hellboy/ltm
ltm is a machine-history debugger for Linux. It records process, file, network, memory, and block-I/O metadata via eBPF, then lets you query the…
 spectralzero/netscope
Offline-first network investigation and response platform for Windows. Turns a pcap or live capture into a full forensic verdict — attack story,…
 deepfence/packetstreamer
⭐ ⭐ Distributed tcpdump for cloud native environments ⭐ ⭐