

Skadi
 orlikoski/skadi
Collect, Process, and Hunt with host based data from MacOS, Windows, and Linux
curated-resourcesdigital-forensicsdisk-forensics+9
orlikoski/skadiCollect, Process, and Hunt with host based data from MacOS, Windows, and Linux
 diogo-fernan/ir-rescue
A Windows Batch script and a Unix Bash script to comprehensively collect host forensic data during incident response.
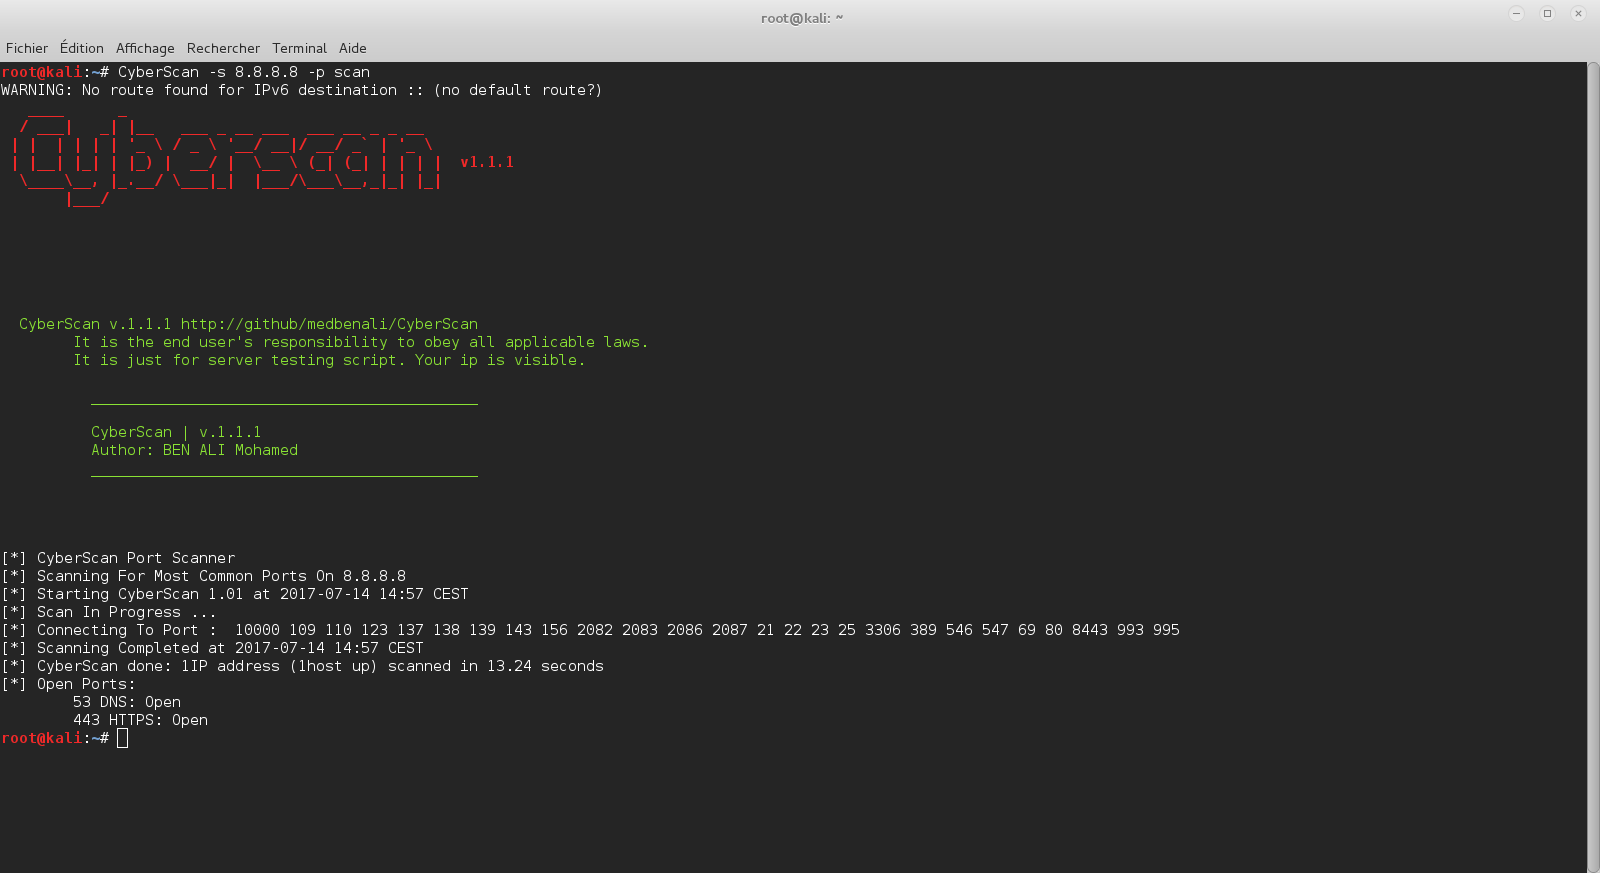 medbenali/cyberscan
Open-source network forensics toolkit for packet analysis, port scanning, host discovery, and IP geolocation. Supports ARP, ICMP, TCP, UDP pings and…

