

grr
 google/grr
Remote live forensics and incident response framework with Python agent for collecting forensic data from endpoints, including memory, disk, and…
digital-forensicsdisk-forensicsforensics+4
5.1k1 day ago
google/grrRemote live forensics and incident response framework with Python agent for collecting forensic data from endpoints, including memory, disk, and…
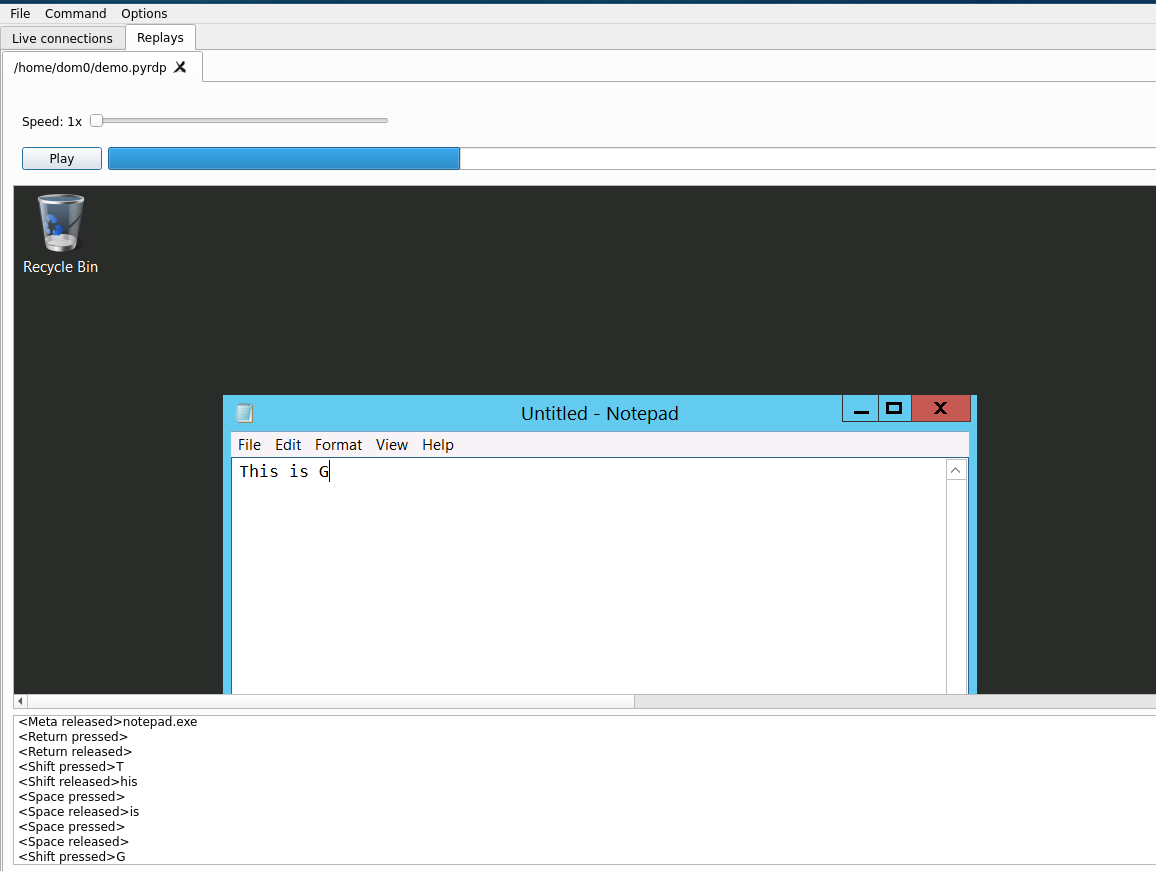 gosecure/pyrdp
RDP monster-in-the-middle (mitm) and library for Python with the ability to watch connections live or after the fact
 0x4d31/fatt
FATT /fingerprintAllTheThings - a pyshark based script for extracting network metadata and fingerprints from pcap files and live network traffic
 bert-janp/incident-response-powershell
PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…
 rjbhide/wireshark-forensics-plugin
Wireshark plugin that correlates network traffic with threat intelligence, asset tags, and vulnerability data to accelerate forensic analysis of PCAP…
 formerlab/shadow-fleet-tracker-light
Open source Baltic Sea shadow fleet tracker. 1200+ vessels, live AIS, cable proximity alerts. No cloud, no subscription, runs locally
 spectralzero/netscope
Offline-first network investigation and response platform for Windows. Turns a pcap or live capture into a full forensic verdict — attack story,…
 wireshark/wireshark
Wireshark's official code repository. You can keep the releases coming by donating at https://wiresharkfoundation.org/donate/.
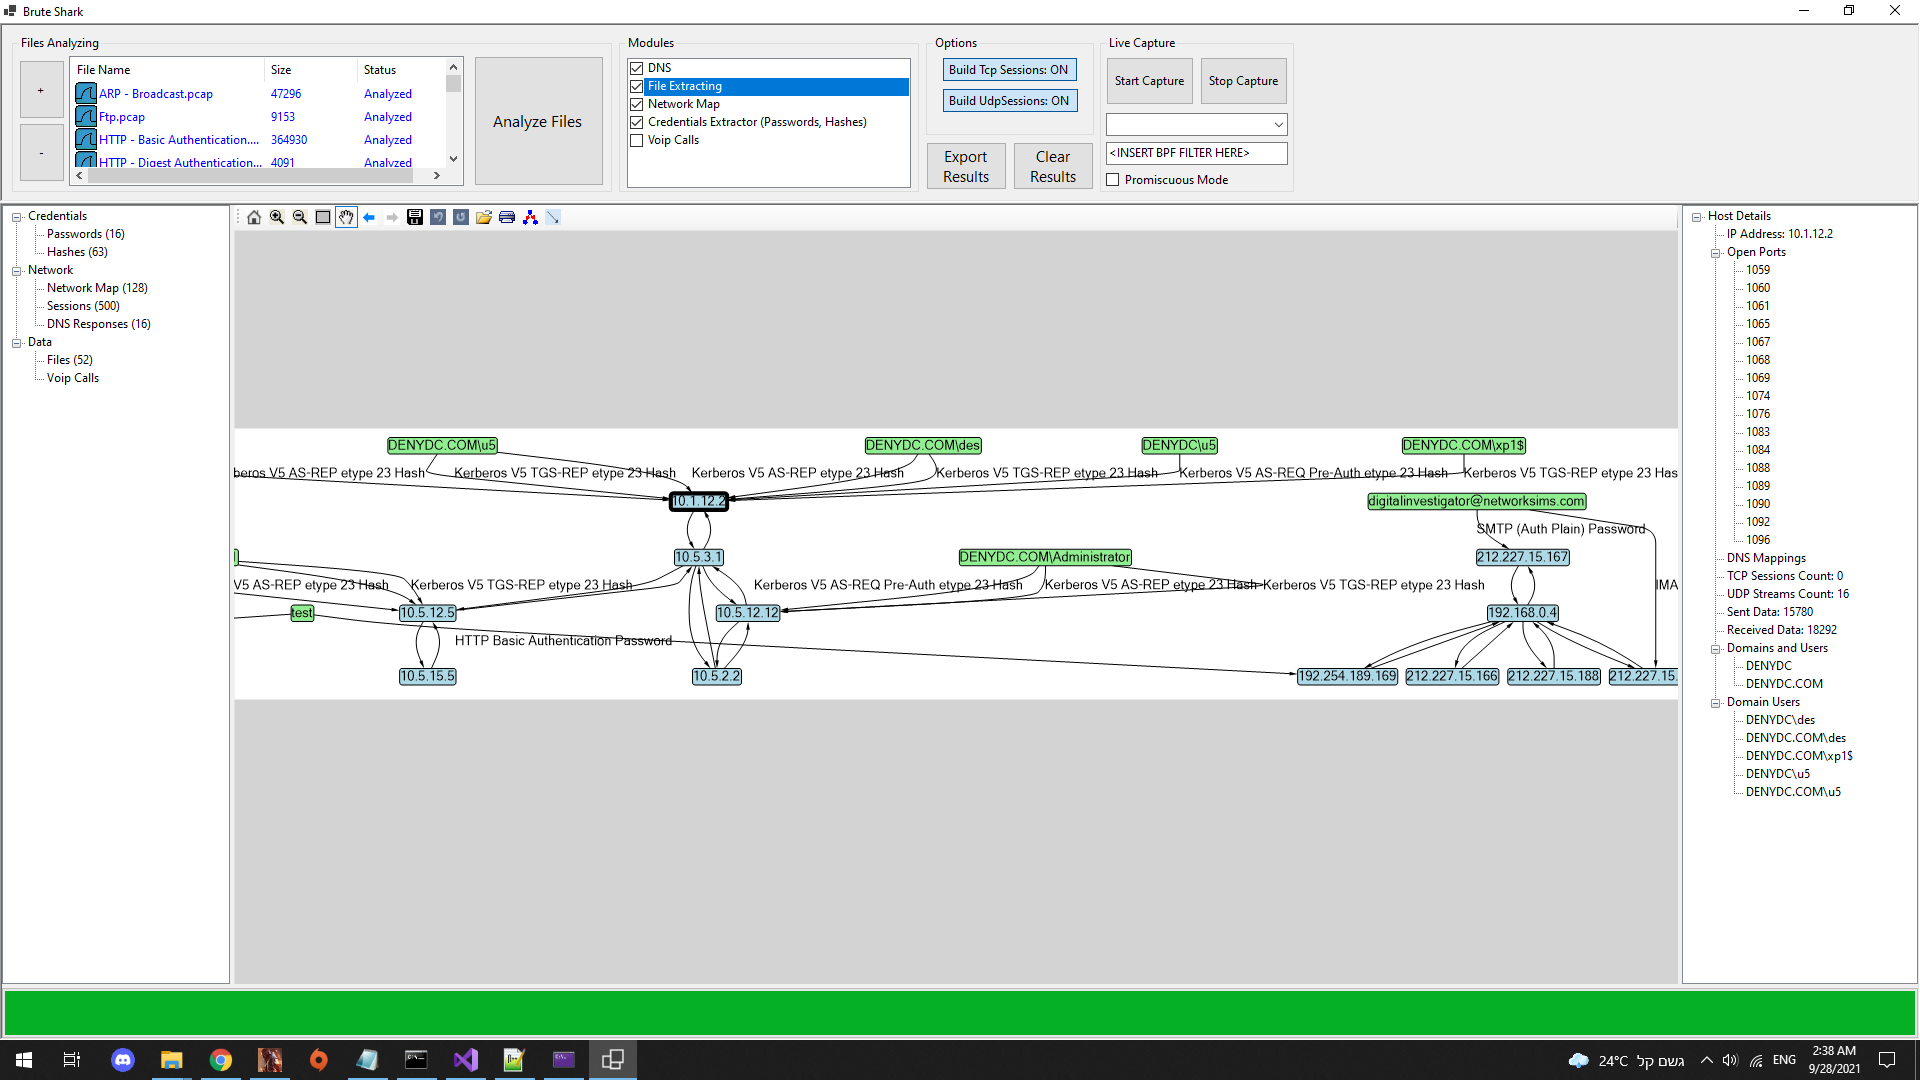
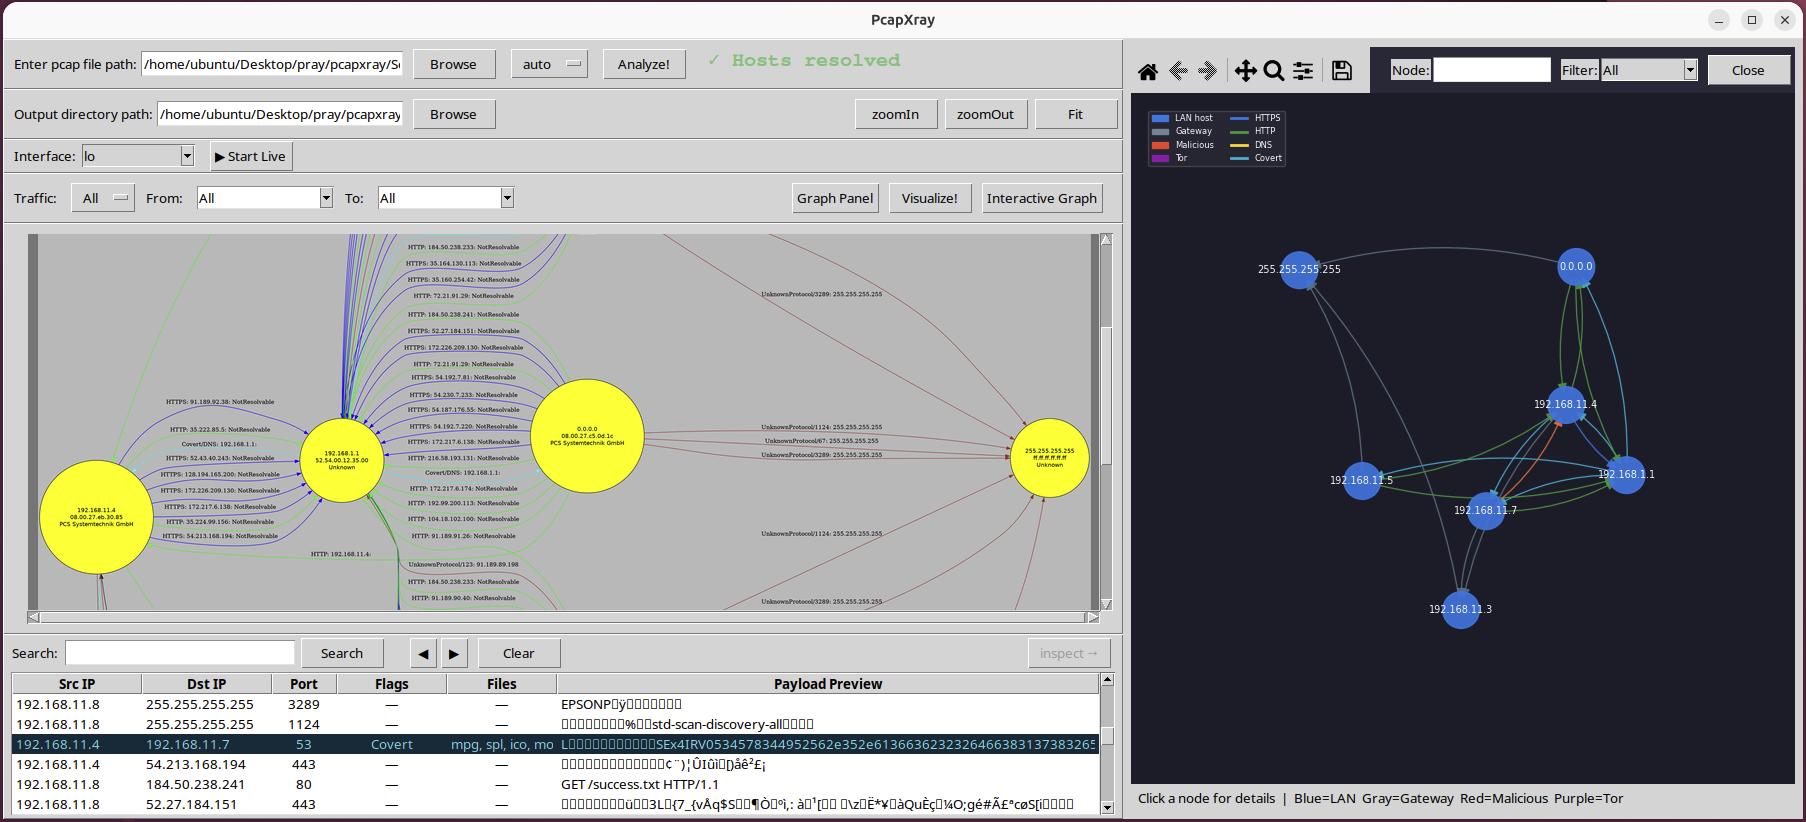 srixivas/pcapxray
❄️ PcapXray - A Network Forensics Tool - To visualize a Packet Capture offline as a Network Diagram including device identification, highlight…
 cisco/joy
A package for capturing and analyzing network flow data and intraflow data, for network research, forensics, and security monitoring.
 kavan00/android-projector-c2-malware
Breakdown of a c2-network of chinese beamers - SilentSDK-Analysis
 security-onion-solutions/security-onion
Security Onion 16.04 - Linux distro for threat hunting, enterprise security monitoring, and log management
 securityronin/memory-forensic
Walk any memory dump. Find what's hidden. Linux + Windows kernel forensics from a single static Rust binary — no Python required.