An-Integrated-Wireless-Network-Forensic-Analysis-Framework

This framework combines a set of existing open source tools into an integrated package that automates the forensics investigation process. It is able…

This framework combines a set of existing open source tools into an integrated package that automates the forensics investigation process. It is able…

Zeek is a powerful network analysis framework that is much different from the typical IDS you may know.

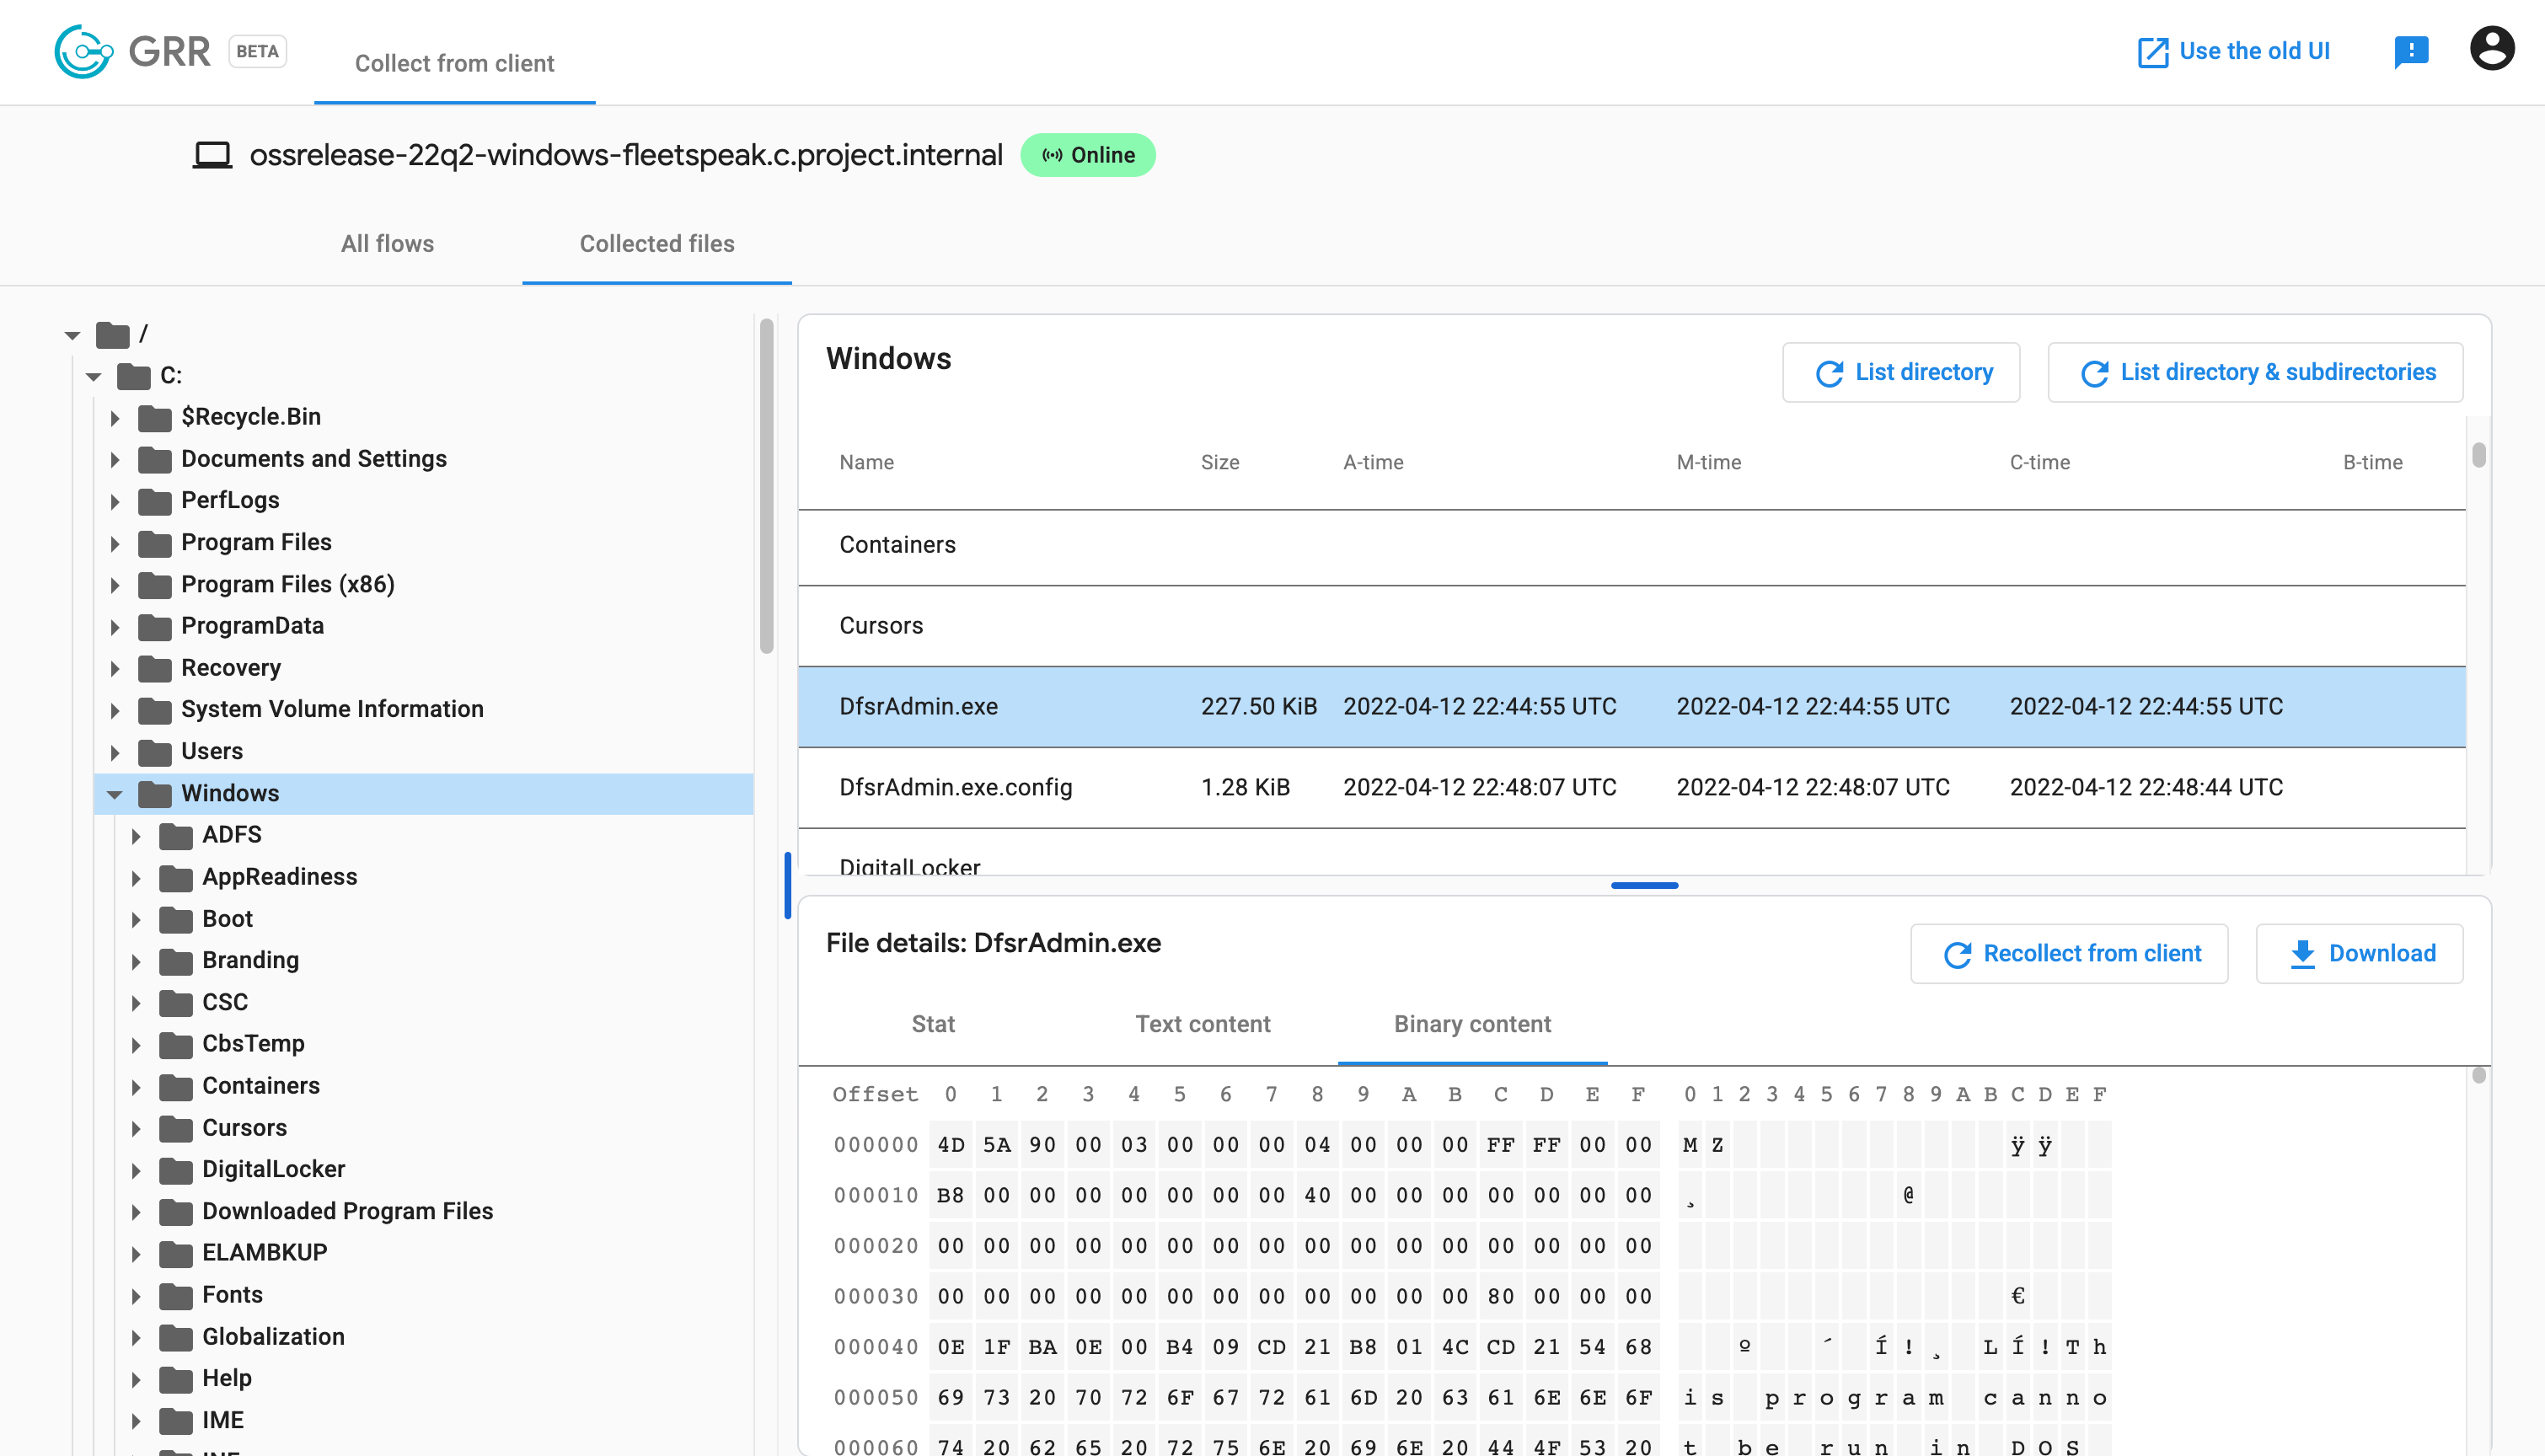
Remote live forensics and incident response framework with Python agent for collecting forensic data from endpoints, including memory, disk, and…

Dshell is a network forensic analysis framework.

Dissect is a digital forensics & incident response framework and toolset that allows you to quickly access and analyse forensic artefacts from…

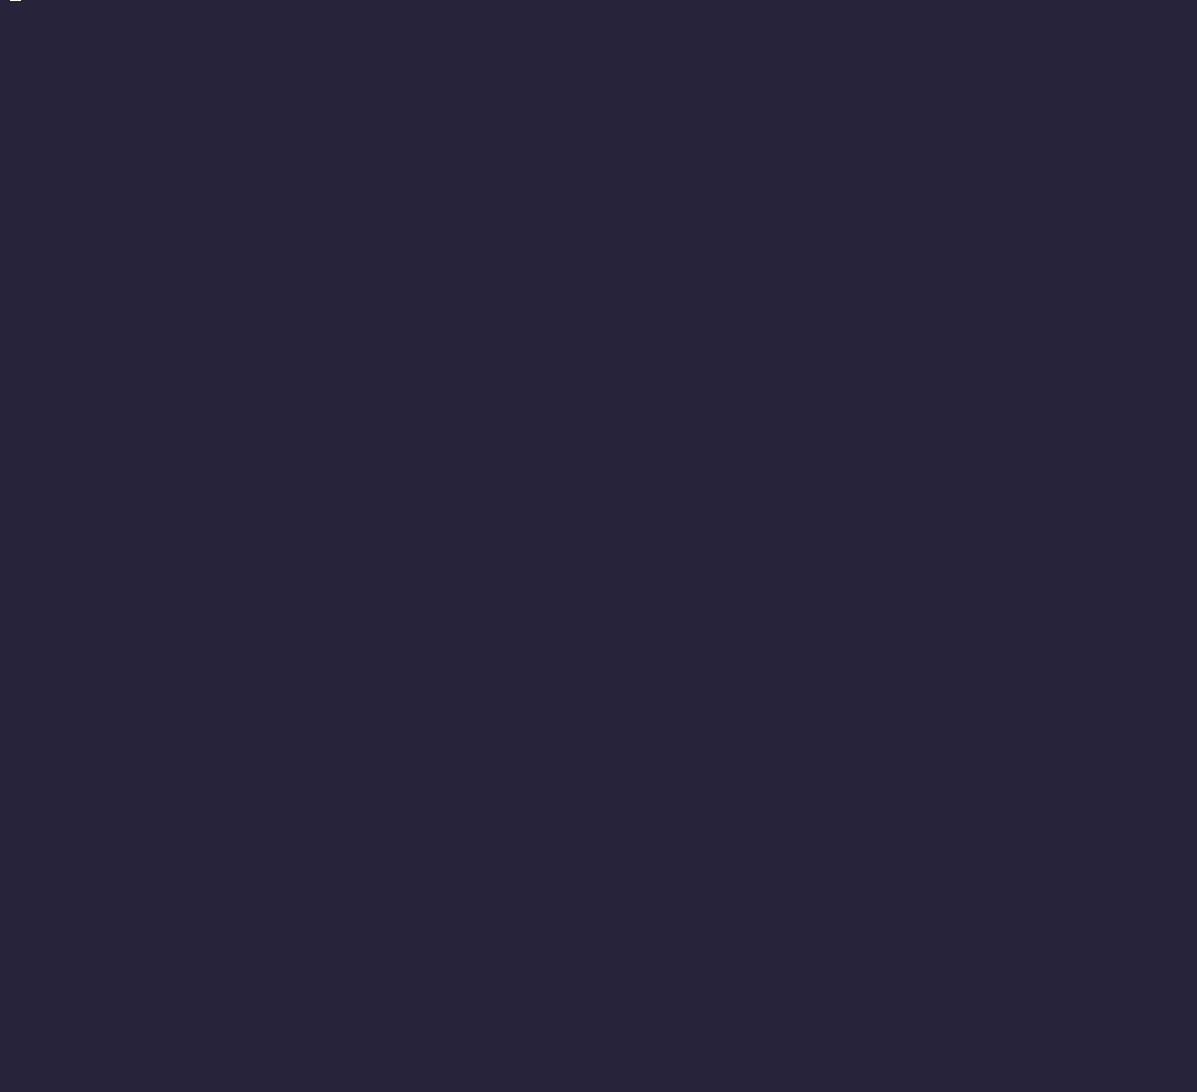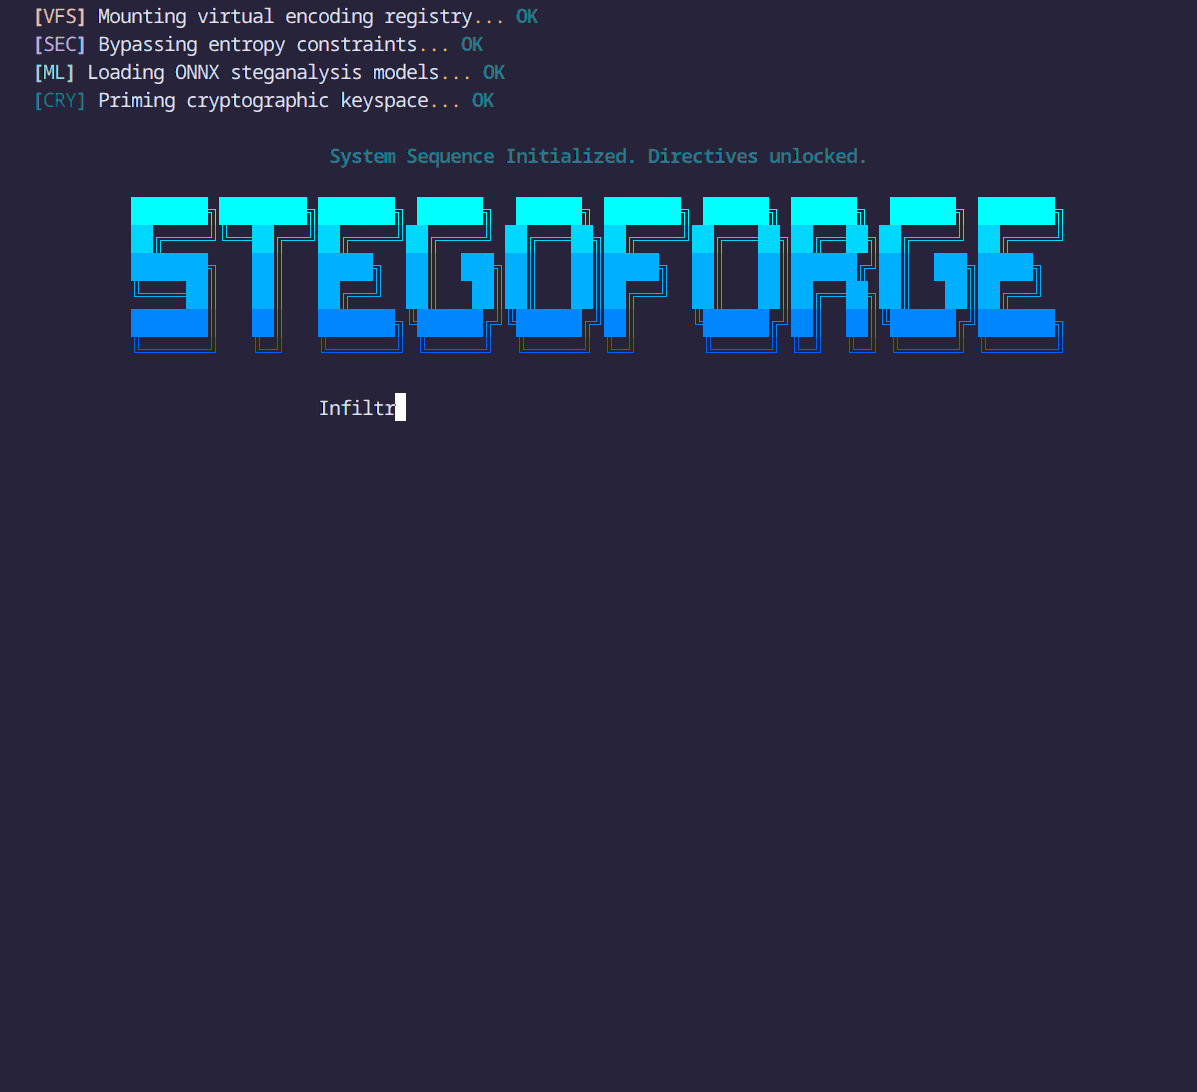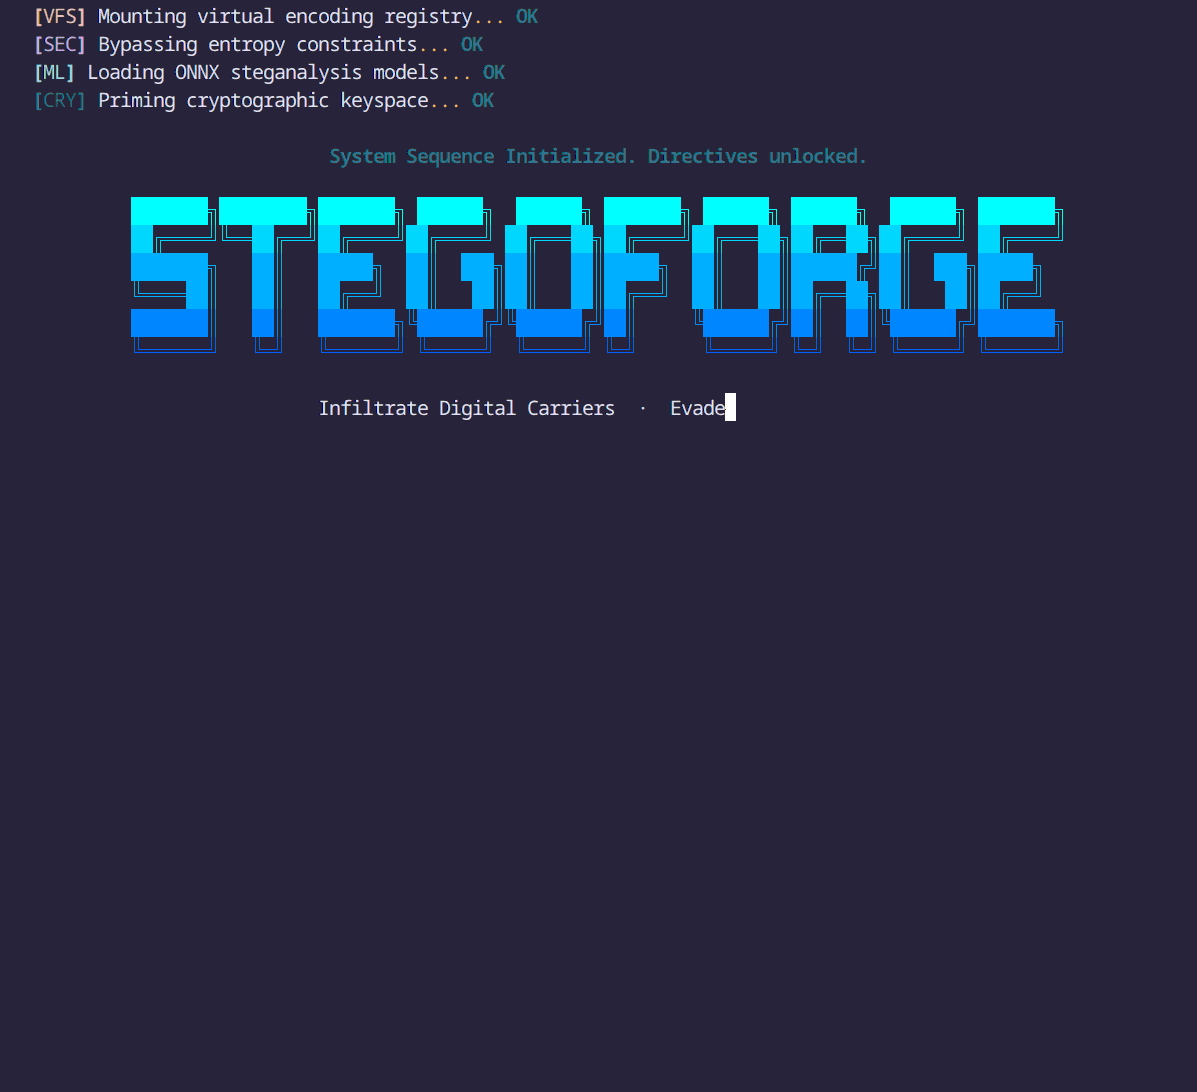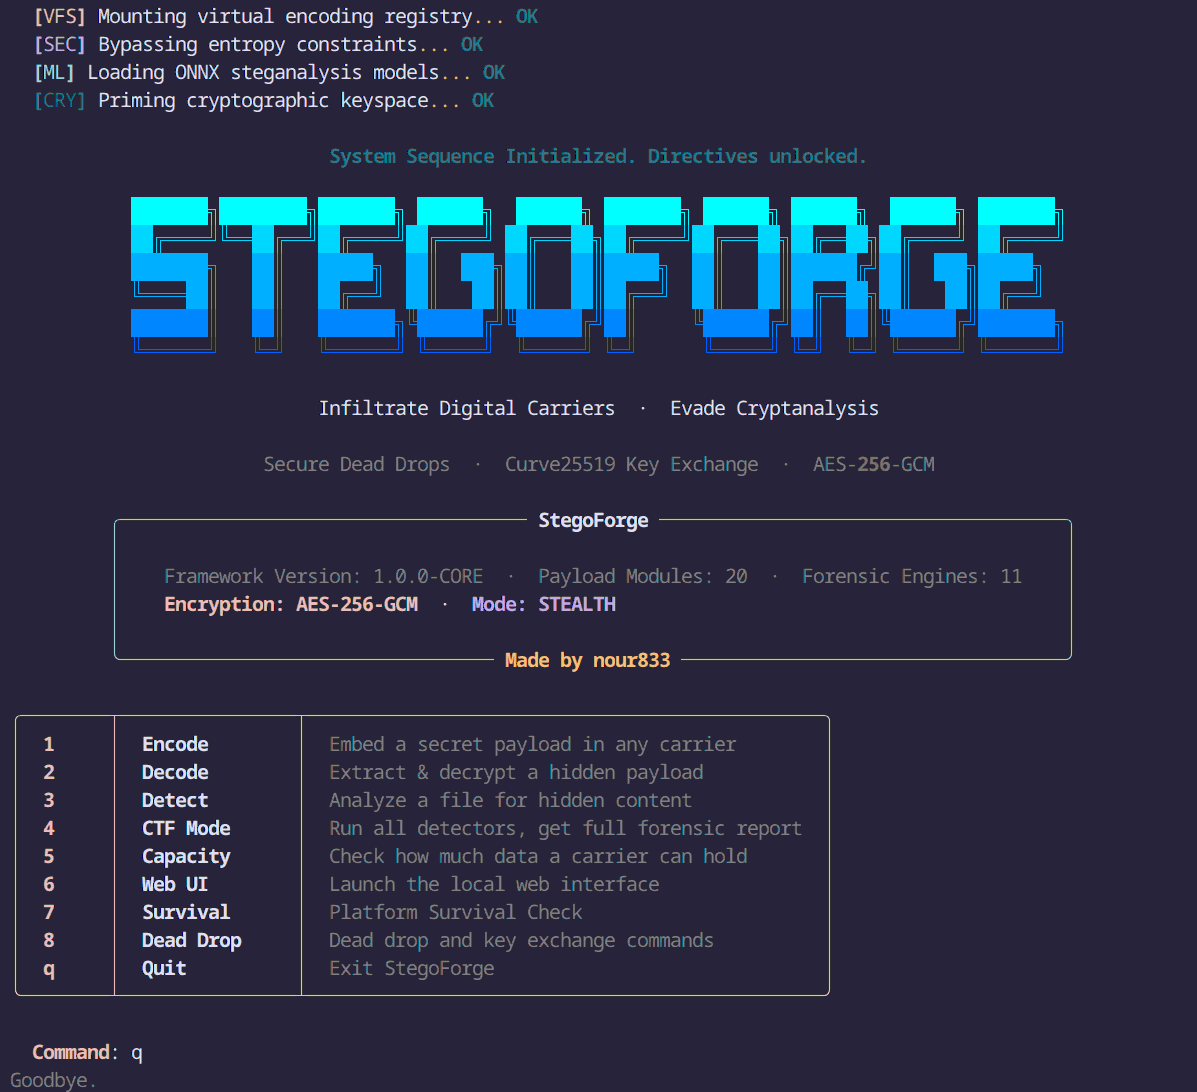
The ultimate steganography and digital forensics toolkit. Hide and extract data across images, audio, video, documents, and network packets, or run…

Malicious HTTP traffic explorer