

PcapPlusPlus
 seladb/pcapplusplus
Multiplatform C++ library for high-performance network packet capture, parsing, crafting, and analysis. Supports libpcap, DPDK, AF_XDP, PF_RING, and…
crawlerdns-analysisforensics+5
3.1k
seladb/pcapplusplusMultiplatform C++ library for high-performance network packet capture, parsing, crafting, and analysis. Supports libpcap, DPDK, AF_XDP, PF_RING, and…
 0x4d31/fatt
FATT /fingerprintAllTheThings - a pyshark based script for extracting network metadata and fingerprints from pcap files and live network traffic
 vikwin/pcapfex
'Packet Capture Forensic Evidence eXtractor' is a tool that finds and extracts files from packet capture files
 rjbhide/wireshark-forensics-plugin
Wireshark plugin that correlates network traffic with threat intelligence, asset tags, and vulnerability data to accelerate forensic analysis of PCAP…
 misp/misp-wireshark
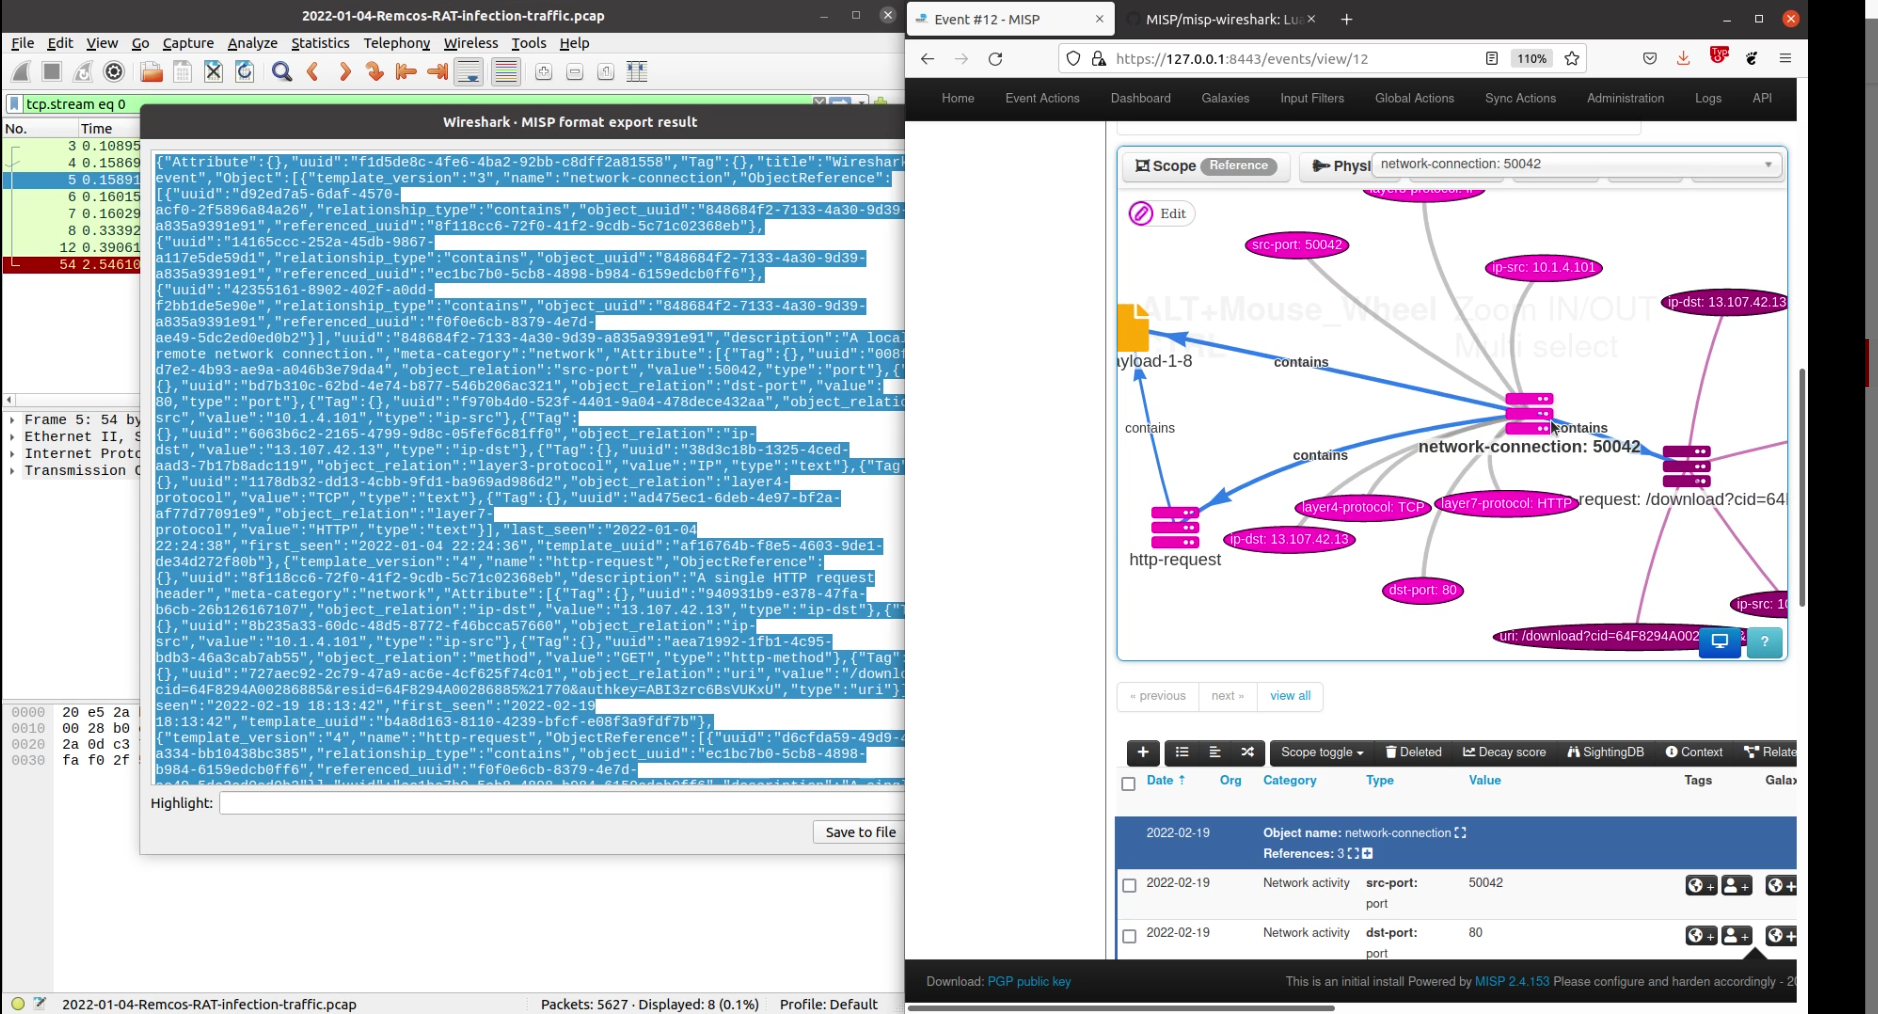
Lua plugin to extract data from Wireshark and convert it into MISP format
 benadia/an-integrated-wireless-network-forensic-analysis-framework
This framework combines a set of existing open source tools into an integrated package that automates the forensics investigation process. It is able…
 wireshark/wireshark
Wireshark's official code repository. You can keep the releases coming by donating at https://wiresharkfoundation.org/donate/.
 netsniff-ng/netsniff-ng
A Swiss army knife for your daily Linux network plumbing.
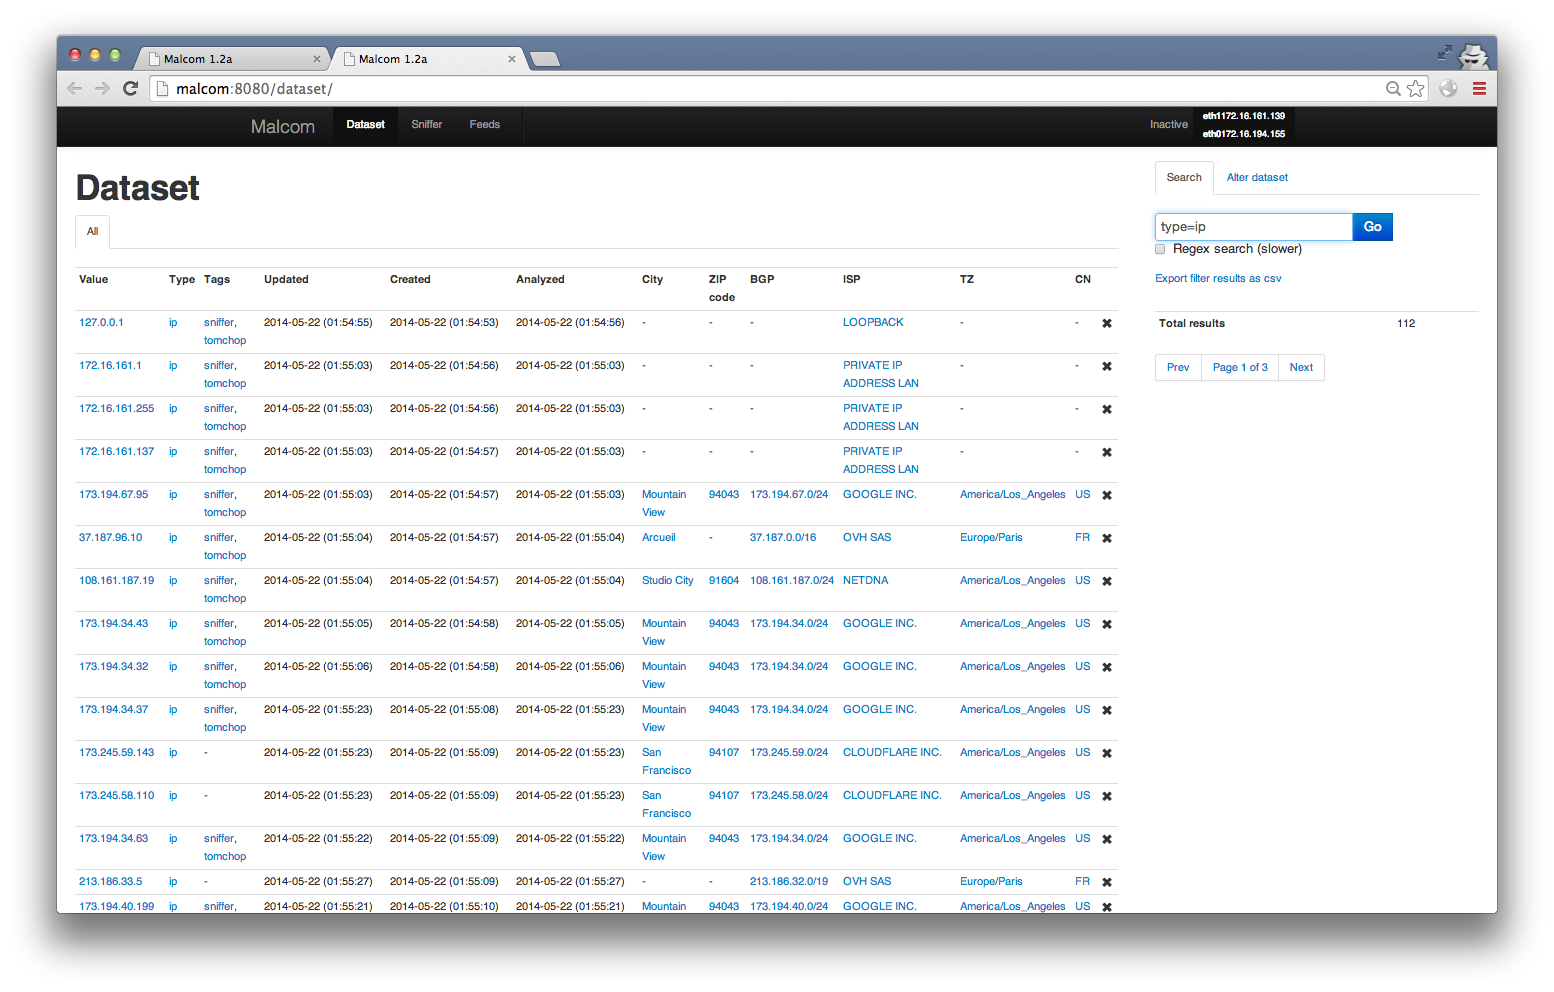 tomchop/malcom
Malcom - Malware Communications Analyzer
 microsoft/etl2pcapng
Utility that converts an .etl file containing a Windows network packet capture into .pcapng format.
 nccgroup/pcap-burp
Pcap importer for Burp
 leonward/openfpc
OpenFPC, Open Source Full Packet Capture
 corelight/zeek-quic
Bro analyzer that detects Google's QUIC protocol
 nccgroup/baskerville
Selective protocol extractor from PCAPs or interfaces

 gcla/termshark
A terminal UI for tshark, inspired by Wireshark
 google/gopacket
Provides packet processing capabilities for Go
 simsong/tcpflow
TCP/IP packet demultiplexer. Download from: