
pyshark
 kiminewt/pyshark
Python wrapper for tshark, allowing python packet parsing using wireshark dissectors
digital-forensicsencryption-decryption-toolsforensics+5
2.5k6 months ago
kiminewt/pysharkPython wrapper for tshark, allowing python packet parsing using wireshark dissectors
 simsong/bulk_extractor
This is the development tree. Production downloads are at:
 simsong/tcpflow
TCP/IP packet demultiplexer. Download from:
 cristianzsh/forensictools
Collection of forensic tools
 eciavatta/caronte
A tool to analyze the network flow during attack/defence Capture the Flag competitions
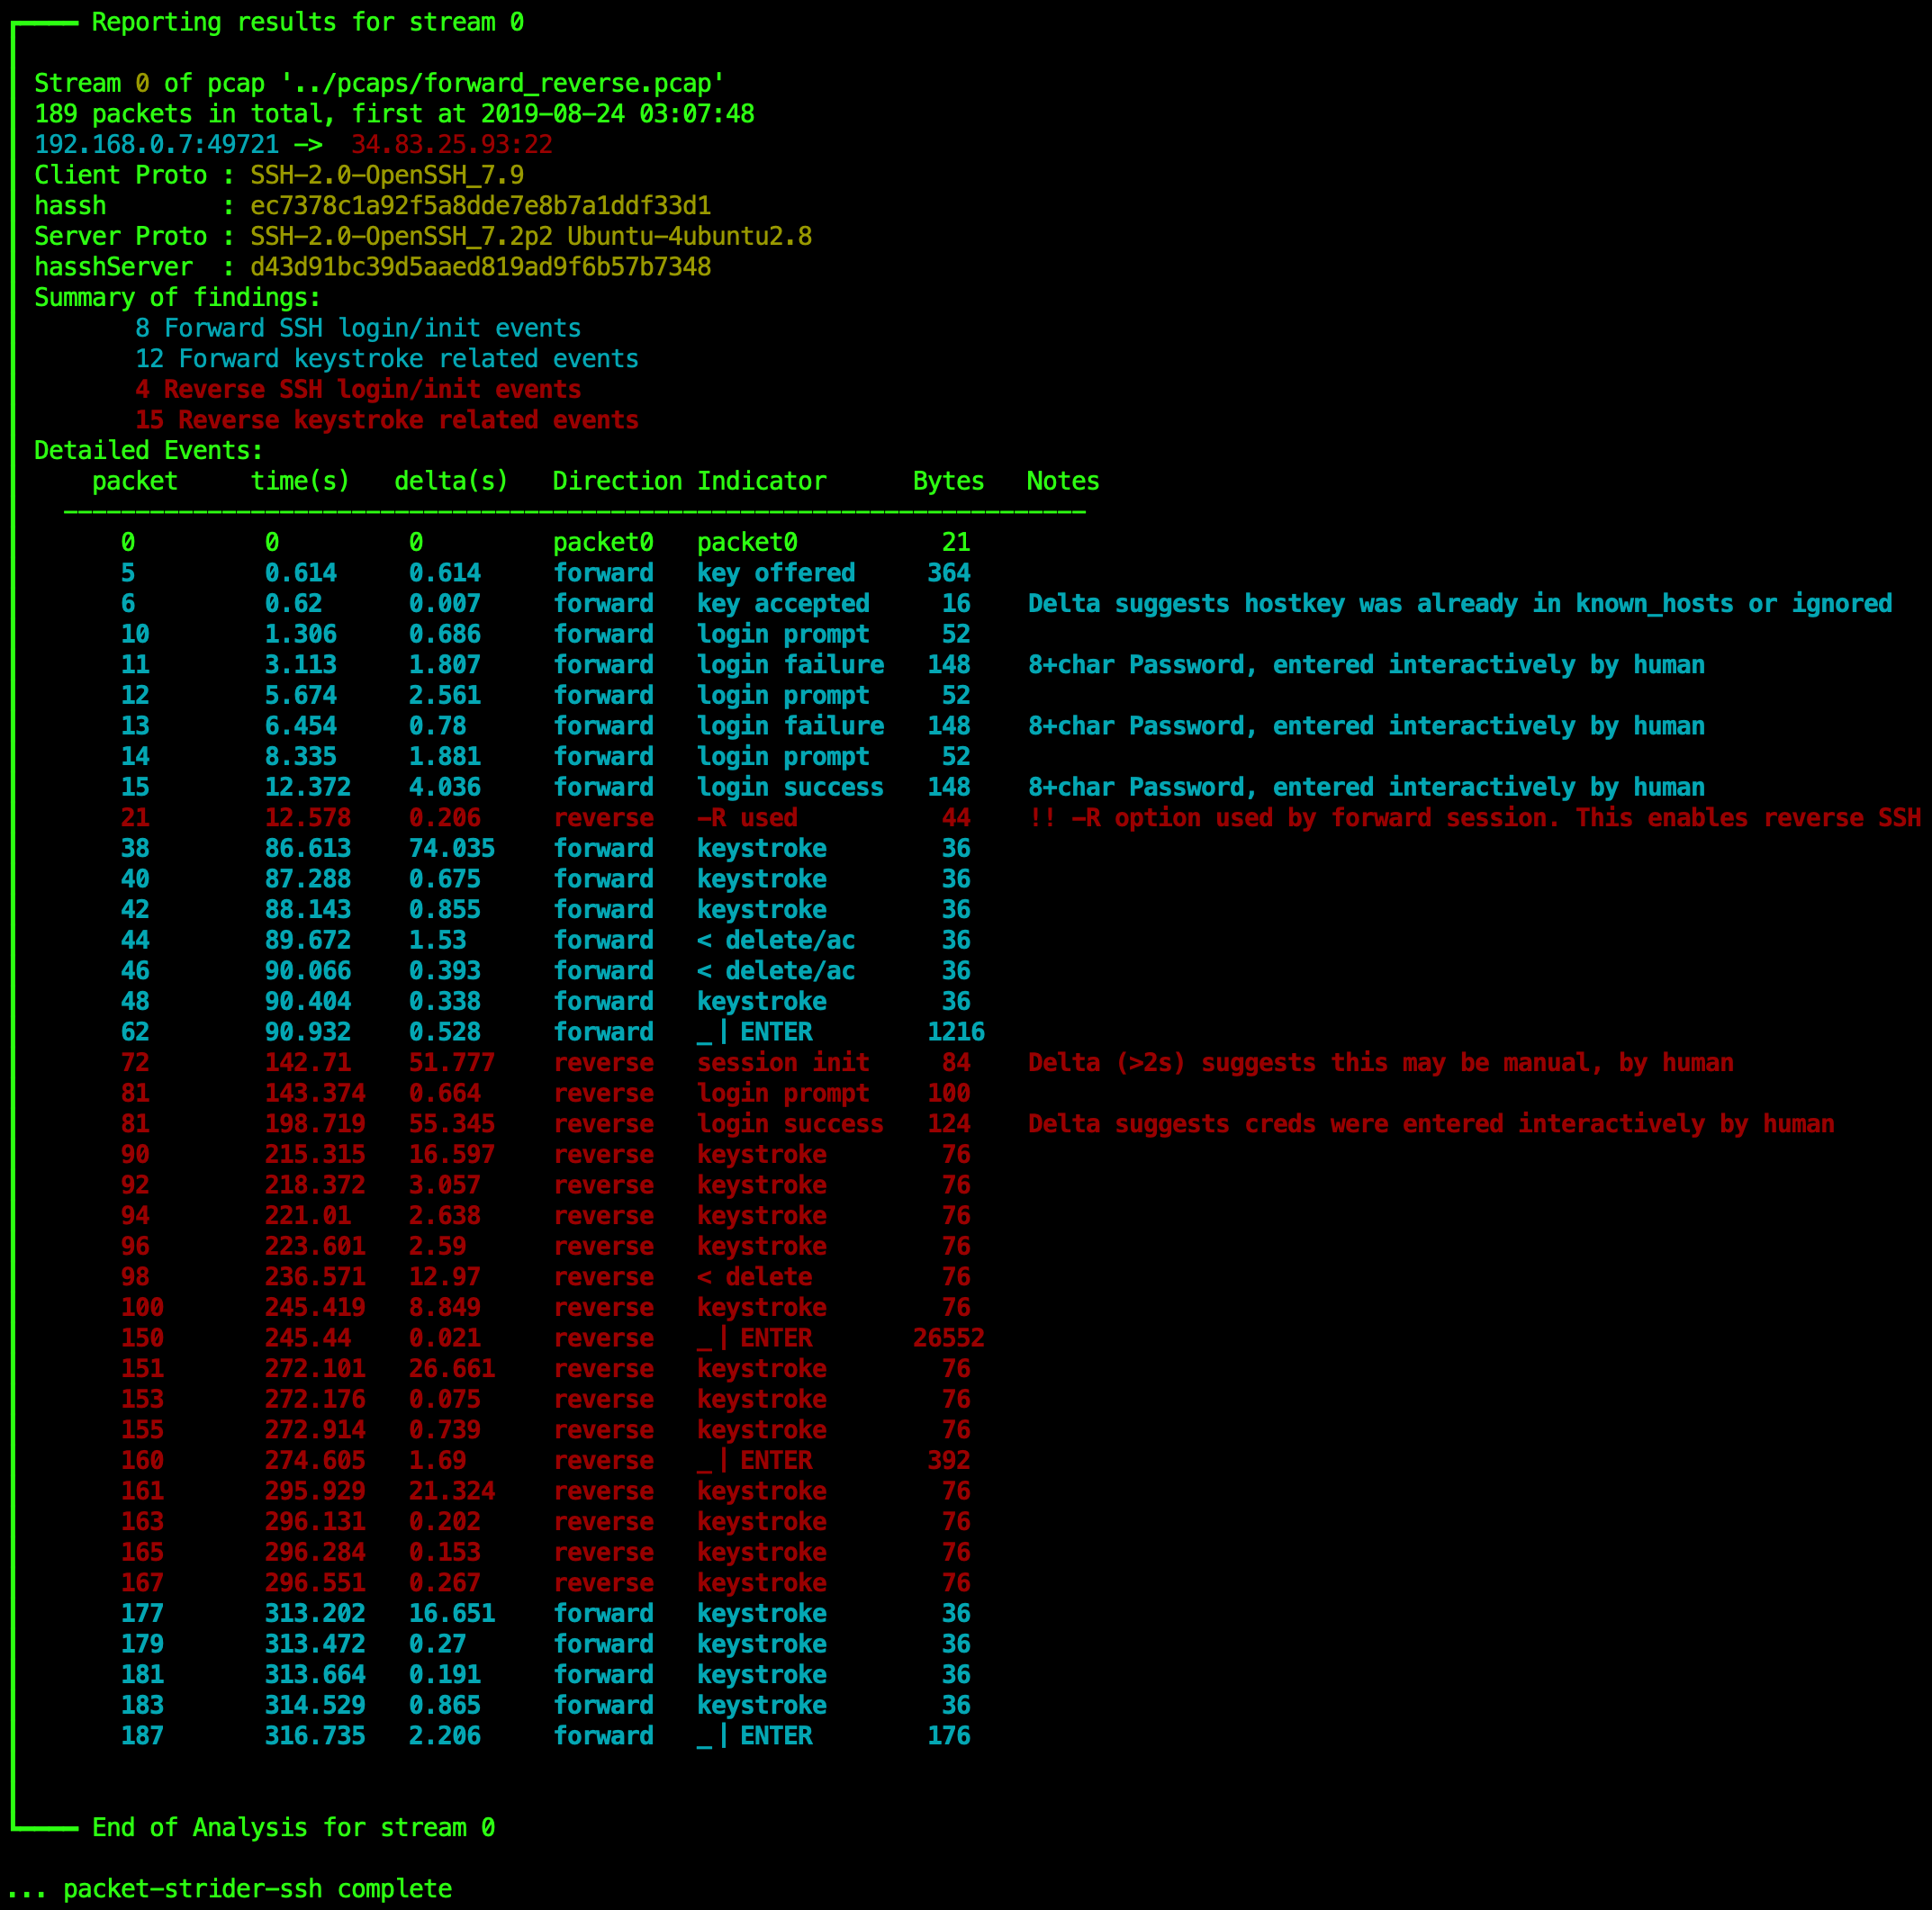 benjeems/packetstrider
A network packet forensics tool for SSH
 cyb3r-monk/rita-j
Implementation of RITA (Real Intelligence Threat Analytics) in Jupyter Notebook with improved scoring algorithm.
 awakecoding/wireshark-rdp
Wireshark RDP resources
 mspicer/pcapinator
A tool for processing a lot of pcaps using tshark
 azizaltuntas/network-analysis-tools
Pcap (capture file) Analysis Toolkit(v.1)
 halildeniz/networkassessment
NetworkAssessment: Network Compromise Assessment Tool
 sydsec/syd
Offline AI Security Assistant for Air-Gapped Pentesting
 weirdmachine64/sharkmcp
A swiss-knife MCP server for analysing PCAP files
 kybr-git/dc30-badge-challenge-writeup
Writeup for the DEF CON 30 badge challenge
 corelight/zeek-community-id
Zeek support for Community ID flow hashing.
 formerlab/shadow-fleet-tracker-light
Open source Baltic Sea shadow fleet tracker. 1200+ vessels, live AIS, cable proximity alerts. No cloud, no subscription, runs locally
 cyberhatcoil/acf
Android Connections Forensics
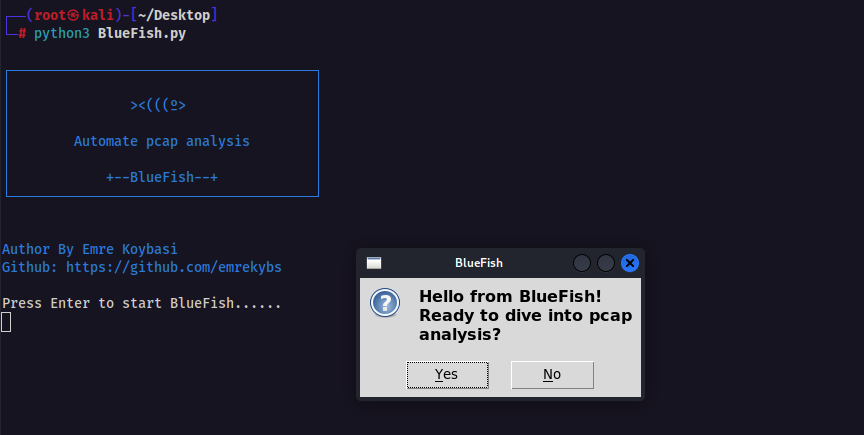 emrekybs/bluefish
Automation tool designed to simplify the analysis of PCAP (Packet Capture) files