


 gcla/termshark
A terminal UI for tshark, inspired by Wireshark
 google/gopacket
Provides packet processing capabilities for Go
 cyb3rmx/qu1cksc0pe
All-in-One malware analysis tool.
 simsong/bulk_extractor
This is the development tree. Production downloads are at:
 kiminewt/pyshark
Python wrapper for tshark, allowing python packet parsing using wireshark dissectors
 simsong/tcpflow
TCP/IP packet demultiplexer. Download from:
 cristianzsh/forensictools
Collection of forensic tools
 eciavatta/caronte
A tool to analyze the network flow during attack/defence Capture the Flag competitions
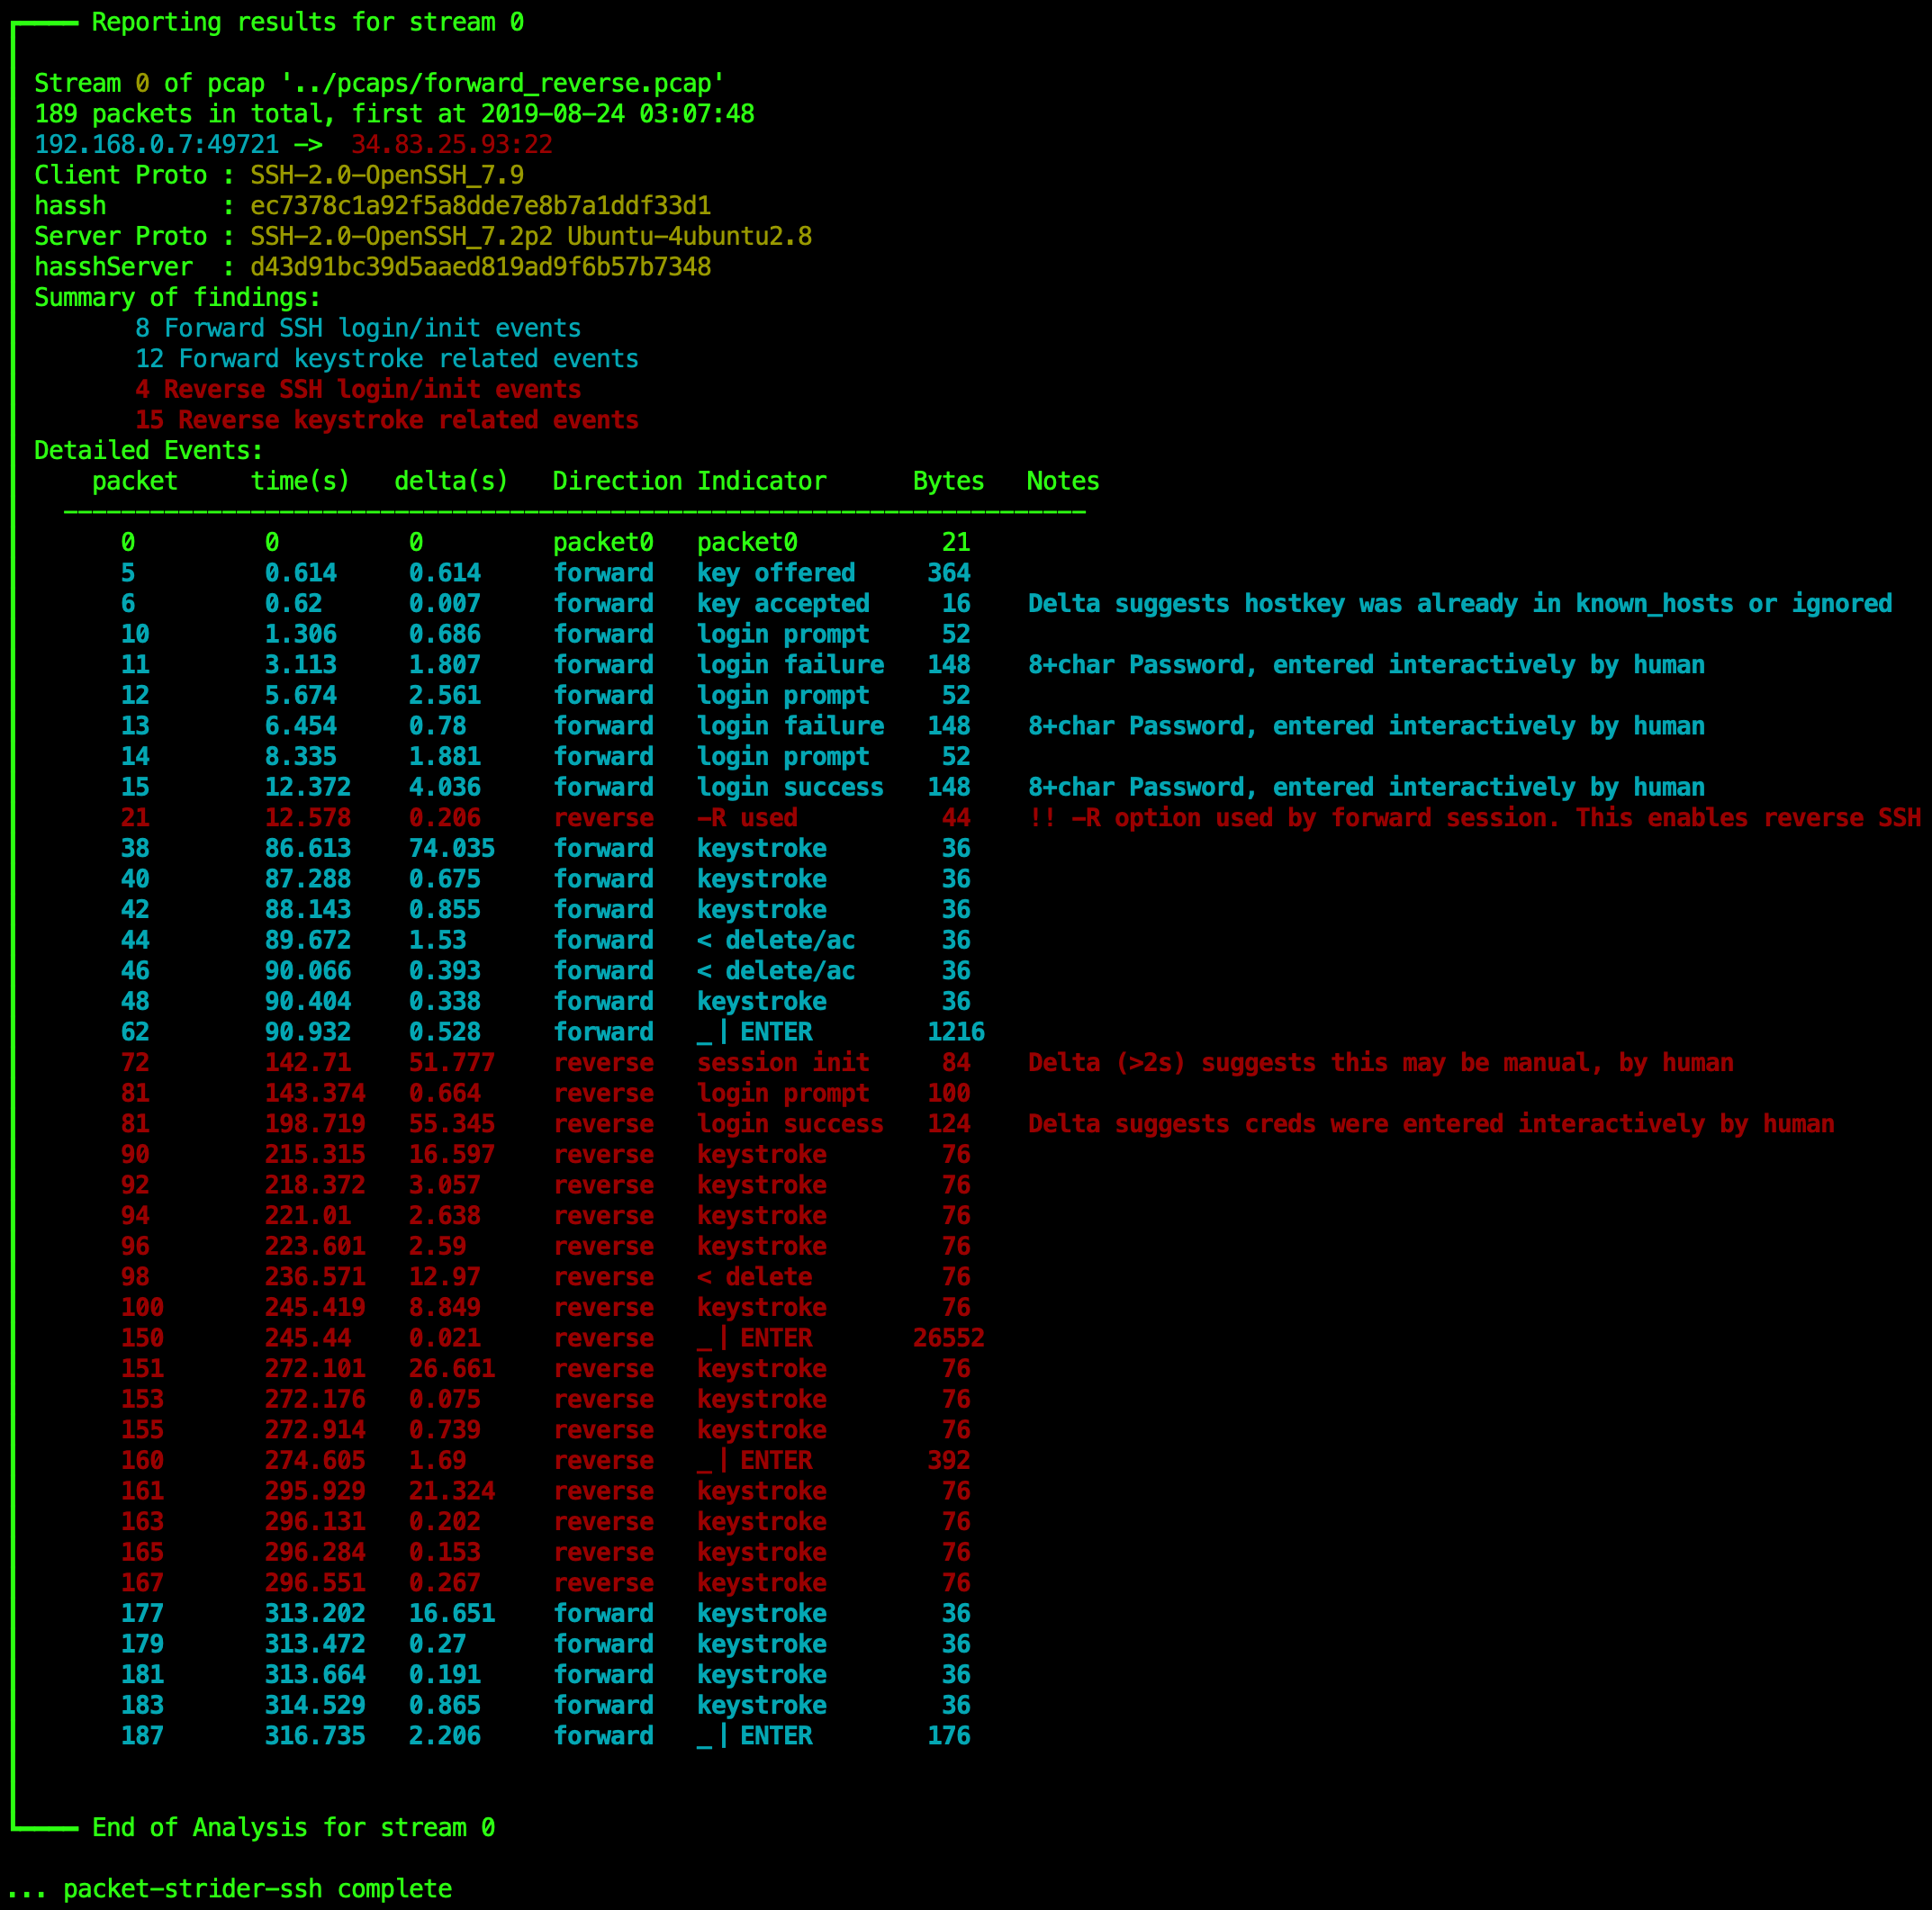 benjeems/packetstrider
A network packet forensics tool for SSH
 awakecoding/wireshark-rdp
Wireshark RDP resources
 mspicer/pcapinator
A tool for processing a lot of pcaps using tshark
 azizaltuntas/network-analysis-tools
Pcap (capture file) Analysis Toolkit(v.1)
 halildeniz/networkassessment
NetworkAssessment: Network Compromise Assessment Tool
 sydsec/syd
Offline AI Security Assistant for Air-Gapped Pentesting
 weirdmachine64/sharkmcp
A swiss-knife MCP server for analysing PCAP files
 kybr-git/dc30-badge-challenge-writeup
Writeup for the DEF CON 30 badge challenge