

plugxdecoder
 kcreyts/plugxdecoder
Decodes PlugX traffic and encrypted/compressed artifacts
digital-forensicsencryption-decryption-toolsforensics+3
38
kcreyts/plugxdecoderDecodes PlugX traffic and encrypted/compressed artifacts
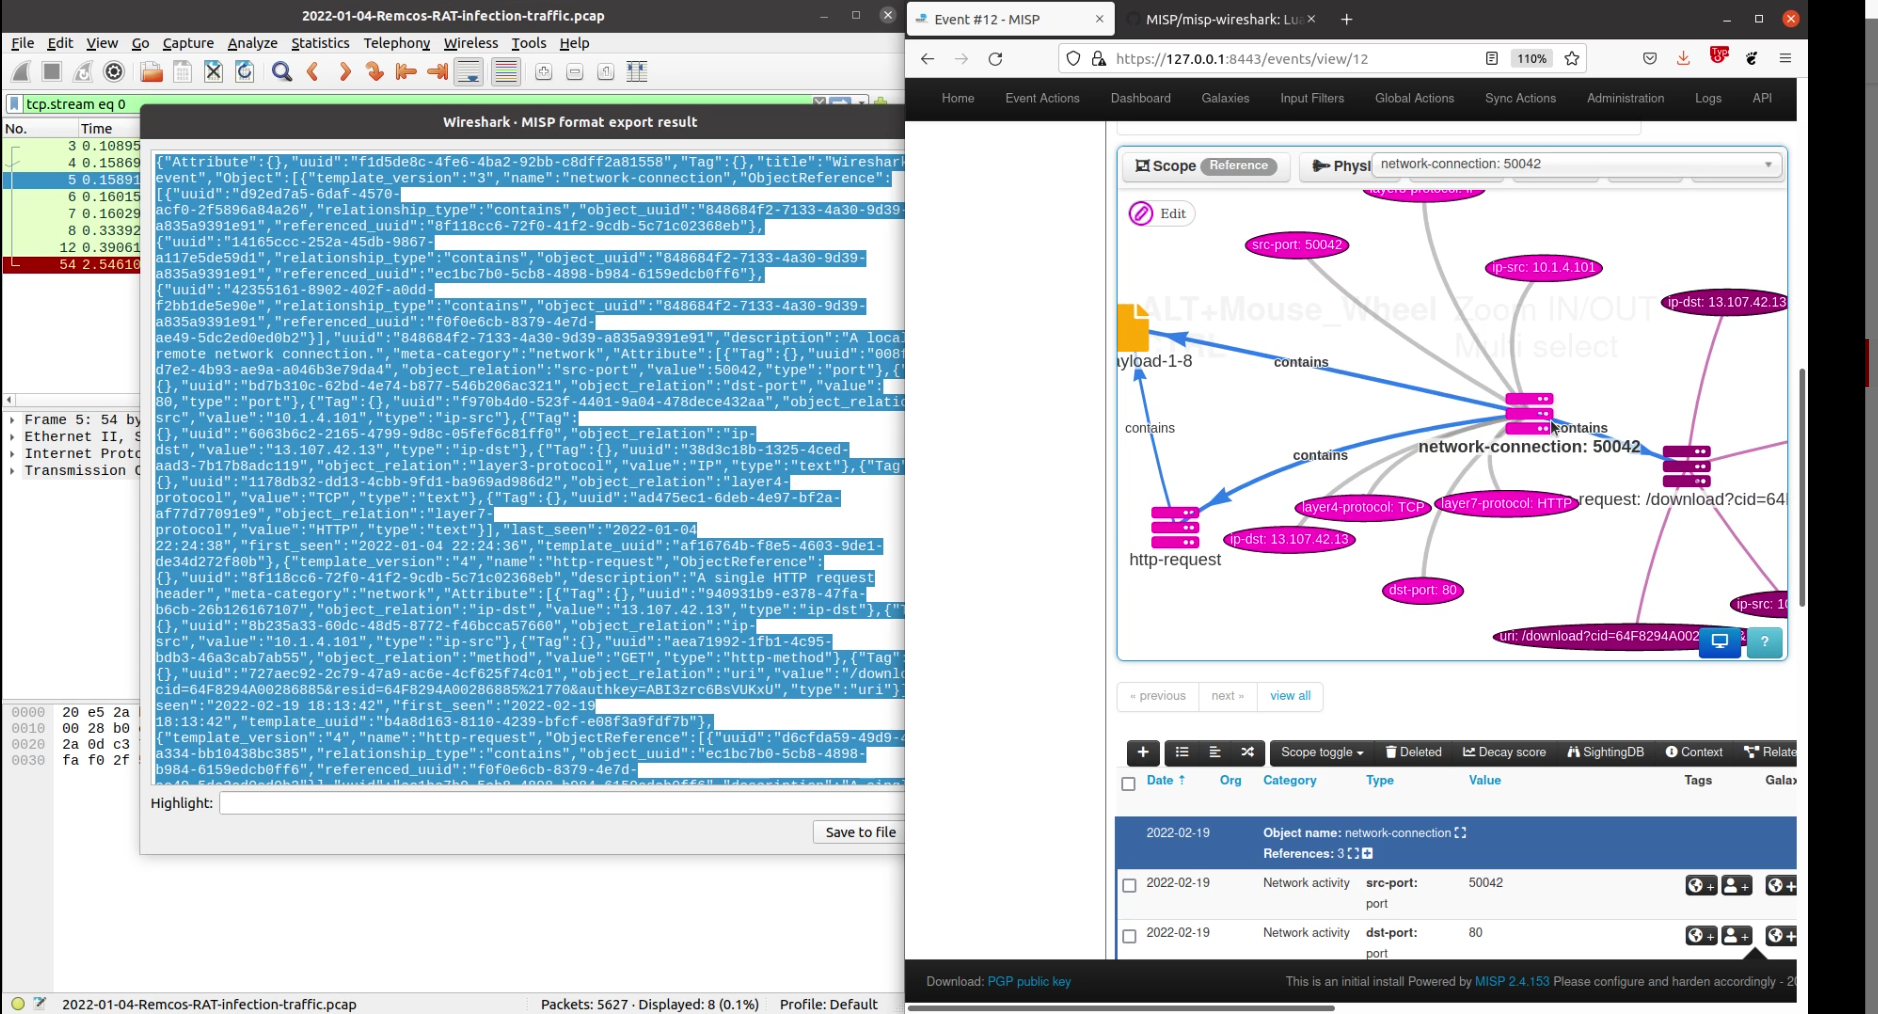 misp/misp-wireshark
Lua plugin to extract data from Wireshark and convert it into MISP format

 lpefferkorn/ipdecap
Decapsulate traffic encapsulated within GRE, IPIP, 6in4, ESP (ipsec) protocols, can also remove IEEE 802.1Q (virtual lan) header. Works with pcap…
 formerlab/shadow-fleet-tracker-light
Open source Baltic Sea shadow fleet tracker. 1200+ vessels, live AIS, cable proximity alerts. No cloud, no subscription, runs locally
 naacbin/covenantdecryptor
Decrypts Covenant C2 communications by extracting RSA private keys from minidumps, recovering AES session keys, and converting network captures to…
 cyberhatcoil/acf
Android Connections Forensics
 emrekybs/bluefish
Automation tool designed to simplify the analysis of PCAP (Packet Capture) files
 r3mrum/loki-parse
A python script that can detect and parse loki-bot (malware) related network traffic. This script can be helpful to DFIR analysts and security…
 securityronin/memory-forensic
Walk any memory dump. Find what's hidden. Linux + Windows kernel forensics from a single static Rust binary — no Python required.
 synacktiv/pcapan
A pcap capture analysis helper
 corelight/zeek-spicy-ipsec
A Zeek IPSec protocol analyzer based on Spicy.
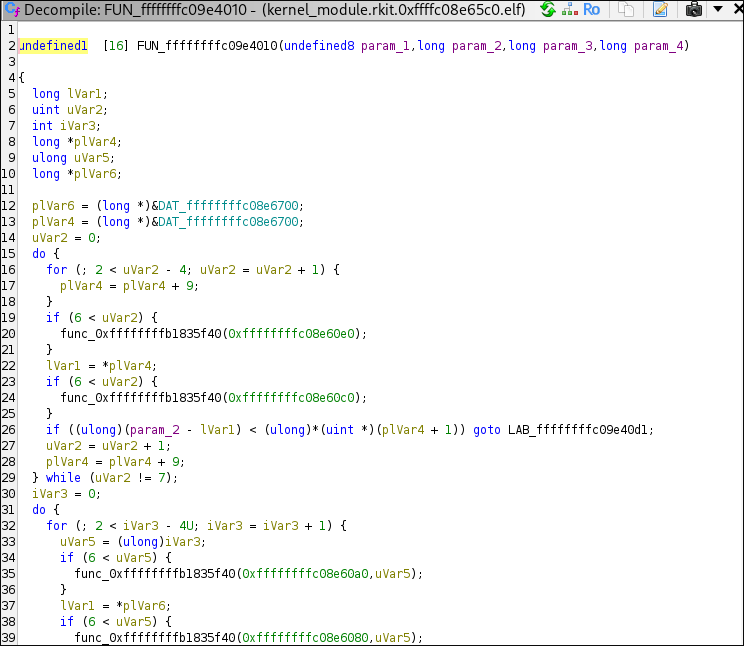 ic3-512/linux-root-kit
End-to-end simulation of a Python dependency confusion attack, sudo privilege escalation (CVE-2025-32463), and rootkit-based persistence - with full…

 nccgroup/baskerville
Selective protocol extractor from PCAPs or interfaces
 jgoyd/fourteen_endpoints
Shell Companies Inside Apple's Privacy Relay
 abiral-timalsina/cyber-defenders-lab-
My write-ups from CyberDefenders' Blue Team labs, solved using Wireshark. Covers TeamCity RCE (CVE-2024-27198), XSS session hijacking, and…
 nao-sec/ramnit_traffic_parser
Parsing Ramnit's traffic