
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
139 results
DFIR4vSphere preview

DFIR4vSphere

GitHubanssi-fr/dfir4vsphere

Powershell module for VMWare vSphere forensics
cloud-infrastructure-securityconfiguration-auditingdefensive-tools+5
189
1 year ago
zeek-community-id preview

zeek-community-id

GitHubcorelight/zeek-community-id

Zeek support for Community ID flow hashing.
log-analysisnetwork-forensicsnetwork-security+1
373 years ago
OpenFPC preview

OpenFPC

GitHubleonward/openfpc

OpenFPC, Open Source Full Packet Capture
forensicsnetwork-forensicsnetwork-security+1
7310 years ago
ndff preview

ndff

GitHubknqyf263/ndff

A flow-based network monitor with Deep Packet Inspection
dns-analysislog-analysisnetwork-forensics+2
289 years ago
zeek-quic preview

zeek-quic

GitHubcorelight/zeek-quic

Bro analyzer that detects Google's QUIC protocol
intrusion-detectionlog-analysisnetwork-forensics+2
125 years ago
zeek-spicy-wireguard preview

zeek-spicy-wireguard

GitHubcorelight/zeek-spicy-wireguard

A Zeek Wireguard protocol analyzer based on Spicy.
network-forensicsnetwork-securitypacket-sniffing-analysis
77 months ago
zeek-spicy-ospf preview

zeek-spicy-ospf

GitHubcorelight/zeek-spicy-ospf

A Zeek OSPF packet analyzer based on Spicy.
anomaly-detectionnetwork-forensicsnetwork-mapping+2
81 year ago
Baskerville preview

Baskerville

GitHubnccgroup/baskerville

Selective protocol extractor from PCAPs or interfaces
incident-responsenetwork-forensicsnetwork-security+1
511 years ago
stenographer preview
Archived

stenographer

GitHubgoogle/stenographer

Stenographer is a packet capture solution which aims to quickly spool all packets to disk, then provide simple, fast access to subsets of those…
forensicsincident-responseintrusion-detection+3
1.8k5 years ago
tcpdump preview

tcpdump

GitHubthe-tcpdump-group/tcpdump

the TCPdump network dissector

dns-analysisforensicslog-analysis+5
3.2k1 month ago
caronte preview

caronte

GitHubeciavatta/caronte

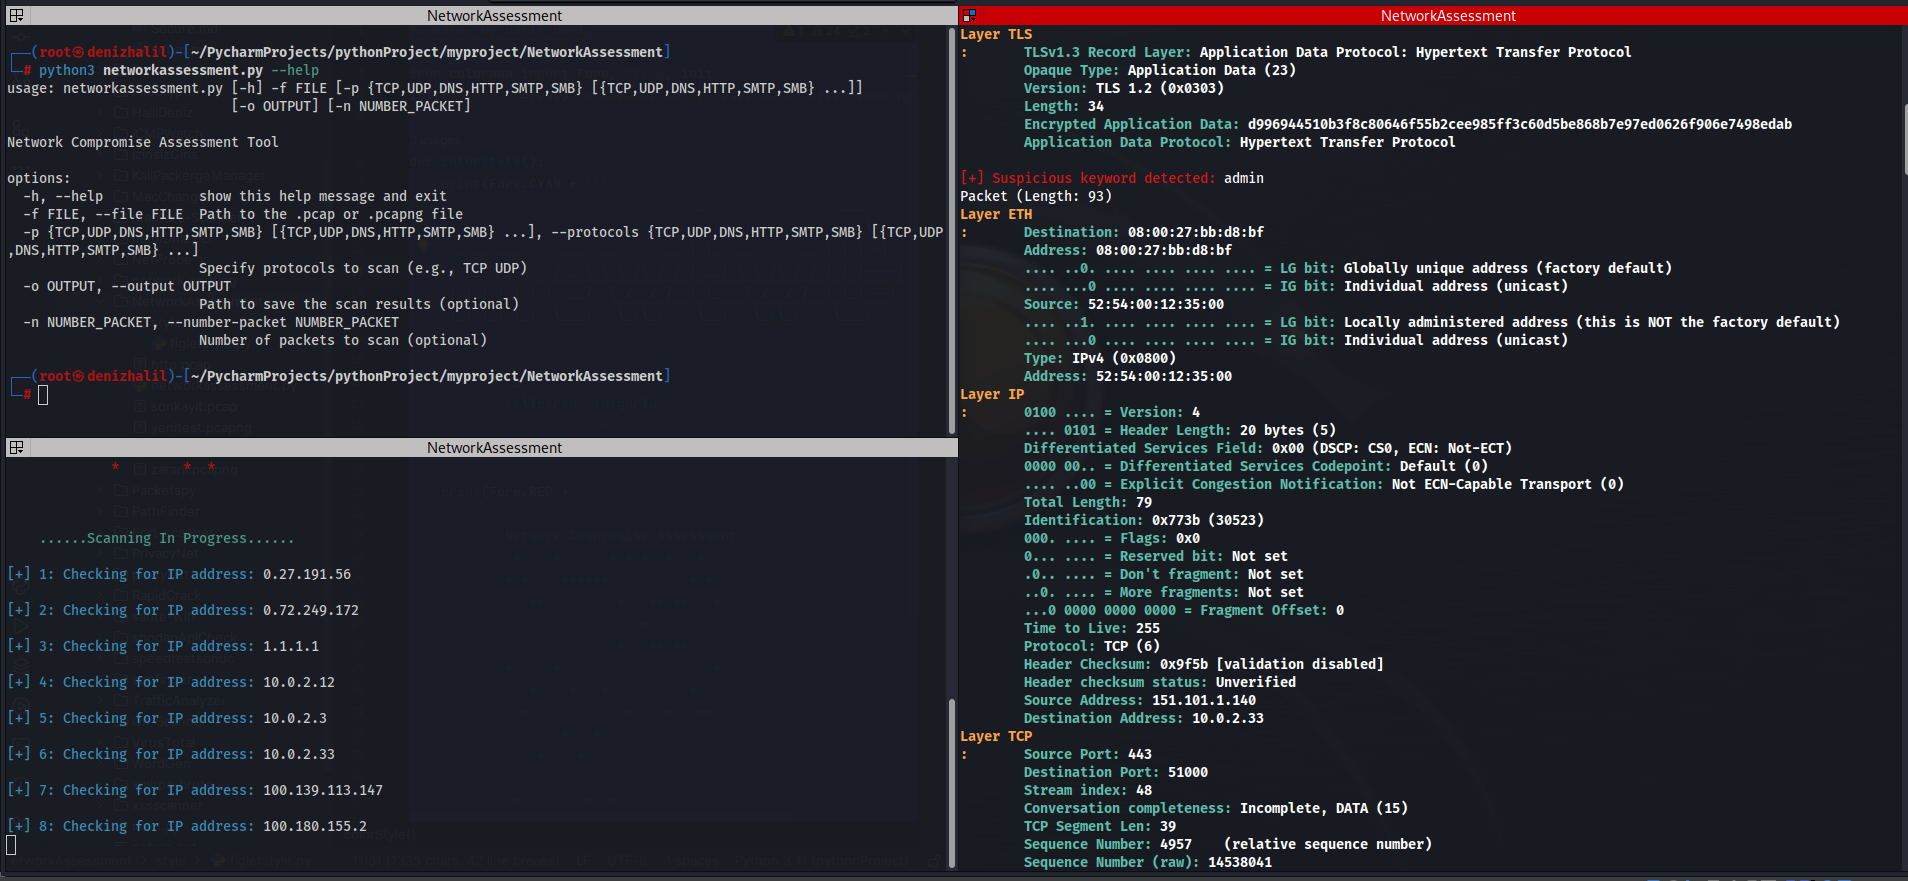
A tool to analyze the network flow during attack/defence Capture the Flag competitions
ctfforensicsnetwork-forensics+1
6544 years ago
NetworkAssessment preview

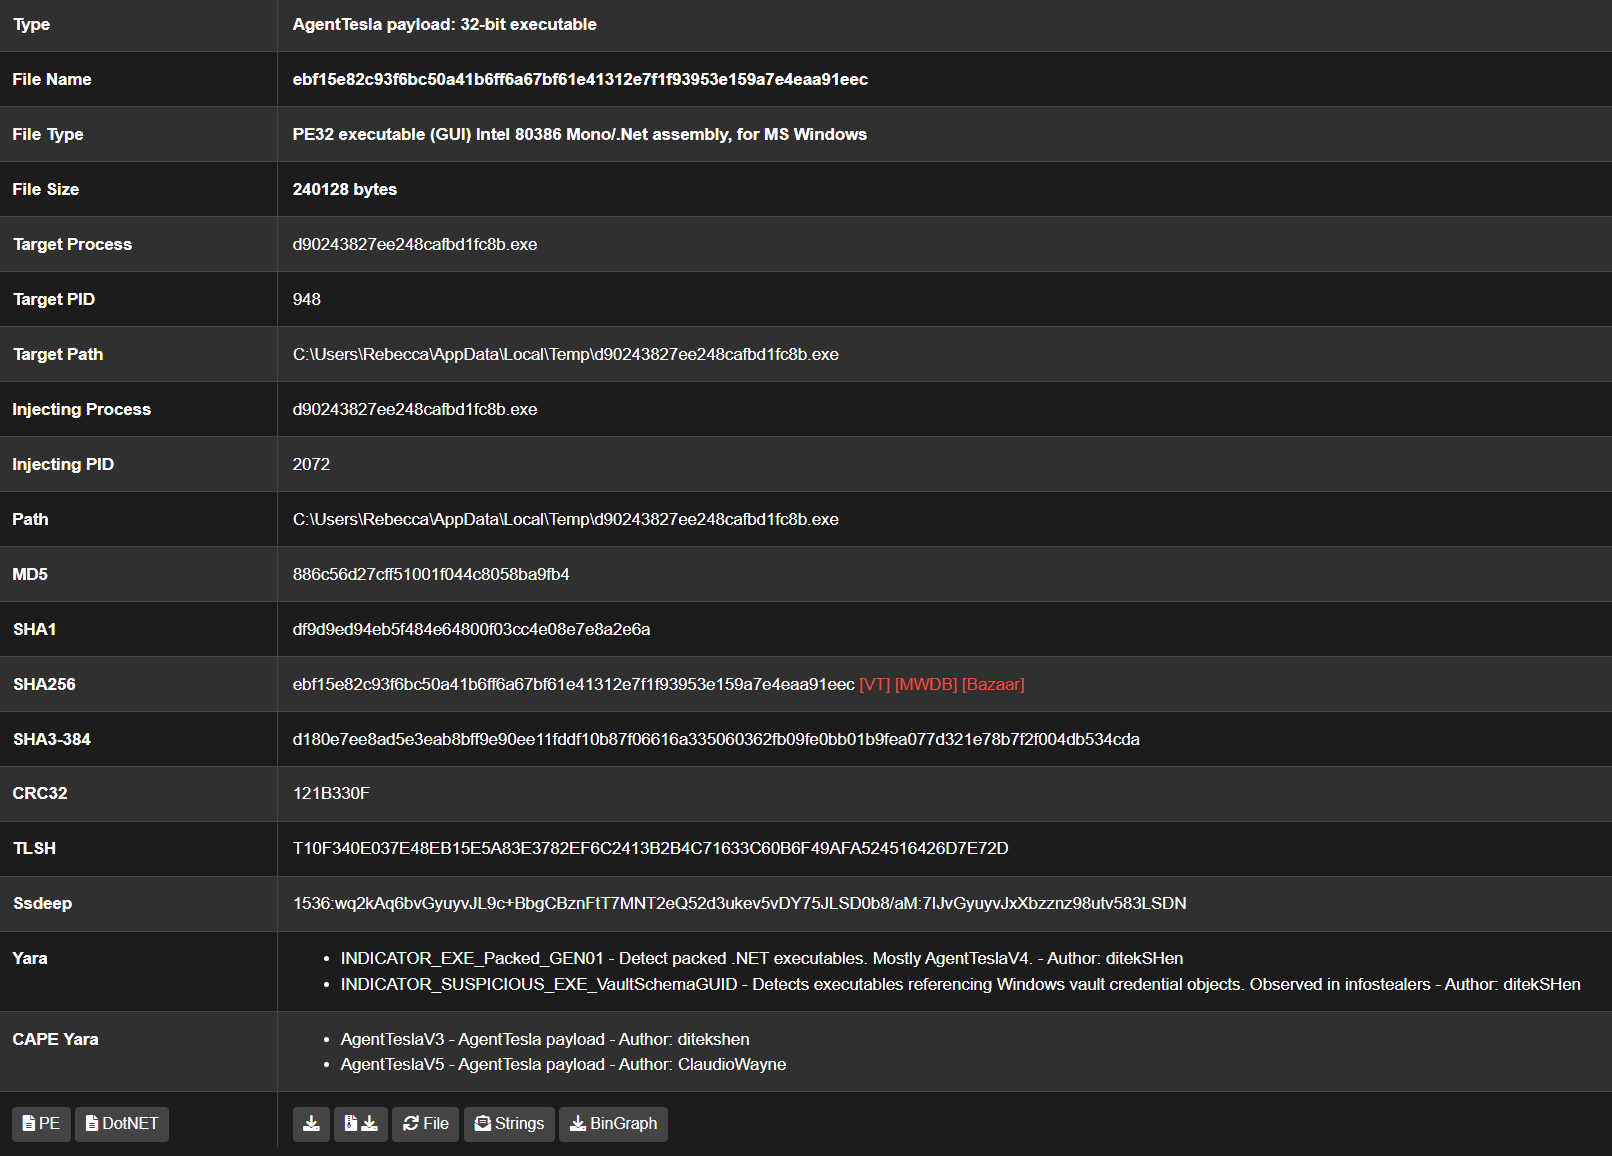
NetworkAssessment

GitHubhalildeniz/networkassessment

NetworkAssessment: Network Compromise Assessment Tool
dns-analysisforensicsintrusion-detection+4
952 years ago
zeek-spicy-ipsec preview

zeek-spicy-ipsec

GitHubcorelight/zeek-spicy-ipsec

A Zeek IPSec protocol analyzer based on Spicy.
intrusion-detectionnetwork-forensicsnetwork-security+1
81 year ago
maltrail preview

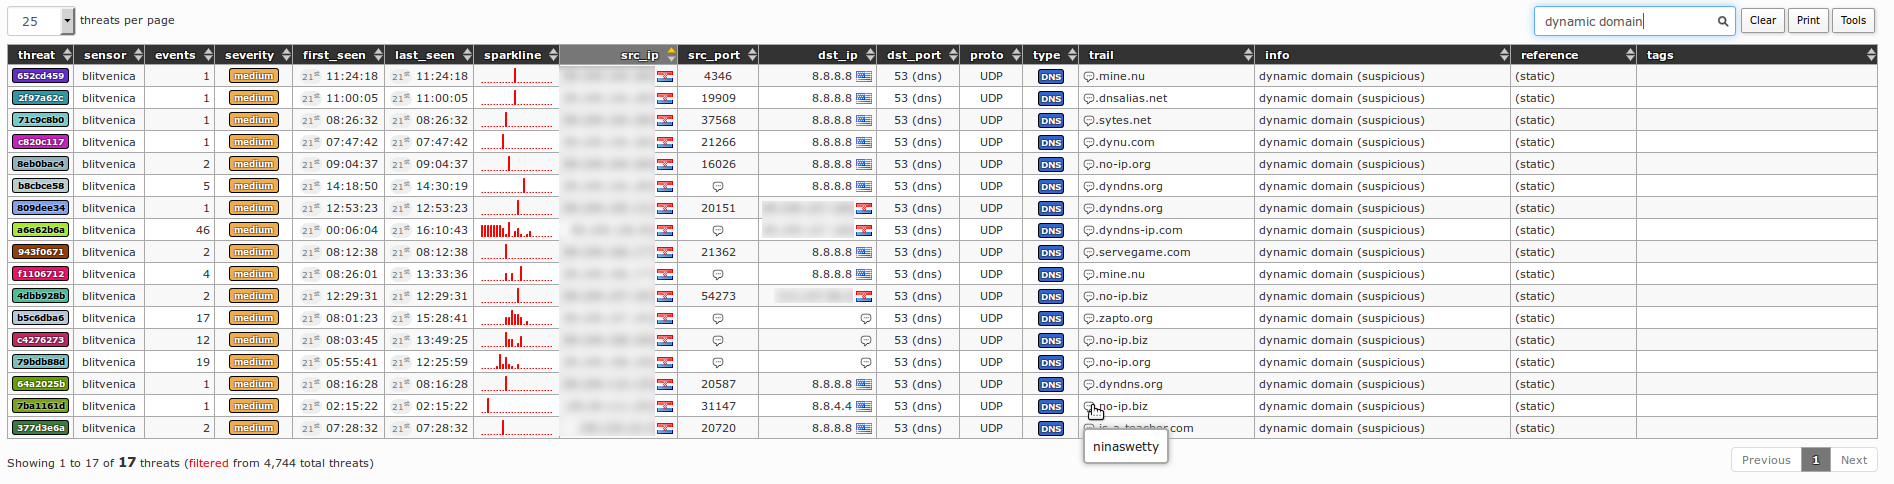
maltrail

GitHubstamparm/maltrail

Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
anomaly-detectionanti-botdefensive-tools+11
8.6k20h 28m ago
suricata preview

suricata

GitHuboisf/suricata

Open-source network IDS/IPS/NSM engine for real-time traffic inspection, intrusion detection and prevention, protocol analysis, and rule-based threat…
anomaly-detectionanti-botdefensive-tools+9
6.7k5 days ago
CAPEv2 preview

CAPEv2

GitHubkevoreilly/capev2

Malware Configuration And Payload Extraction
debuggersdynamic-analysis-sandboxingeducation+6
3.6k3 days ago
CAPEsolo preview

CAPEsolo

GitHubcapesandbox/capesolo

Standalone Windows VM malware sandbox running capemon, with GUI triage viewer, YARA signatures, IOC extraction, network analysis, and…
defensive-toolsdynamic-analysis-sandboxingforensics+7
6010 days ago
ltm preview

ltm

GitHubagent-hellboy/ltm

ltm is a machine-history debugger for Linux. It records process, file, network, memory, and block-I/O metadata via eBPF, then lets you query the…

debuggersdigital-forensicsdisk-forensics+7
252 months ago
Previous1…5678Next