
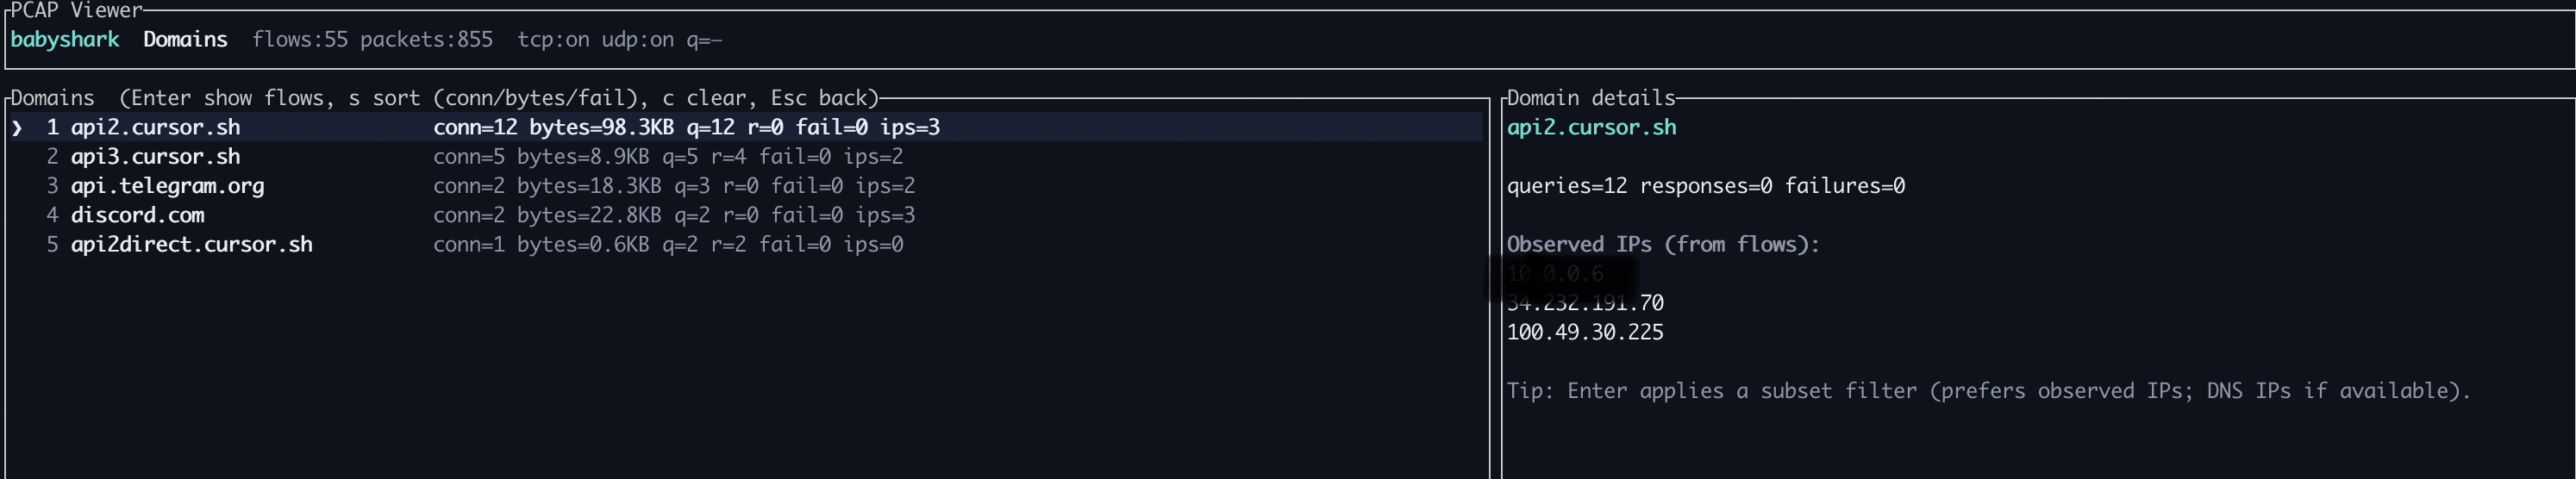
babyshark
 vignesh07/babyshark
Flows-first PCAP TUI (case files, gorgeous UX). Do do do do.
anomaly-detectiondns-analysisforensics+5
vignesh07/babysharkFlows-first PCAP TUI (case files, gorgeous UX). Do do do do.
 awakecoding/wireshark-rdp
Wireshark RDP resources
 vikwin/pcapfex
'Packet Capture Forensic Evidence eXtractor' is a tool that finds and extracts files from packet capture files
 rjbhide/wireshark-forensics-plugin
Wireshark plugin that correlates network traffic with threat intelligence, asset tags, and vulnerability data to accelerate forensic analysis of PCAP…
 anssi-fr/dfir4vsphere
Powershell module for VMWare vSphere forensics
 nccgroup/pcap-burp
Pcap importer for Burp
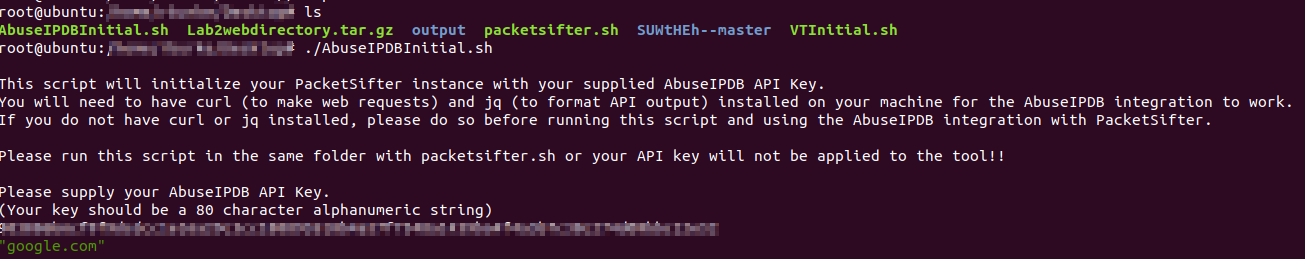 packetsifter/packetsiftertool
PacketSifter is a tool/script that is designed to aid analysts in sifting through a packet capture (pcap) to find noteworthy traffic. Packetsifter…
 capesandbox/capesolo
Standalone Windows VM malware sandbox running capemon, with GUI triage viewer, YARA signatures, IOC extraction, network analysis, and…
 leonward/openfpc
OpenFPC, Open Source Full Packet Capture
 kdbugk/game-of-kingshot-re
Educational reverse engineering study of a Unity/IL2CPP Android game. Documents gateway protocol decoding, native anti-tampering SDK analysis, SSL…
 kybr-git/dc30-badge-challenge-writeup
Writeup for the DEF CON 30 badge challenge
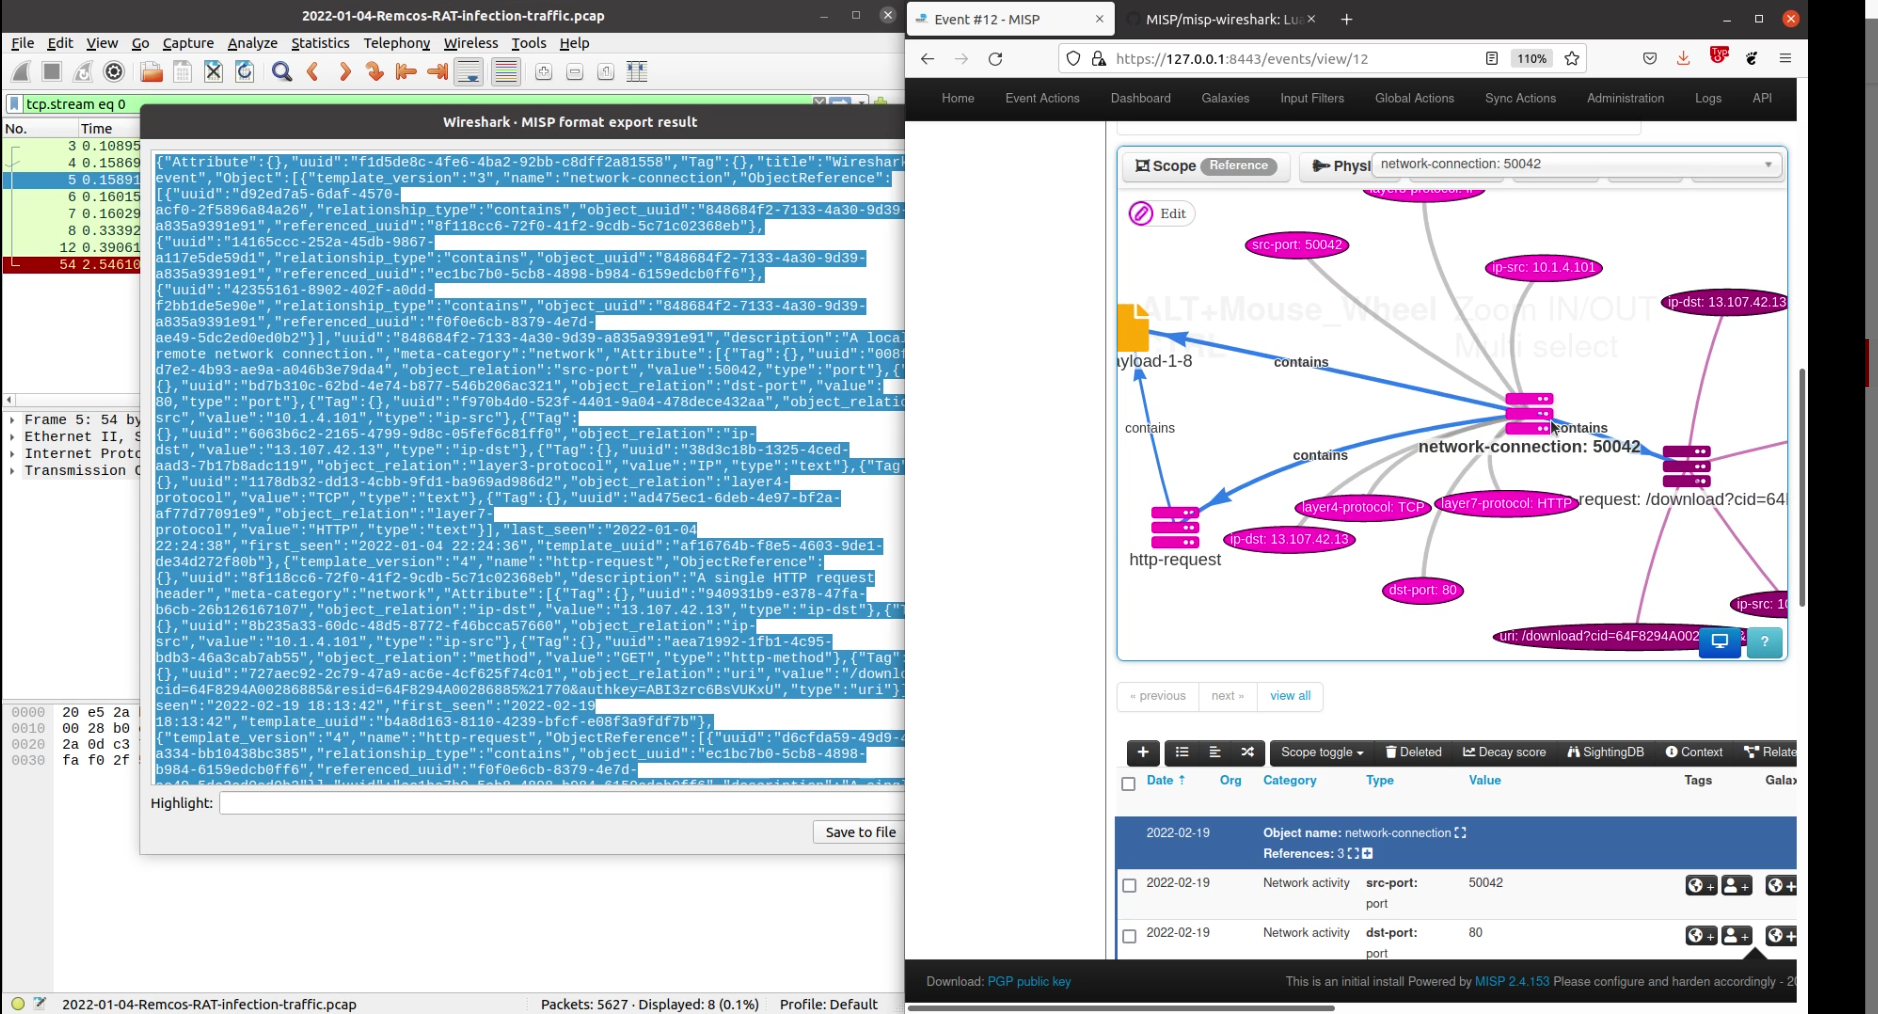 misp/misp-wireshark
Lua plugin to extract data from Wireshark and convert it into MISP format
 corelight/zeek-community-id
Zeek support for Community ID flow hashing.
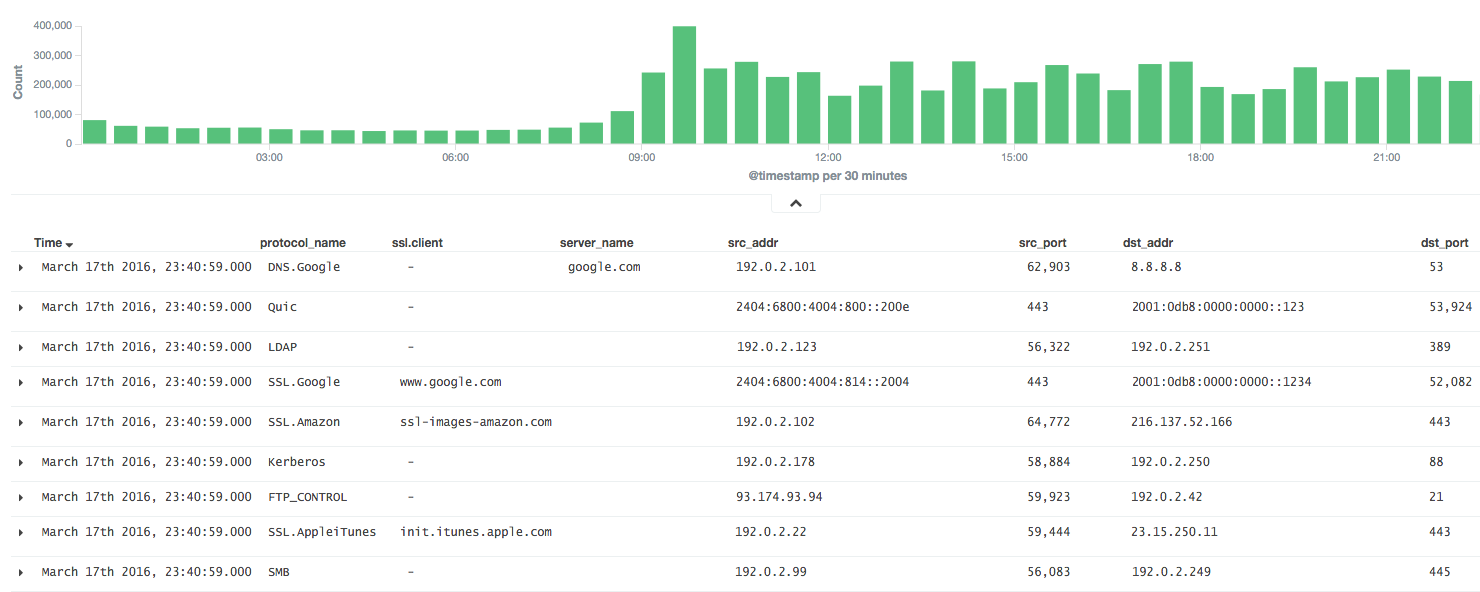 knqyf263/ndff
A flow-based network monitor with Deep Packet Inspection
 synacktiv/pcapan
A pcap capture analysis helper
 nccgroup/mortimer
A collection of scripts for processing network forensics type data and intelligence, mainly into a postgres database.
 corelight/zeek-spicy-ipsec
A Zeek IPSec protocol analyzer based on Spicy.
 corelight/zeek-spicy-wireguard
A Zeek Wireguard protocol analyzer based on Spicy.