

linux-root-kit
 ic3-512/linux-root-kit
End-to-end simulation of a Python dependency confusion attack, sudo privilege escalation (CVE-2025-32463), and rootkit-based persistence - with full…
command-and-controldigital-forensicseducation+8
10
ic3-512/linux-root-kitEnd-to-end simulation of a Python dependency confusion attack, sudo privilege escalation (CVE-2025-32463), and rootkit-based persistence - with full…
 benadia/an-integrated-wireless-network-forensic-analysis-framework
This framework combines a set of existing open source tools into an integrated package that automates the forensics investigation process. It is able…
 alzeaty1/security-writeups
CTF writeups and teaching scripts for web security, bug bounty techniques, and network forensics, with blank-value versions for active practice.
 mohamedbrek/soc335-cve-2024-49138-exploitation-detected
LetsDefend SOC lab investigating CVE-2024-49138 exploitation and related malicious activity.
 spectralzero/netscope
Offline-first network investigation and response platform for Windows. Turns a pcap or live capture into a full forensic verdict — attack story,…
 ahmed-tarek22752/rce-cve-2017-0199-detection-analysis
This repository contains a full blue-team malware analysis of a real malicious DOCX exploiting CVE-2017-0199. The lab includes sandbox execution,…
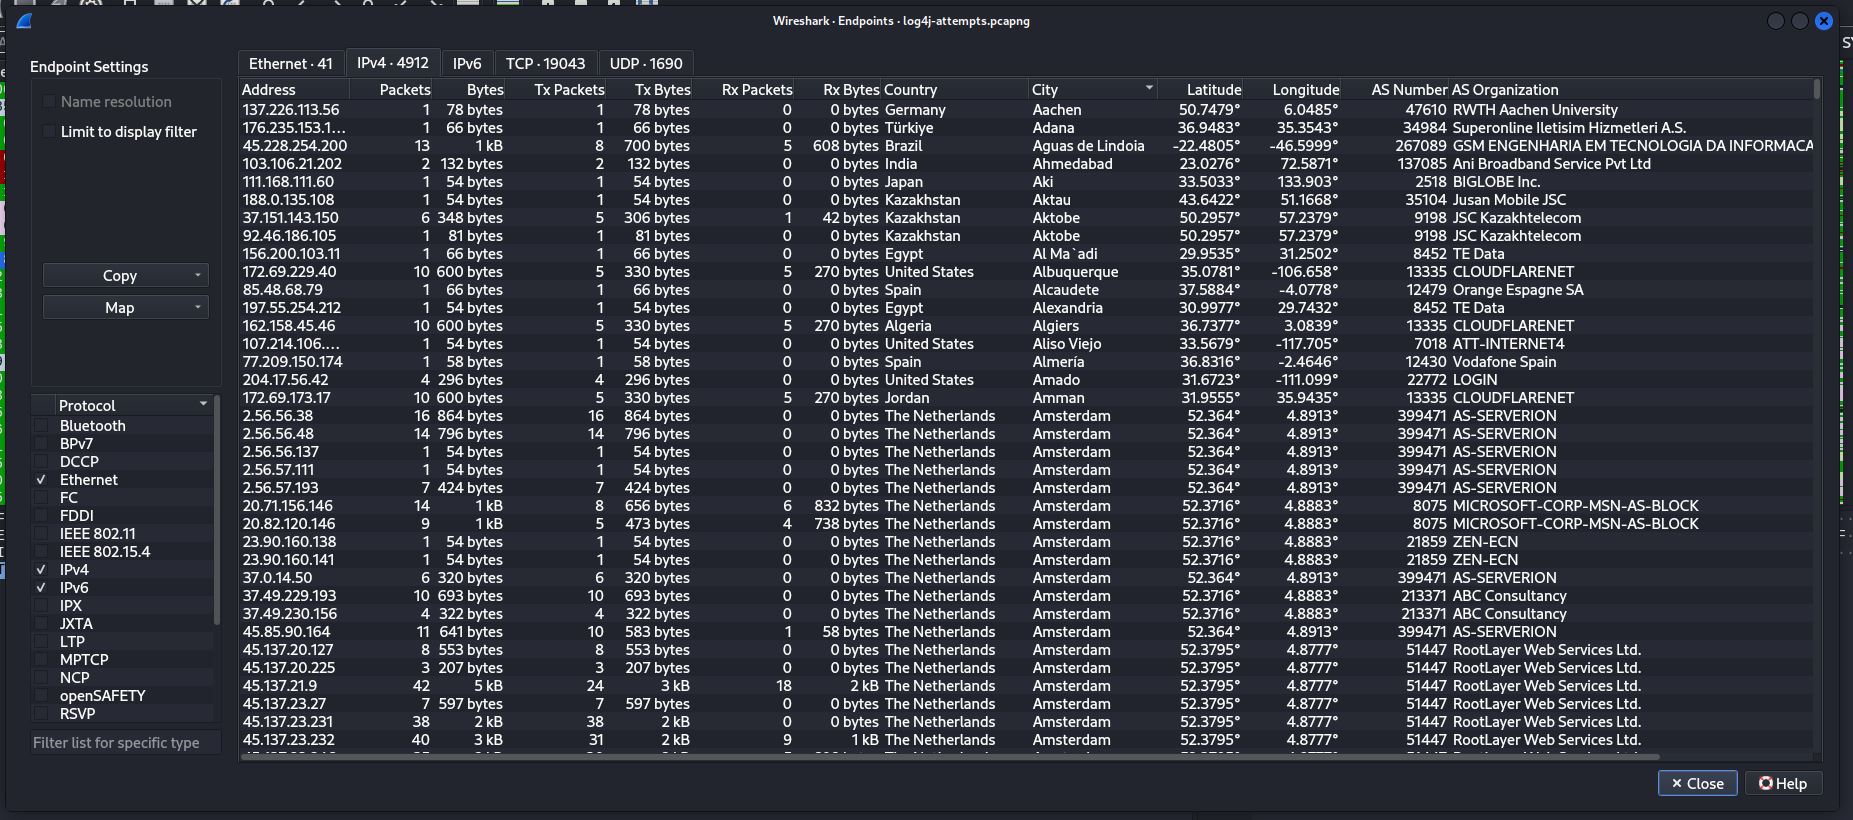 kirkdjohnson/wireshark
Downloaded a packet capture (.pcapng) file from malware-traffic-analysis.net which was an example of an attempted attack against a webserver using…
 zedocun/incident-analysis-response-check-point-security-gateway-cve-2024-24919-lfi-exploitation
Incident Response (IR) case study documenting the investigation of an exploitation attempt targeting CVE-2024-24919 (Arbitrary File Read) on a Check…
 0x0allenace/windows-malware-behavioral-analysis
Behavioral Malware Analysis of a Simulated Multi-Stage Windows Malware Sample using FLARE-VM and REMnux. Evidence-driven DFIR investigation with IOC…
 nicholasc03/dns-poisoning-triage-lab
Forensic triage of DNS cache poisoning in legacy hardware. Includes PCAP analysis of 839-byte unsolicited record injections, CVE-2025-40778 mapping,…
 corelight/corelightforsplunk
Splunk app for integrating and analyzing Corelight network detection data, enabling real-time threat hunting and incident response.
 aelshimony-cloud/openwire-cve-2023-46604-investigation
Incident response walkthrough analyzing CVE-2023-46604 exploitation of Apache ActiveMQ via OpenWire, including PCAP analysis, IOC identification, and…
 trinadh-dasari-cyber/eternalblue-ms17-010-research
Controlled reproduction of CVE-2017-0144 (EternalBlue) in an isolated AWS EC2 lab — exploit analysis, Wireshark traffic capture, and MITRE ATT&CK…
 magentabear/cve-2019-11043-vulnerability
Hands-on lab reproducing CVE-2019-11043 PHP-FPM RCE behind nginx, demonstrating reverse-tunnel persistence, memory forensics, and network traffic…
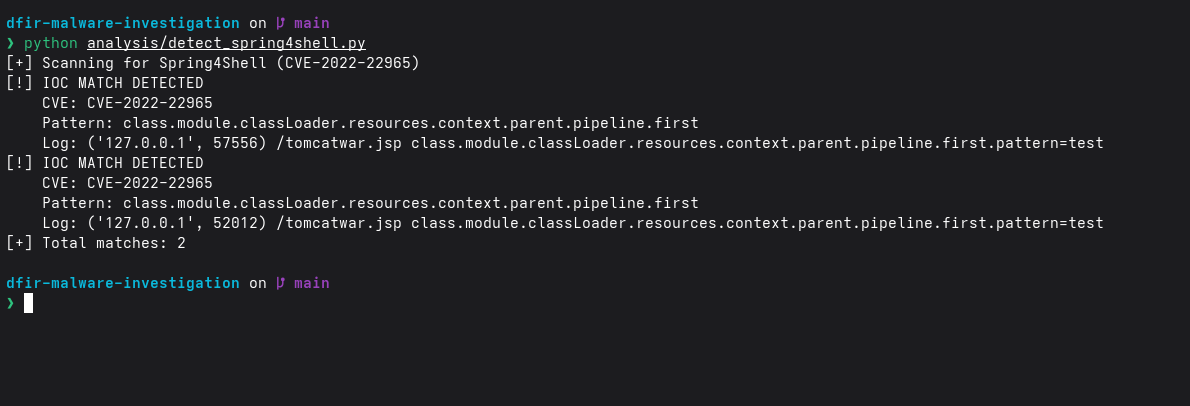 suyash-r-k/dfir-malware-investigation
Spring4Shell (CVE-2022-22965) DFIR lab with exploit simulation, Python WAF, IOC-based detection, and PCAP analysis.
 microlaser/dns_watchdog_windows2
PowerShell script that monitors Windows DNS traffic via pktmon to detect poisoning, spoofing, rogue resolver responses, and gateway MAC changes,…
 security-onion-solutions/security-onion
Security Onion 16.04 - Linux distro for threat hunting, enterprise security monitoring, and log management
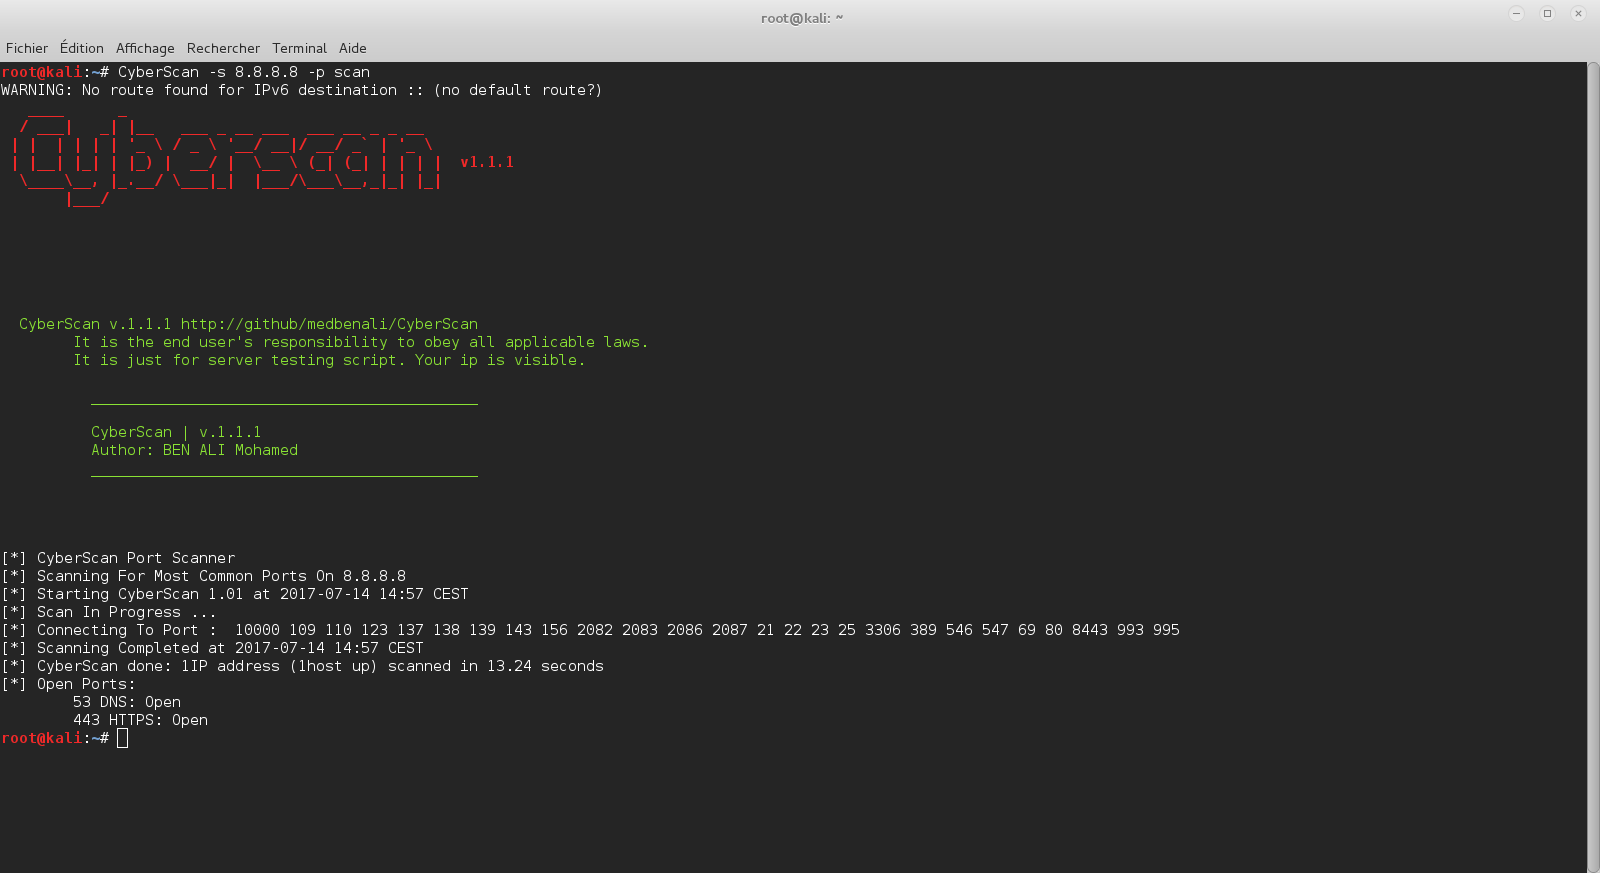 medbenali/cyberscan
Open-source network forensics toolkit for packet analysis, port scanning, host discovery, and IP geolocation. Supports ARP, ICMP, TCP, UDP pings and…