

passivedns
 gamelinux/passivedns
A network sniffer that logs all DNS server replies for use in a passive DNS setup
dns-analysisforensicsincident-response+3
1.7k3 days ago
gamelinux/passivednsA network sniffer that logs all DNS server replies for use in a passive DNS setup
 foxio-llc/ja4
JA4+ is a suite of network fingerprinting standards
 jstrosch/malware-samples
Malware samples, analysis exercises and other interesting resources.
 cisco/joy
A package for capturing and analyzing network flow data and intraflow data, for network research, forensics, and security monitoring.
 omriher/captipper
Malicious HTTP traffic explorer
 azr43lkn1ght/dfir-labs
Hands-on DFIR challenges covering digital forensics, incident response, malware analysis, and threat hunting with CTF-style flags and real-world…
 orlikoski/skadi
Collect, Process, and Hunt with host based data from MacOS, Windows, and Linux
 benjeems/packetstrider
A network packet forensics tool for SSH
 vignesh07/babyshark
Flows-first PCAP TUI (case files, gorgeous UX). Do do do do.
 mspicer/pcapinator
A tool for processing a lot of pcaps using tshark
 z4l4mi/ipgeo
Extracts IP addresses from pcap/pcapng network traffic files and generates CSV reports with geolocation, ISP, and organizational details for each IP.
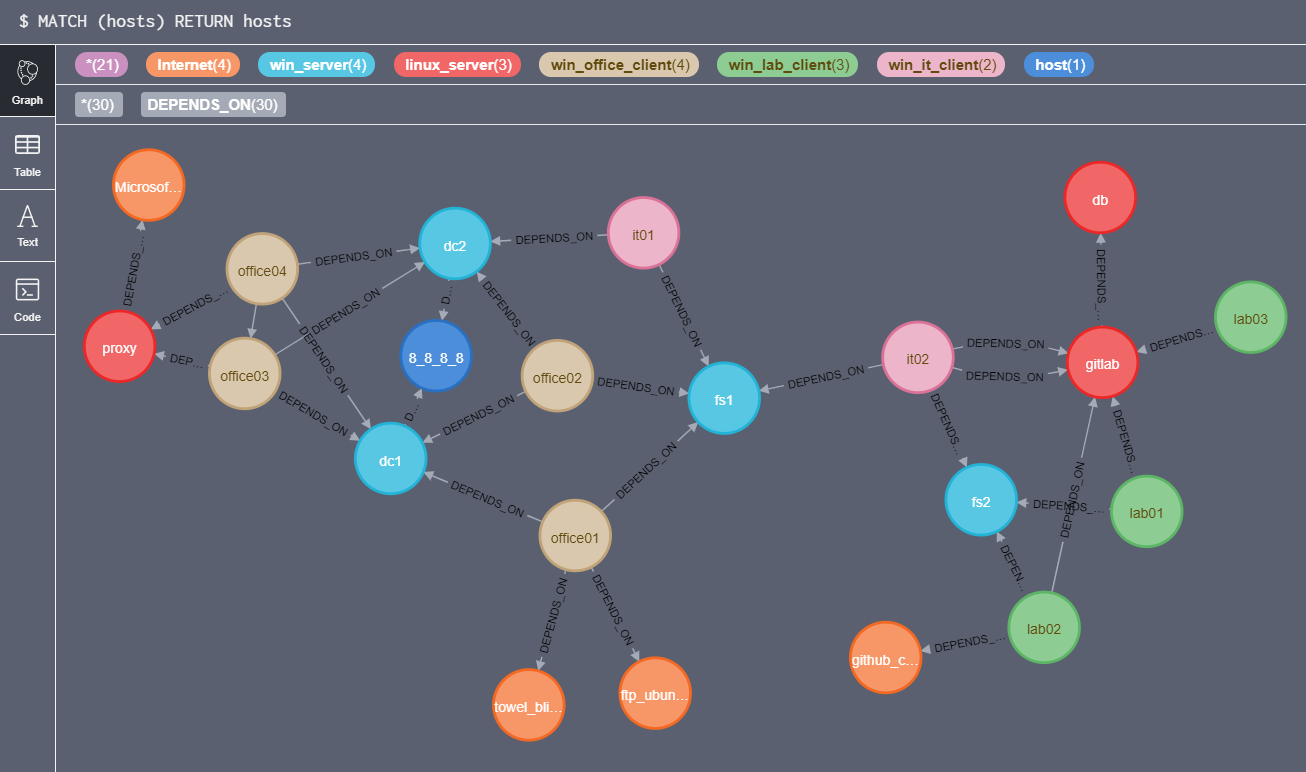 trinitor/netstat2neo4j
create cypher create statements for neo4j out of netstat files from multiple machines
 kdbugk/game-of-kingshot-re
Educational reverse engineering study of a Unity/IL2CPP Android game. Documents gateway protocol decoding, native anti-tampering SDK analysis, SSL…
 cyberhatcoil/acf
Android Connections Forensics
 ahmed-tarek22752/security-vulnerability-in-microsoft-office.
Blue-team analysis of a malicious DOCX exploiting CVE-2017-0199, covering sandbox detonation, network forensics, IOC extraction, MITRE ATT&CK…
 google/grr
Remote live forensics and incident response framework with Python agent for collecting forensic data from endpoints, including memory, disk, and…
