Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
49 results
Network-Analysis-Tools preview

Network-Analysis-Tools

GitHubazizaltuntas/network-analysis-tools

Pcap (capture file) Analysis Toolkit(v.1)
forensicsinformation-gatheringnetwork-forensics+2
110
9 years ago
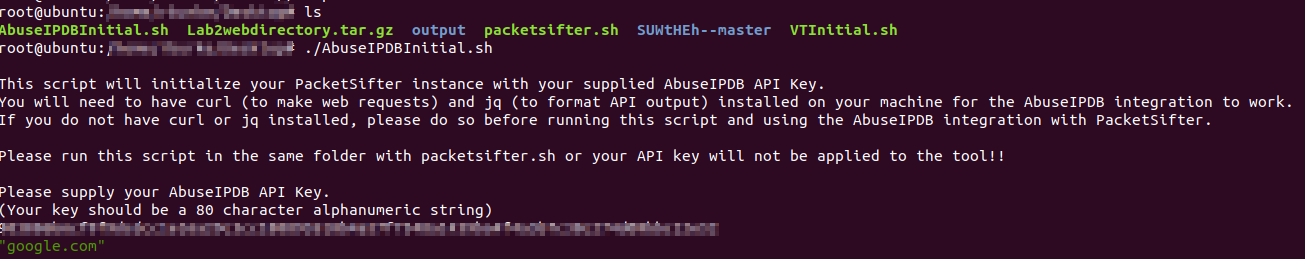
packetsifterTool preview

packetsifterTool

GitHubpacketsifter/packetsiftertool

PacketSifter is a tool/script that is designed to aid analysts in sifting through a packet capture (pcap) to find noteworthy traffic. Packetsifter…

defensive-toolsdigital-forensicsforensics+5
935 years ago
NetworkAssessment preview

NetworkAssessment

GitHubhalildeniz/networkassessment

NetworkAssessment: Network Compromise Assessment Tool
dns-analysisforensicsintrusion-detection+4
952 years ago
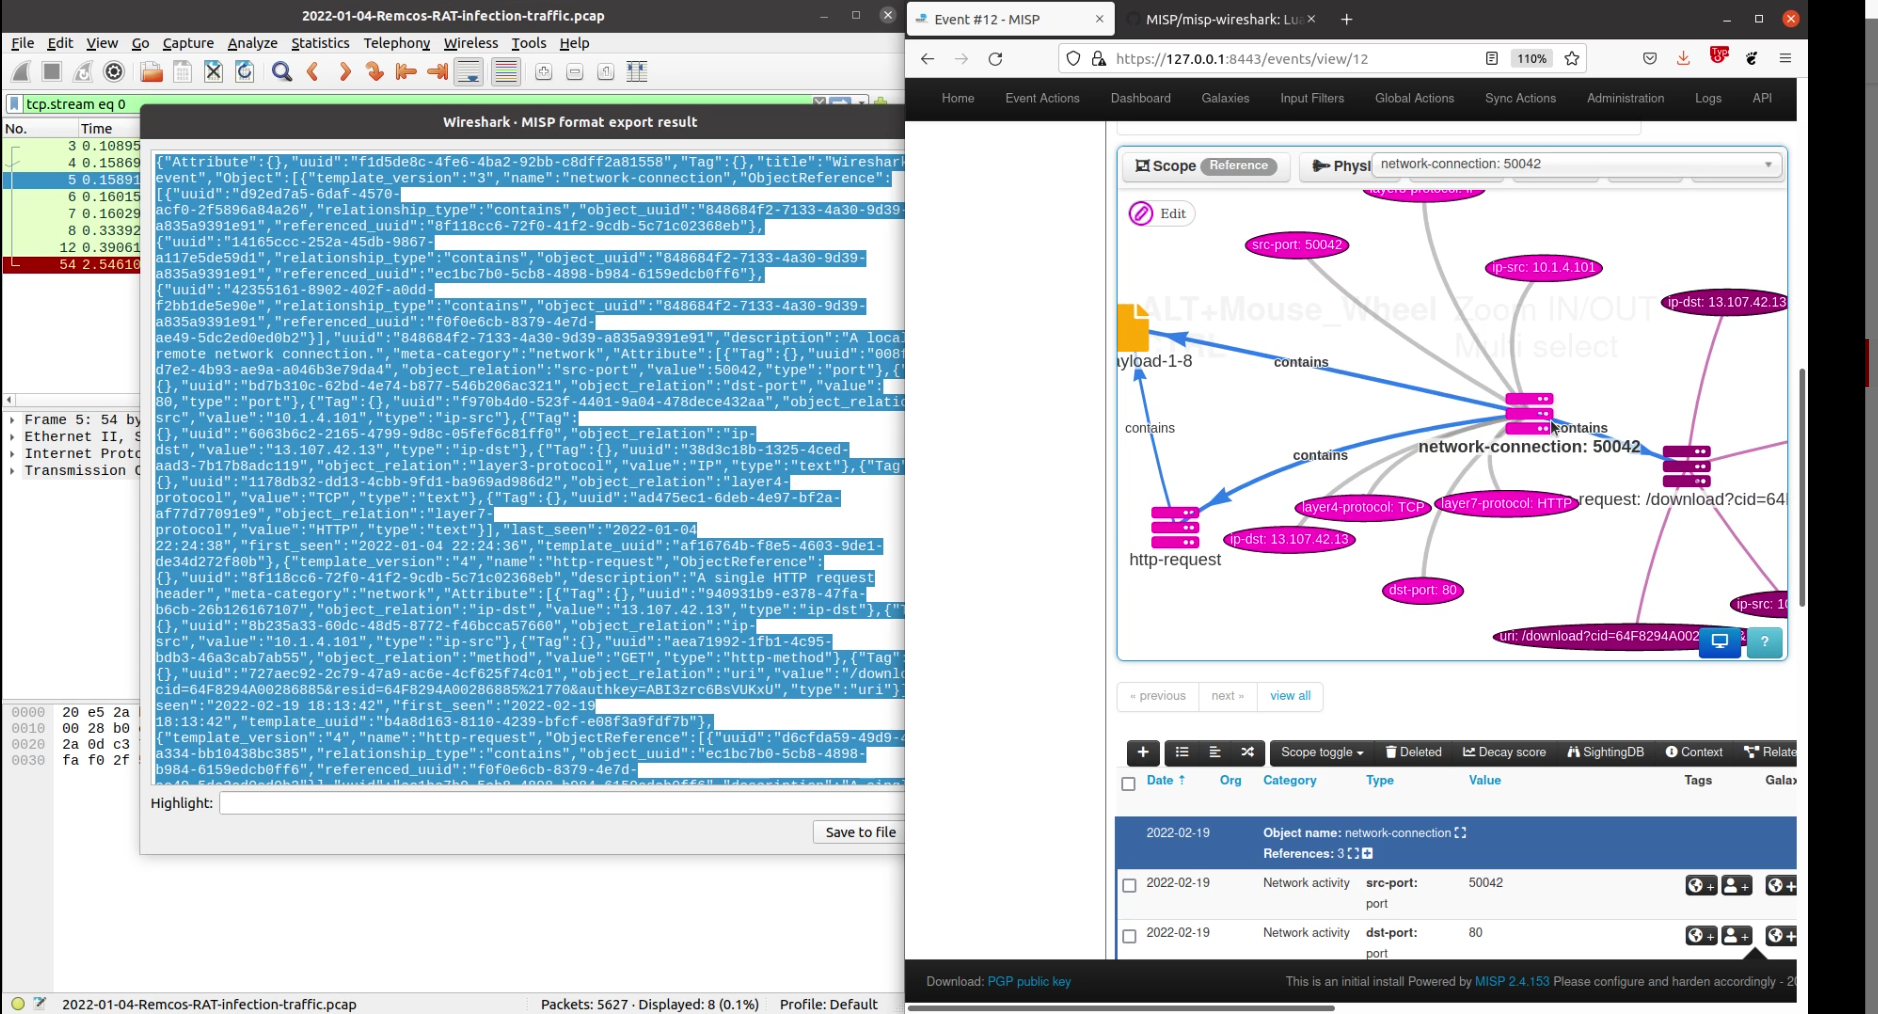
misp-wireshark preview

misp-wireshark

GitHubmisp/misp-wireshark

Lua plugin to extract data from Wireshark and convert it into MISP format

digital-forensicsforensicsnetwork-forensics+2
502 years ago
plugxdecoder preview

plugxdecoder

GitHubkcreyts/plugxdecoder

Decodes PlugX traffic and encrypted/compressed artifacts
digital-forensicsencryption-decryption-toolsforensics+3
3813 years ago
ipdecap preview

ipdecap

GitHublpefferkorn/ipdecap

Decapsulate traffic encapsulated within GRE, IPIP, 6in4, ESP (ipsec) protocols, can also remove IEEE 802.1Q (virtual lan) header. Works with pcap…
encryption-decryption-toolsforensicsnetwork-forensics+3
357 years ago
shadow-fleet-tracker-light preview

shadow-fleet-tracker-light

GitHubformerlab/shadow-fleet-tracker-light

Open source Baltic Sea shadow fleet tracker. 1200+ vessels, live AIS, cable proximity alerts. No cloud, no subscription, runs locally
data-exfiltrationdigital-forensicsdns-analysis+9
434 months ago
BlueFish preview

BlueFish

GitHubemrekybs/bluefish

Automation tool designed to simplify the analysis of PCAP (Packet Capture) files
forensicsincident-responseinformation-gathering+2
205 months ago
Baskerville preview

Baskerville

GitHubnccgroup/baskerville

Selective protocol extractor from PCAPs or interfaces
incident-responsenetwork-forensicsnetwork-security+1
511 years ago
Cyber-Defenders-lab- preview

Cyber-Defenders-lab-

GitHubabiral-timalsina/cyber-defenders-lab-

My write-ups from CyberDefenders' Blue Team labs, solved using Wireshark. Covers TeamCity RCE (CVE-2024-27198), XSS session hijacking, and…
digital-forensicseducationincident-response+3
1 month ago
Wireshark preview

Wireshark

GitHubkirkdjohnson/wireshark

Downloaded a packet capture (.pcapng) file from malware-traffic-analysis.net which was an example of an attempted attack against a webserver using…
command-and-controldigital-forensicseducation+9
32 years ago
XLS-to-DBatLoader-or-GuLoader-for-AgentTesla-variant preview

XLS-to-DBatLoader-or-GuLoader-for-AgentTesla-variant

GitHubblackoclock/xls-to-dbatloader-or-guloader-for-agenttesla-variant

CVE-2017-0199 XLS --> HTA --> VBS --> STEGANOGRAPHY --> DBATLOADER/GULOADER STYLE MALWARE
command-and-controldigital-forensicsexploitation+4
6 months ago
dfir-malware-investigation preview

dfir-malware-investigation

GitHubsuyash-r-k/dfir-malware-investigation

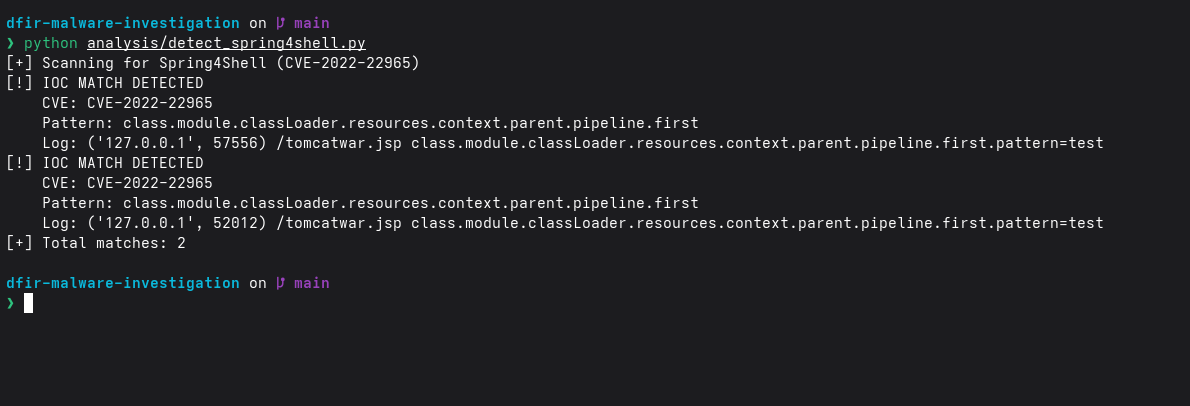
Spring4Shell (CVE-2022-22965) DFIR lab with exploit simulation, Python WAF, IOC-based detection, and PCAP analysis.

digital-forensicseducationincident-response+9
7 months ago
Previous123Next