
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
36 results
pcapfex preview

pcapfex

GitHubvikwin/pcapfex

'Packet Capture Forensic Evidence eXtractor' is a tool that finds and extracts files from packet capture files
data-recoverydigital-forensicsforensics+2
2306 years ago
wireshark-forensics-plugin preview

wireshark-forensics-plugin

GitHubrjbhide/wireshark-forensics-plugin

Wireshark plugin that correlates network traffic with threat intelligence, asset tags, and vulnerability data to accelerate forensic analysis of PCAP…

digital-forensicsforensicsnetwork-forensics+3
1024 years ago
pcap-burp preview

pcap-burp

GitHubnccgroup/pcap-burp

Pcap importer for Burp

network-forensicspacket-sniffing-analysispenetration-testing+2
1145 years ago
OpenFPC preview

OpenFPC

GitHubleonward/openfpc

OpenFPC, Open Source Full Packet Capture

forensicsnetwork-forensicsnetwork-security+1
7310 years ago
NetworkAssessment preview

NetworkAssessment

GitHubhalildeniz/networkassessment

NetworkAssessment: Network Compromise Assessment Tool
dns-analysisforensicsintrusion-detection+4
952 years ago
misp-wireshark preview

misp-wireshark

GitHubmisp/misp-wireshark

Lua plugin to extract data from Wireshark and convert it into MISP format

digital-forensicsforensicsnetwork-forensics+2
502 years ago
zeek-community-id preview

zeek-community-id

GitHubcorelight/zeek-community-id

Zeek support for Community ID flow hashing.
log-analysisnetwork-forensicsnetwork-security+1
373 years ago
drovorub-hunt preview

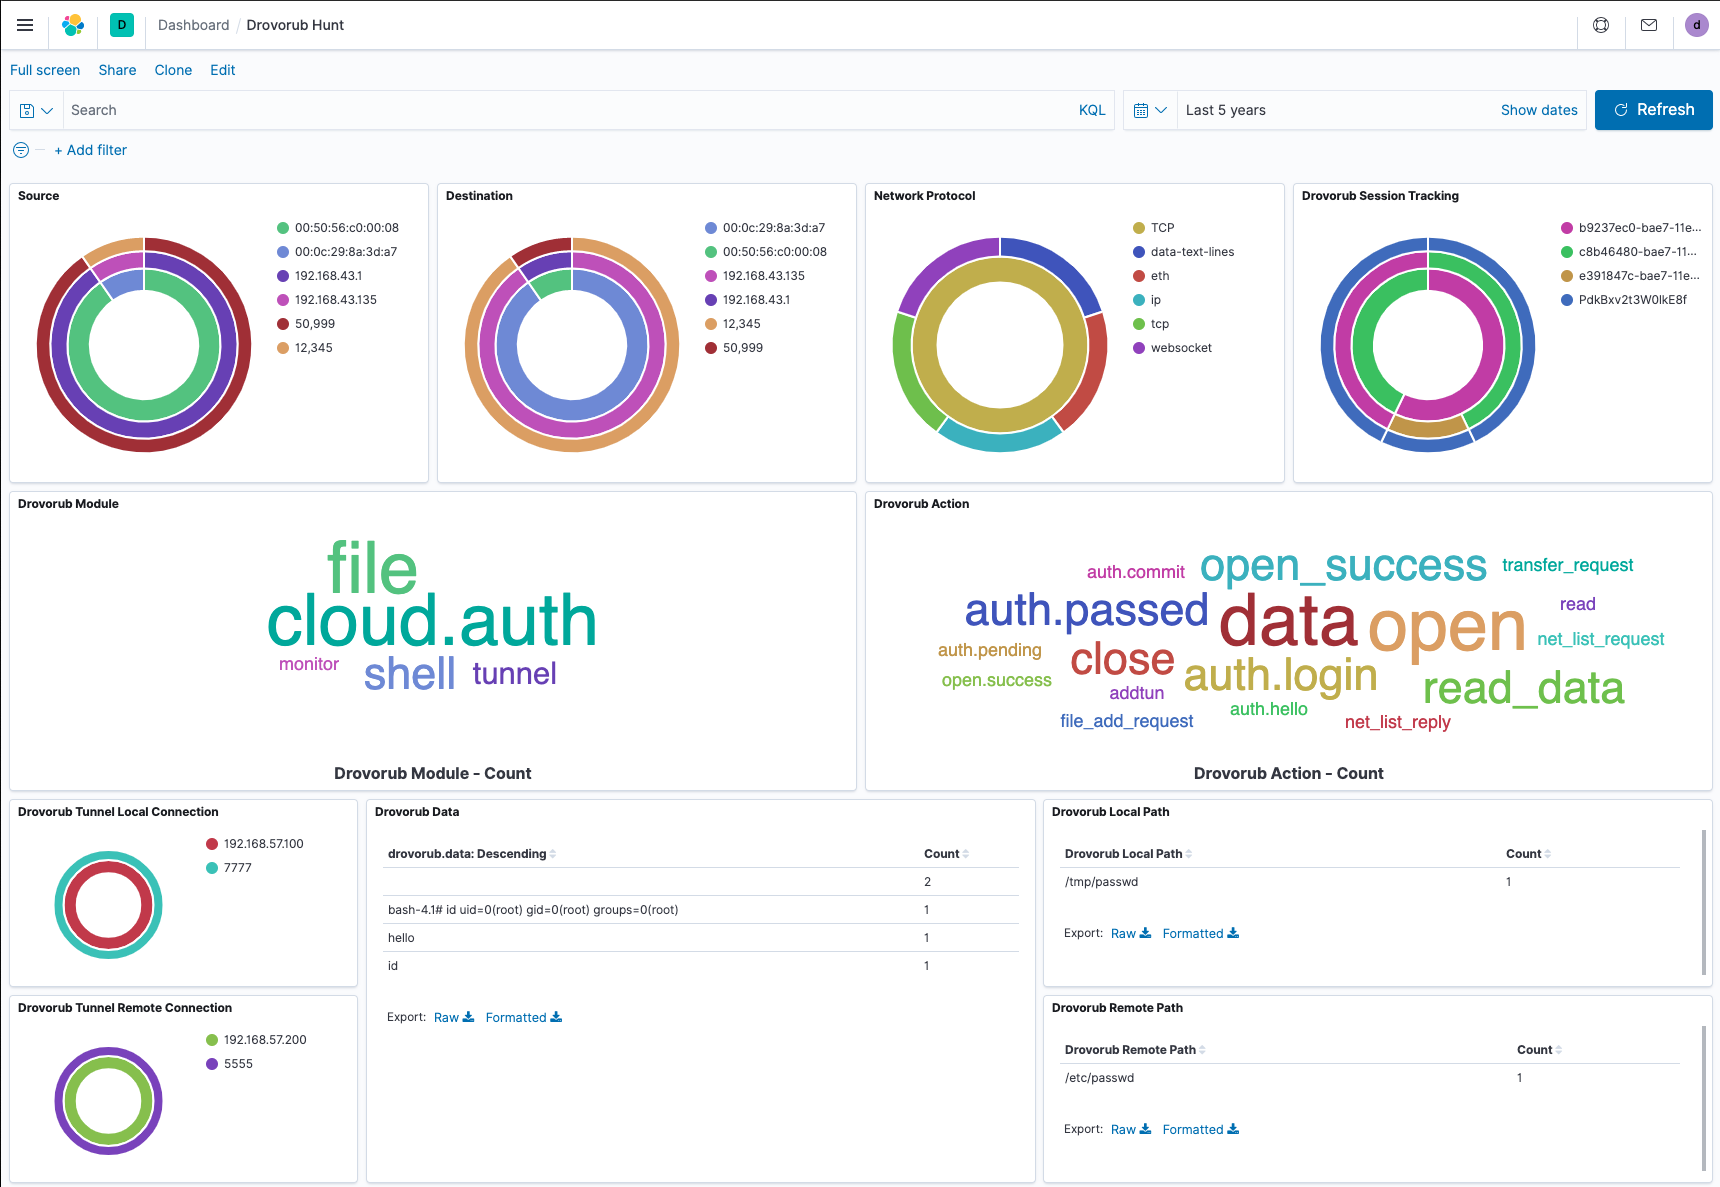
drovorub-hunt

GitHubinsane-forensics/drovorub-hunt

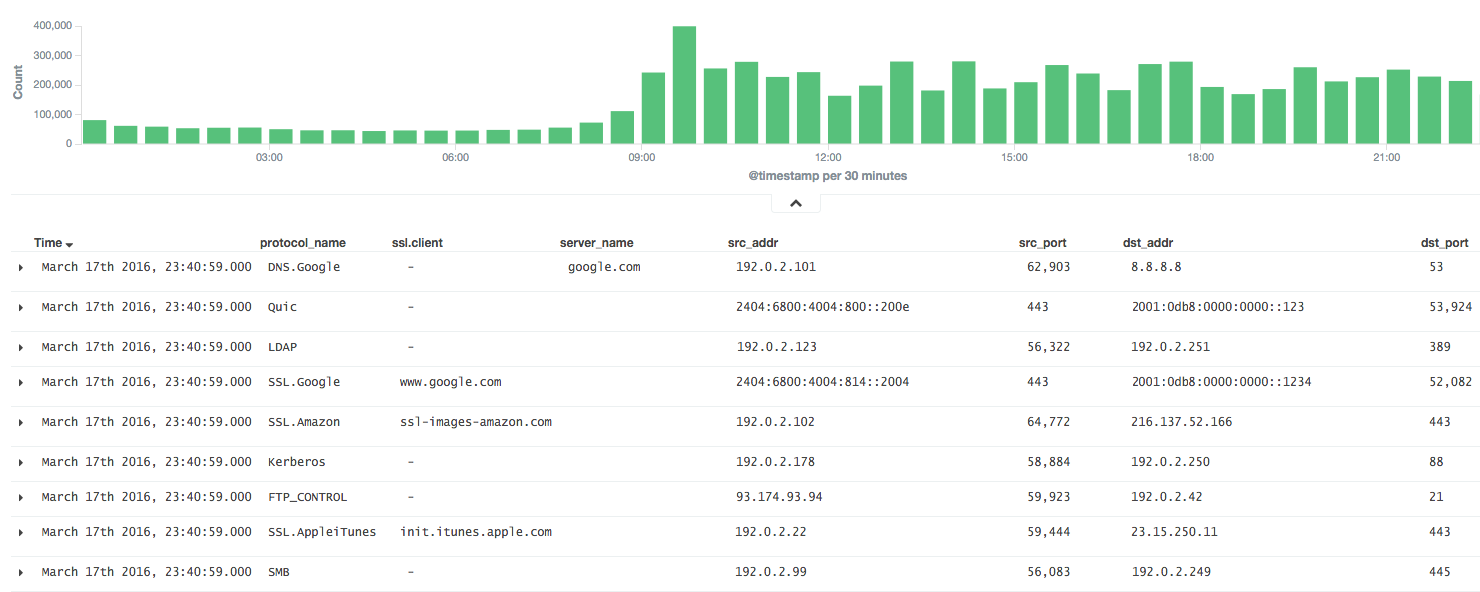
A tool to assist with network-based hunting for GRU's Drovorub malware c2
incident-responseintrusion-detectionmalware-analysis+3
256 years ago
ndff preview

ndff

GitHubknqyf263/ndff

A flow-based network monitor with Deep Packet Inspection

dns-analysislog-analysisnetwork-forensics+2
289 years ago
zeek-spicy-ipsec preview

zeek-spicy-ipsec

GitHubcorelight/zeek-spicy-ipsec

A Zeek IPSec protocol analyzer based on Spicy.
intrusion-detectionnetwork-forensicsnetwork-security+1
81 year ago
zeek-spicy-wireguard preview

zeek-spicy-wireguard

GitHubcorelight/zeek-spicy-wireguard

A Zeek Wireguard protocol analyzer based on Spicy.
network-forensicsnetwork-securitypacket-sniffing-analysis
77 months ago
zeek-quic preview

zeek-quic

GitHubcorelight/zeek-quic

Bro analyzer that detects Google's QUIC protocol

intrusion-detectionlog-analysisnetwork-forensics+2
115 years ago
zeek-spicy-ospf preview

zeek-spicy-ospf

GitHubcorelight/zeek-spicy-ospf

A Zeek OSPF packet analyzer based on Spicy.

anomaly-detectionnetwork-forensicsnetwork-mapping+2
81 year ago
An-Integrated-Wireless-Network-Forensic-Analysis-Framework preview

An-Integrated-Wireless-Network-Forensic-Analysis-Framework

GitHubbenadia/an-integrated-wireless-network-forensic-analysis-framework

This framework combines a set of existing open source tools into an integrated package that automates the forensics investigation process. It is able…
digital-forensicsforensicsnetwork-forensics+2
68 years ago
Baskerville preview

Baskerville

GitHubnccgroup/baskerville

Selective protocol extractor from PCAPs or interfaces

incident-responsenetwork-forensicsnetwork-security+1
511 years ago
CorelightForSplunk preview

CorelightForSplunk

GitHubcorelight/corelightforsplunk

Splunk app for integrating and analyzing Corelight network detection data, enabling real-time threat hunting and incident response.

anomaly-detectionincident-responselog-analysis+4
21 year ago
Network-Filesystem-Forensics preview

Network-Filesystem-Forensics

GitHubgilberto47831/network-filesystem-forensics

Reports on post-exploitation on honeypot exploiting vulnerable wu-ftpd (CVE-2001-0550)
digital-forensicsforensicsnetwork-forensics+2
4 years ago
stenographer preview
Archived

stenographer

GitHubgoogle/stenographer

Stenographer is a packet capture solution which aims to quickly spool all packets to disk, then provide simple, fast access to subsets of those…

forensicsincident-responseintrusion-detection+3
1.8k5 years ago
Previous12Next