
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
127 results
fatt preview

fatt

GitHub0x4d31/fatt

FATT /fingerprintAllTheThings - a pyshark based script for extracting network metadata and fingerprints from pcap files and live network traffic

network-forensicspacket-sniffing-analysisthreat-intelligence
6854 years ago
Incident-Response-Powershell preview

Incident-Response-Powershell

GitHubbert-janp/incident-response-powershell

PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…
digital-forensicsdisk-forensicsforensics+6
8113 months ago
irflow-timeline preview

irflow-timeline

GitHubr3nzsec/irflow-timeline

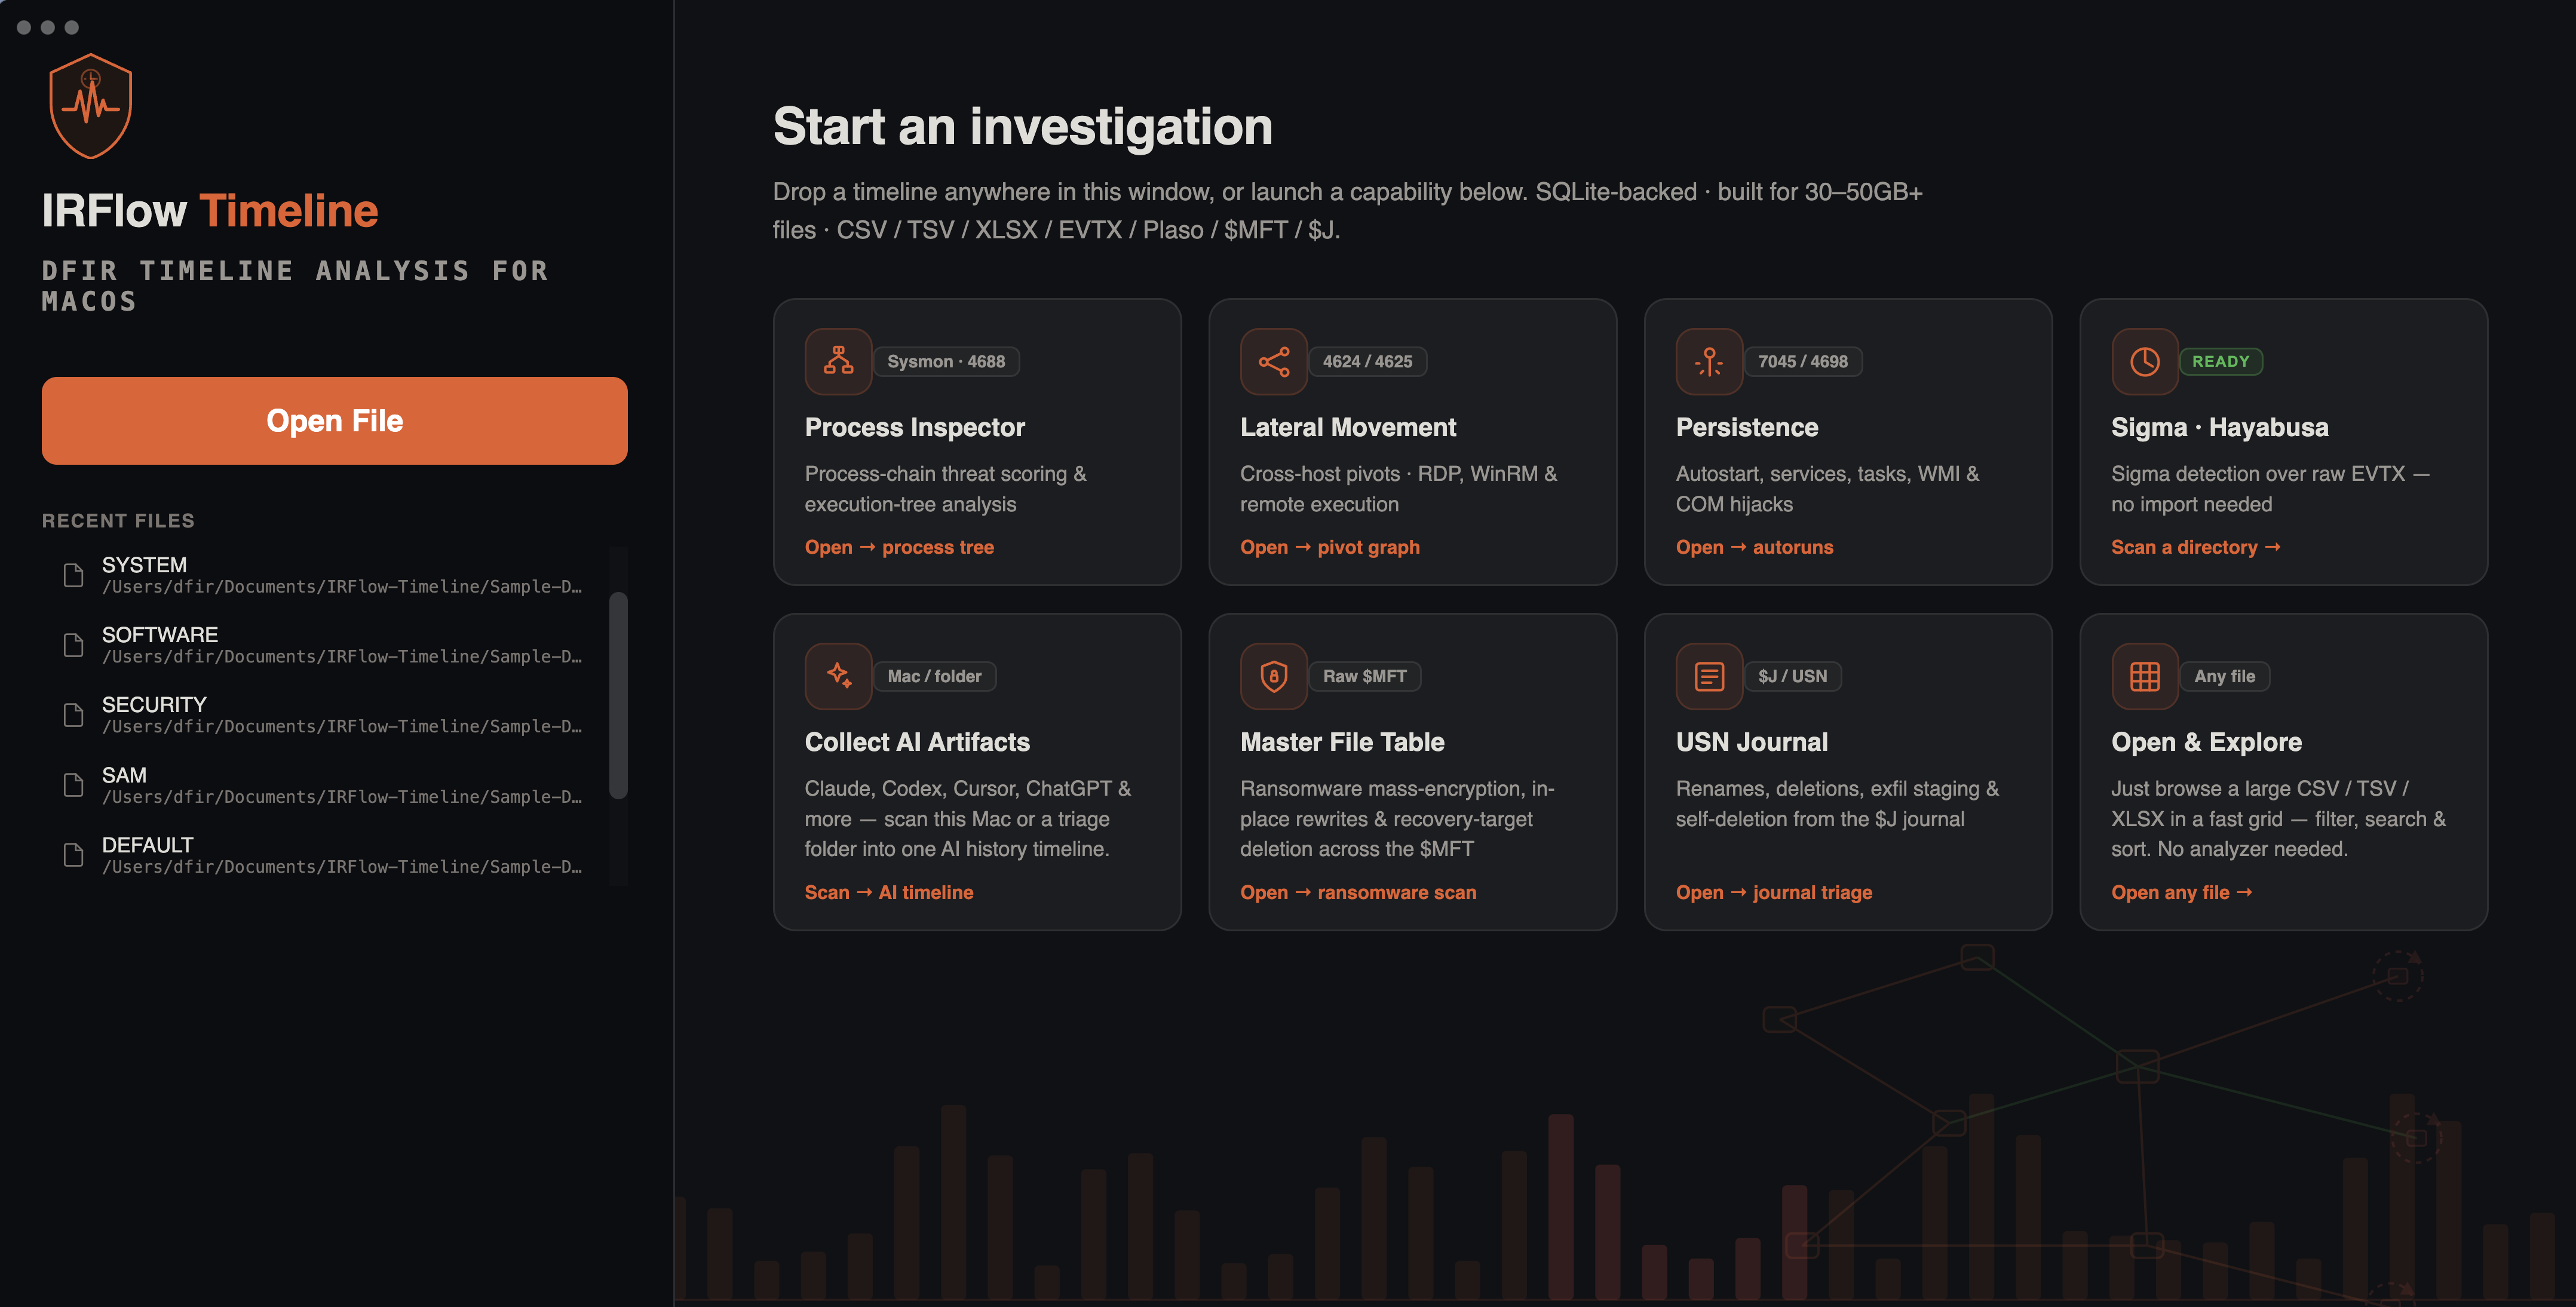
DFIR Timeline Analysis for macOS — SQLite-backed viewer for CSV, TSV, XLSX, EVTX, Plaso, $MFT, and $J files with AI Artifacts, AI Secret Hunt,…
digital-forensicsdisk-forensicsforensics+7
3679 days ago
CyberScan preview

CyberScan

GitHubmedbenali/cyberscan

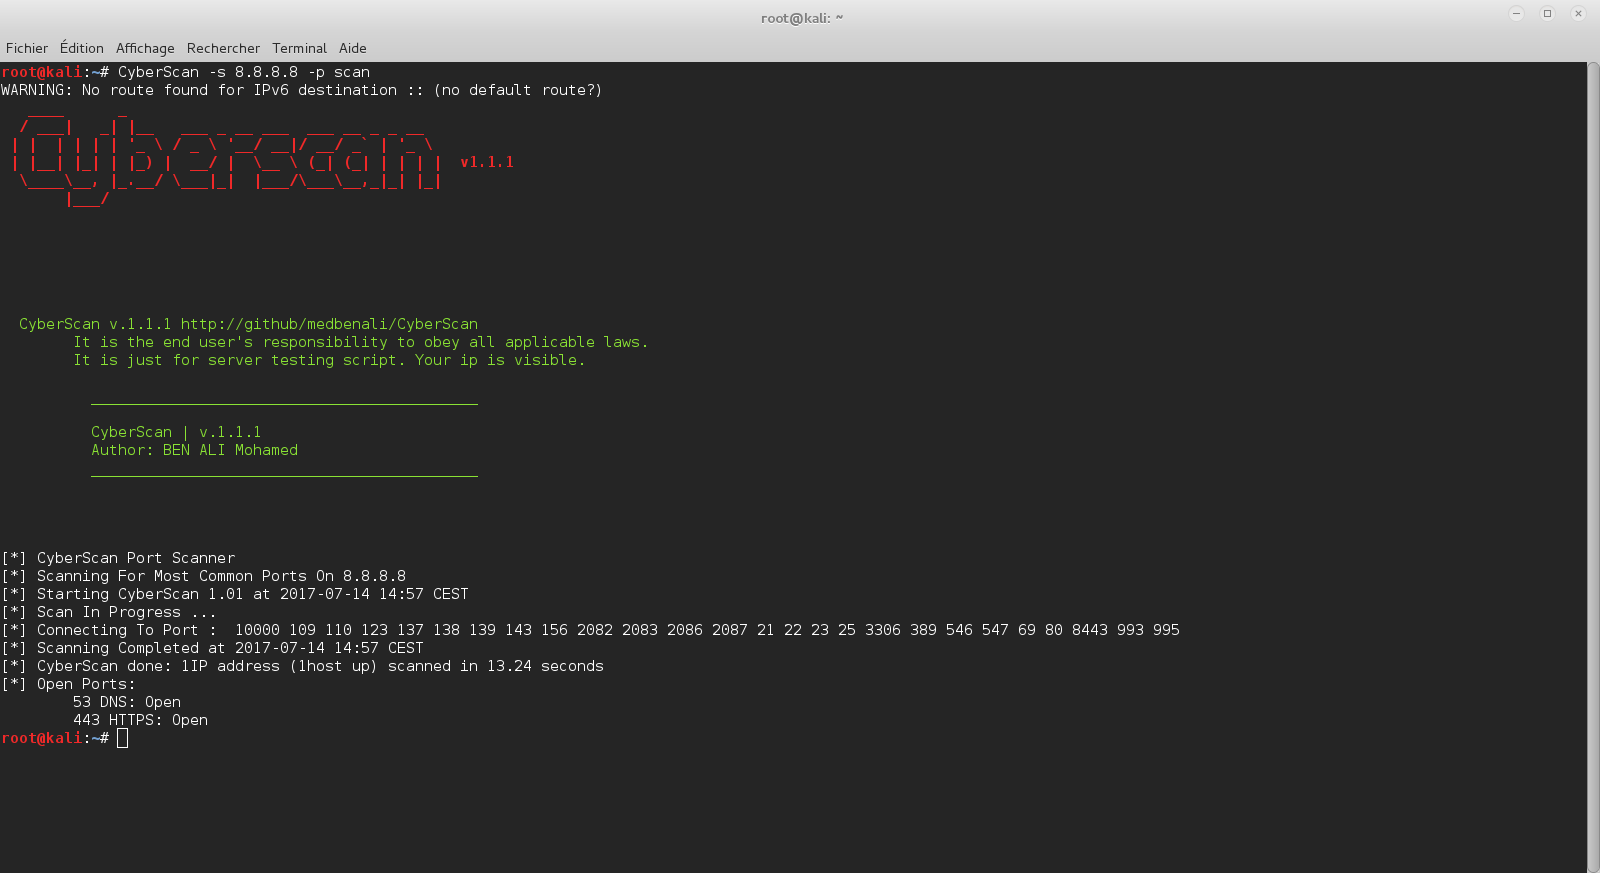
Open-source network forensics toolkit for packet analysis, port scanning, host discovery, and IP geolocation. Supports ARP, ICMP, TCP, UDP pings and…
information-gatheringnetwork-forensicsnetwork-mapping+3
4694 months ago
awesome-dfir-skills preview

awesome-dfir-skills

GitHubtsale/awesome-dfir-skills

A curated collection of DFIR skills and workflows for InfoSec practitioners.
curated-resourcesdigital-forensicseducation+7
3224 months ago
dissect.cobaltstrike preview

dissect.cobaltstrike

GitHubfox-it/dissect.cobaltstrike

Python library for dissecting and parsing Cobalt Strike related data such as Beacon payloads and Malleable C2 Profiles

binary-analysiscommand-and-controldigital-forensics+4
1962 months ago
IpGeo preview

IpGeo

GitHubz4l4mi/ipgeo

Extracts IP addresses from pcap/pcapng network traffic files and generates CSV reports with geolocation, ISP, and organizational details for each IP.
information-gatheringnetwork-forensicsosint+1
1323 years ago
DFIR4vSphere preview

DFIR4vSphere

GitHubanssi-fr/dfir4vsphere

Powershell module for VMWare vSphere forensics
cloud-infrastructure-securityconfiguration-auditingdefensive-tools+5
1881 year ago
pcapinator preview

pcapinator

GitHubmspicer/pcapinator

A tool for processing a lot of pcaps using tshark

forensicsinformation-gatheringnetwork-forensics+2
1552 years ago
pcap-burp preview

pcap-burp

GitHubnccgroup/pcap-burp

Pcap importer for Burp
network-forensicspacket-sniffing-analysispenetration-testing+2
1145 years ago
syd preview

syd

GitHubsydsec/syd

Offline AI Security Assistant for Air-Gapped Pentesting
ai-securityexploitationforensics+8
875 months ago
netstat2neo4j preview

netstat2neo4j

GitHubtrinitor/netstat2neo4j

create cypher create statements for neo4j out of netstat files from multiple machines
information-gatheringlog-analysisnetwork-forensics
415 years ago
HiddenNetworks-Python preview

HiddenNetworks-Python

GitHubtelefonica/hiddennetworks-python

USB device connection forensics tool that traces physical device-to-computer relationships across local and domain networks, generating visual graphs…

digital-forensicsforensicsinformation-gathering+2
386 years ago
zeek-community-id preview

zeek-community-id

GitHubcorelight/zeek-community-id

Zeek support for Community ID flow hashing.
log-analysisnetwork-forensicsnetwork-security+1
373 years ago
drovorub-hunt preview

drovorub-hunt

GitHubinsane-forensics/drovorub-hunt

A tool to assist with network-based hunting for GRU's Drovorub malware c2

incident-responseintrusion-detectionmalware-analysis+3
256 years ago
Mortimer preview

Mortimer

GitHubnccgroup/mortimer

A collection of scripts for processing network forensics type data and intelligence, mainly into a postgres database.

forensicsioc-managementlog-analysis+3
1211 years ago
An-Integrated-Wireless-Network-Forensic-Analysis-Framework preview

An-Integrated-Wireless-Network-Forensic-Analysis-Framework

GitHubbenadia/an-integrated-wireless-network-forensic-analysis-framework

This framework combines a set of existing open source tools into an integrated package that automates the forensics investigation process. It is able…
digital-forensicsforensicsnetwork-forensics+2
68 years ago
SOC-Investigation-CVE-2024-49138 preview

SOC-Investigation-CVE-2024-49138

GitHubbasitsajidapply-stack/soc-investigation-cve-2024-49138

Investigation and Incident Response report for LetsDefend Alert SOC335 (CVE-2024-49138 Exploitation)

digital-forensicseducationincident-response+3
25 days ago
Previous123…8Next