

passivedns
 gamelinux/passivedns
A network sniffer that logs all DNS server replies for use in a passive DNS setup
dns-analysisforensicsincident-response+3
1.7k3 days ago
gamelinux/passivednsA network sniffer that logs all DNS server replies for use in a passive DNS setup
 hasamba/dfir-companion
DFIR forensics companion server + capture extension
 weirdmachine64/sharkmcp
A swiss-knife MCP server for analysing PCAP files
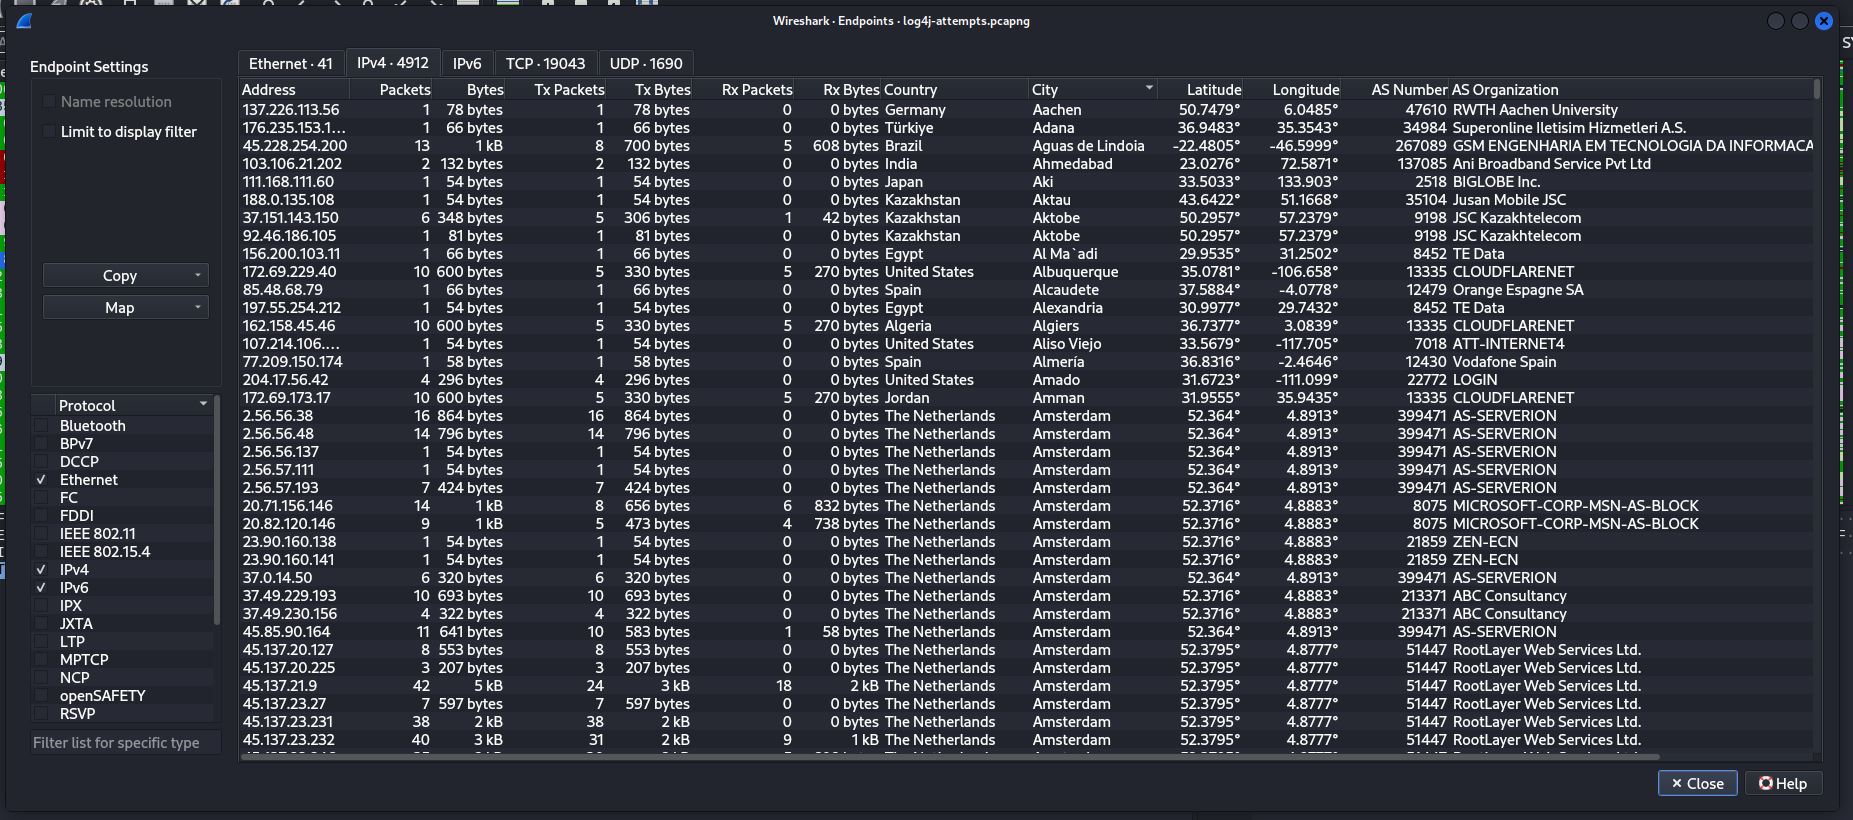 kirkdjohnson/wireshark
Downloaded a packet capture (.pcapng) file from malware-traffic-analysis.net which was an example of an attempted attack against a webserver using…