

honeypot-data
 0x4d31/honeypot-data
Public honeypot datasets and observation reports with HTTP/TLS fingerprint data (JA3/JA4), pseudonymized source IPs, and exploitation attempt…
incident-responseinformation-gatheringioc-management+4
44
0x4d31/honeypot-dataPublic honeypot datasets and observation reports with HTTP/TLS fingerprint data (JA3/JA4), pseudonymized source IPs, and exploitation attempt…
 proxymanapp/tcpviewer
The best-in-class macOS app to See every packet clearly on your Mac. Alternative to Wireshark
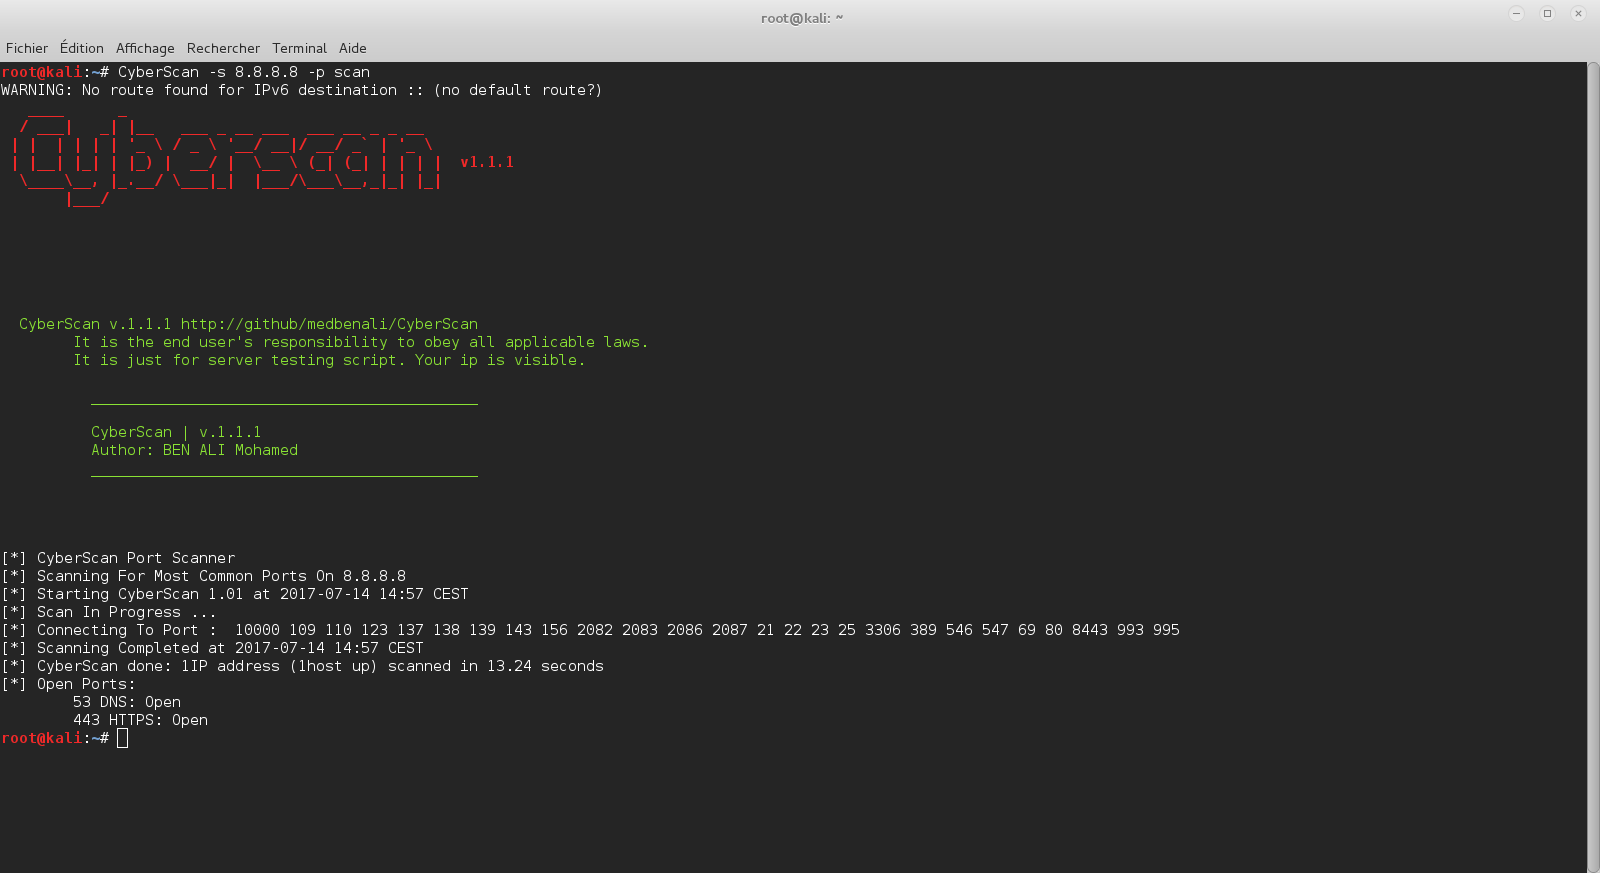 medbenali/cyberscan
Open-source network forensics toolkit for packet analysis, port scanning, host discovery, and IP geolocation. Supports ARP, ICMP, TCP, UDP pings and…
 emrekybs/bryobio
It was developed to speed up the processes of SOC Analysts during analysis
 emrekybs/bluefish
Automation tool designed to simplify the analysis of PCAP (Packet Capture) files
 corelight/zeek-spicy-stun
A Zeek STUN protocol analyzer based on Spicy.
 mspicer/pcapinator
A tool for processing a lot of pcaps using tshark
 synacktiv/pcapan
A pcap capture analysis helper
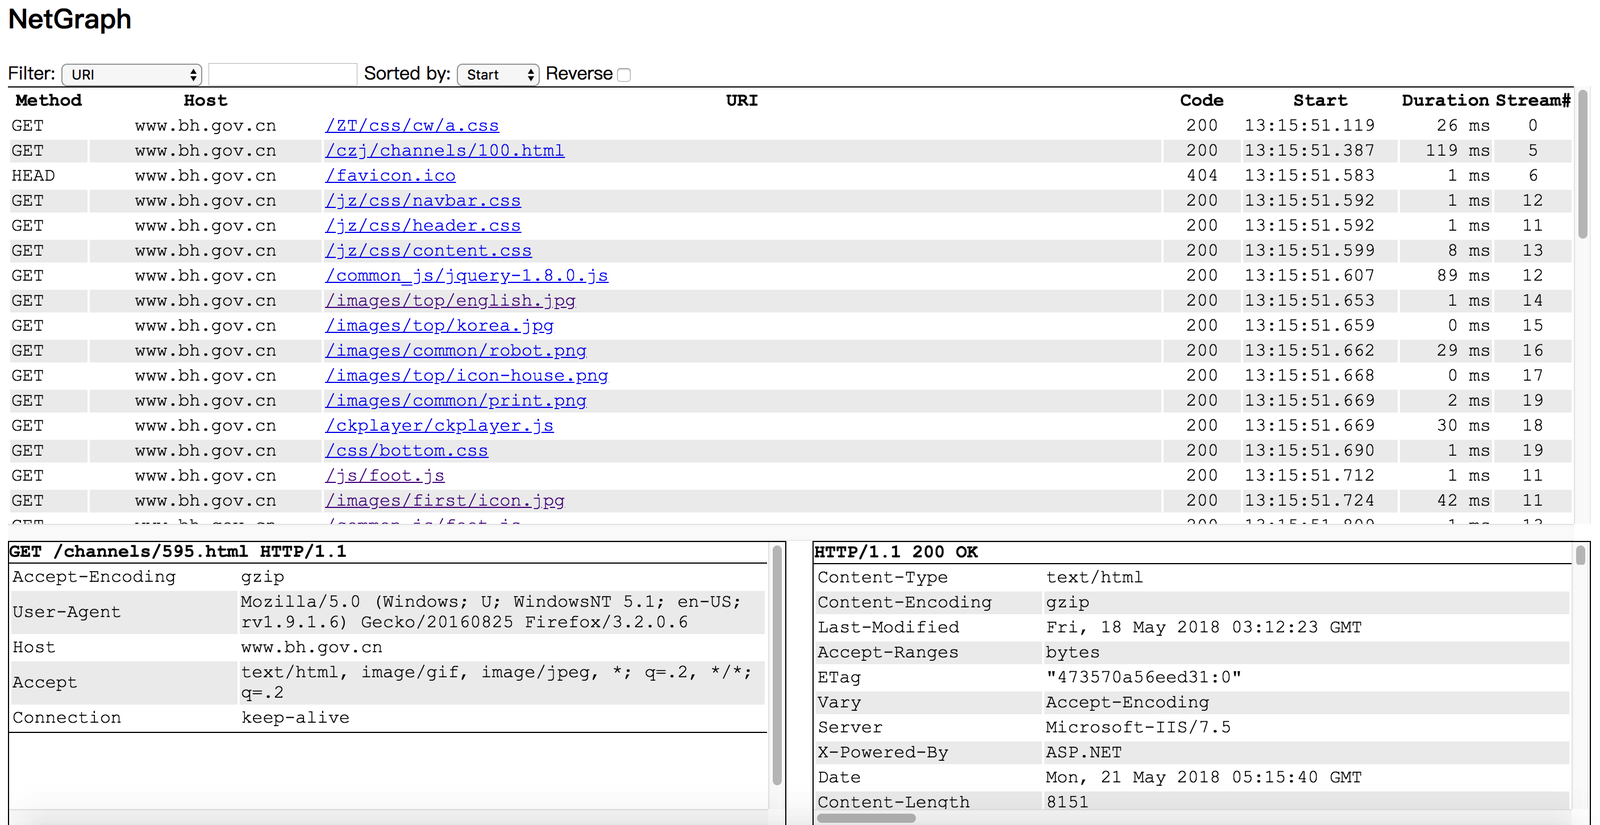 ga0/netgraph
A cross platform http sniffer with a web UI
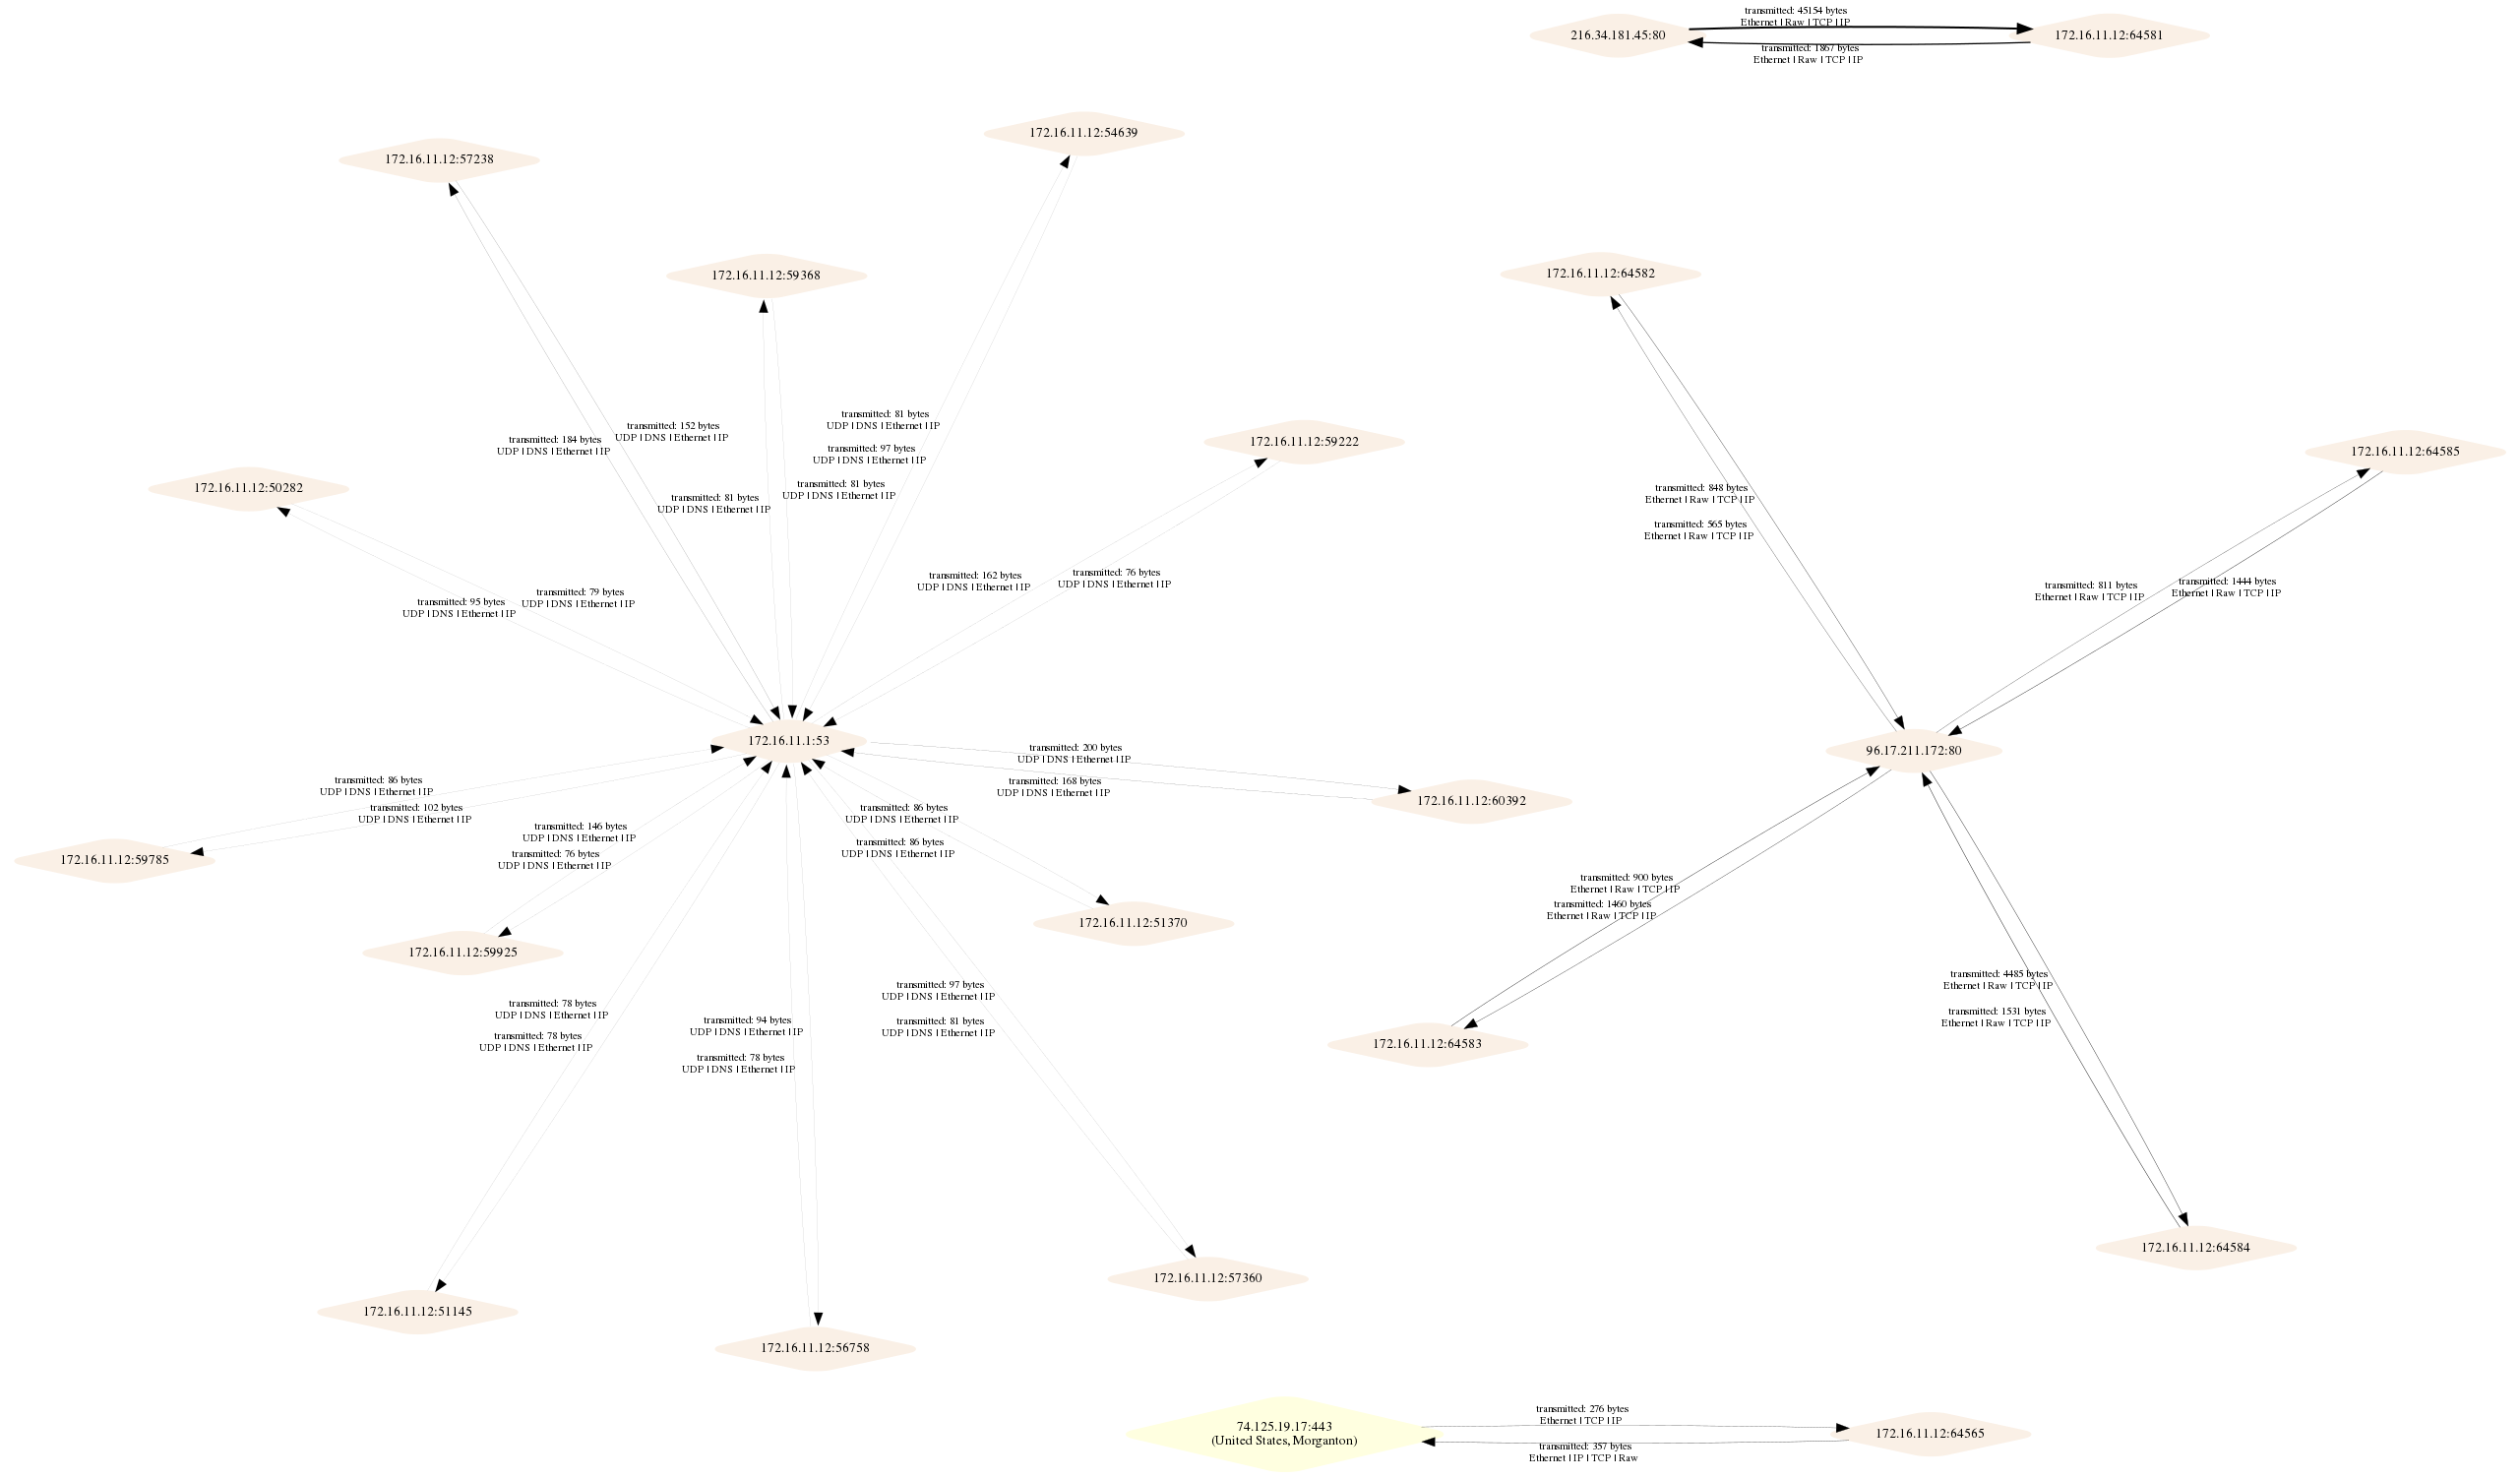 1ultimat3/pcapviz
Visualize network topologies and collect graph statistics based on pcap files
 z4l4mi/ipgeo
Extracts IP addresses from pcap/pcapng network traffic files and generates CSV reports with geolocation, ISP, and organizational details for each IP.
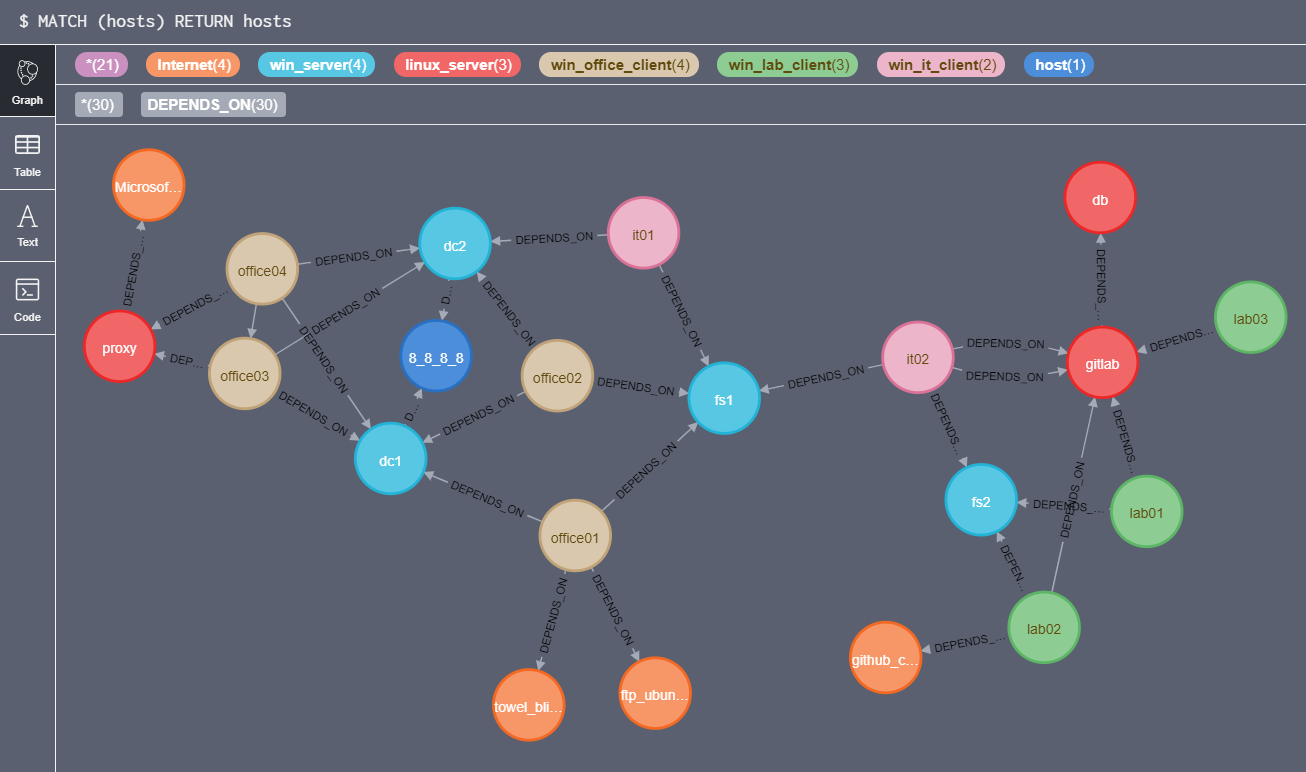 trinitor/netstat2neo4j
create cypher create statements for neo4j out of netstat files from multiple machines
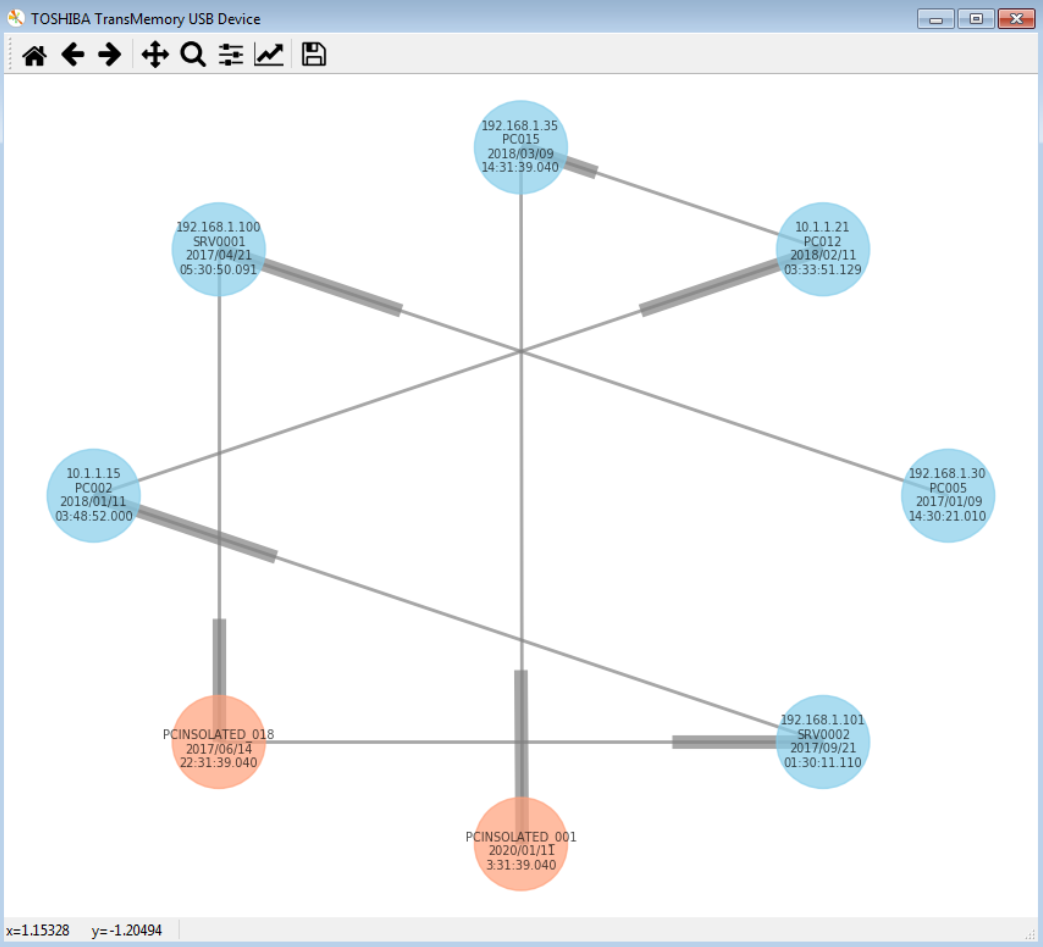 telefonica/hiddennetworks-python
USB device connection forensics tool that traces physical device-to-computer relationships across local and domain networks, generating visual graphs…
 azizaltuntas/network-analysis-tools
Pcap (capture file) Analysis Toolkit(v.1)