
Sandb0x-Xtract0r
Automated cross-platform sandbox that detonates suspicious files in isolated VMs/emulators, captures network and memory artifacts, and creates LLM…
dynamic-analysis-sandboxingmalware-analysismemory-forensics+3
3

Automated cross-platform sandbox that detonates suspicious files in isolated VMs/emulators, captures network and memory artifacts, and creates LLM…

All-in-One malware analysis tool.

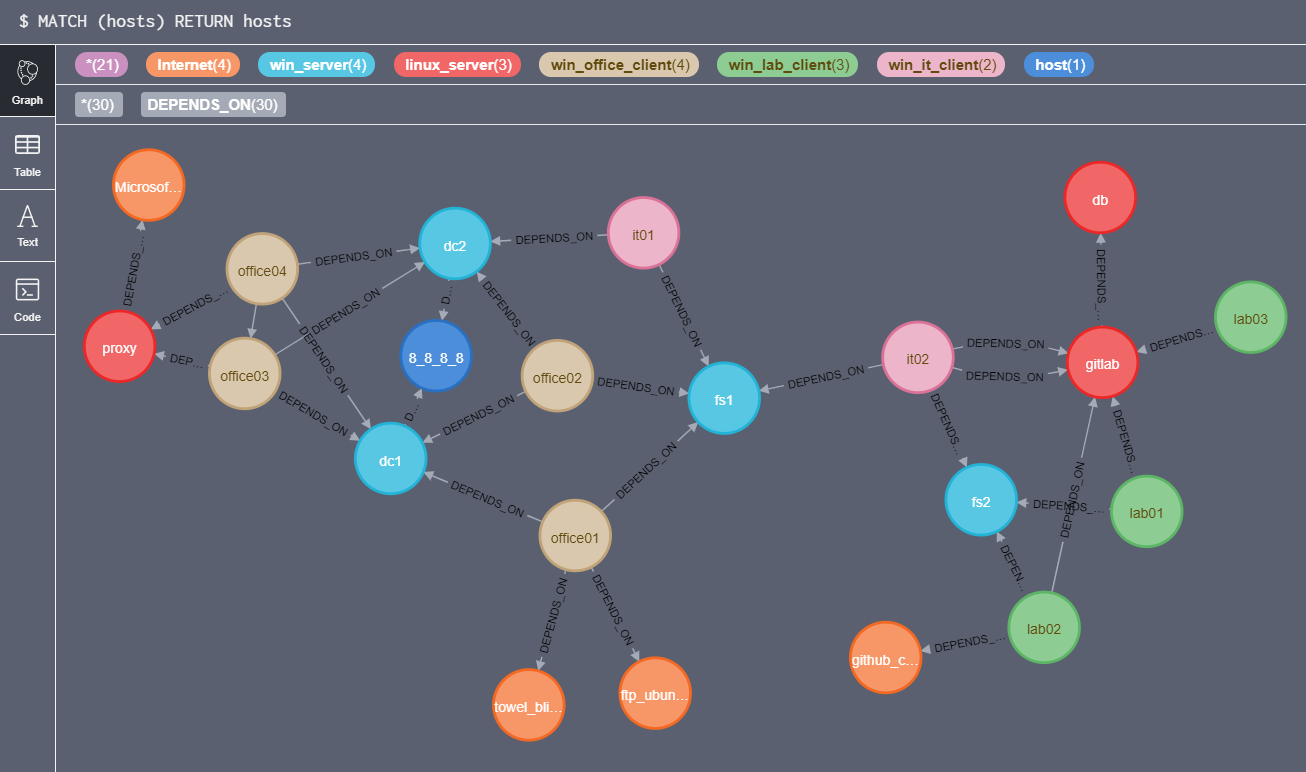
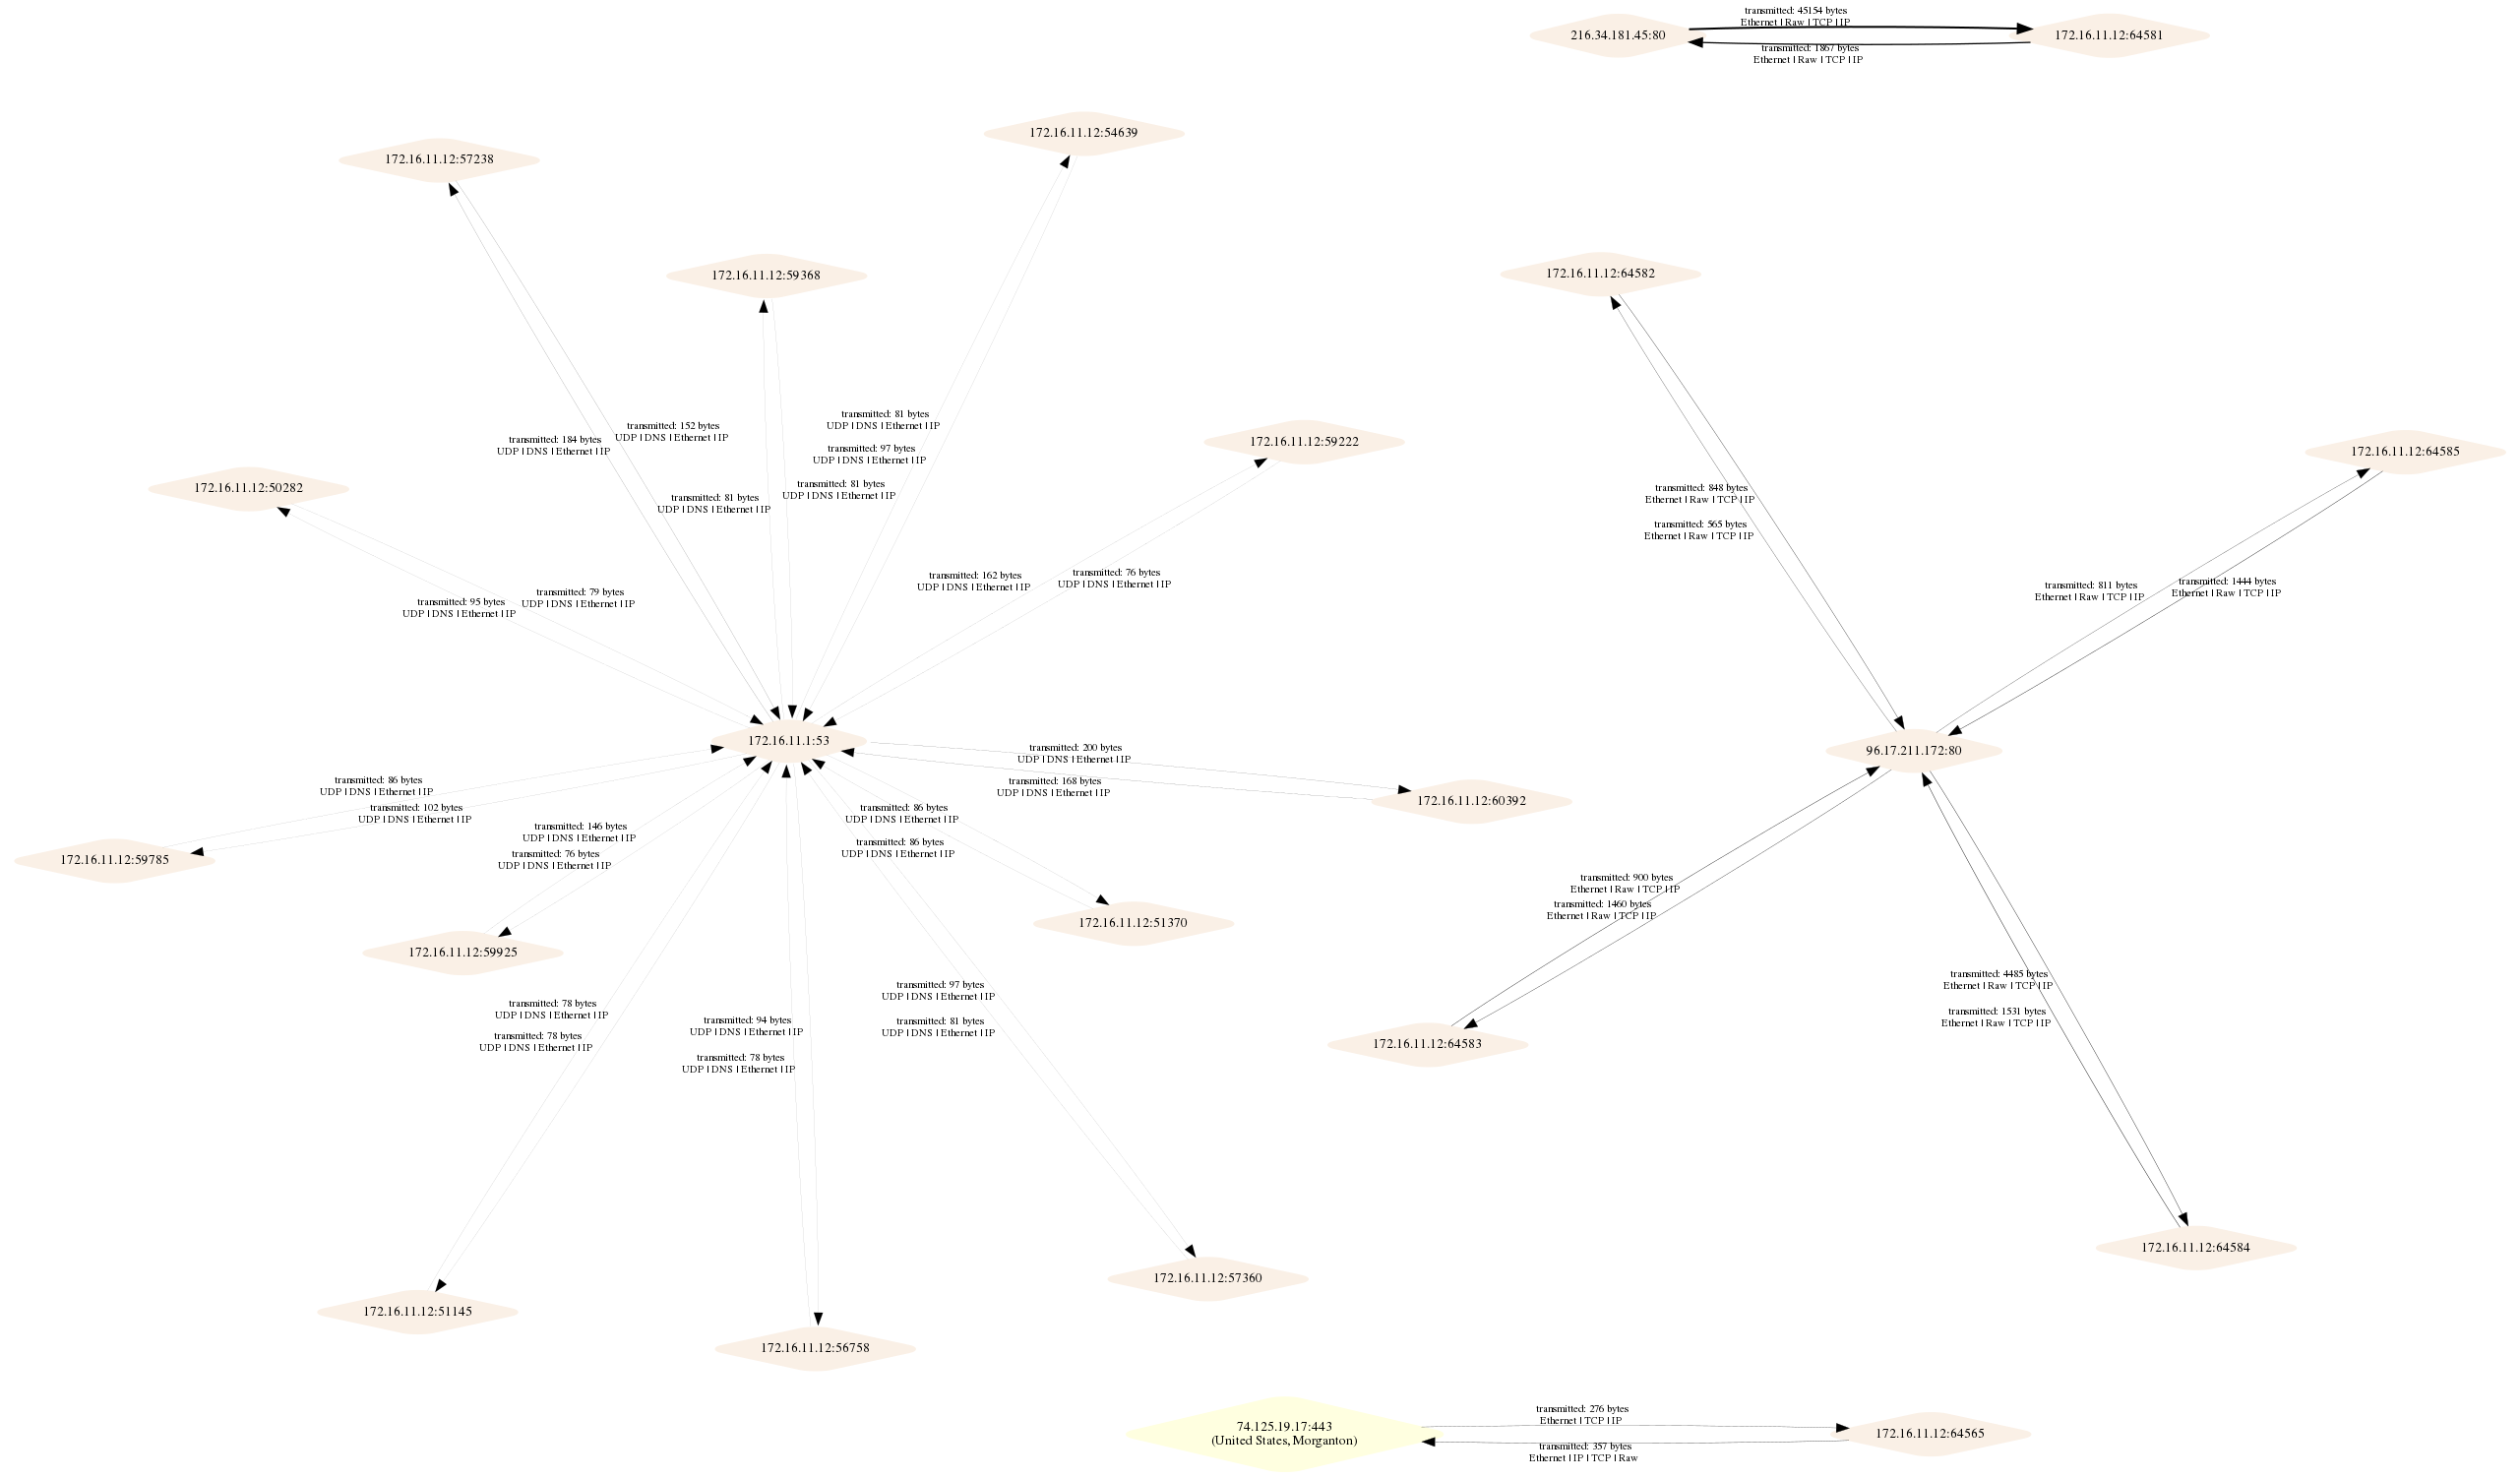
Visualize network topologies and collect graph statistics based on pcap files

PacketSifter is a tool/script that is designed to aid analysts in sifting through a packet capture (pcap) to find noteworthy traffic. Packetsifter…

create cypher create statements for neo4j out of netstat files from multiple machines

Selective protocol extractor from PCAPs or interfaces