
Wireshark
 wireshark/wireshark
Wireshark's official code repository. You can keep the releases coming by donating at https://wiresharkfoundation.org/donate/.
dns-analysisforensicsnetwork-forensics+3
1.6k
wireshark/wiresharkWireshark's official code repository. You can keep the releases coming by donating at https://wiresharkfoundation.org/donate/.

 seladb/pcapplusplus
Multiplatform C++ library for high-performance network packet capture, parsing, crafting, and analysis. Supports libpcap, DPDK, AF_XDP, PF_RING, and…

 corelight/zeek-spicy-wireguard
A Zeek Wireguard protocol analyzer based on Spicy.
 simsong/tcpflow
TCP/IP packet demultiplexer. Download from:
 corelight/zeek-spicy-ipsec
A Zeek IPSec protocol analyzer based on Spicy.
 corelight/zeek-spicy-ospf
A Zeek OSPF packet analyzer based on Spicy.
 netsniff-ng/netsniff-ng
A Swiss army knife for your daily Linux network plumbing.
 microsoft/etl2pcapng
Utility that converts an .etl file containing a Windows network packet capture into .pcapng format.
 google/gopacket
Provides packet processing capabilities for Go
 halildeniz/networkassessment
NetworkAssessment: Network Compromise Assessment Tool
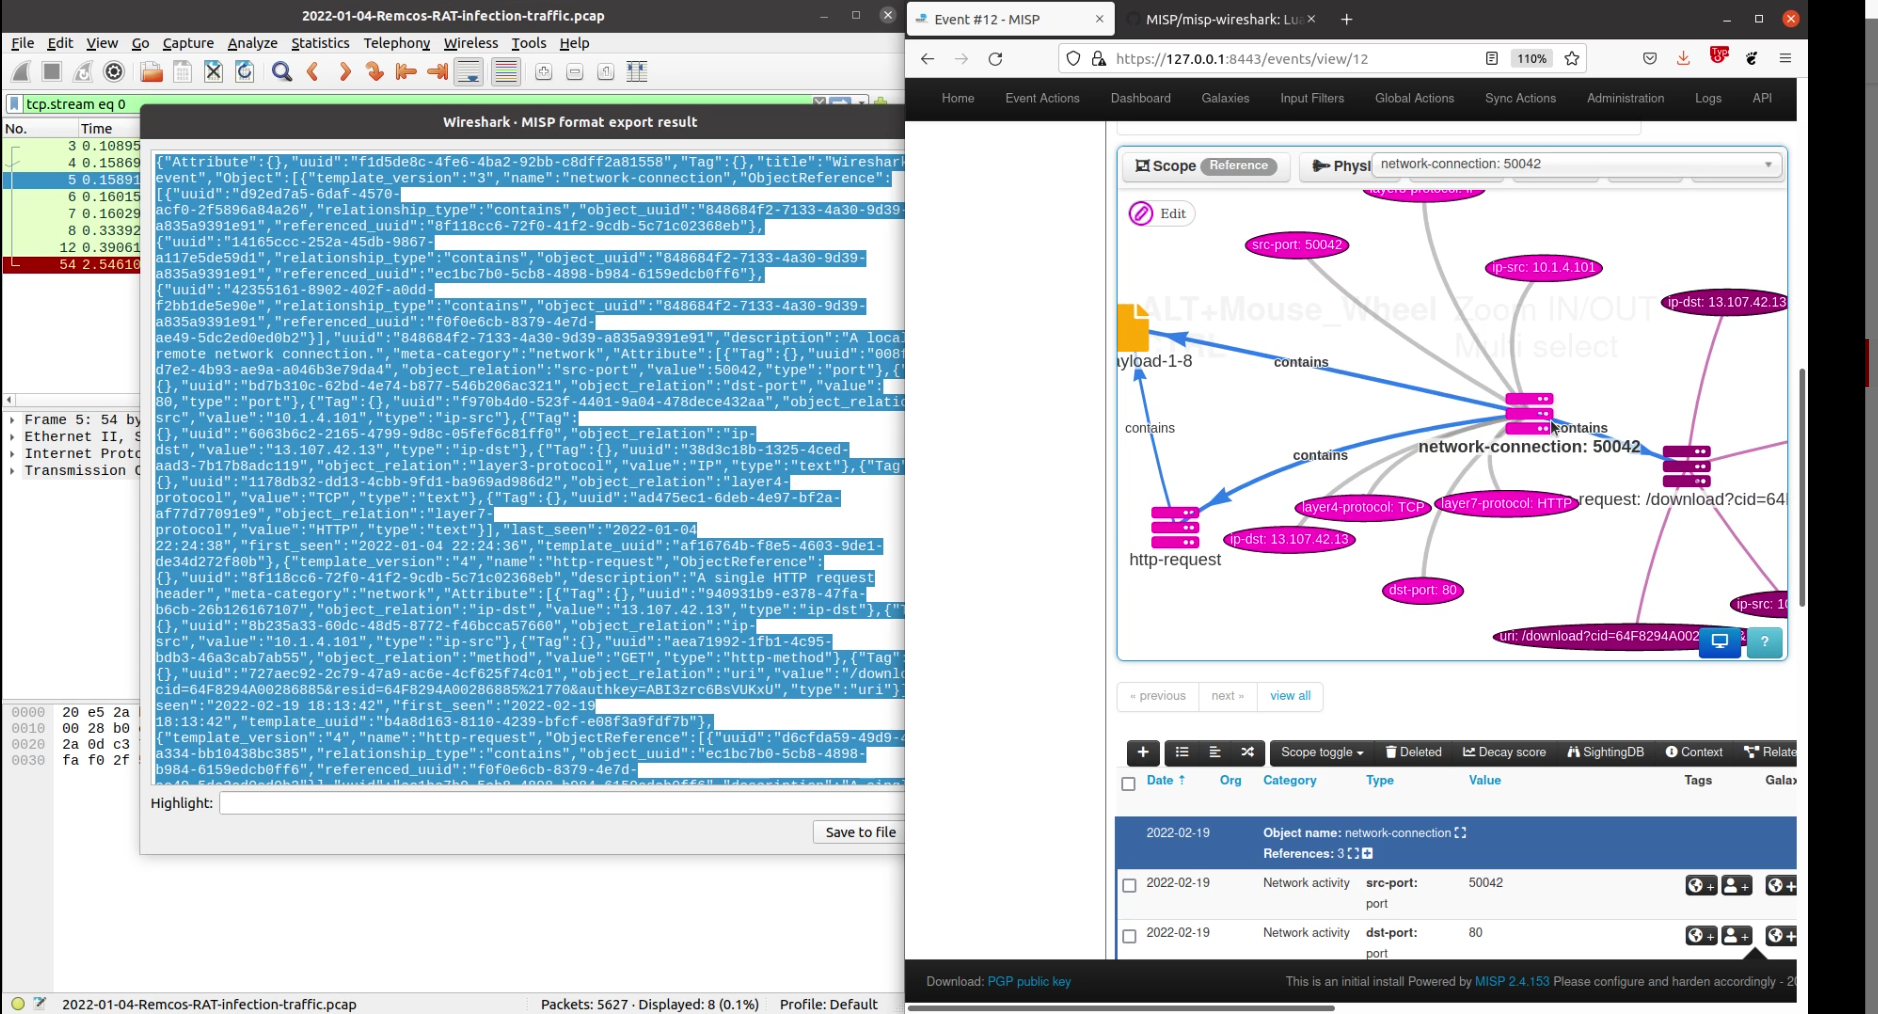 misp/misp-wireshark
Lua plugin to extract data from Wireshark and convert it into MISP format
 corelight/zeek-community-id
Zeek support for Community ID flow hashing.
 gcla/termshark
A terminal UI for tshark, inspired by Wireshark
 gilberto47831/network-filesystem-forensics
Reports on post-exploitation on honeypot exploiting vulnerable wu-ftpd (CVE-2001-0550)
 0x4d31/fatt
FATT /fingerprintAllTheThings - a pyshark based script for extracting network metadata and fingerprints from pcap files and live network traffic
 rjbhide/wireshark-forensics-plugin
Wireshark plugin that correlates network traffic with threat intelligence, asset tags, and vulnerability data to accelerate forensic analysis of PCAP…
 google/stenographer
Stenographer is a packet capture solution which aims to quickly spool all packets to disk, then provide simple, fast access to subsets of those…