
CapTipper
 omriher/captipper
Malicious HTTP traffic explorer
digital-forensicsexploit-frameworksforensics+5
omriher/captipperMalicious HTTP traffic explorer
 benadia/an-integrated-wireless-network-forensic-analysis-framework
This framework combines a set of existing open source tools into an integrated package that automates the forensics investigation process. It is able…
 usarmyresearchlab/dshell
Dshell is a network forensic analysis framework.
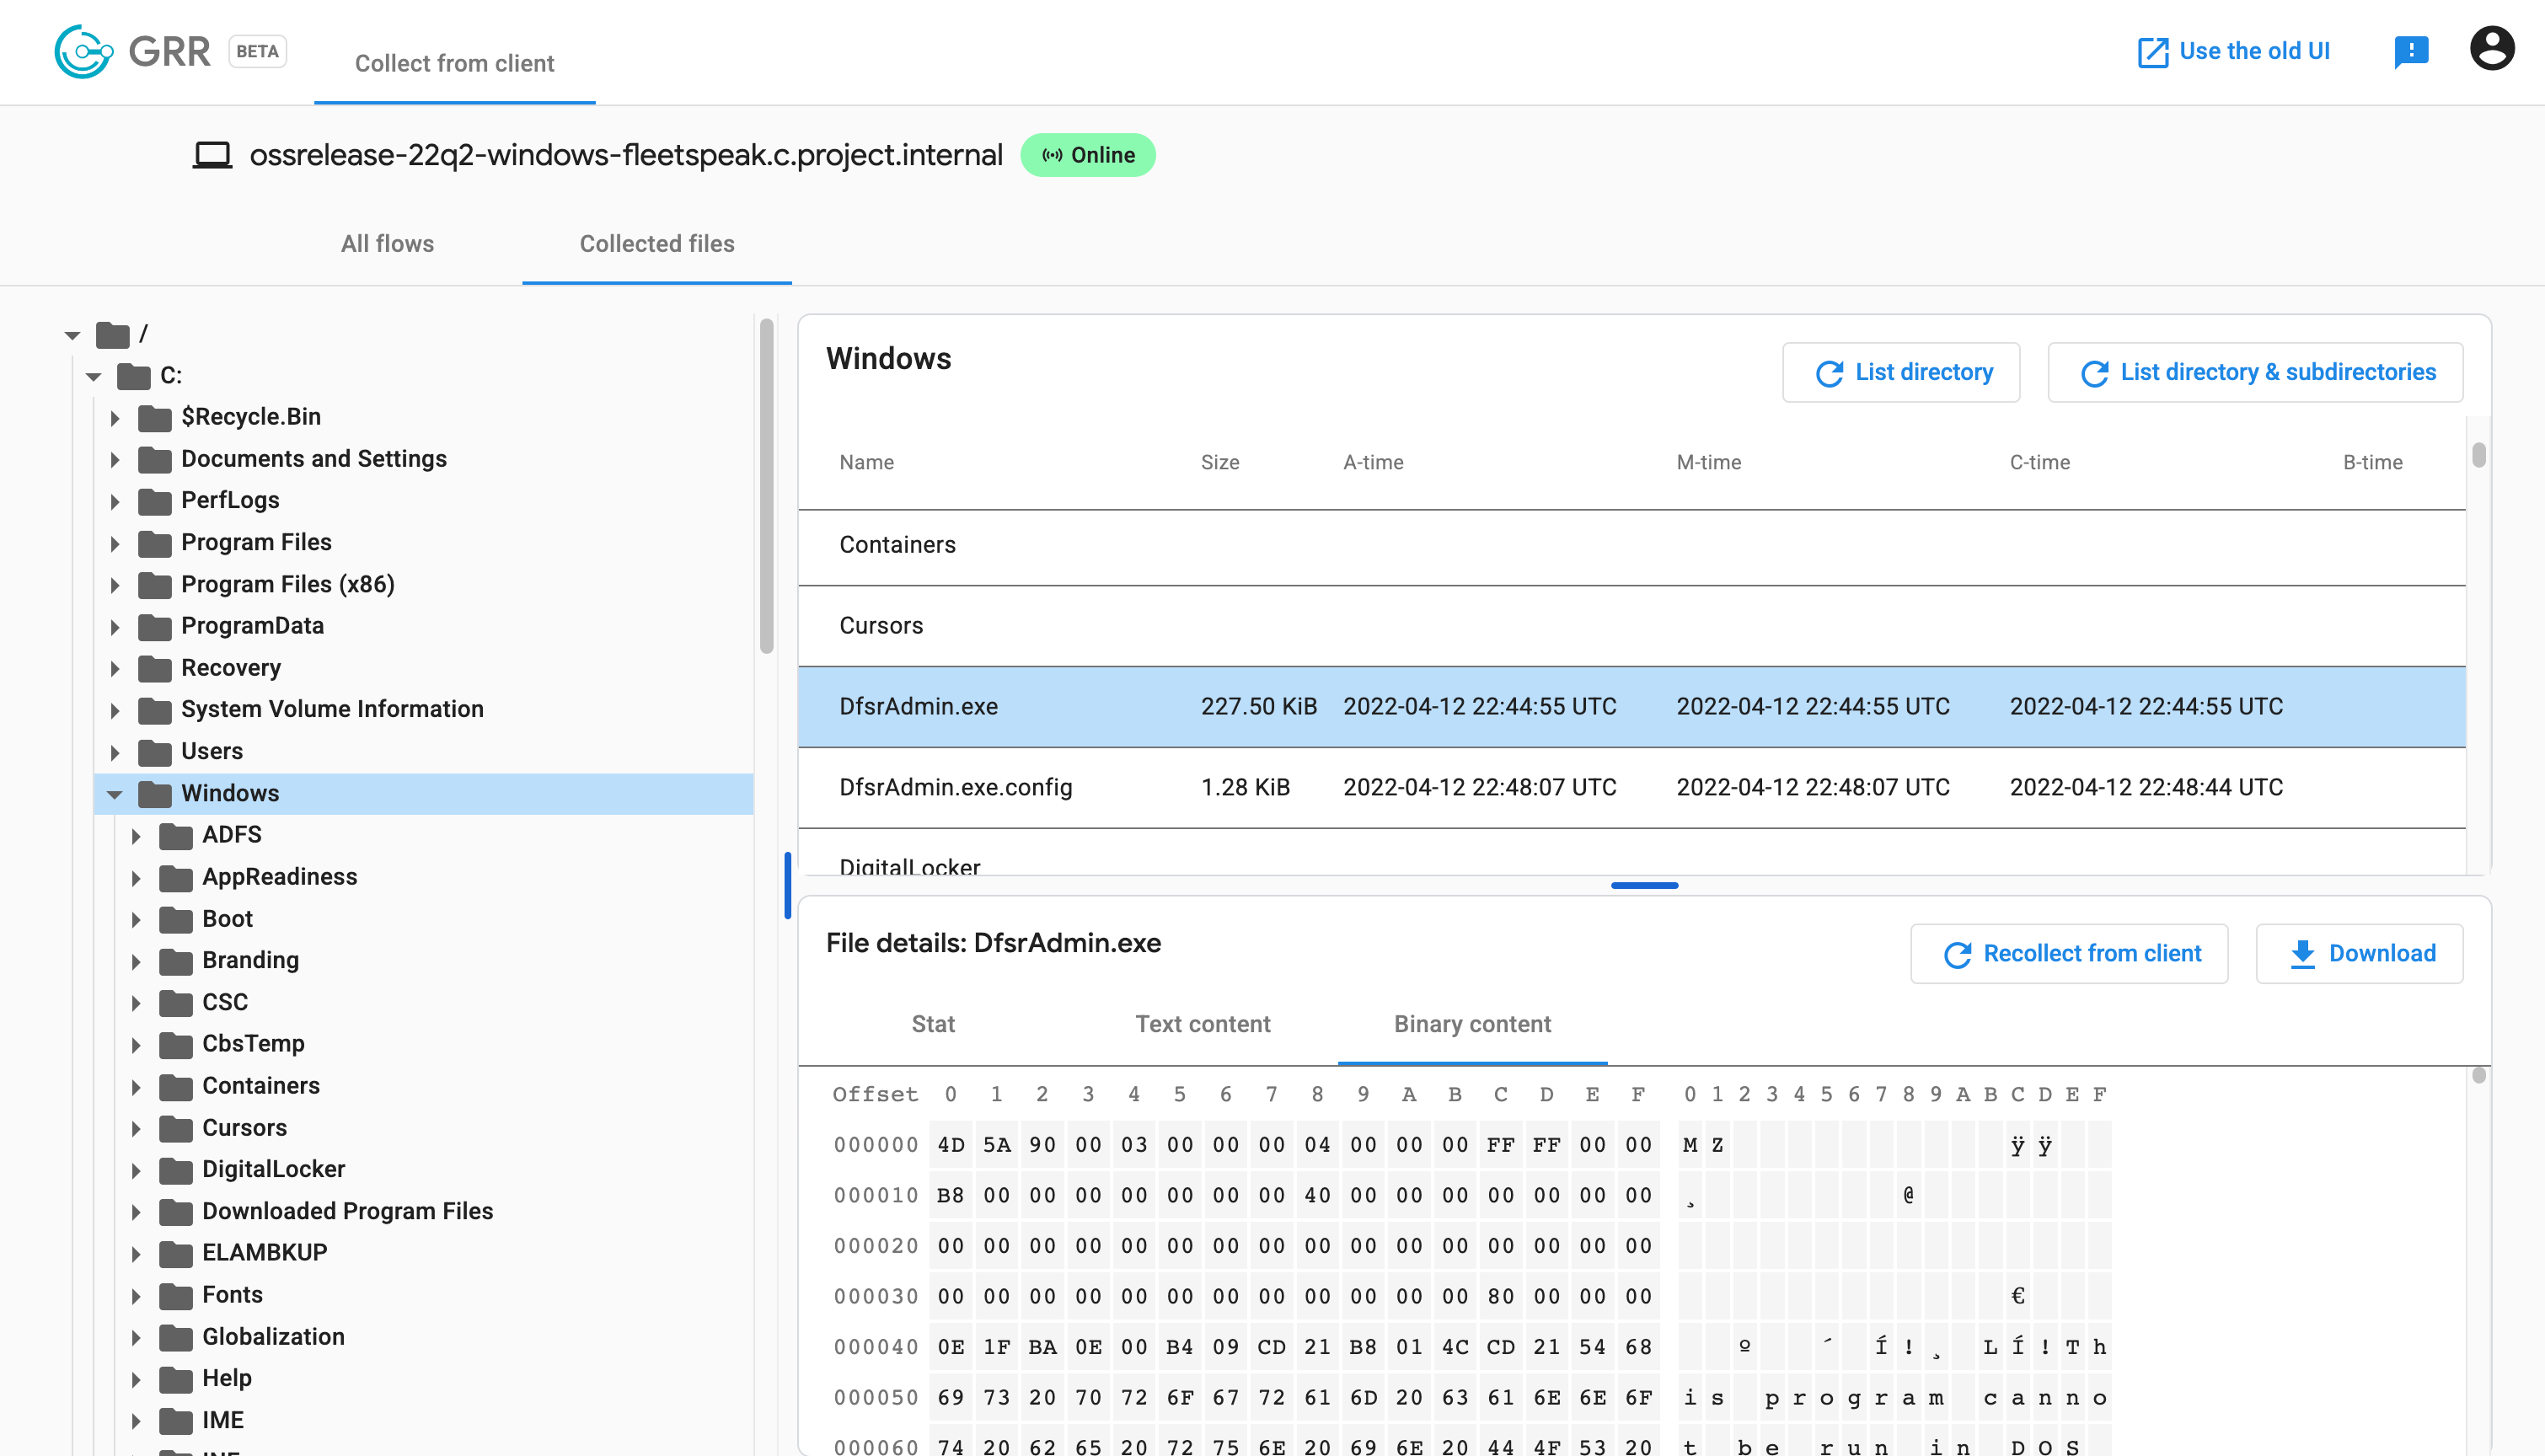 google/grr
Remote live forensics and incident response framework with Python agent for collecting forensic data from endpoints, including memory, disk, and…
 zeek/zeek
Zeek is a powerful network analysis framework that is much different from the typical IDS you may know.
 fox-it/dissect
Dissect is a digital forensics & incident response framework and toolset that allows you to quickly access and analyse forensic artefacts from…