
gopacket
 google/gopacket
Provides packet processing capabilities for Go
network-forensicsnetwork-securitypacket-sniffing-analysis+1
google/gopacketProvides packet processing capabilities for Go
 google/timesketch
Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…
 anssi-fr/dfir4vsphere
Powershell module for VMWare vSphere forensics
 cyb3r-monk/rita-j
Implementation of RITA (Real Intelligence Threat Analytics) in Jupyter Notebook with improved scoring algorithm.
 zedocun/incident-analysis-response-check-point-security-gateway-cve-2024-24919-lfi-exploitation
Incident Response (IR) case study documenting the investigation of an exploitation attempt targeting CVE-2024-24919 (Arbitrary File Read) on a Check…
 nccgroup/baskerville
Selective protocol extractor from PCAPs or interfaces
 nccgroup/pcap-burp
Pcap importer for Burp
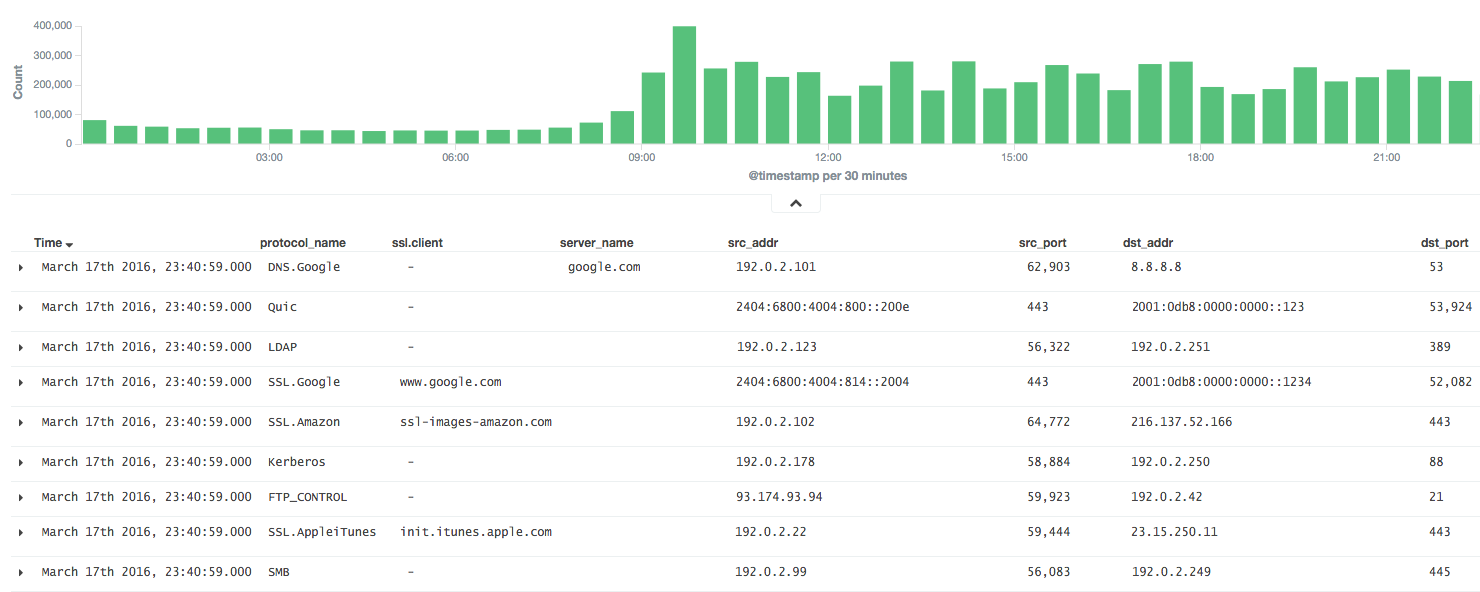 knqyf263/ndff
A flow-based network monitor with Deep Packet Inspection
 corelight/corelightforsplunk
Splunk app for integrating and analyzing Corelight network detection data, enabling real-time threat hunting and incident response.
 corelight/zeek-community-id
Zeek support for Community ID flow hashing.
 corelight/zeek-quic
Bro analyzer that detects Google's QUIC protocol
 corelight/zeek-spicy-ipsec
A Zeek IPSec protocol analyzer based on Spicy.
 corelight/zeek-spicy-ospf
A Zeek OSPF packet analyzer based on Spicy.
 corelight/zeek-spicy-wireguard
A Zeek Wireguard protocol analyzer based on Spicy.

 cisagov/malcolm
Containerized network traffic analysis suite ingesting PCAP, Zeek logs, and Suricata alerts for automated normalization, enrichment, and correlation…
 gilberto47831/network-filesystem-forensics
Reports on post-exploitation on honeypot exploiting vulnerable wu-ftpd (CVE-2001-0550)

 wireshark/wireshark
Wireshark's official code repository. You can keep the releases coming by donating at https://wiresharkfoundation.org/donate/.