Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
32 results
dns_watchdog_windows2 preview

dns_watchdog_windows2

GitHubmicrolaser/dns_watchdog_windows2

PowerShell script that monitors Windows DNS traffic via pktmon to detect poisoning, spoofing, rogue resolver responses, and gateway MAC changes,…

anomaly-detectiondefensive-toolsdns-analysis+5
15 days ago
CAPEsolo preview

CAPEsolo

GitHubcapesandbox/capesolo

Standalone Windows VM malware sandbox running capemon, with GUI triage viewer, YARA signatures, IOC extraction, network analysis, and…

defensive-toolsdynamic-analysis-sandboxingforensics+7
604 days ago
memory-forensic preview

memory-forensic

GitHubsecurityronin/memory-forensic

Walk any memory dump. Find what's hidden. Linux + Windows kernel forensics from a single static Rust binary — no Python required.

binary-analysiscontainer-escapedata-recovery+7
131 month ago
wireshark preview

wireshark

GitHubwireshark/wireshark

Capture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…
bluetooth-securitydata-exfiltrationdigital-forensics+11
10.0k5h 7m ago
windows-malware-behavioral-analysis preview

windows-malware-behavioral-analysis

GitHub0x0allenace/windows-malware-behavioral-analysis

Behavioral Malware Analysis of a Simulated Multi-Stage Windows Malware Sample using FLARE-VM and REMnux. Evidence-driven DFIR investigation with IOC…

digital-forensicsdynamic-analysis-sandboxingeducation+8
12 months ago
NetScope preview

NetScope

GitHubspectralzero/netscope

Offline-first network investigation and response platform for Windows. Turns a pcap or live capture into a full forensic verdict — attack story,…

anomaly-detectiondigital-forensicsincident-response+5
31 month ago
plugxdecoder preview

plugxdecoder

GitHubkcreyts/plugxdecoder

Decodes PlugX traffic and encrypted/compressed artifacts

digital-forensicsencryption-decryption-toolsforensics+3
3813 years ago
tcpdump preview

tcpdump

GitHubthe-tcpdump-group/tcpdump

the TCPdump network dissector

dns-analysisforensicslog-analysis+5
3.2k13 days ago
Wireshark preview

Wireshark

GitLabwireshark/wireshark

Wireshark's official code repository. You can keep the releases coming by donating at https://wiresharkfoundation.org/donate/.

dns-analysisforensicsnetwork-forensics+3
1.6k4h 50m ago
RCE-CVE-2017-0199-detection-analysis preview

RCE-CVE-2017-0199-detection-analysis

GitHubahmed-tarek22752/rce-cve-2017-0199-detection-analysis

This repository contains a full blue-team malware analysis of a real malicious DOCX exploiting CVE-2017-0199. The lab includes sandbox execution,…

command-and-controldigital-forensicseducation+8
21 month ago
Incident-Response-Powershell preview

Incident-Response-Powershell

GitHubbert-janp/incident-response-powershell

PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…
digital-forensicsdisk-forensicsforensics+6
8174 months ago
shadow-fleet-tracker-light preview

shadow-fleet-tracker-light

GitHubformerlab/shadow-fleet-tracker-light

Open source Baltic Sea shadow fleet tracker. 1200+ vessels, live AIS, cable proximity alerts. No cloud, no subscription, runs locally

data-exfiltrationdigital-forensicsdns-analysis+9
445 months ago
irflow-timeline preview

irflow-timeline

GitHubr3nzsec/irflow-timeline

DFIR Timeline Analysis for macOS — SQLite-backed viewer for CSV, TSV, XLSX, EVTX, Plaso, $MFT, and $J files with AI Artifacts, AI Secret Hunt,…
digital-forensicsdisk-forensicsforensics+7
37227 days ago
Digital-Forensics-Guide preview

Digital-Forensics-Guide

GitHubmikeroyal/digital-forensics-guide

Digital Forensics Guide. Learn all about Digital Forensics, Computer Forensics, Mobile device Forensics, Network Forensics, and Database Forensics.

curated-resourcesdigital-forensicseducation+7
3.2k2 years ago
ir-rescue preview

ir-rescue

GitHubdiogo-fernan/ir-rescue

A Windows Batch script and a Unix Bash script to comprehensively collect host forensic data during incident response.

digital-forensicsdisk-forensicsforensics+6
4885 years ago
PcapPlusPlus preview

PcapPlusPlus

GitHubseladb/pcapplusplus

Multiplatform C++ library for high-performance network packet capture, parsing, crafting, and analysis. Supports libpcap, DPDK, AF_XDP, PF_RING, and…
crawlerdns-analysisforensics+5
3.1k3 days ago
CyberScan preview

CyberScan

GitHubmedbenali/cyberscan

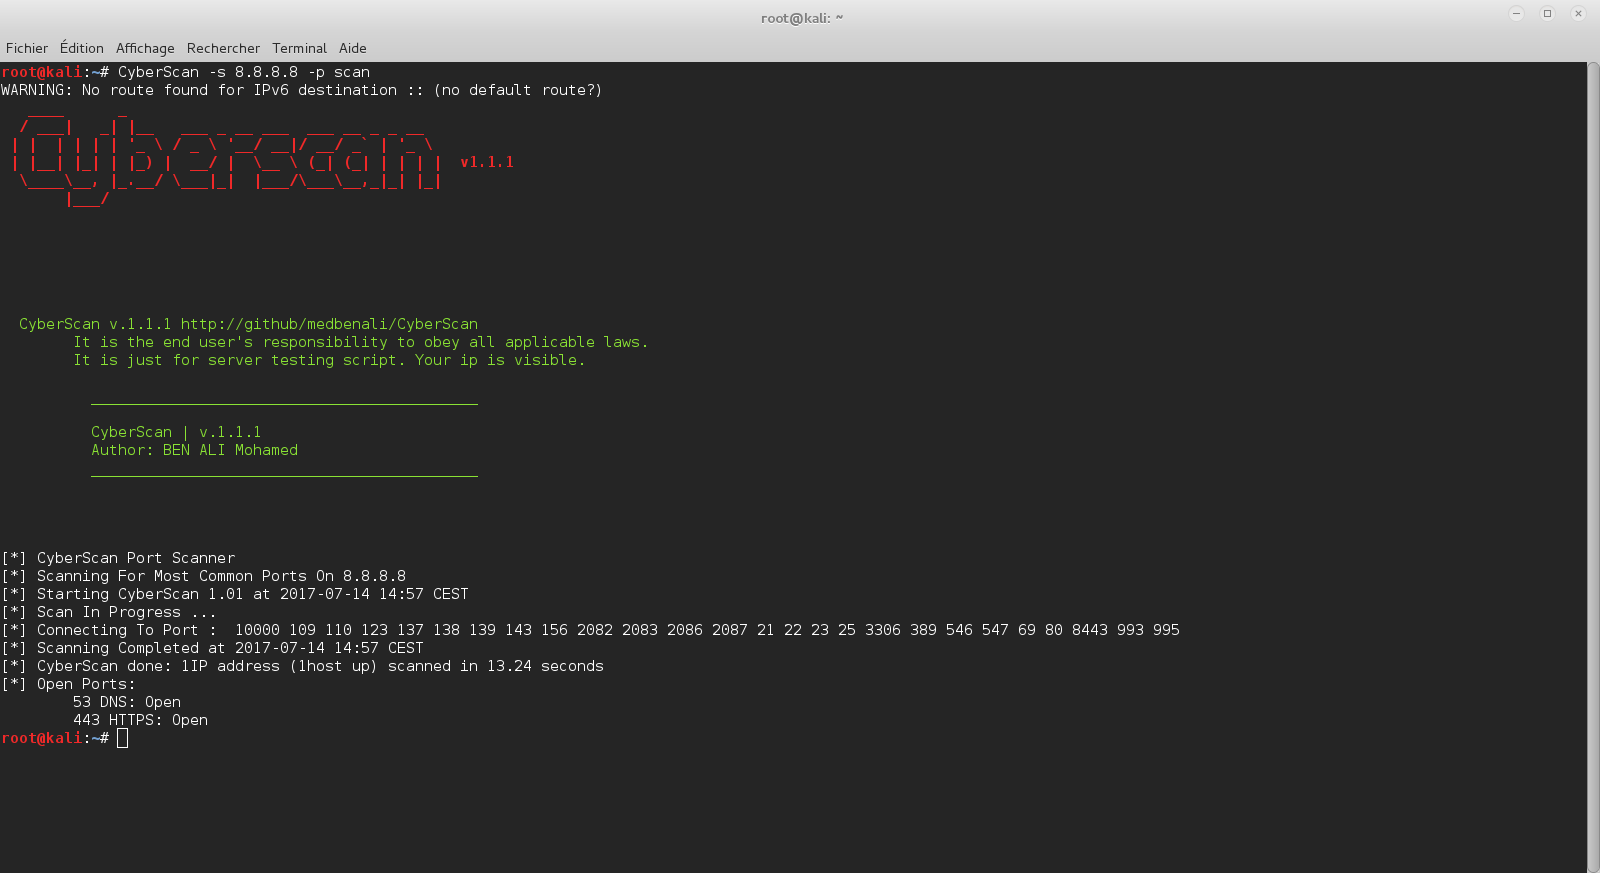
Open-source network forensics toolkit for packet analysis, port scanning, host discovery, and IP geolocation. Supports ARP, ICMP, TCP, UDP pings and…

information-gatheringnetwork-forensicsnetwork-mapping+3
4705 months ago
Loki preview

Loki

GitHubneo23x0/loki

IOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…

anomaly-detectiondigital-forensicsdisk-forensics+11
3.8k8 months ago
Previous12Next

