
joy
 cisco/joy
A package for capturing and analyzing network flow data and intraflow data, for network research, forensics, and security monitoring.
anomaly-detectiondigital-forensicsdns-analysis+7
1.4k6 years ago
cisco/joyA package for capturing and analyzing network flow data and intraflow data, for network research, forensics, and security monitoring.
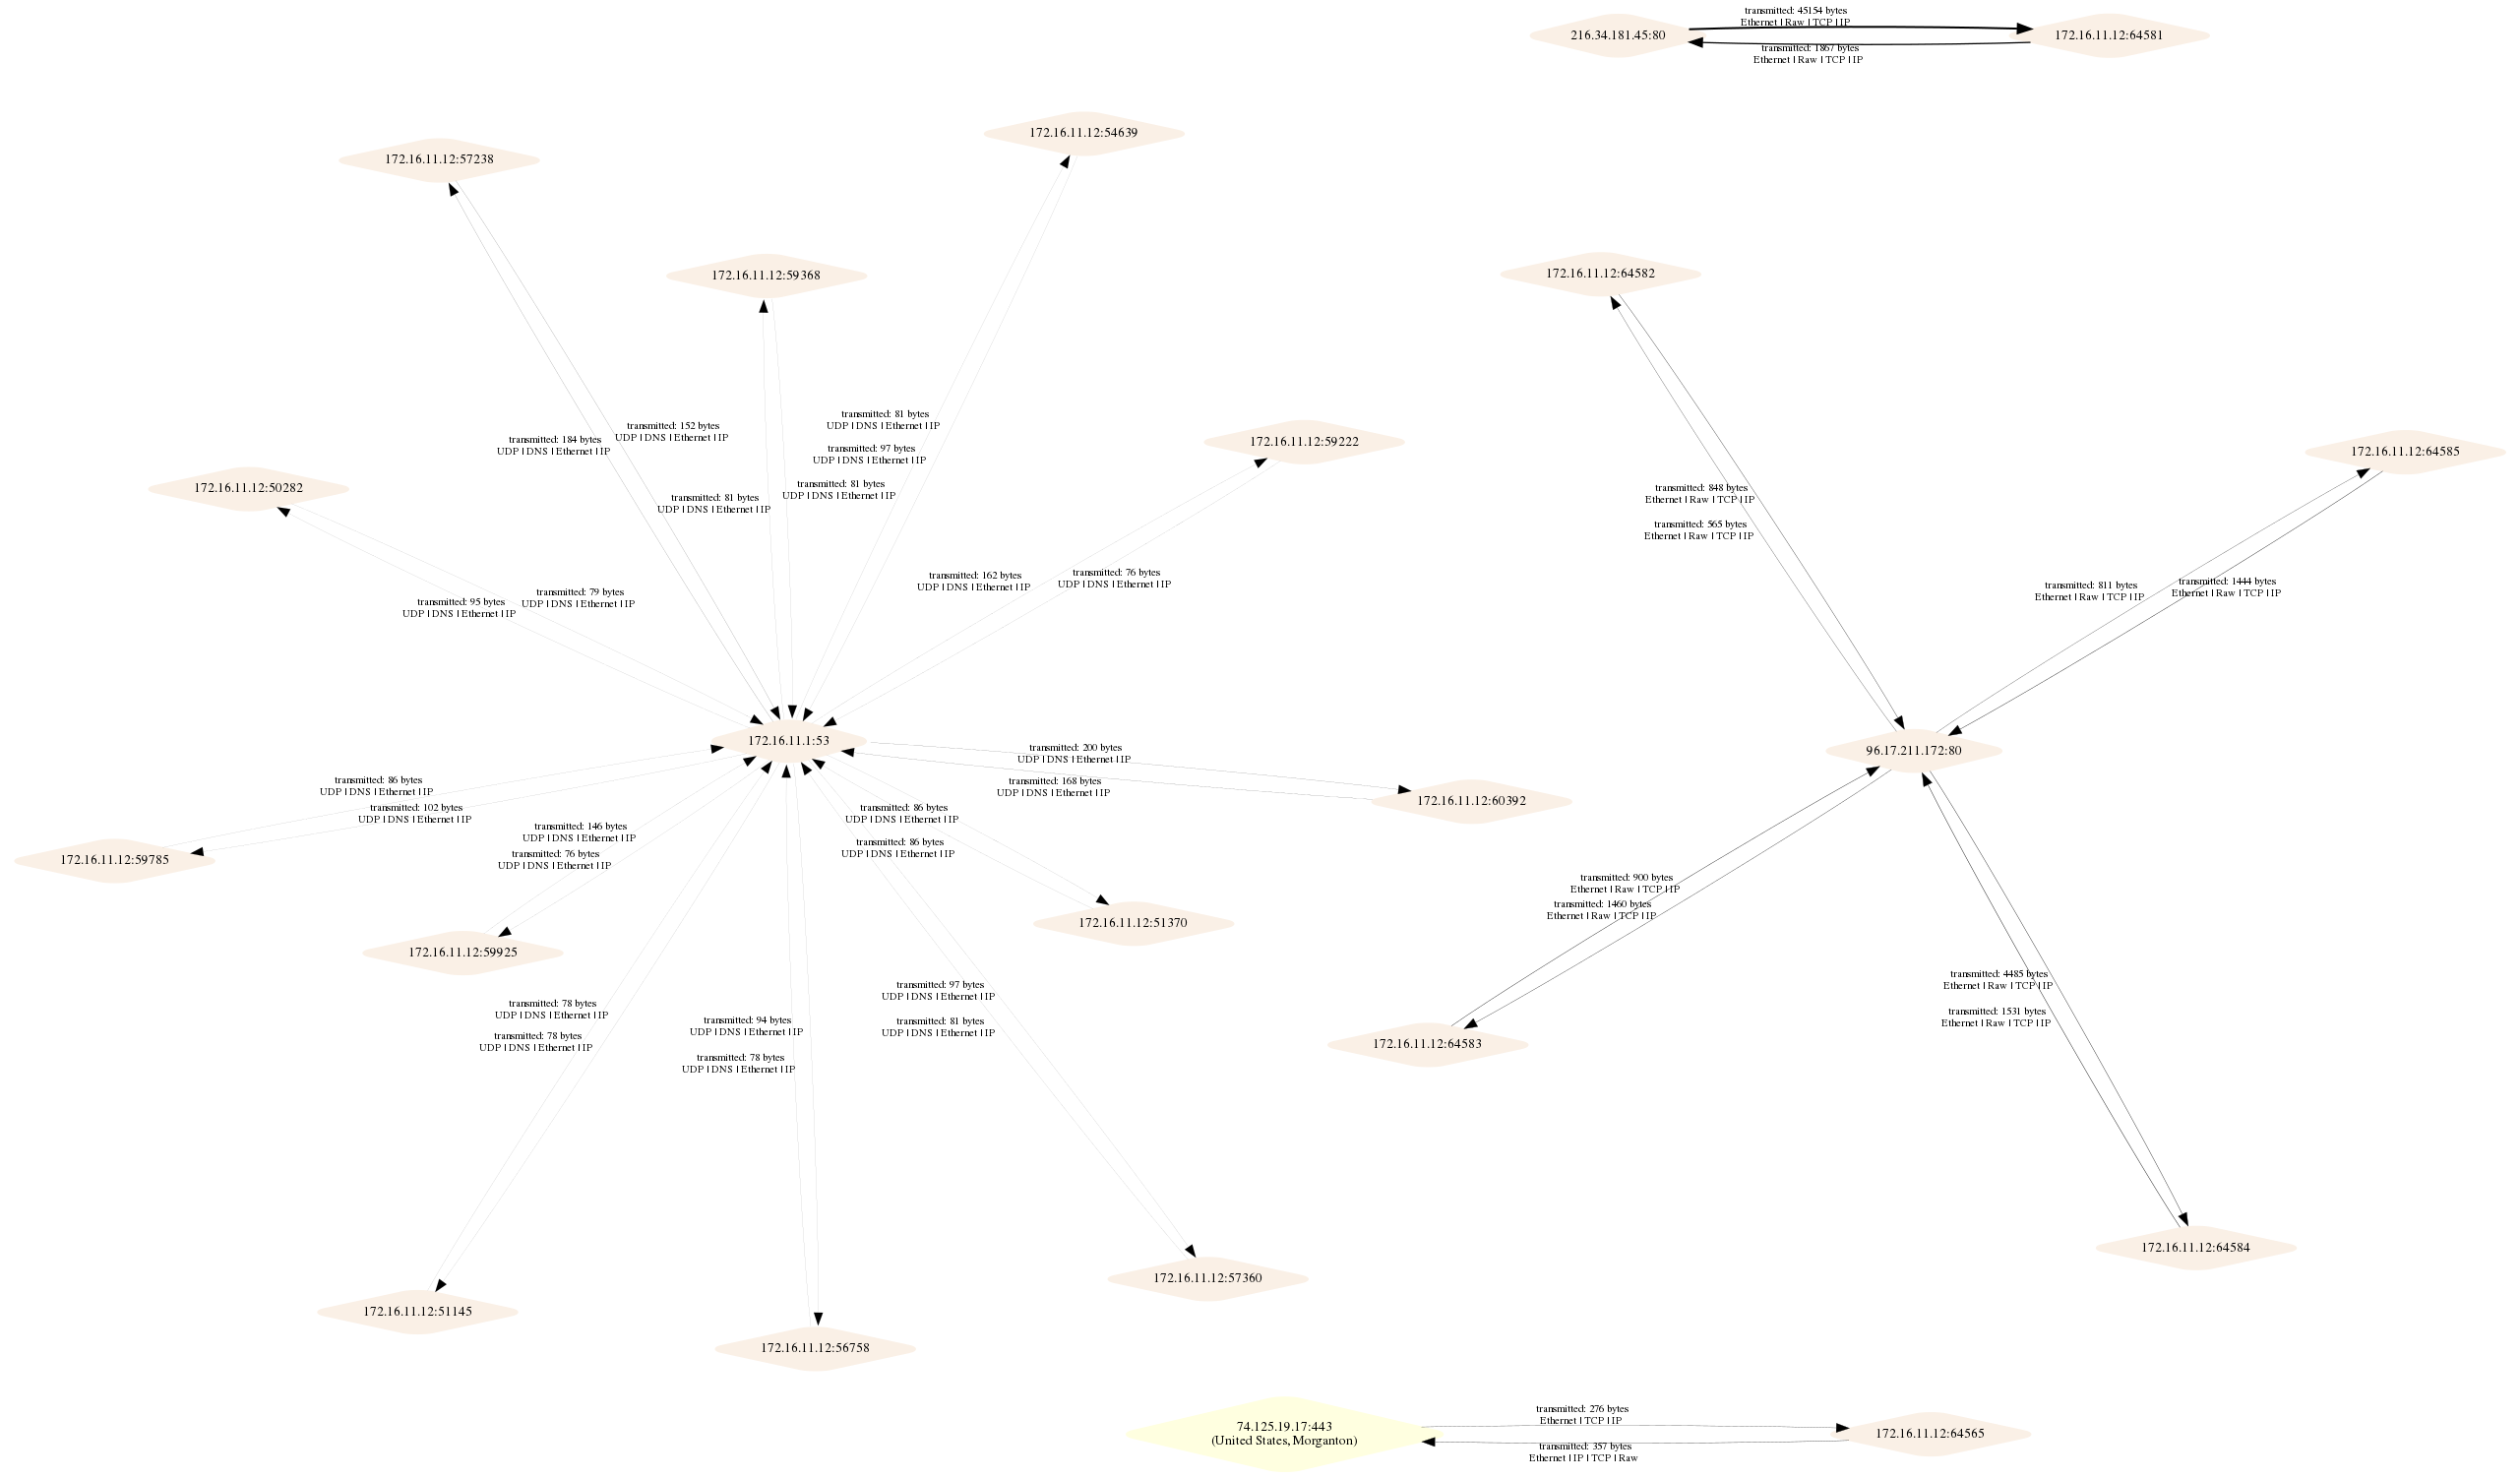 1ultimat3/pcapviz
Visualize network topologies and collect graph statistics based on pcap files
 secdev/scapy
Python-based interactive packet manipulation library for forging, decoding, sending, capturing, and analyzing network packets across a wide range of…
 0x4d31/fatt
FATT /fingerprintAllTheThings - a pyshark based script for extracting network metadata and fingerprints from pcap files and live network traffic
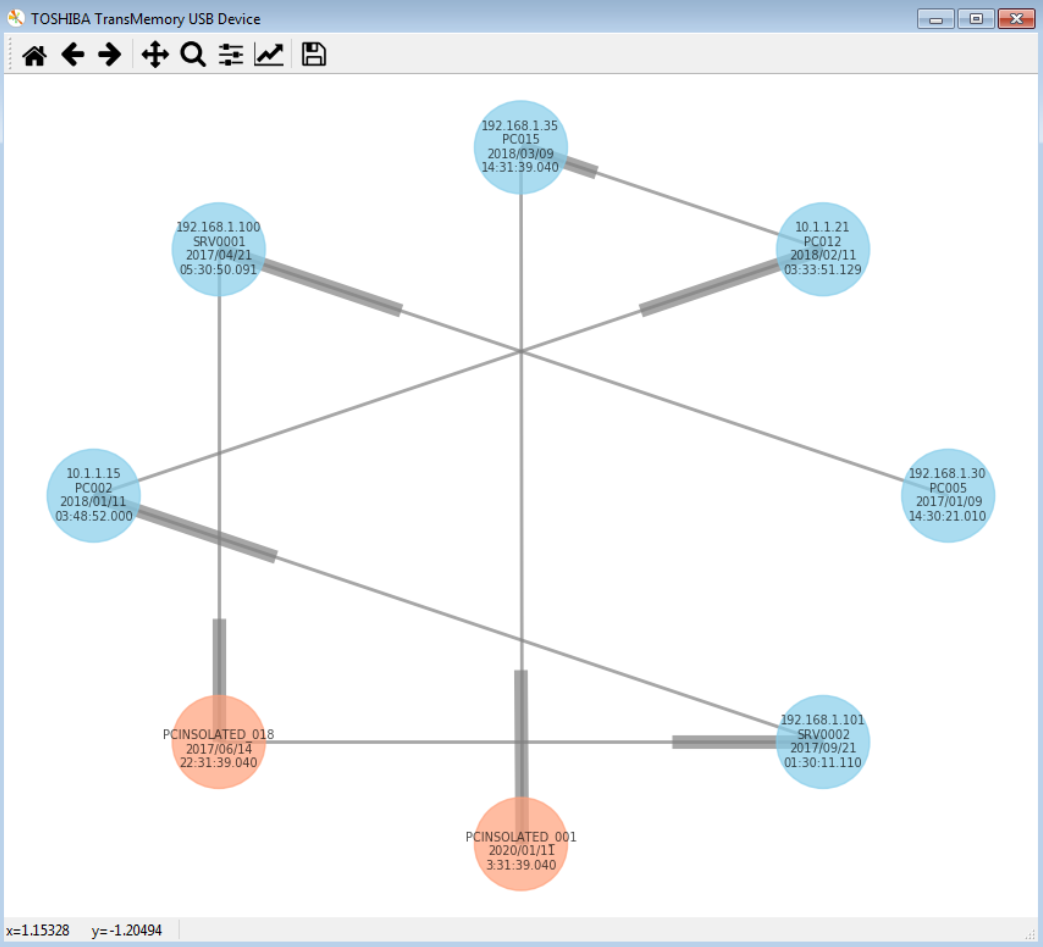 telefonica/hiddennetworks-python
USB device connection forensics tool that traces physical device-to-computer relationships across local and domain networks, generating visual graphs…
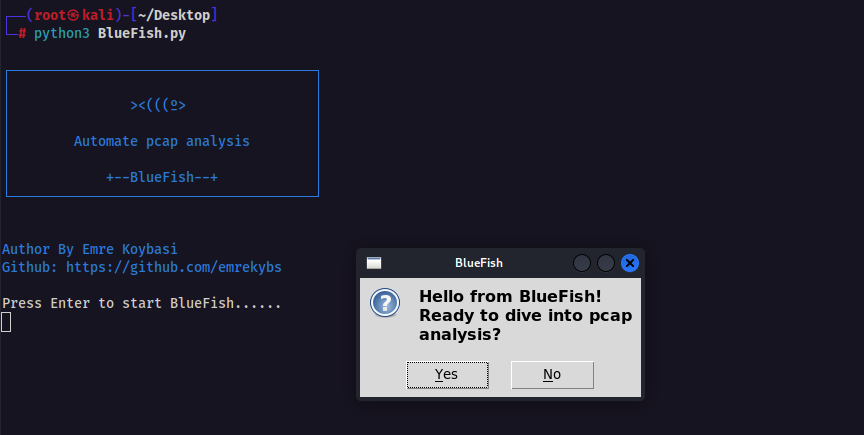 emrekybs/bluefish
Automation tool designed to simplify the analysis of PCAP (Packet Capture) files