
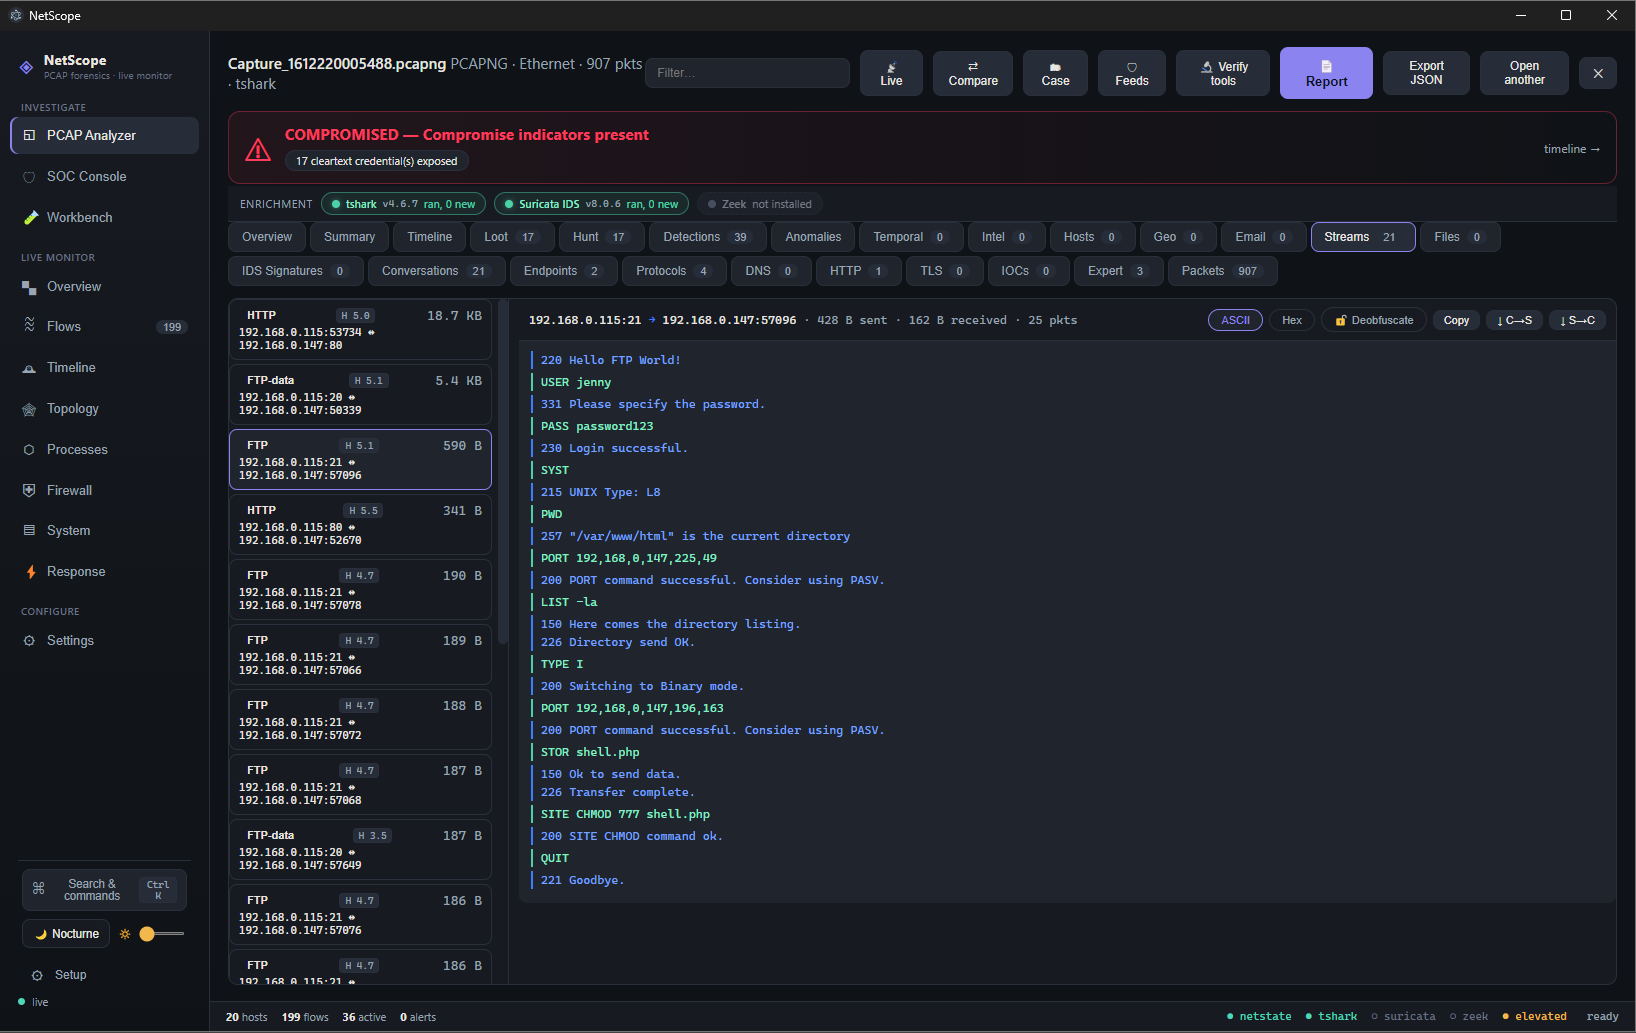
NetScope
 spectralzero/netscope
Offline-first network investigation and response platform for Windows. Turns a pcap or live capture into a full forensic verdict — attack story,…
anomaly-detectiondigital-forensicsincident-response+5
3
spectralzero/netscopeOffline-first network investigation and response platform for Windows. Turns a pcap or live capture into a full forensic verdict — attack story,…
 diogo-fernan/ir-rescue
A Windows Batch script and a Unix Bash script to comprehensively collect host forensic data during incident response.
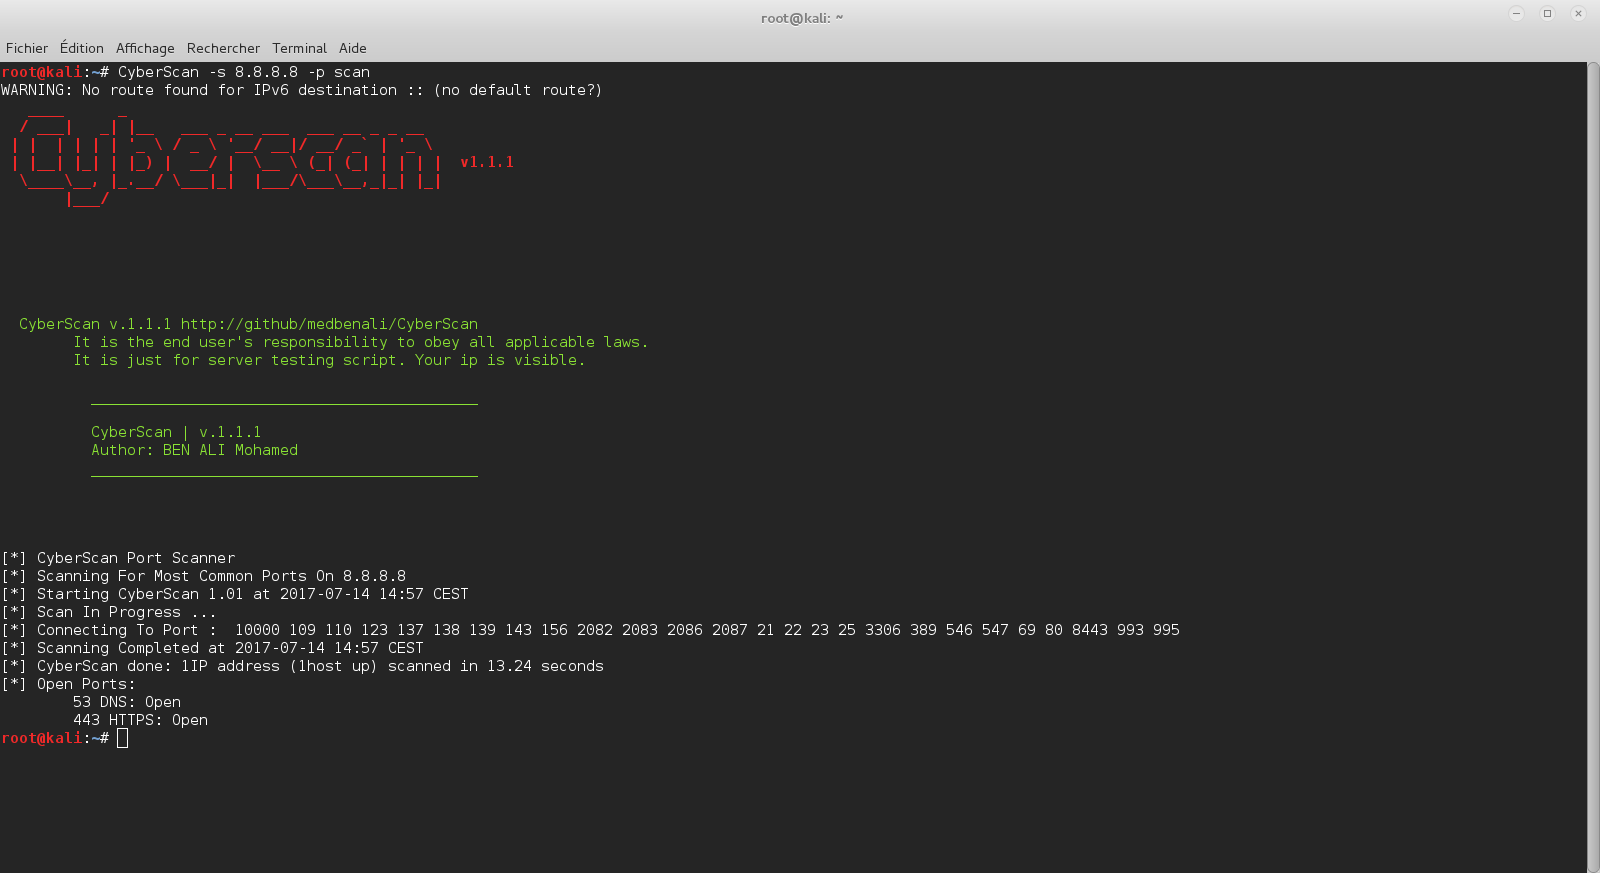 medbenali/cyberscan
Open-source network forensics toolkit for packet analysis, port scanning, host discovery, and IP geolocation. Supports ARP, ICMP, TCP, UDP pings and…
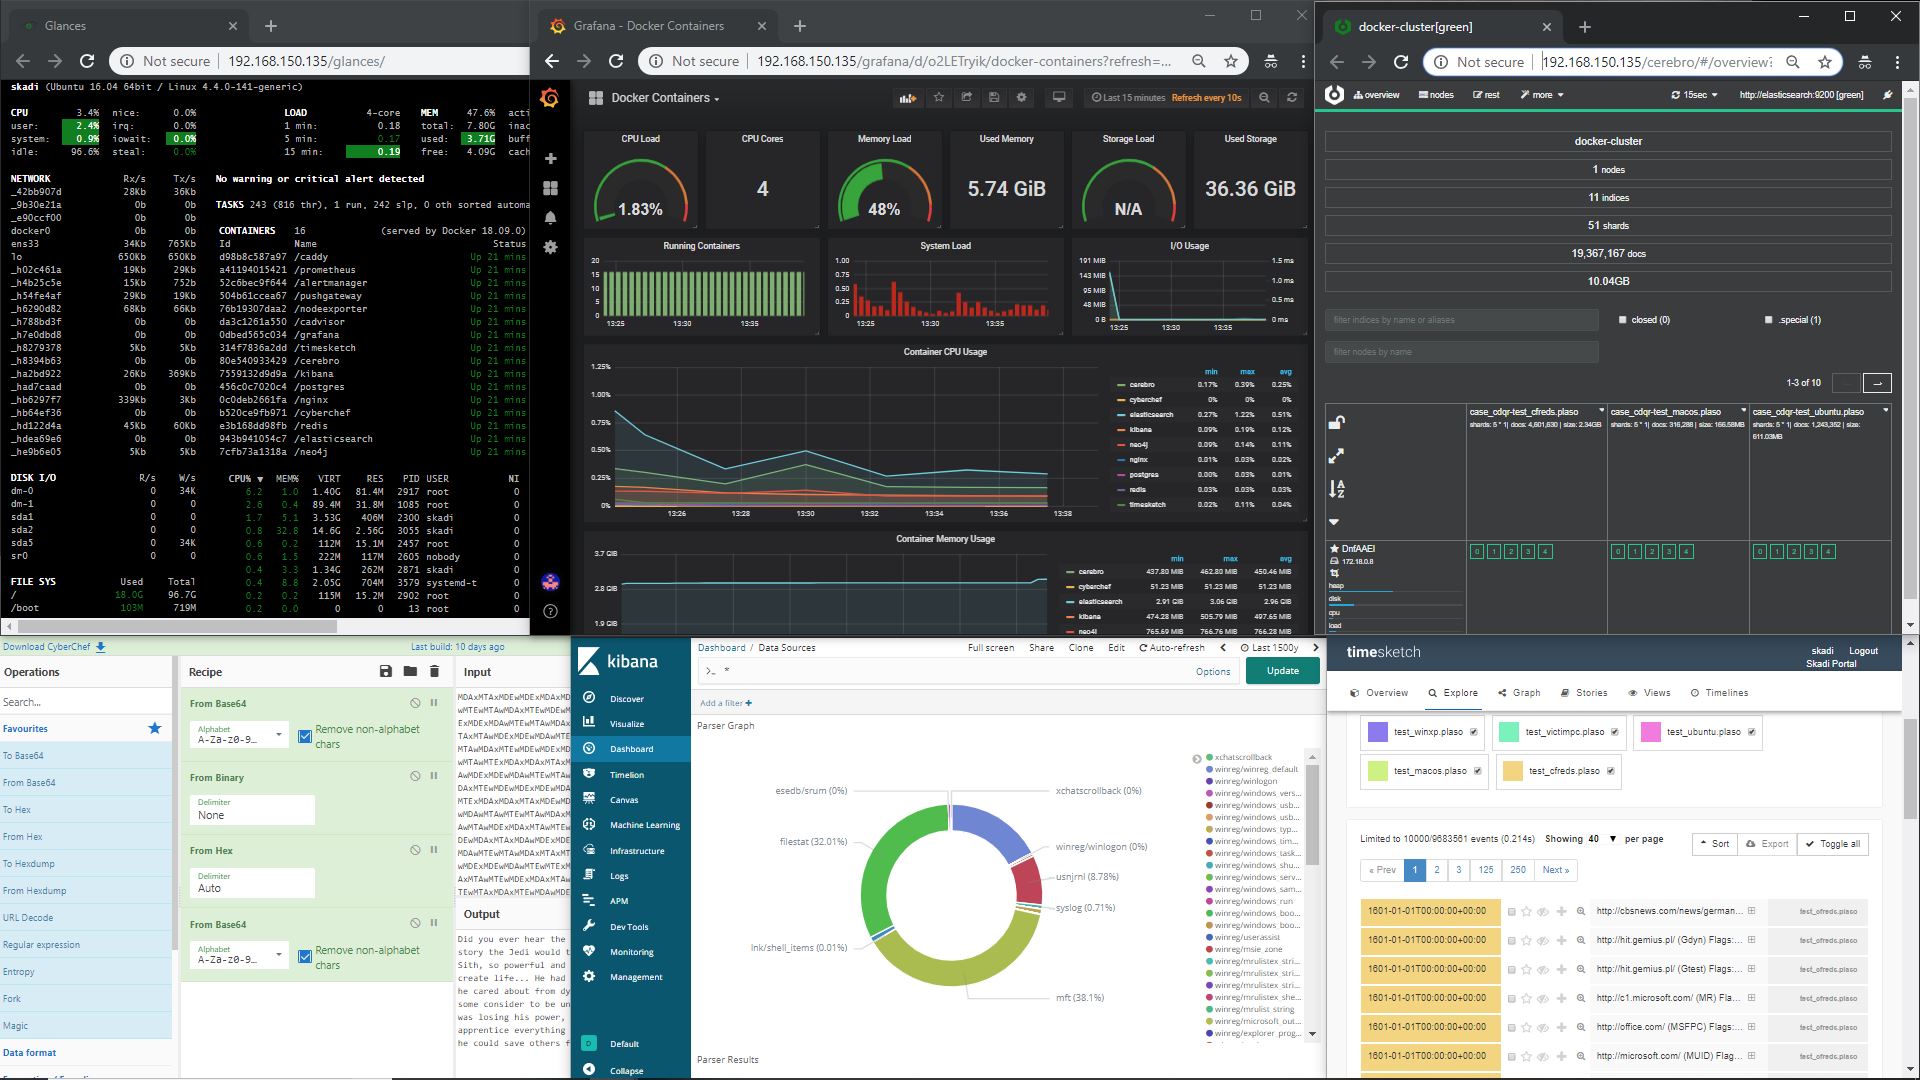 orlikoski/skadi
Collect, Process, and Hunt with host based data from MacOS, Windows, and Linux
