
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
43 results
gopacket preview

gopacket

GitHubgoogle/gopacket

Provides packet processing capabilities for Go

network-forensicsnetwork-securitypacket-sniffing-analysis+1
6.8k
1 year ago
wireshark preview

wireshark

GitHubwireshark/wireshark

Capture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…

bluetooth-securitydata-exfiltrationdigital-forensics+11
9.9k2 days ago
securityonion preview

securityonion

GitHubsecurity-onion-solutions/securityonion

Open-source security monitoring platform for threat hunting, intrusion detection, log management, incident response, and endpoint visibility with…
anomaly-detectionanti-botdefensive-tools+9
4.9k2 days ago
Cyber-Defenders-lab- preview

Cyber-Defenders-lab-

GitHubabiral-timalsina/cyber-defenders-lab-

My write-ups from CyberDefenders' Blue Team labs, solved using Wireshark. Covers TeamCity RCE (CVE-2024-27198), XSS session hijacking, and…
digital-forensicseducationincident-response+3
1 month ago
Baskerville preview

Baskerville

GitHubnccgroup/baskerville

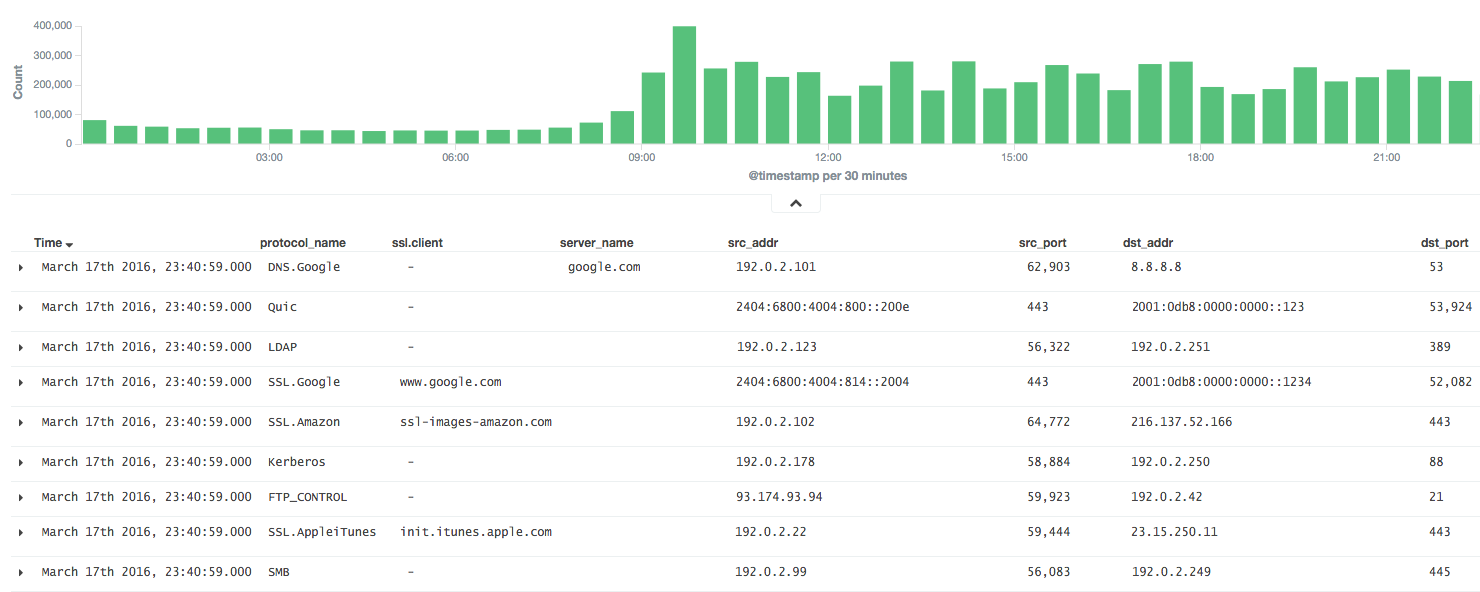
Selective protocol extractor from PCAPs or interfaces

incident-responsenetwork-forensicsnetwork-security+1
511 years ago
pcap-burp preview

pcap-burp

GitHubnccgroup/pcap-burp

Pcap importer for Burp
network-forensicspacket-sniffing-analysispenetration-testing+2
1145 years ago
ndff preview

ndff

GitHubknqyf263/ndff

A flow-based network monitor with Deep Packet Inspection

dns-analysislog-analysisnetwork-forensics+2
289 years ago
zeek-community-id preview

zeek-community-id

GitHubcorelight/zeek-community-id

Zeek support for Community ID flow hashing.
log-analysisnetwork-forensicsnetwork-security+1
373 years ago
zeek-quic preview

zeek-quic

GitHubcorelight/zeek-quic

Bro analyzer that detects Google's QUIC protocol

intrusion-detectionlog-analysisnetwork-forensics+2
115 years ago
zeek-spicy-ipsec preview

zeek-spicy-ipsec

GitHubcorelight/zeek-spicy-ipsec

A Zeek IPSec protocol analyzer based on Spicy.

intrusion-detectionnetwork-forensicsnetwork-security+1
811 months ago
zeek-spicy-ospf preview

zeek-spicy-ospf

GitHubcorelight/zeek-spicy-ospf

A Zeek OSPF packet analyzer based on Spicy.
anomaly-detectionnetwork-forensicsnetwork-mapping+2
81 year ago
zeek-spicy-wireguard preview

zeek-spicy-wireguard

GitHubcorelight/zeek-spicy-wireguard

A Zeek Wireguard protocol analyzer based on Spicy.
network-forensicsnetwork-securitypacket-sniffing-analysis
76 months ago
Wireshark preview

Wireshark

GitHubkirkdjohnson/wireshark

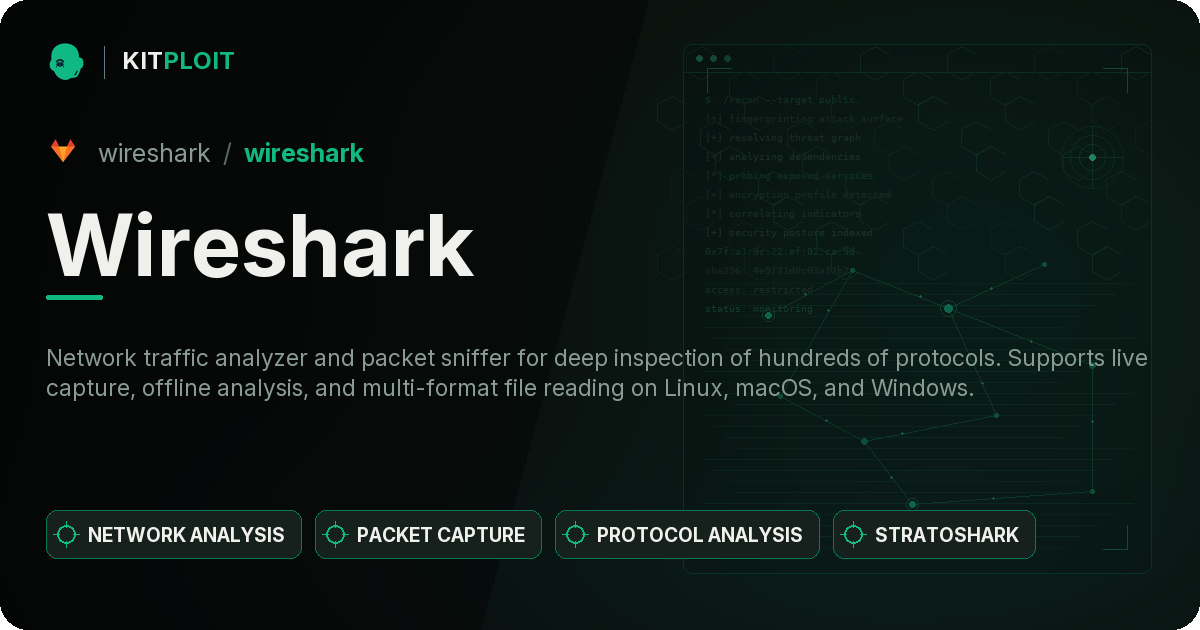
Downloaded a packet capture (.pcapng) file from malware-traffic-analysis.net which was an example of an attempted attack against a webserver using…

command-and-controldigital-forensicseducation+9
32 years ago
ptcpdump preview

ptcpdump

GitHubmozillazg/ptcpdump

eBPF-based packet analyzer that captures network traffic with automatic process, container, and Kubernetes pod metadata annotation, supporting…

cloud-securitycontainer-securitydigital-forensics+5
1.3k4 months ago
Network-Filesystem-Forensics preview

Network-Filesystem-Forensics

GitHubgilberto47831/network-filesystem-forensics

Reports on post-exploitation on honeypot exploiting vulnerable wu-ftpd (CVE-2001-0550)
digital-forensicsforensicsnetwork-forensics+2
4 years ago
Wireshark preview

Wireshark

GitLabwireshark/wireshark

Wireshark's official code repository. You can keep the releases coming by donating at https://wiresharkfoundation.org/donate/.
dns-analysisforensicsnetwork-forensics+3
1.6k8h 33m ago
PcapPlusPlus preview

PcapPlusPlus

GitHubseladb/pcapplusplus

Multiplatform C++ library for high-performance network packet capture, parsing, crafting, and analysis. Supports libpcap, DPDK, AF_XDP, PF_RING, and…
crawlerdns-analysisforensics+5
3.1k2 days ago
CyberScan preview

CyberScan

GitHubmedbenali/cyberscan

Open-source network forensics toolkit for packet analysis, port scanning, host discovery, and IP geolocation. Supports ARP, ICMP, TCP, UDP pings and…

information-gatheringnetwork-forensicsnetwork-mapping+3
4694 months ago
Previous123Next
