
Dshell
 usarmyresearchlab/dshell
Dshell is a network forensic analysis framework.
digital-forensicsdns-analysisforensics+3
usarmyresearchlab/dshellDshell is a network forensic analysis framework.
 google/grr
Remote live forensics and incident response framework with Python agent for collecting forensic data from endpoints, including memory, disk, and…
 benadia/an-integrated-wireless-network-forensic-analysis-framework
This framework combines a set of existing open source tools into an integrated package that automates the forensics investigation process. It is able…
 fox-it/dissect
Dissect is a digital forensics & incident response framework and toolset that allows you to quickly access and analyse forensic artefacts from…
 cyb3r-monk/rita-j
Implementation of RITA (Real Intelligence Threat Analytics) in Jupyter Notebook with improved scoring algorithm.
 omriher/captipper
Malicious HTTP traffic explorer
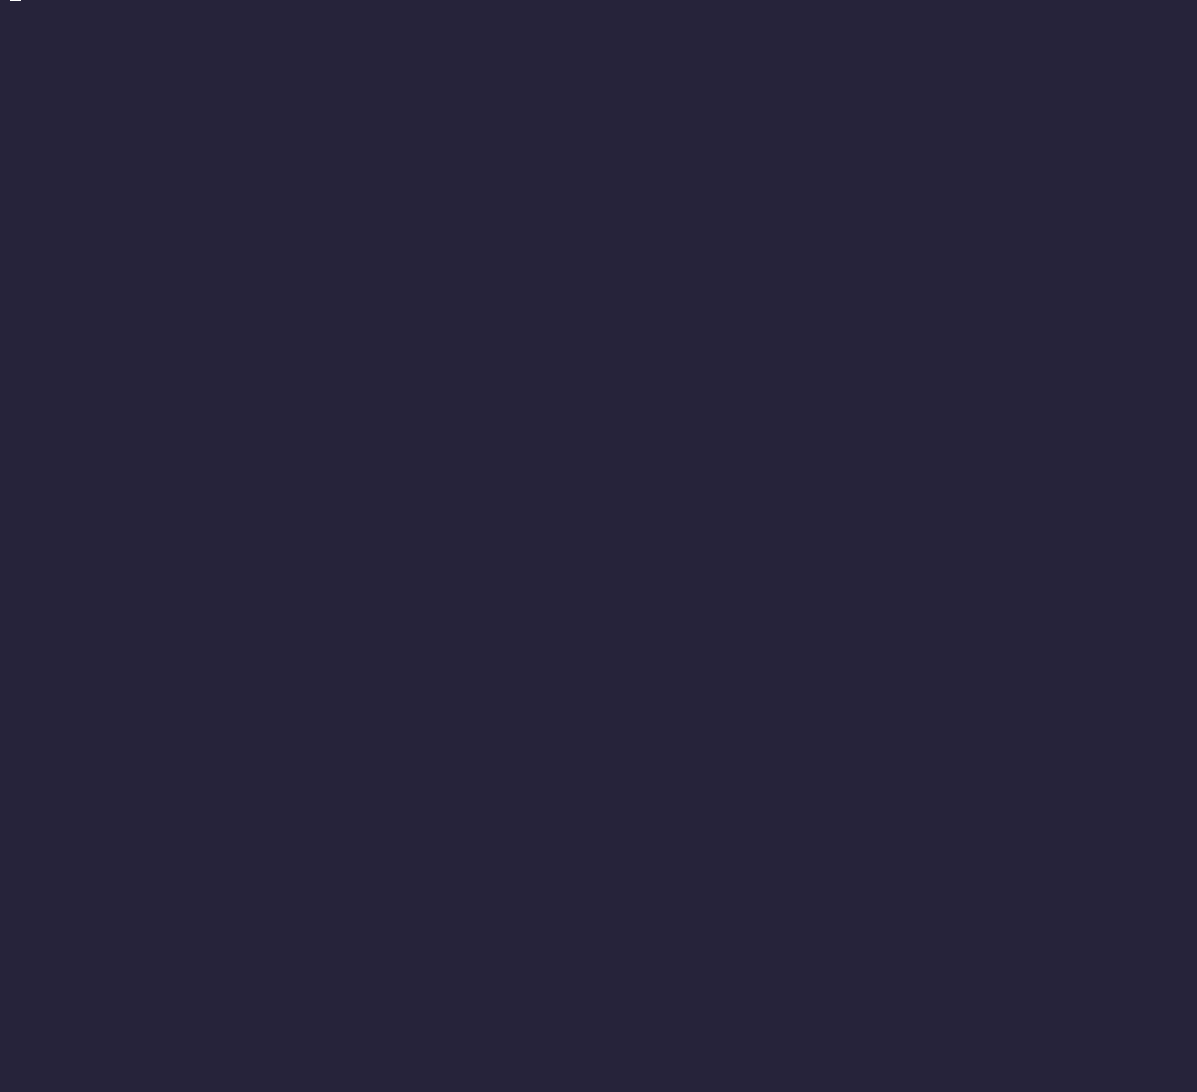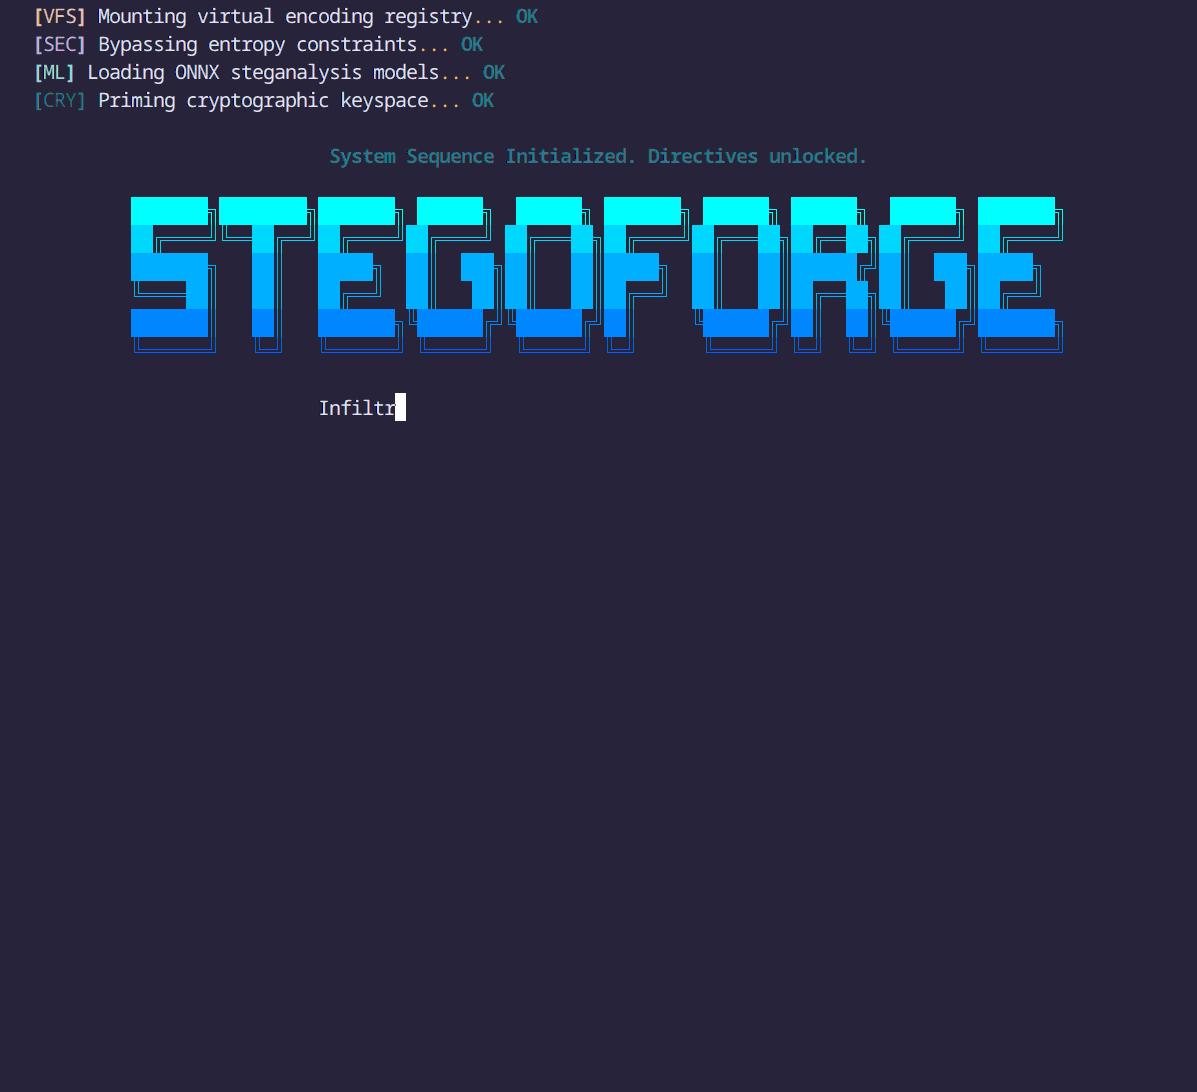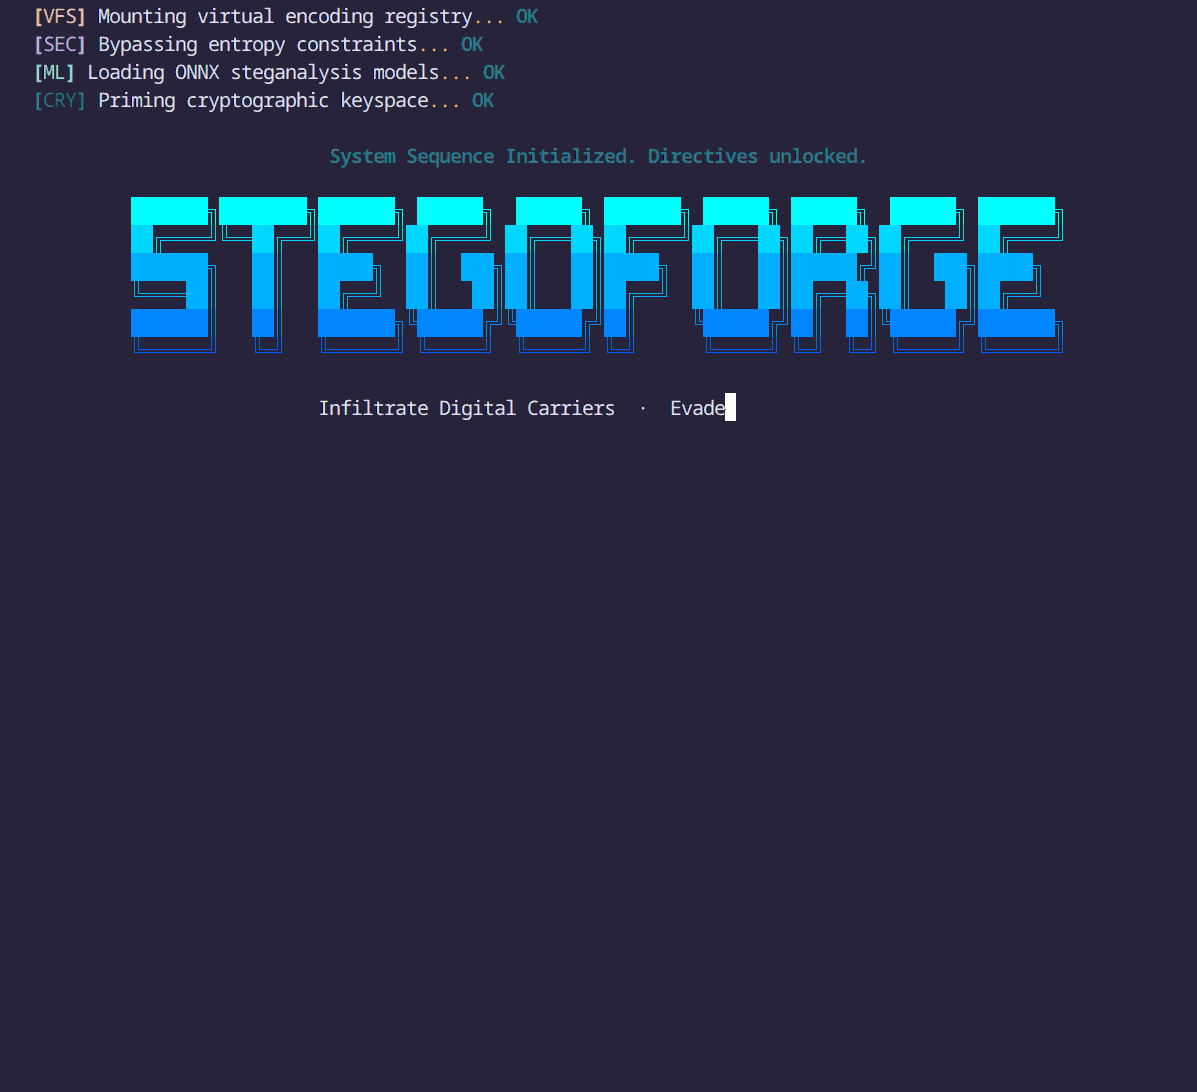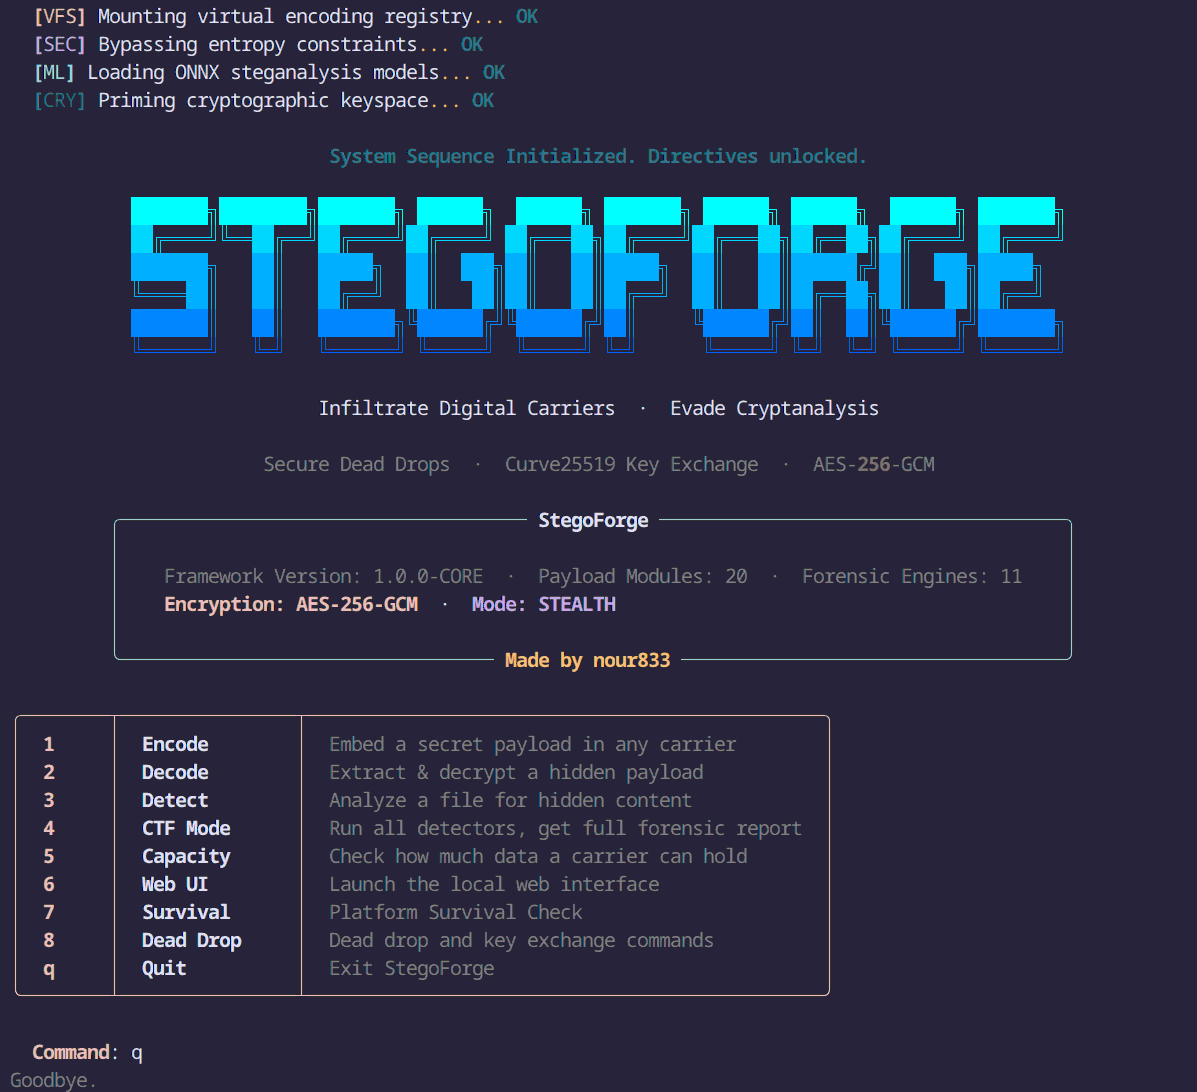 nour833/stegoforge
The ultimate steganography and digital forensics toolkit. Hide and extract data across images, audio, video, documents, and network packets, or run…