
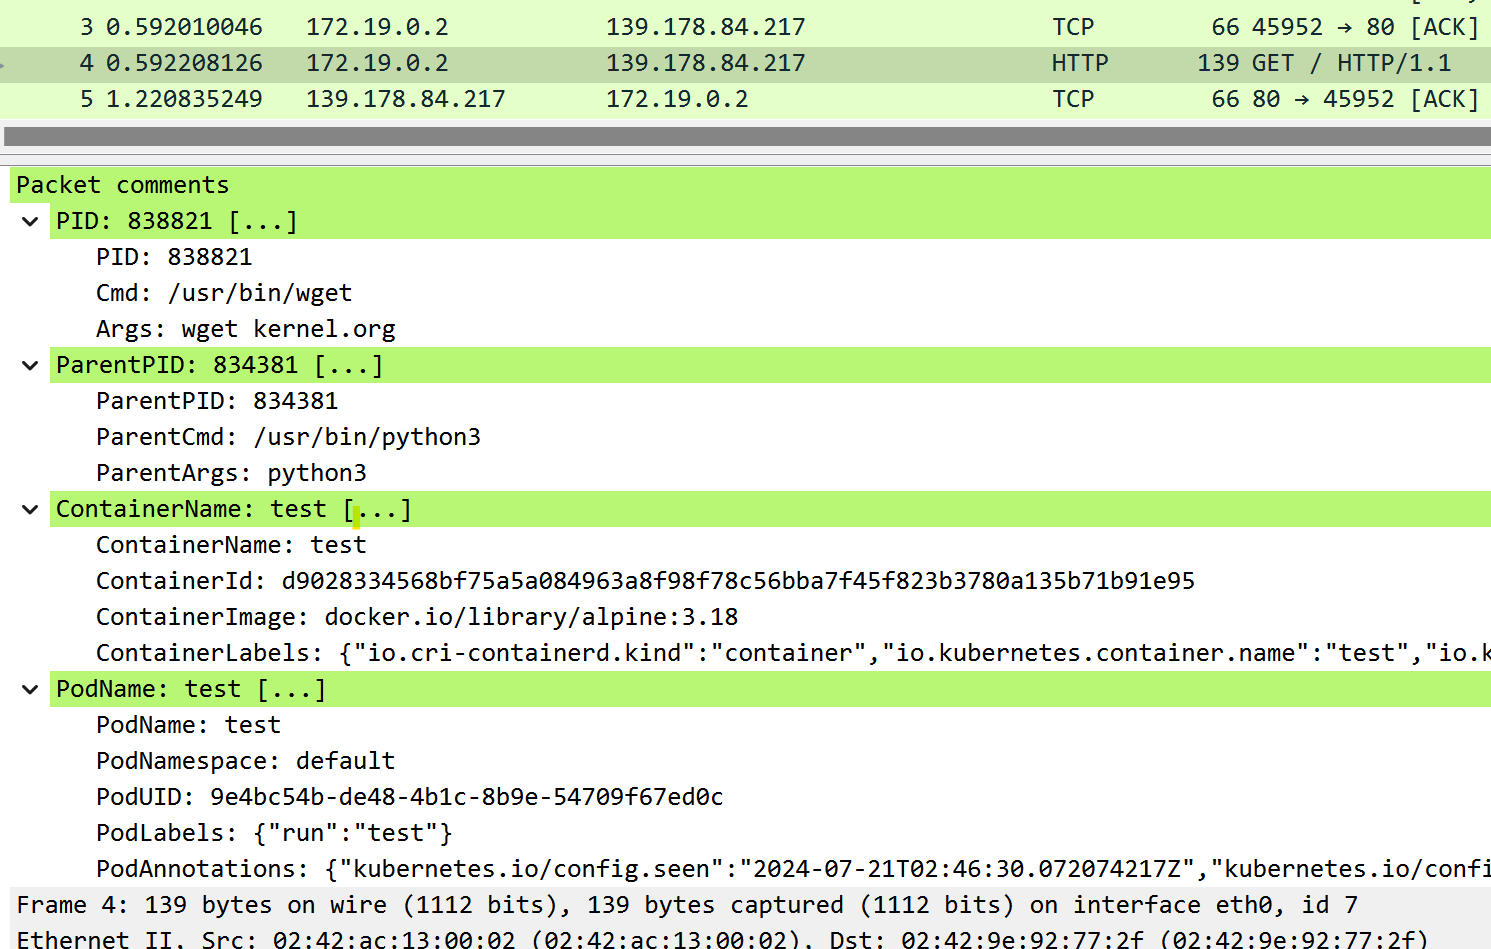
ptcpdump
 mozillazg/ptcpdump
eBPF-based packet analyzer that captures network traffic with automatic process, container, and Kubernetes pod metadata annotation, supporting…
cloud-securitycontainer-securitydigital-forensics+5
1.3k
mozillazg/ptcpdumpeBPF-based packet analyzer that captures network traffic with automatic process, container, and Kubernetes pod metadata annotation, supporting…
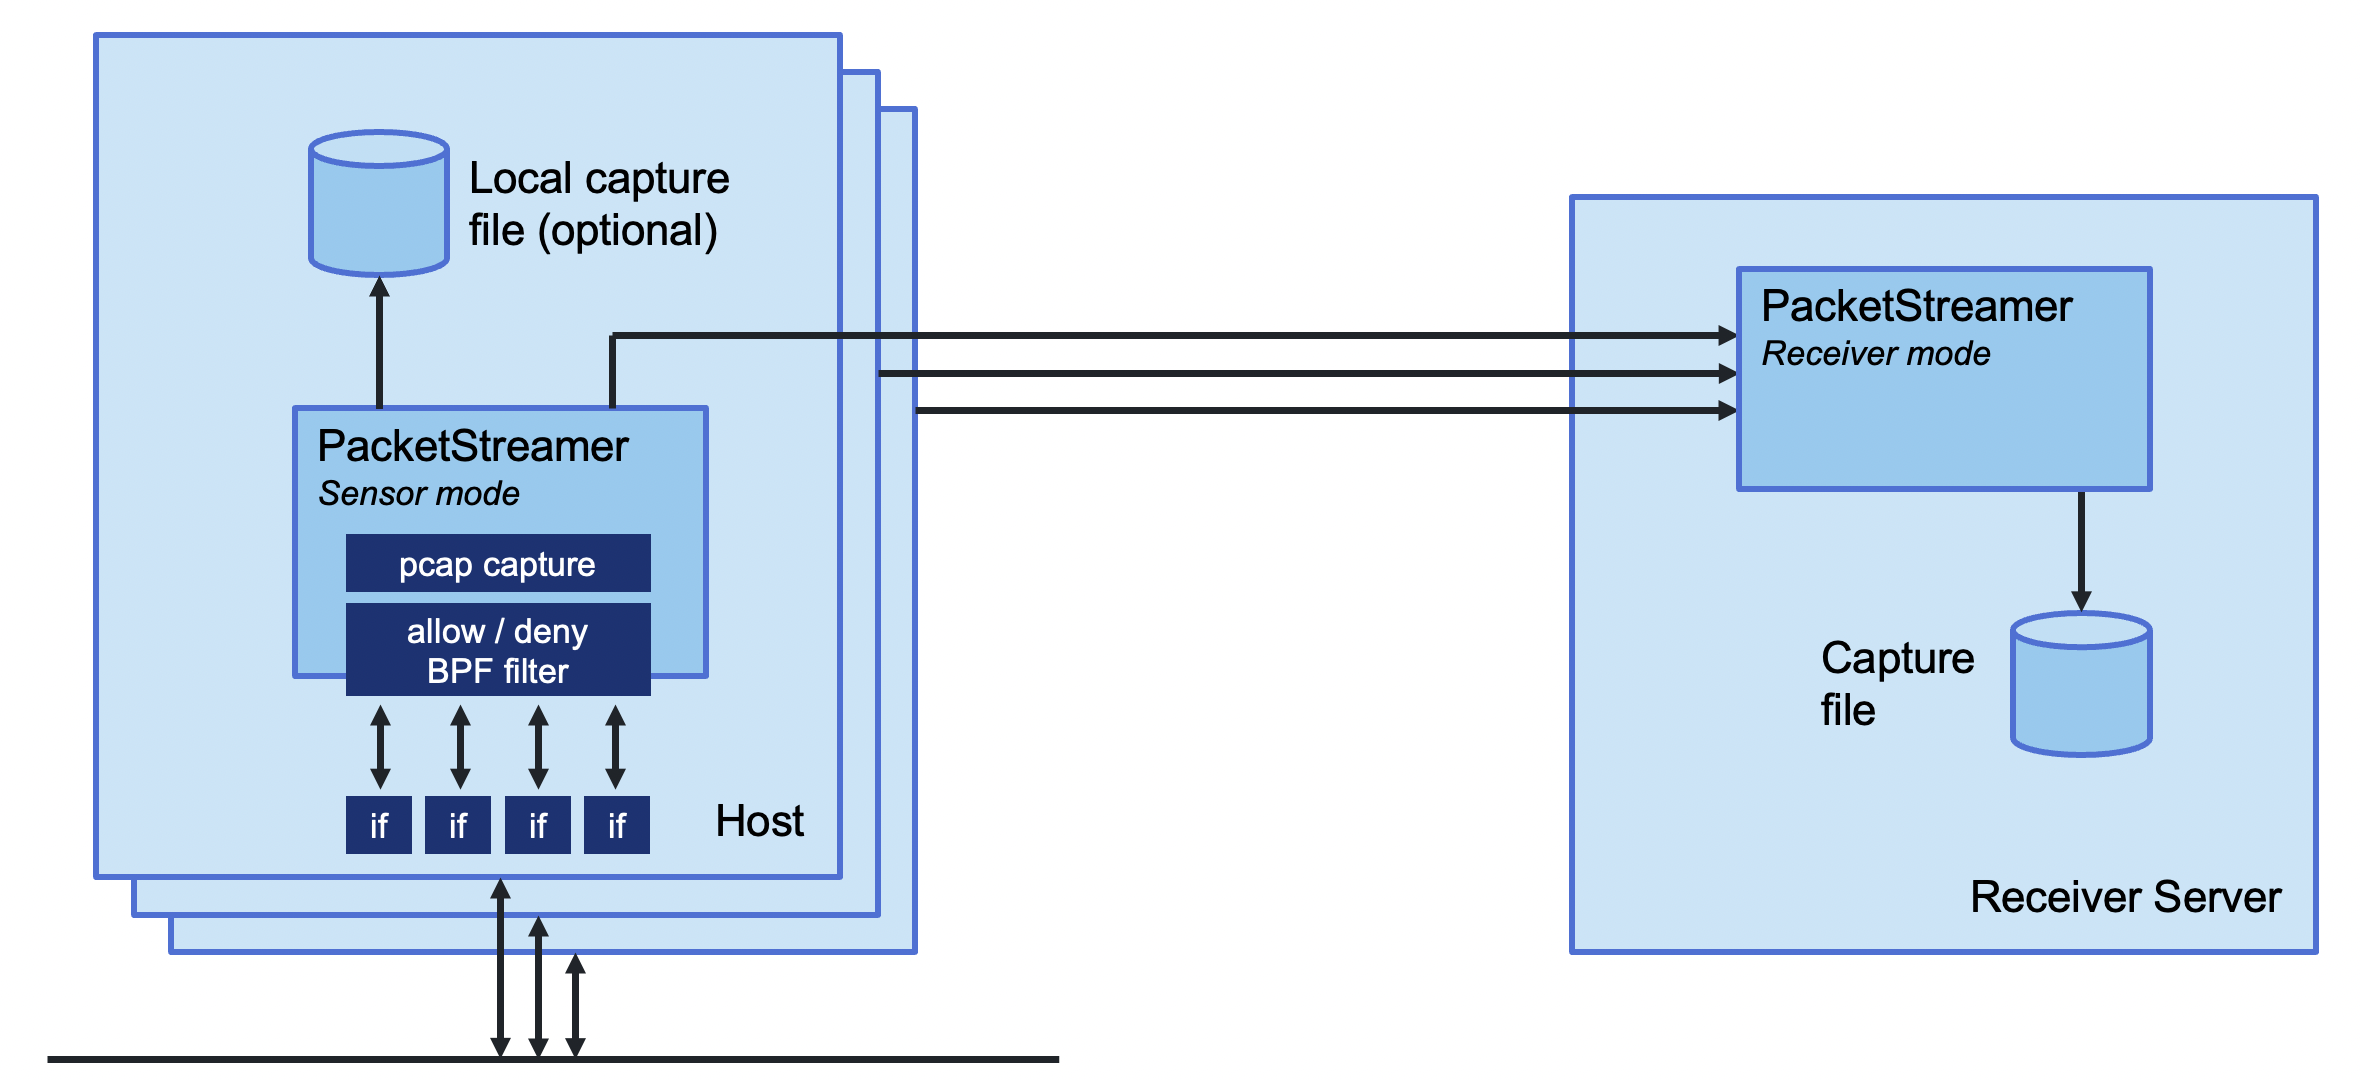 deepfence/packetstreamer
⭐ ⭐ Distributed tcpdump for cloud native environments ⭐ ⭐
 alzeaty1/security-writeups
CTF writeups and teaching scripts for web security, bug bounty techniques, and network forensics, with blank-value versions for active practice.
 anssi-fr/dfir4vsphere
Powershell module for VMWare vSphere forensics