

maltrail
 stamparm/maltrail
Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
anomaly-detectionanti-botdefensive-tools+11
8.6k
stamparm/maltrailReal-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
 zeek/zeek
Zeek is a powerful network analysis framework that is much different from the typical IDS you may know.
 wireshark/wireshark
Capture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…

 gamelinux/passivedns
A network sniffer that logs all DNS server replies for use in a passive DNS setup

 netsniff-ng/netsniff-ng
A Swiss army knife for your daily Linux network plumbing.
 seladb/pcapplusplus
Multiplatform C++ library for high-performance network packet capture, parsing, crafting, and analysis. Supports libpcap, DPDK, AF_XDP, PF_RING, and…
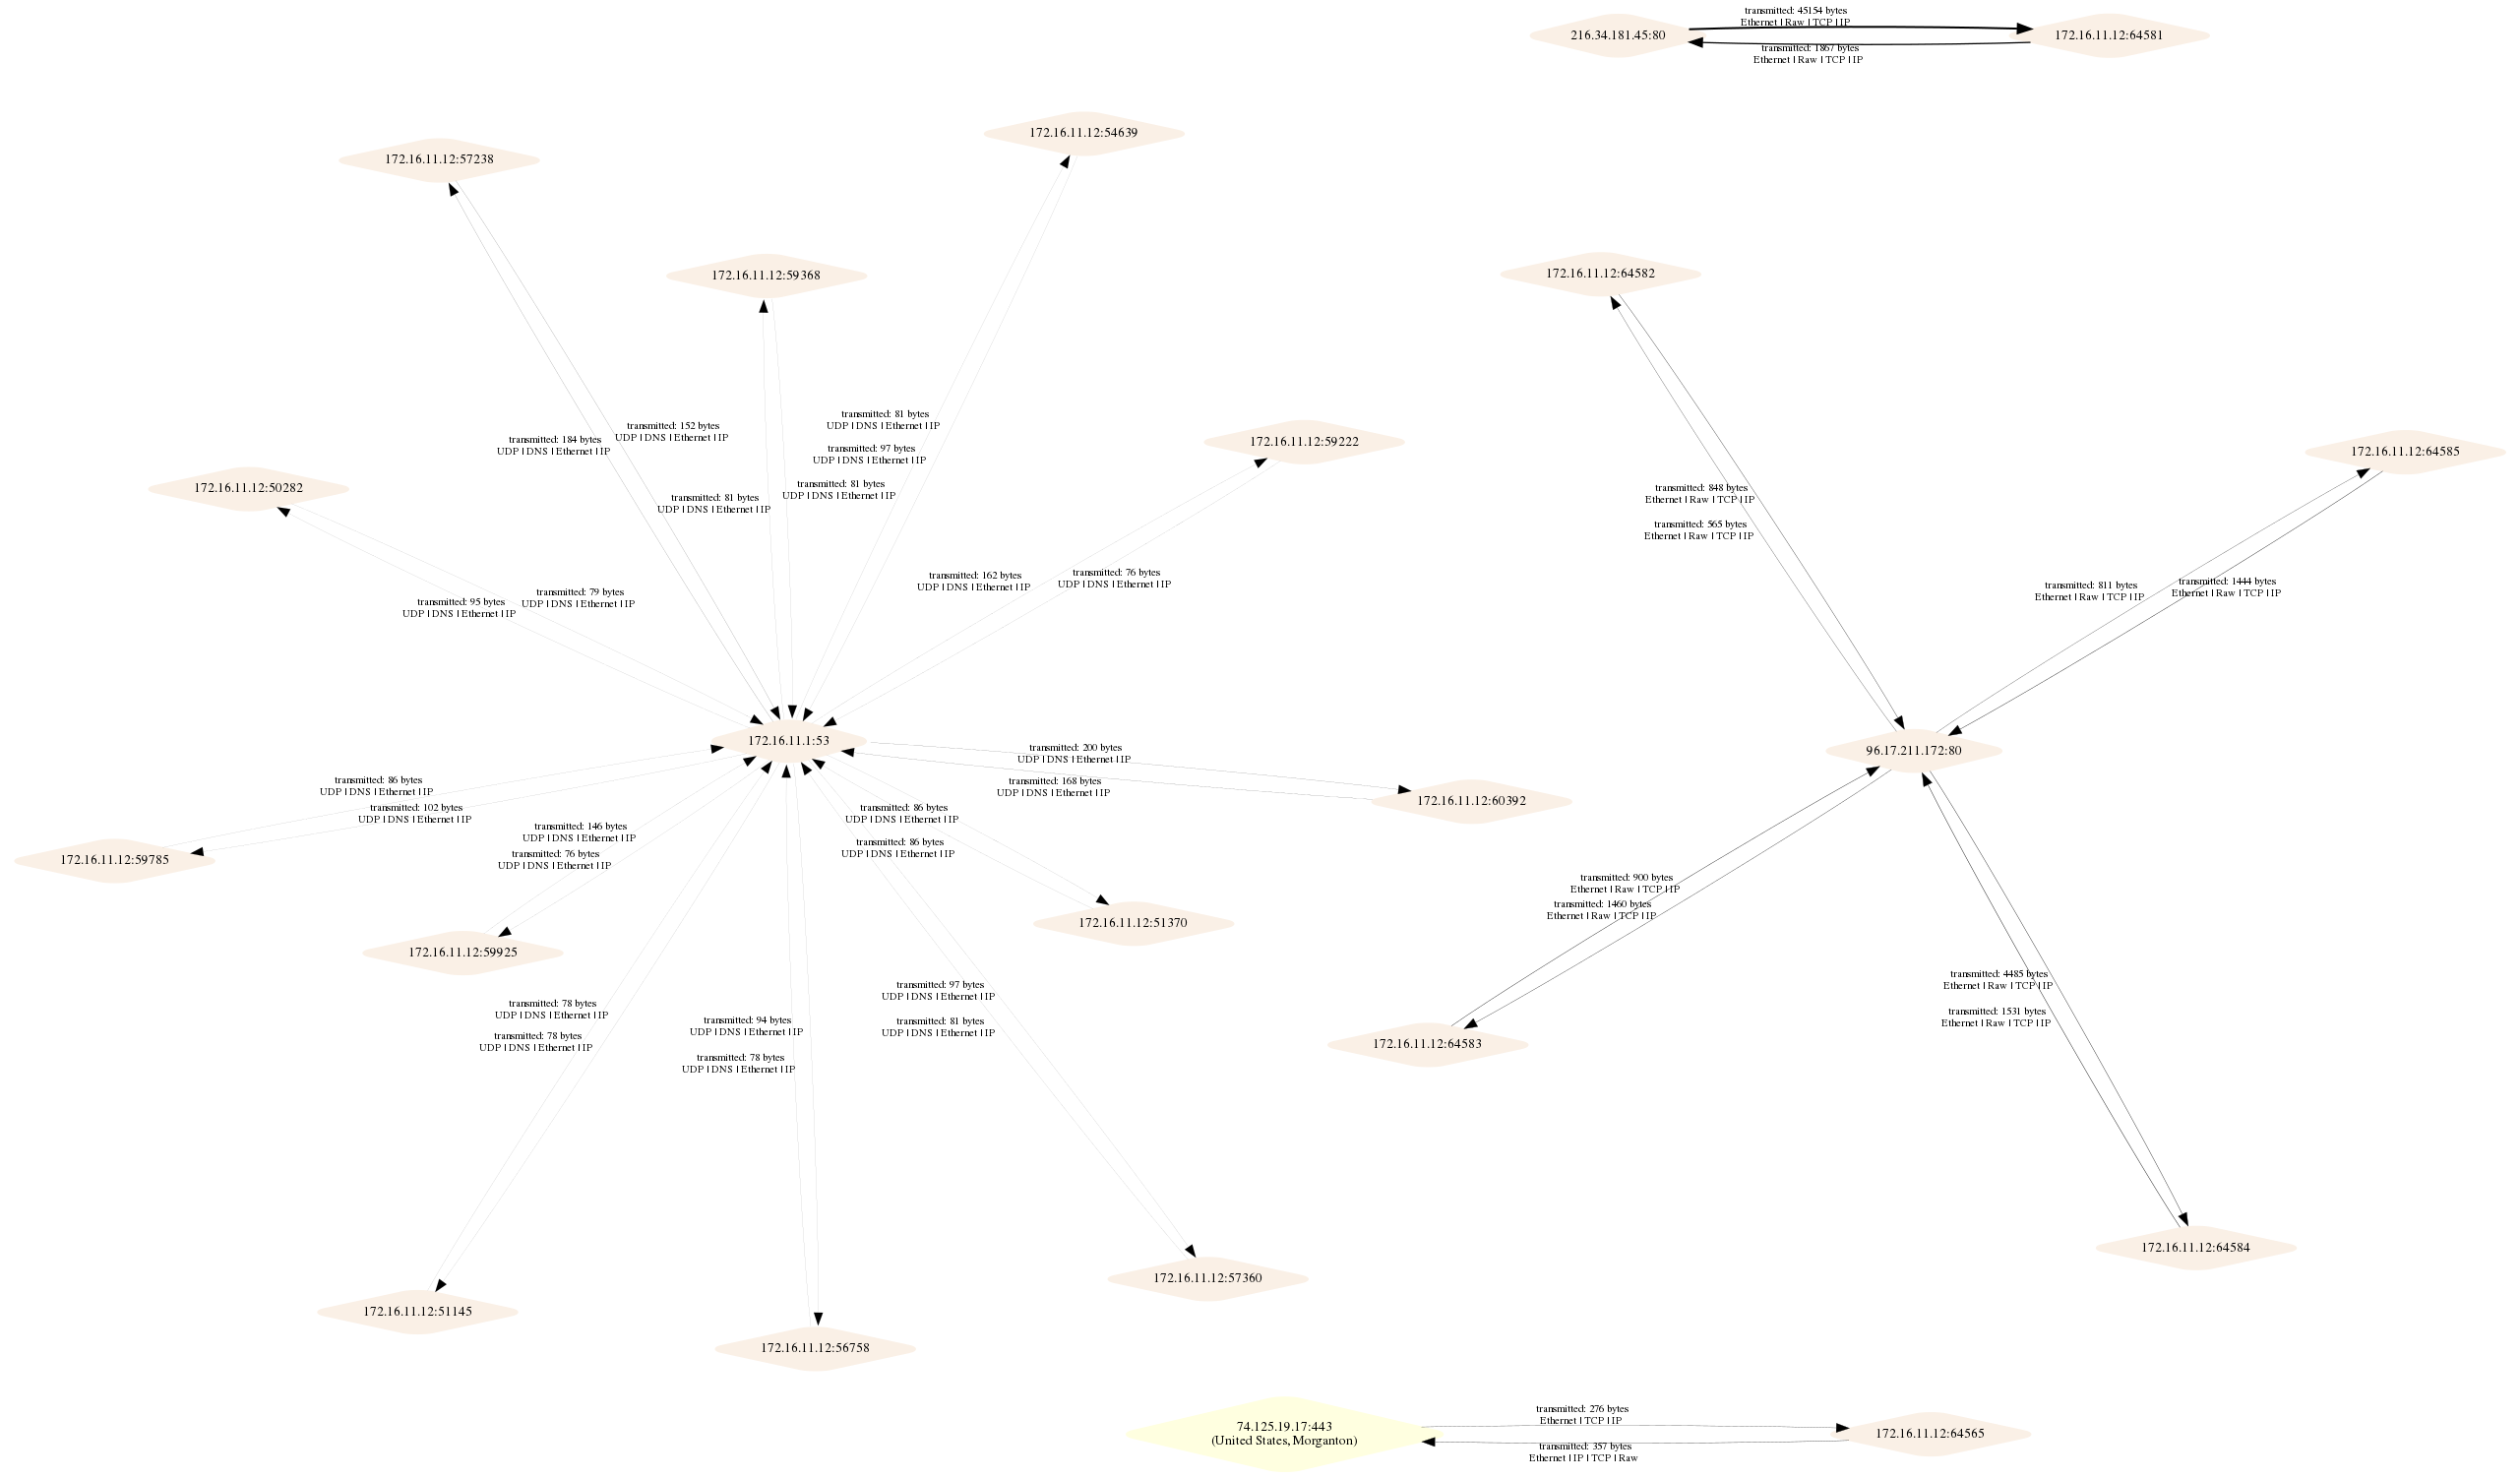 1ultimat3/pcapviz
Visualize network topologies and collect graph statistics based on pcap files
 secdev/scapy
Python-based interactive packet manipulation library for forging, decoding, sending, capturing, and analyzing network packets across a wide range of…
 prox0959/omnitriage
Zero-dependency, sub-second Windows live digital forensics & incident response (DFIR) triage engine for USB responders.
 simsong/bulk_extractor
This is the development tree. Production downloads are at:
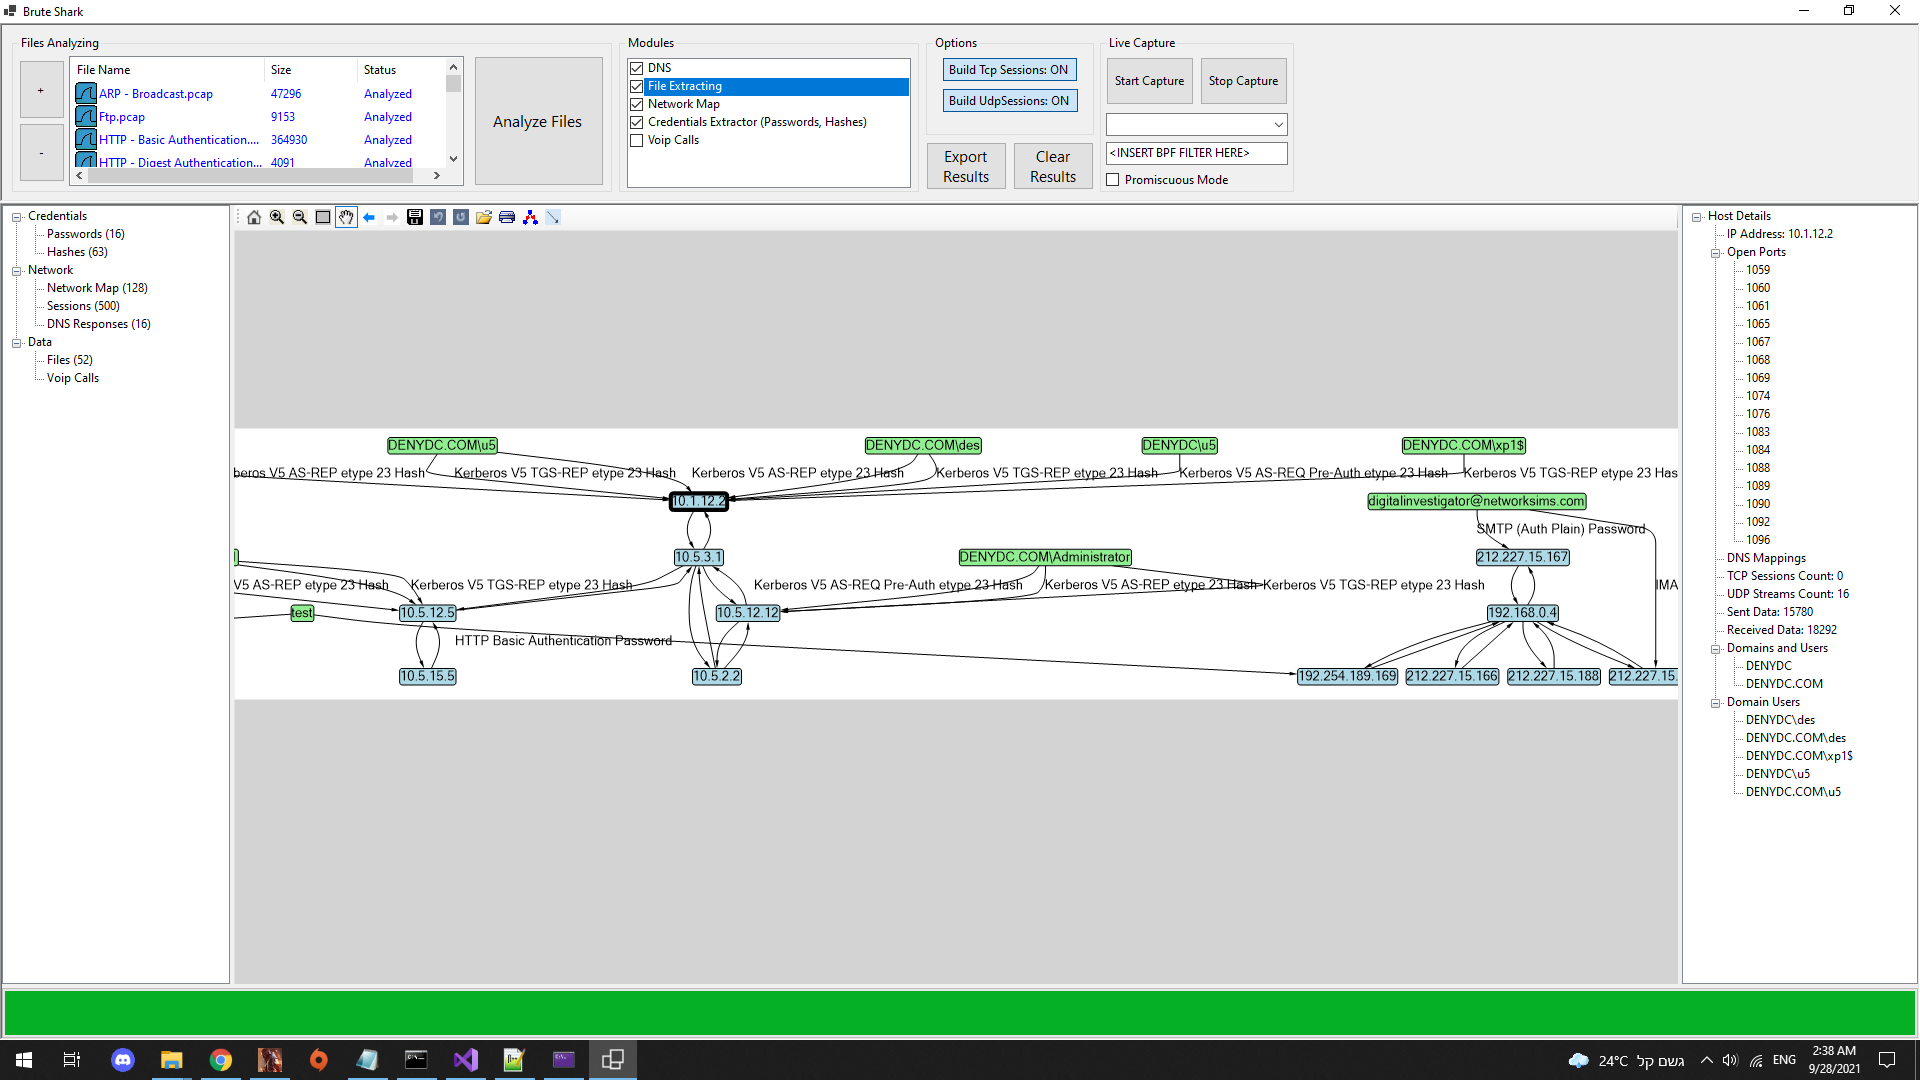
 foxio-llc/ja4
JA4+ is a suite of network fingerprinting standards
 emrekybs/bryobio
It was developed to speed up the processes of SOC Analysts during analysis
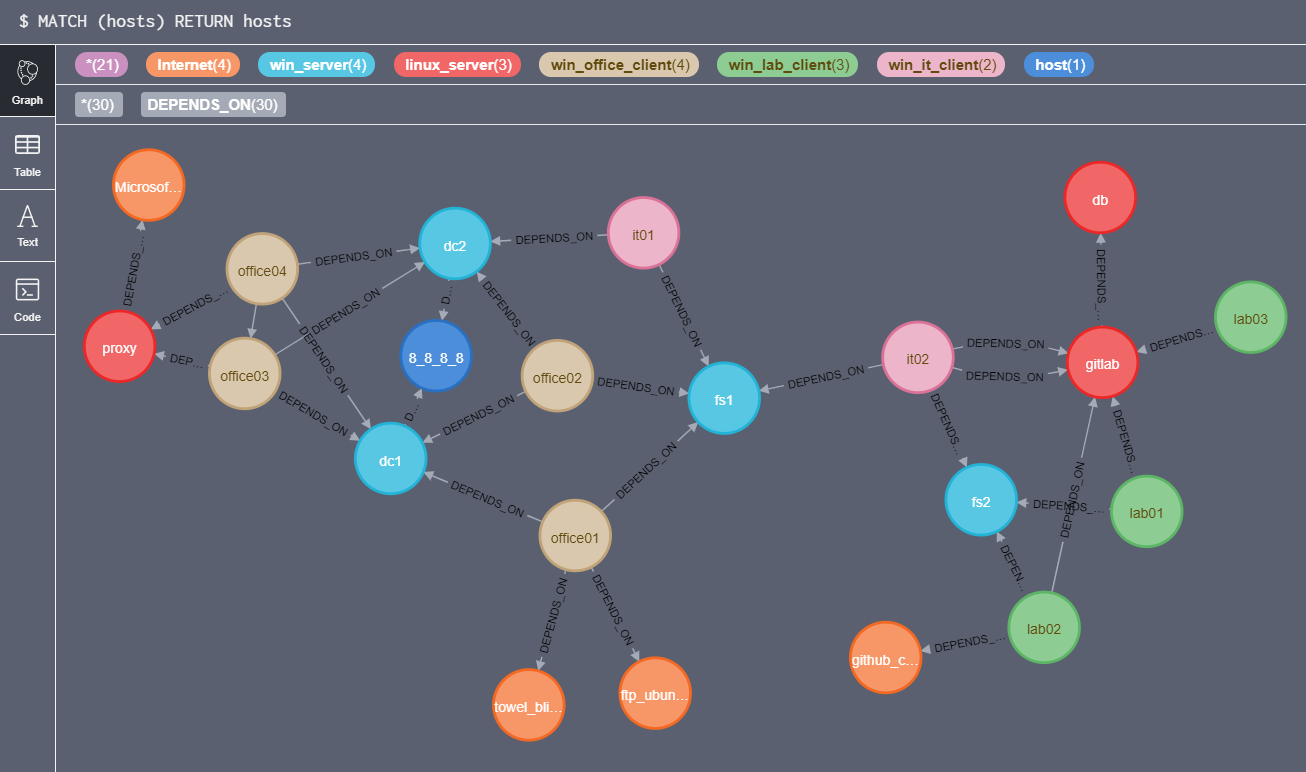 trinitor/netstat2neo4j
create cypher create statements for neo4j out of netstat files from multiple machines
 synacktiv/pcapan
A pcap capture analysis helper
 microlaser/dns_watchdog_windows2
PowerShell script that monitors Windows DNS traffic via pktmon to detect poisoning, spoofing, rogue resolver responses, and gateway MAC changes,…