

Dshell
 usarmyresearchlab/dshell
Dshell is a network forensic analysis framework.
digital-forensicsdns-analysisforensics+3
usarmyresearchlab/dshellDshell is a network forensic analysis framework.
 bert-janp/incident-response-powershell
PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…

 google/grr
Remote live forensics and incident response framework with Python agent for collecting forensic data from endpoints, including memory, disk, and…

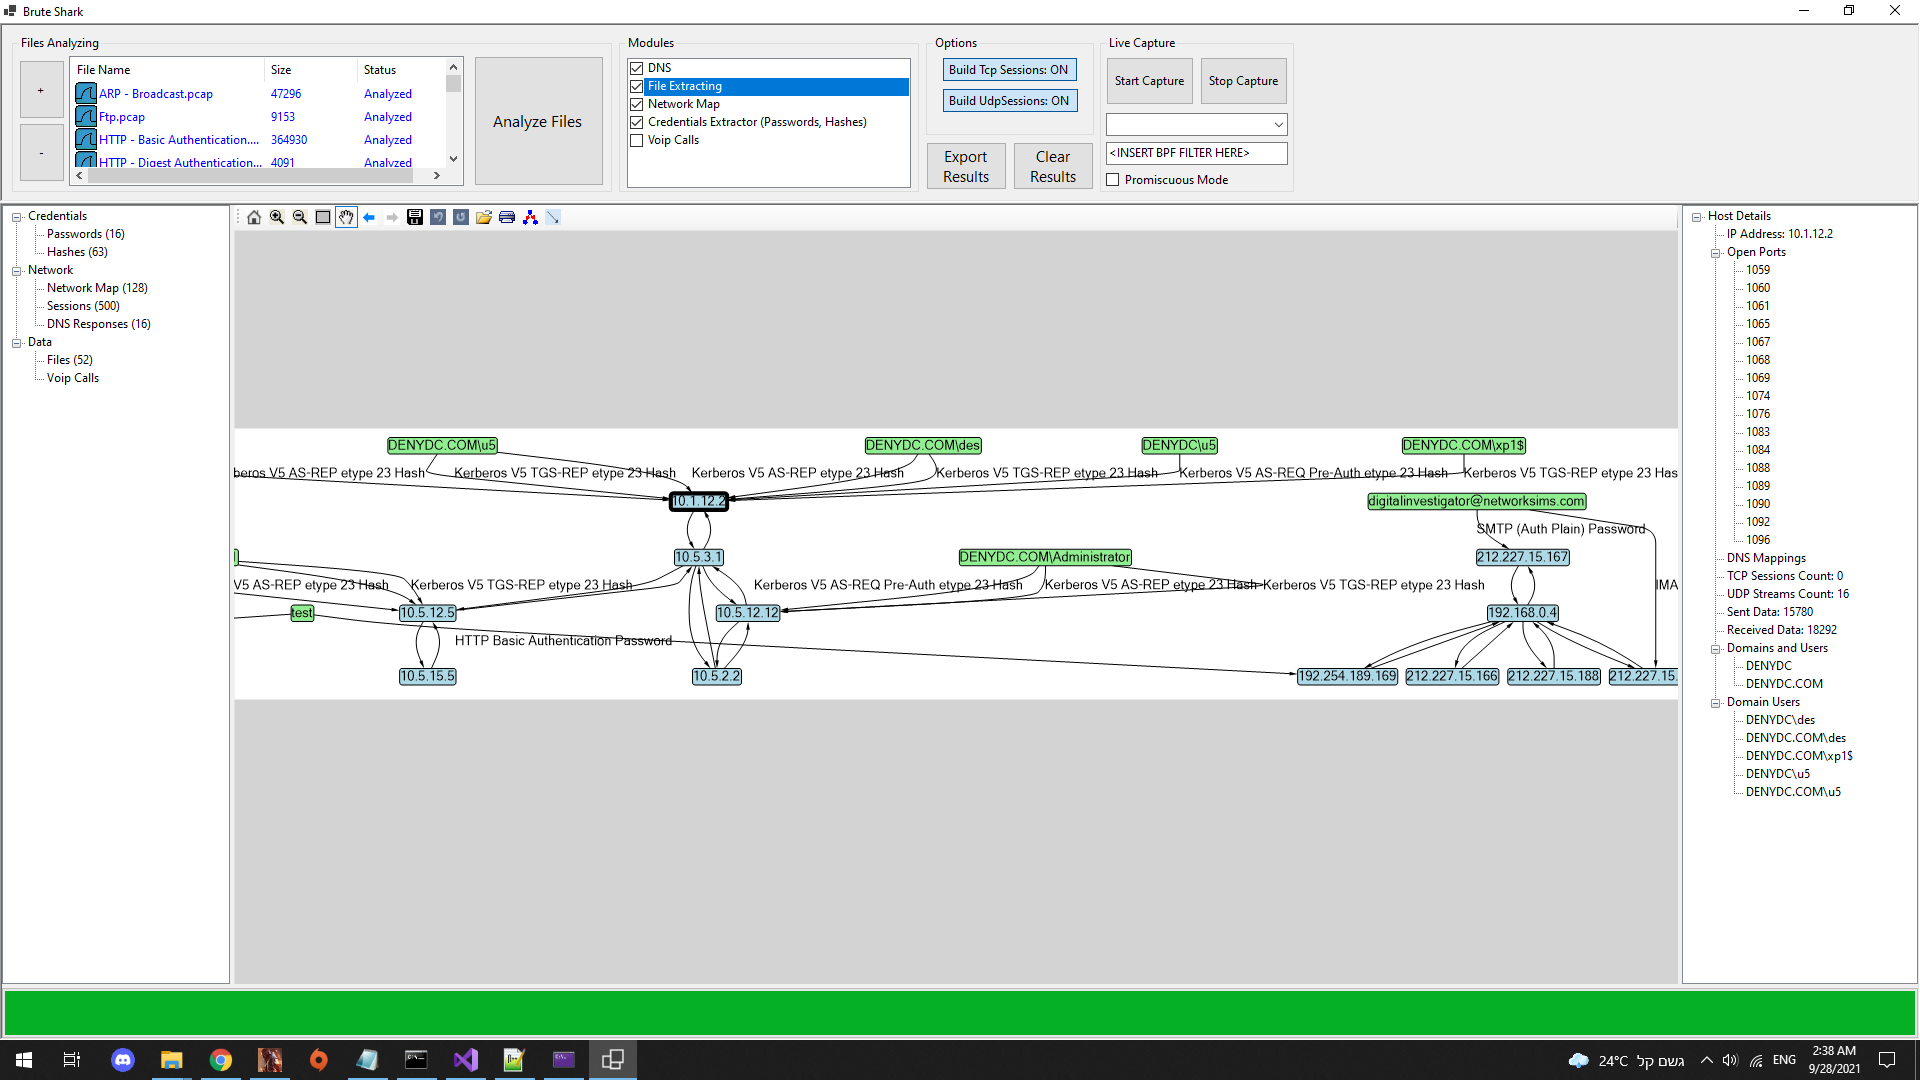
 simsong/bulk_extractor
This is the development tree. Production downloads are at:
 google/timesketch
Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…
 spectralzero/netscope
Offline-first network investigation and response platform for Windows. Turns a pcap or live capture into a full forensic verdict — attack story,…
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
 ntop/ntopng
Web-based Traffic and Cybersecurity Network Traffic Monitoring
 securityronin/memory-forensic
Walk any memory dump. Find what's hidden. Linux + Windows kernel forensics from a single static Rust binary — no Python required.
 fox-it/dissect
Dissect is a digital forensics & incident response framework and toolset that allows you to quickly access and analyse forensic artefacts from…
 cristianzsh/forensictools
Collection of forensic tools
 ic3-512/linux-root-kit
End-to-end simulation of a Python dependency confusion attack, sudo privilege escalation (CVE-2025-32463), and rootkit-based persistence - with full…
 vikwin/pcapfex
'Packet Capture Forensic Evidence eXtractor' is a tool that finds and extracts files from packet capture files
 cyberhatcoil/acf
Android Connections Forensics
 nicholasc03/dns-poisoning-triage-lab
Forensic triage of DNS cache poisoning in legacy hardware. Includes PCAP analysis of 839-byte unsolicited record injections, CVE-2025-40778 mapping,…