Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
79 results
wireshark preview

wireshark

GitHubwireshark/wireshark

Capture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…

bluetooth-securitydata-exfiltrationdigital-forensics+11
10.1k
8h 47m ago
Dshell preview

Dshell

GitHubusarmyresearchlab/dshell

Dshell is a network forensic analysis framework.

digital-forensicsdns-analysisforensics+3
5.5k2 years ago
Loki preview

Loki

GitHubneo23x0/loki

IOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…

anomaly-detectiondigital-forensicsdisk-forensics+11
3.8k9 months ago
ja4 preview

ja4

GitHubfoxio-llc/ja4

JA4+ is a suite of network fingerprinting standards

dns-analysisencryption-decryption-toolsfingerprint-spoofing+9
2.2k22 days ago
Android-Projector-C2-Malware preview

Android-Projector-C2-Malware

GitHubkavan00/android-projector-c2-malware

Breakdown of a c2-network of chinese beamers - SilentSDK-Analysis

android-securitycommand-and-controldigital-forensics+9
3025 days ago
PcapPlusPlus preview

PcapPlusPlus

GitHubseladb/pcapplusplus

Multiplatform C++ library for high-performance network packet capture, parsing, crafting, and analysis. Supports libpcap, DPDK, AF_XDP, PF_RING, and…

crawlerdns-analysisforensics+5
3.2k1 day ago
dns_watchdog_windows2 preview

dns_watchdog_windows2

GitHubmicrolaser/dns_watchdog_windows2

PowerShell script that monitors Windows DNS traffic via pktmon to detect poisoning, spoofing, rogue resolver responses, and gateway MAC changes,…

anomaly-detectiondefensive-toolsdns-analysis+5
1 month ago
scapy preview

scapy

GitHubsecdev/scapy

Python-based interactive packet manipulation library for forging, decoding, sending, capturing, and analyzing network packets across a wide range of…

bluetooth-securitycryptographydata-exfiltration+23
12.7k11h 3m ago
CAPEv2 preview

CAPEv2

GitHubkevoreilly/capev2

Malware Configuration And Payload Extraction

debuggersdynamic-analysis-sandboxingeducation+6
3.6k9h 42m ago
passivedns preview

passivedns

GitHubgamelinux/passivedns

A network sniffer that logs all DNS server replies for use in a passive DNS setup
dns-analysisforensicsincident-response+3
1.7k10 days ago
so-crates preview

so-crates

GitHubdougburks/so-crates

SO-CRATES: Security Onion Containerized Rapid Analysis of Threats, Evil, and Sus!

container-securitydigital-forensicseducation+8
6242 days ago
DFIR-LABS preview

DFIR-LABS

GitHubazr43lkn1ght/dfir-labs

Hands-on DFIR challenges covering digital forensics, incident response, malware analysis, and threat hunting with CTF-style flags and real-world…
ctfdigital-forensicsdisk-forensics+6
6601 month ago
termshark preview

termshark

GitHubgcla/termshark

A terminal UI for tshark, inspired by Wireshark
network-forensicsnetwork-securitypacket-sniffing-analysis+1
10.0k3 years ago
netsniff-ng preview

netsniff-ng

GitHubnetsniff-ng/netsniff-ng

A Swiss army knife for your daily Linux network plumbing.
network-forensicsnetwork-mappingnetwork-security+4
1.4k1 year ago
BruteShark preview

BruteShark

GitHubodedshimon/bruteshark

Network Analysis Tool

dns-analysisforensicshash-analysis+4
3.4k4 years ago
fatt preview

fatt

GitHub0x4d31/fatt

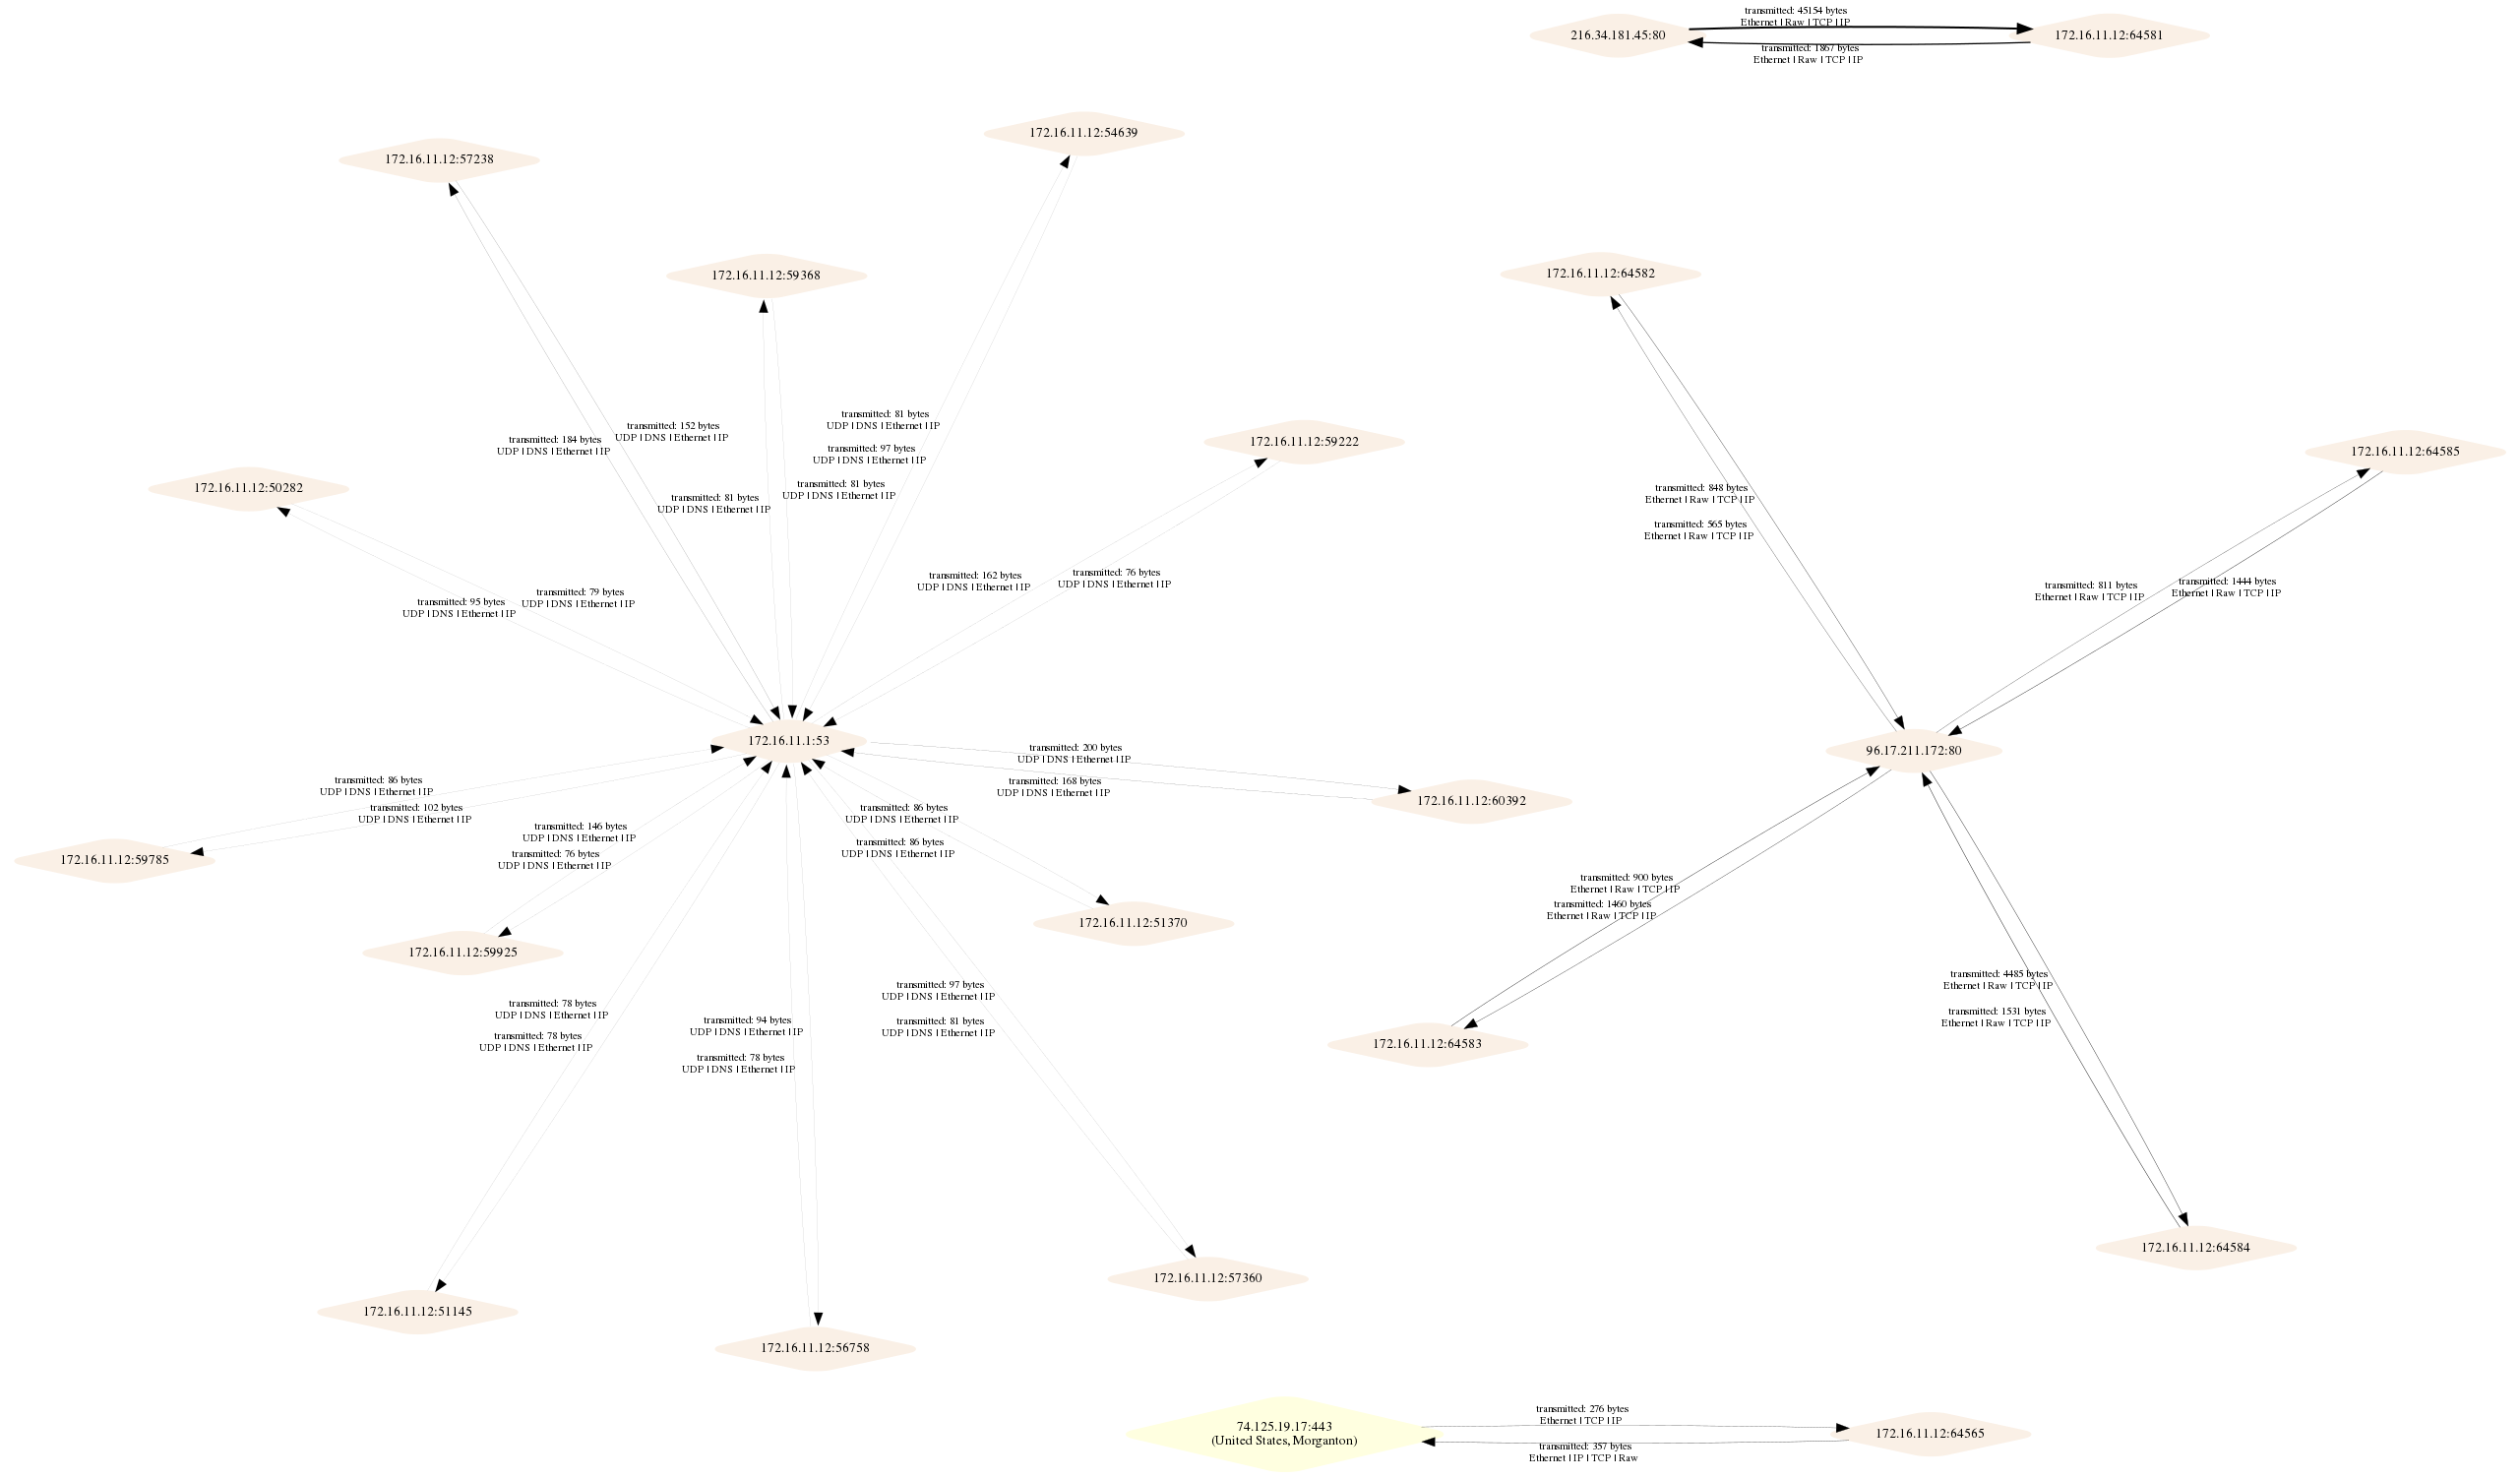
FATT /fingerprintAllTheThings - a pyshark based script for extracting network metadata and fingerprints from pcap files and live network traffic
network-forensicspacket-sniffing-analysisthreat-intelligence
6854 years ago
PcapViz preview

PcapViz

GitHub1ultimat3/pcapviz

Visualize network topologies and collect graph statistics based on pcap files

information-gatheringnetwork-forensicsnetwork-mapping+1
3603 years ago
arkime preview

arkime

GitHubarkime/arkime

Arkime is an open source, large scale, full packet capturing, indexing, and database system.

defensive-toolsdigital-forensicsforensics+7
7.6k1h 41m ago
Previous12345Next