
passivedns
 gamelinux/passivedns
A network sniffer that logs all DNS server replies for use in a passive DNS setup
dns-analysisforensicsincident-response+3
gamelinux/passivednsA network sniffer that logs all DNS server replies for use in a passive DNS setup
 emrekybs/bryobio
It was developed to speed up the processes of SOC Analysts during analysis
 mspicer/pcapinator
A tool for processing a lot of pcaps using tshark
 z4l4mi/ipgeo
Extracts IP addresses from pcap/pcapng network traffic files and generates CSV reports with geolocation, ISP, and organizational details for each IP.
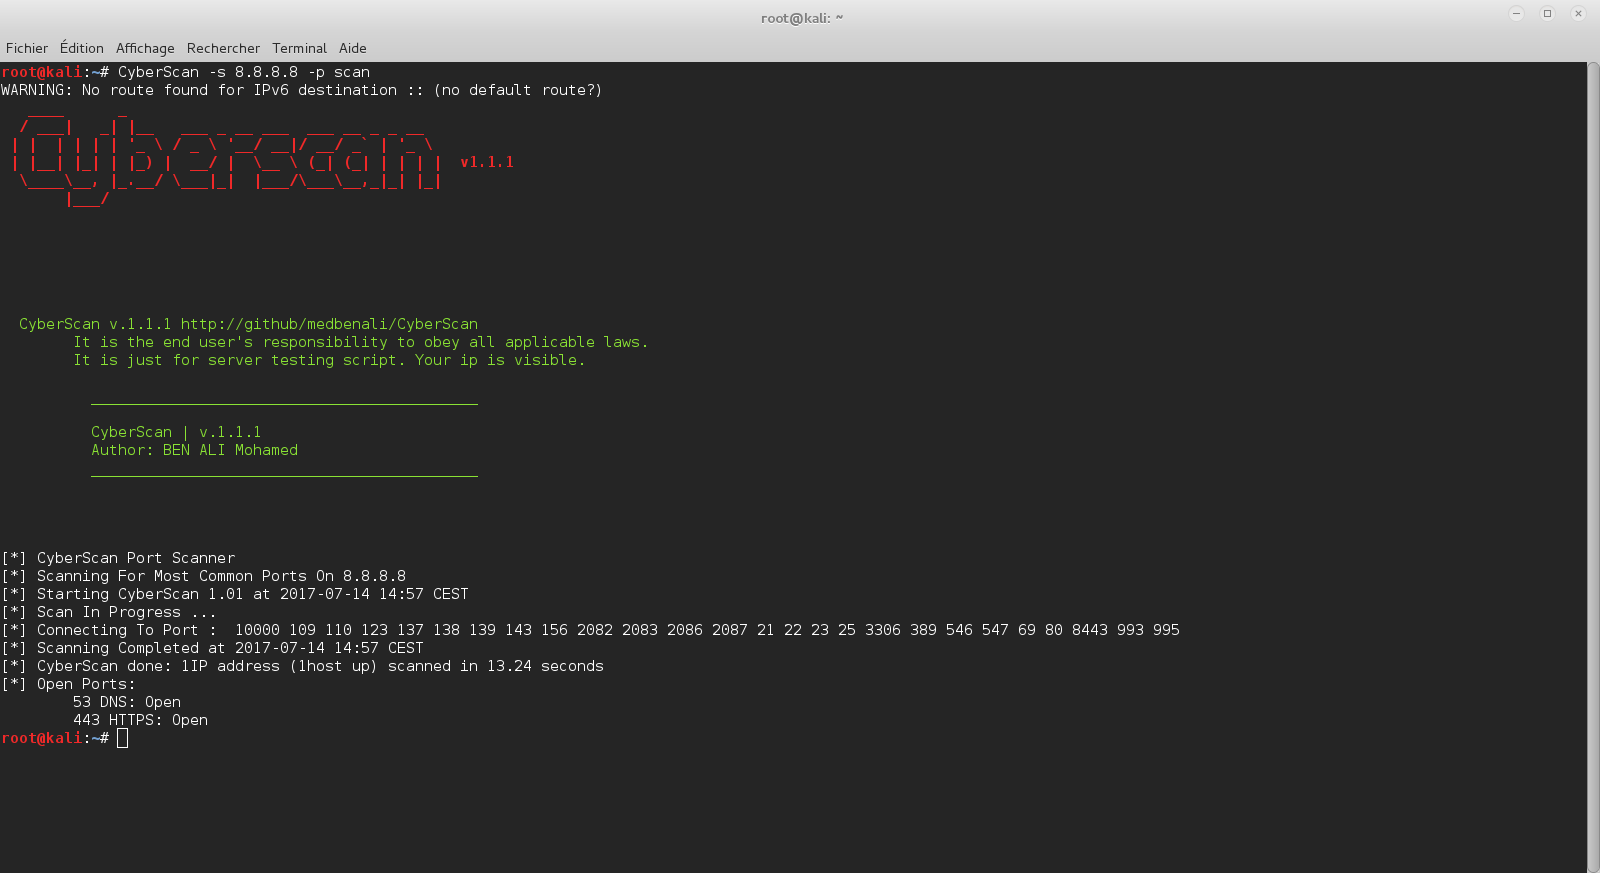 medbenali/cyberscan
Open-source network forensics toolkit for packet analysis, port scanning, host discovery, and IP geolocation. Supports ARP, ICMP, TCP, UDP pings and…
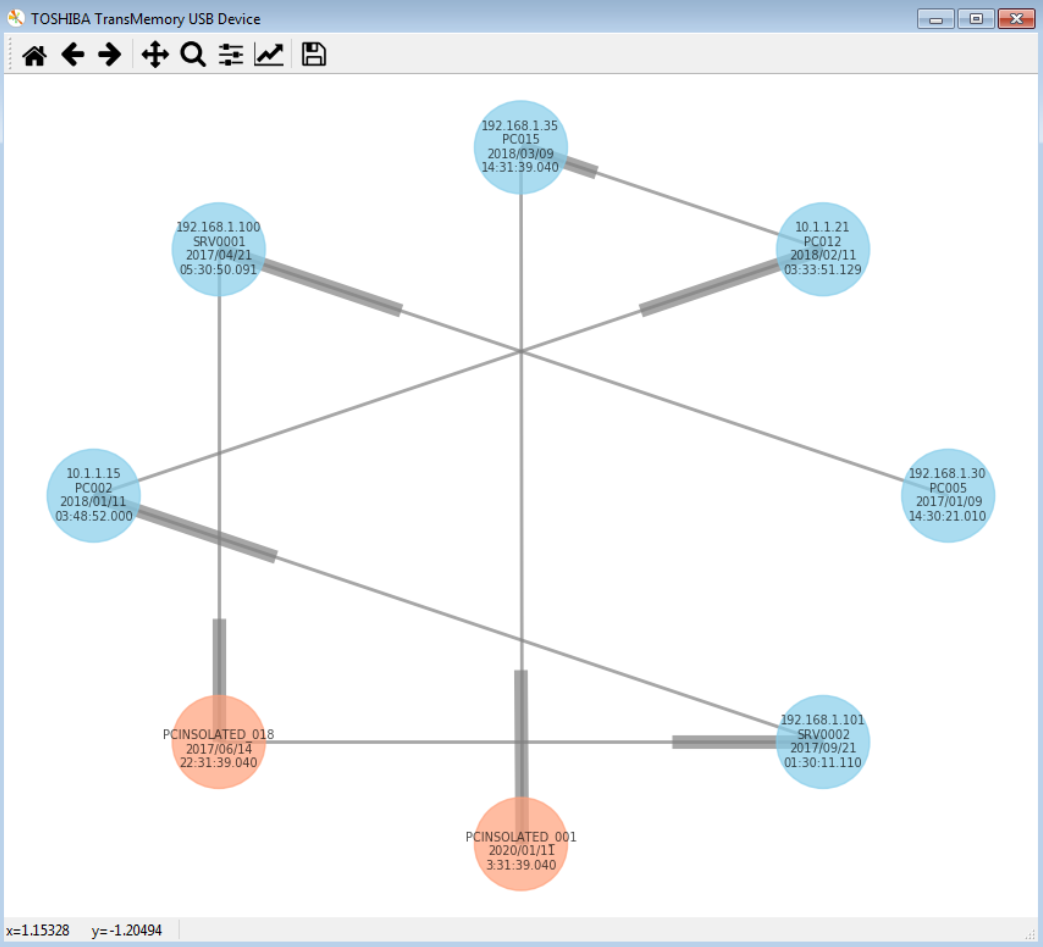 telefonica/hiddennetworks-python
USB device connection forensics tool that traces physical device-to-computer relationships across local and domain networks, generating visual graphs…
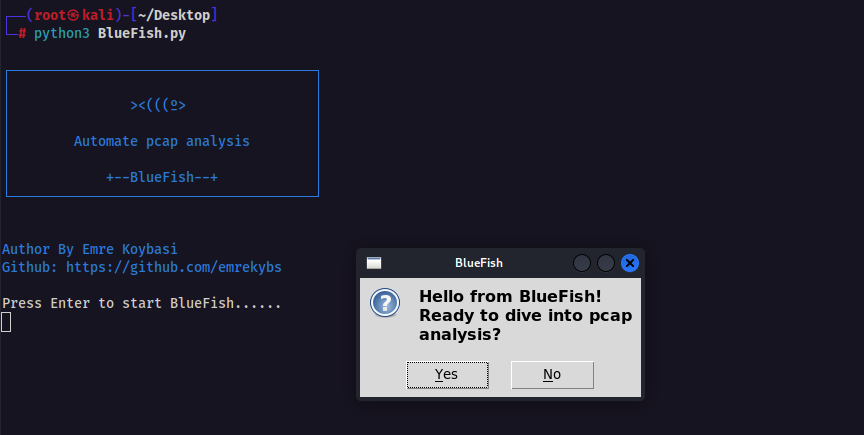 emrekybs/bluefish
Automation tool designed to simplify the analysis of PCAP (Packet Capture) files