
ipa-medit
 sterrasec/ipa-medit
Memory modification tool for re-signed ipa supports iOS apps running on iPhone and Apple Silicon Mac without jailbreaking.
binary-analysisios-securitymemory-forensics+3
211
sterrasec/ipa-meditMemory modification tool for re-signed ipa supports iOS apps running on iPhone and Apple Silicon Mac without jailbreaking.
 sensepost/objection
Frida-powered runtime mobile exploration toolkit for assessing iOS and Android app security. Bypass SSL pinning, dump keychains, manipulate heap…
 sterrasec/apk-medit
memory search and patch tool on debuggable apk without root & ndk
 lntrx/cve-2021-28663
Proof-of-concept exploit for CVE-2021-28663, a design flaw in the Mali GPU Android kernel driver enabling arbitrary read via memory alias and…
 quarkslab/cve-2020-0069_poc
Proof-of-concept exploit for CVE-2020-0069 on Mediatek Android devices, enabling kernel memory read/write and syscall hooking for privilege…
 thomasking2014/slides
Curated collection of security conference slide decks covering Android rooting, kernel exploitation, browser memory corruption, JIT mitigations, and…
 vichhka-git/renef-skills
Agent Skill for operating renef.io — Android ARM64 dynamic instrumentation: hook native/Java, patch memory, trace syscalls, bypass SSL pinning/root…
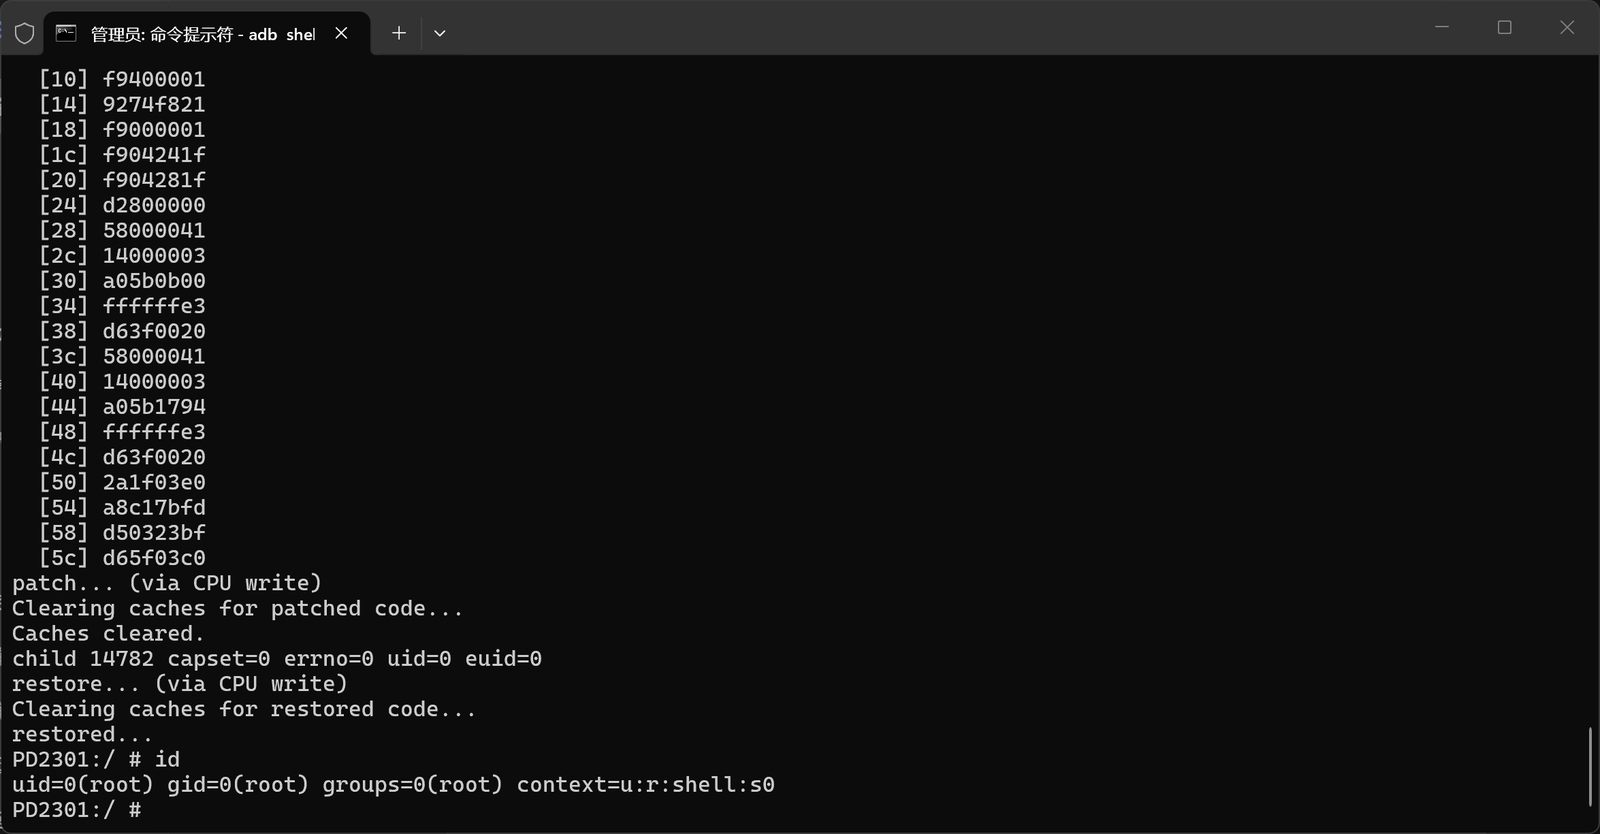 qingizi7/cve-2025-21479_iqooneo8
Local root exploit for CVE-2025-21479 (Adreno KGSL) on iQOO Neo8 (SM8475) - physical memory r/w, disables SELinux, spawns root shell
 hiikezoe/libfb_mem_exploit
CVE-2013-2596 memory corruption exploit for Android devices, targeting a kernel vulnerability to achieve privilege escalation.
 fi01/libmsm_cameraconfig_exploit
C exploit for CVE-2013-2595 targeting a kernel memory corruption in Qualcomm MSM camera driver on Android devices, enabling local privilege…
 diabl0w/cve-2022-22057_sm-f926u
Qualcomm kgsl driver exploit (CVE-2022-22057) for Samsung Galaxy devices achieving arbitrary kernel memory read/write, SELinux bypass, and temporary…
 betalphafai/cve-2015-6637
Proof-of-concept exploit for Android privilege escalation vulnerability CVE-2015-6637, demonstrating memory corruption to gain elevated privileges.
 satirush/cve-2025-14174-poc
Proof-of-Concept exploit for CVE-2025-14174 (EUVD-2025-203113) - Memory corruption in ANGLE allowing out-of-bounds access and RCE in web browsers.…
 lsw29475/cve-2020-0022
Exploit for CVE-2020-0022, an Android Bluetooth RCE vulnerability. Provides proof-of-concept code for testing and understanding the memory corruption…
 woaphone/cve-2021-28664-poc
PoC skeleton for CVE-2021-28664, a Mali kbase GPU driver use-after-free, demonstrating a kernel arbitrary physical memory read/write primitive on…
 hasan-khalil/cve-2020-6514
Exploit for CVE-2020-6514 targeting WebRTC SCTP memory corruption in Android applications. Uses Frida to hook native functions and alter SCTP packets…
 jordelmir/elysium-vanguard-sentinel-audit
The official Sentinel Edition v7.11 - Hypervisor Detection & Kernel Memory Audit Suite for Honor Magic V2. Investigating CVE-2025-38352 and EL2 RKP…
 ravss/bluetooth-crash-cve-2017-0785
Exploit script for CVE-2017-0785 that crashes the Bluetooth module on Android 4.0+ devices by sending crafted SDP search requests, causing…