
CVE-2015-6612
 secmob/cve-2015-6612
Proof-of-concept exploit for Android CVE-2015-6612, demonstrating a privilege escalation vulnerability with a working PoC for security research and…
android-securitybinary-exploitationexploitation+3
23
secmob/cve-2015-6612Proof-of-concept exploit for Android CVE-2015-6612, demonstrating a privilege escalation vulnerability with a working PoC for security research and…
 isecpartners/introspy-ios
Security profiling for blackbox iOS
 a2333c/dfroot
Android root tool for Samsung Galaxy S25 Ultra (SM-S938B) that chains DirtyFrag CVE-2026-43284 and CVE-2026-43499 to gain root automatically at boot…
 httptoolkit/frida-interception-and-unpinning
Frida scripts to rewrite mobile applications at runtime to directly MitM all HTTPS traffic
 nst/spyphone
This project shows the kind of data a rogue iPhone application can collect.
 sc1341/instagramosint
An Instagram Open Source Intelligence Tool - Archive
 iswaxan/jailedcement
Simple iOS bootlooper using CVE-2022-46689. Desguised as onlyfans
 m0bilesecurity/rms-runtime-mobile-security
Runtime Mobile Security (RMS) 📱🔥 - is a powerful web interface that helps you to manipulate Android and iOS Apps at Runtime
 hackerhouse-opensource/exploits
exploits and proof-of-concept vulnerability demonstration files from the team at Hacker House
 pwnaccelerator/stagefright-cve-2015-3864
PoC - Binary patches for CVE-2015-3864 (NOT for production, use at your own risk)
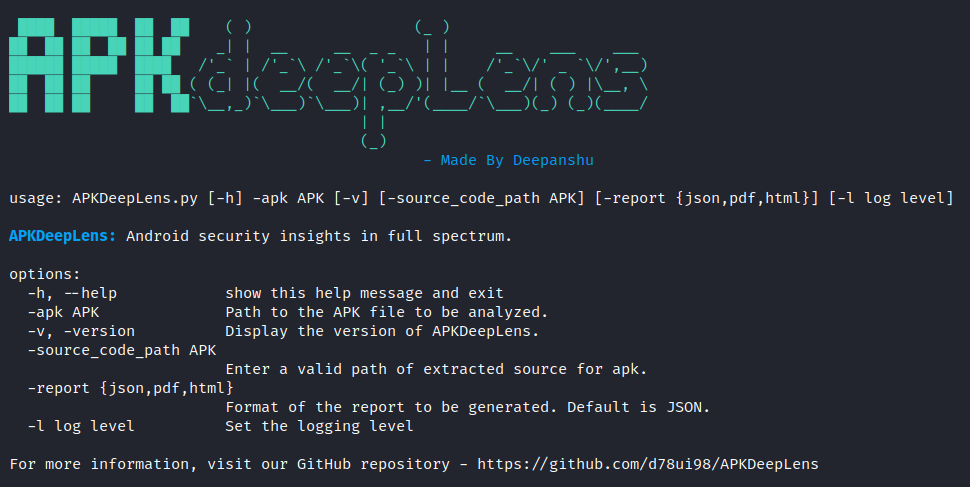 d78ui98/apkdeeplens
Android security insights in full spectrum.
 georgiaw/smartphone-pentest-framework
Repository for the Smartphone Pentest Framework (SPF)
 ejfkdev/ddc
Android DEX → Java decompiler in Rust, built for speed — full apps in seconds, queries in milliseconds. Progressive analysis, javac-verified output,…
 owasp/igoat-swift
OWASP iGoat (Swift) - A Damn Vulnerable Swift Application for iOS
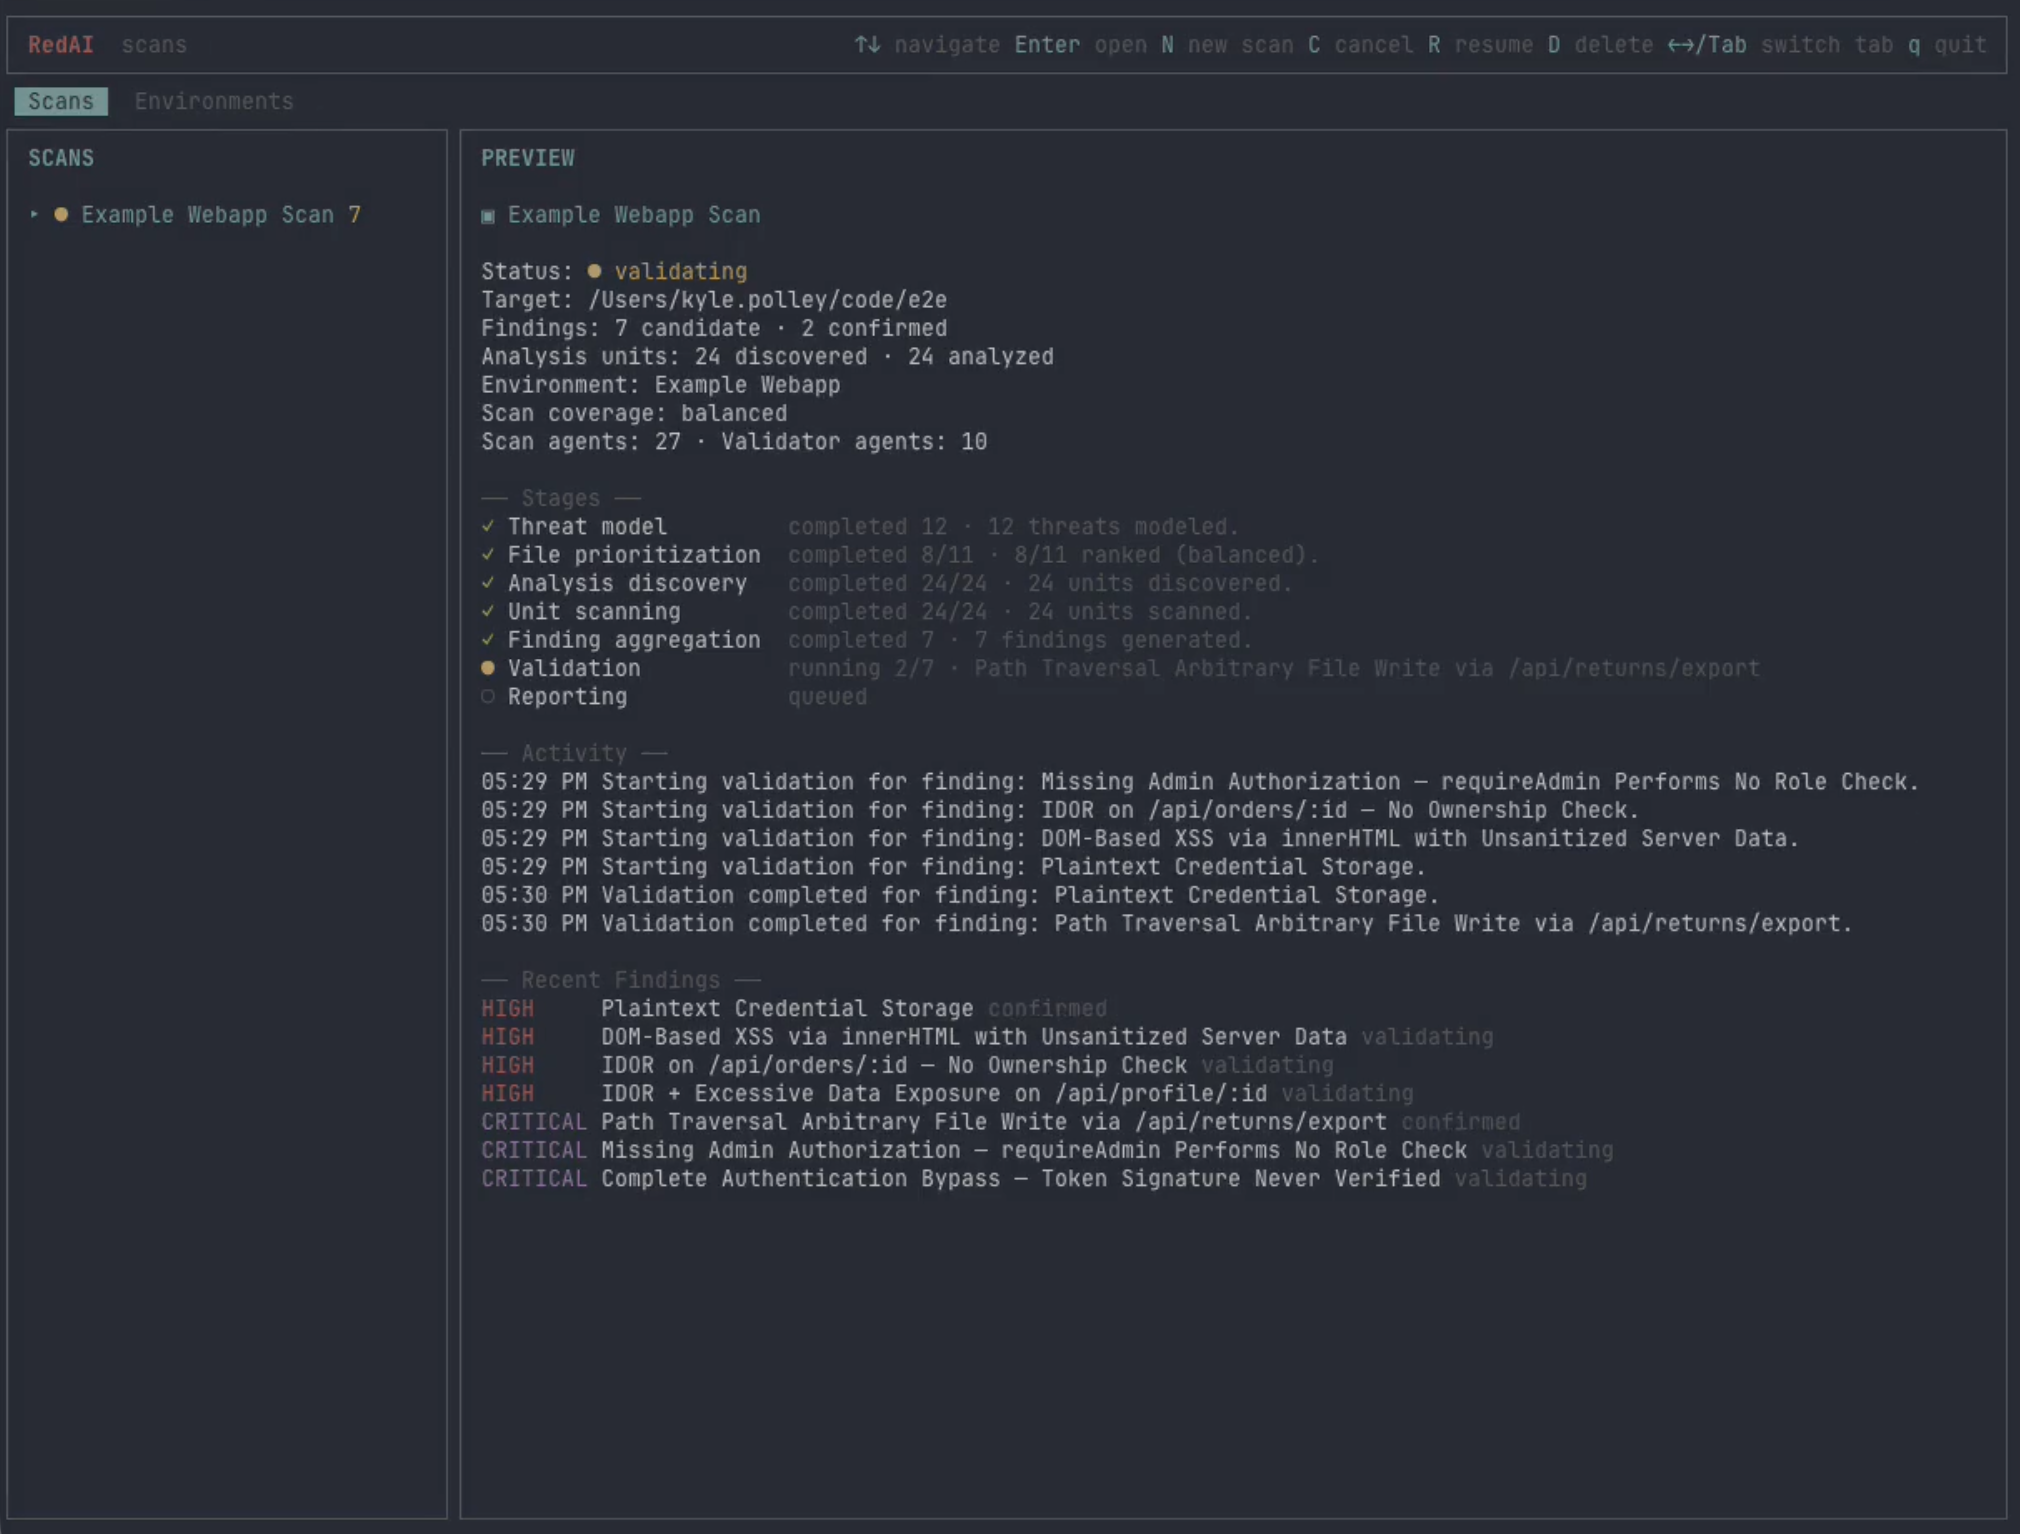 kpolley/redai
AI-driven vulnerability discovery and live validation
 vikramaditya015/samsung-android-lpe
Poc for CVE-2026-20980, CVE-2026-20981, CVE-2026-20982
 leosol/initroot
Exploiting CVE-2016-10277 for Secure Boot and Device Locking bypass
 begitdj/cve-2019-2215-markw
Exploit for CVE-2019-2215 to gain temporary root on Xiaomi MIUI devices, enabling bootloader unlock and system modifications.